

boofuzz
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
dns-fuzzingfuzzingnetwork-security+3
jtpereyda/boofuzzA fork and successor of the Sulley Fuzzing Framework

 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 razvandimescu/numa
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides
 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.
 crypt0s/fakedns
A regular-expression based python MITM DNS server with support for DNS Rebinding attacks
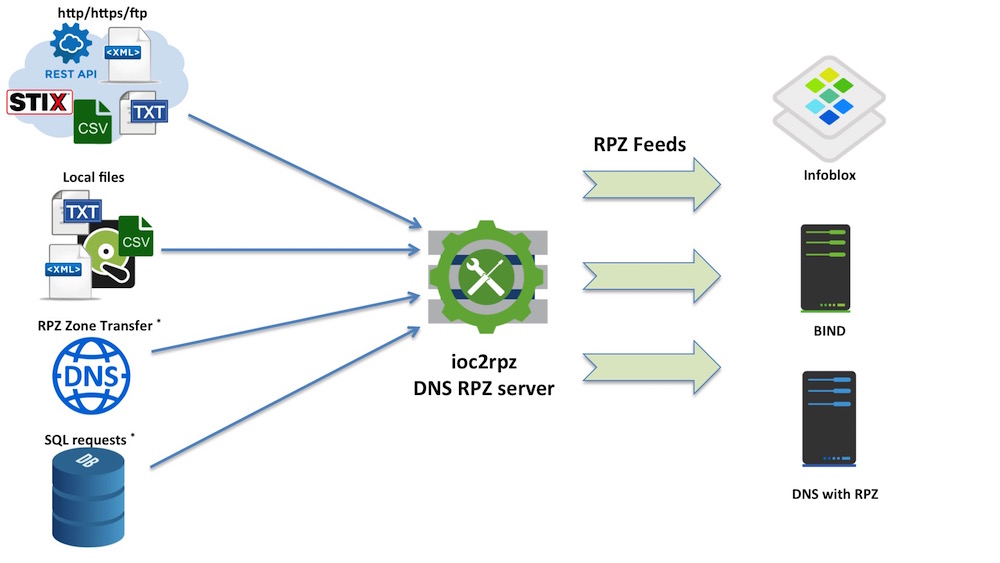 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
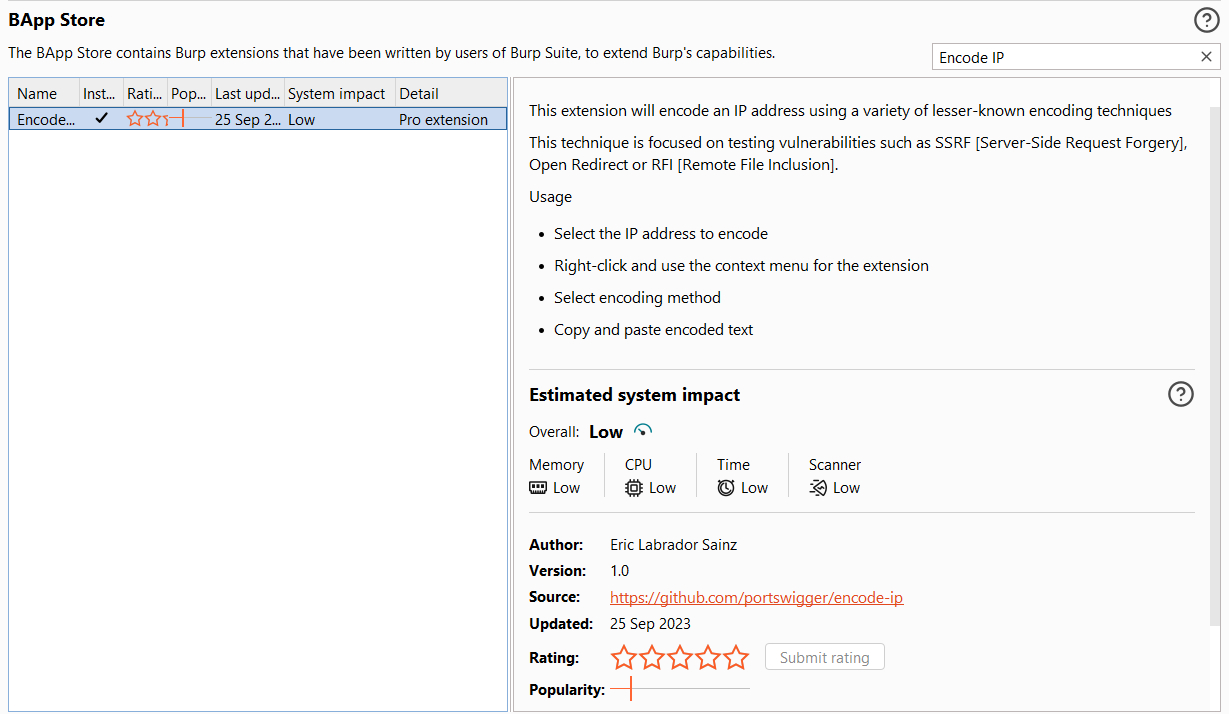 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 hackintoanetwork/cve-2023-52235-poc-spacex-starlink-dns-rebinding
Proof-of-concept exploit for CVE-2023-52235 demonstrating DNS rebinding attack against SpaceX Starlink user terminals to bypass network security…