

 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
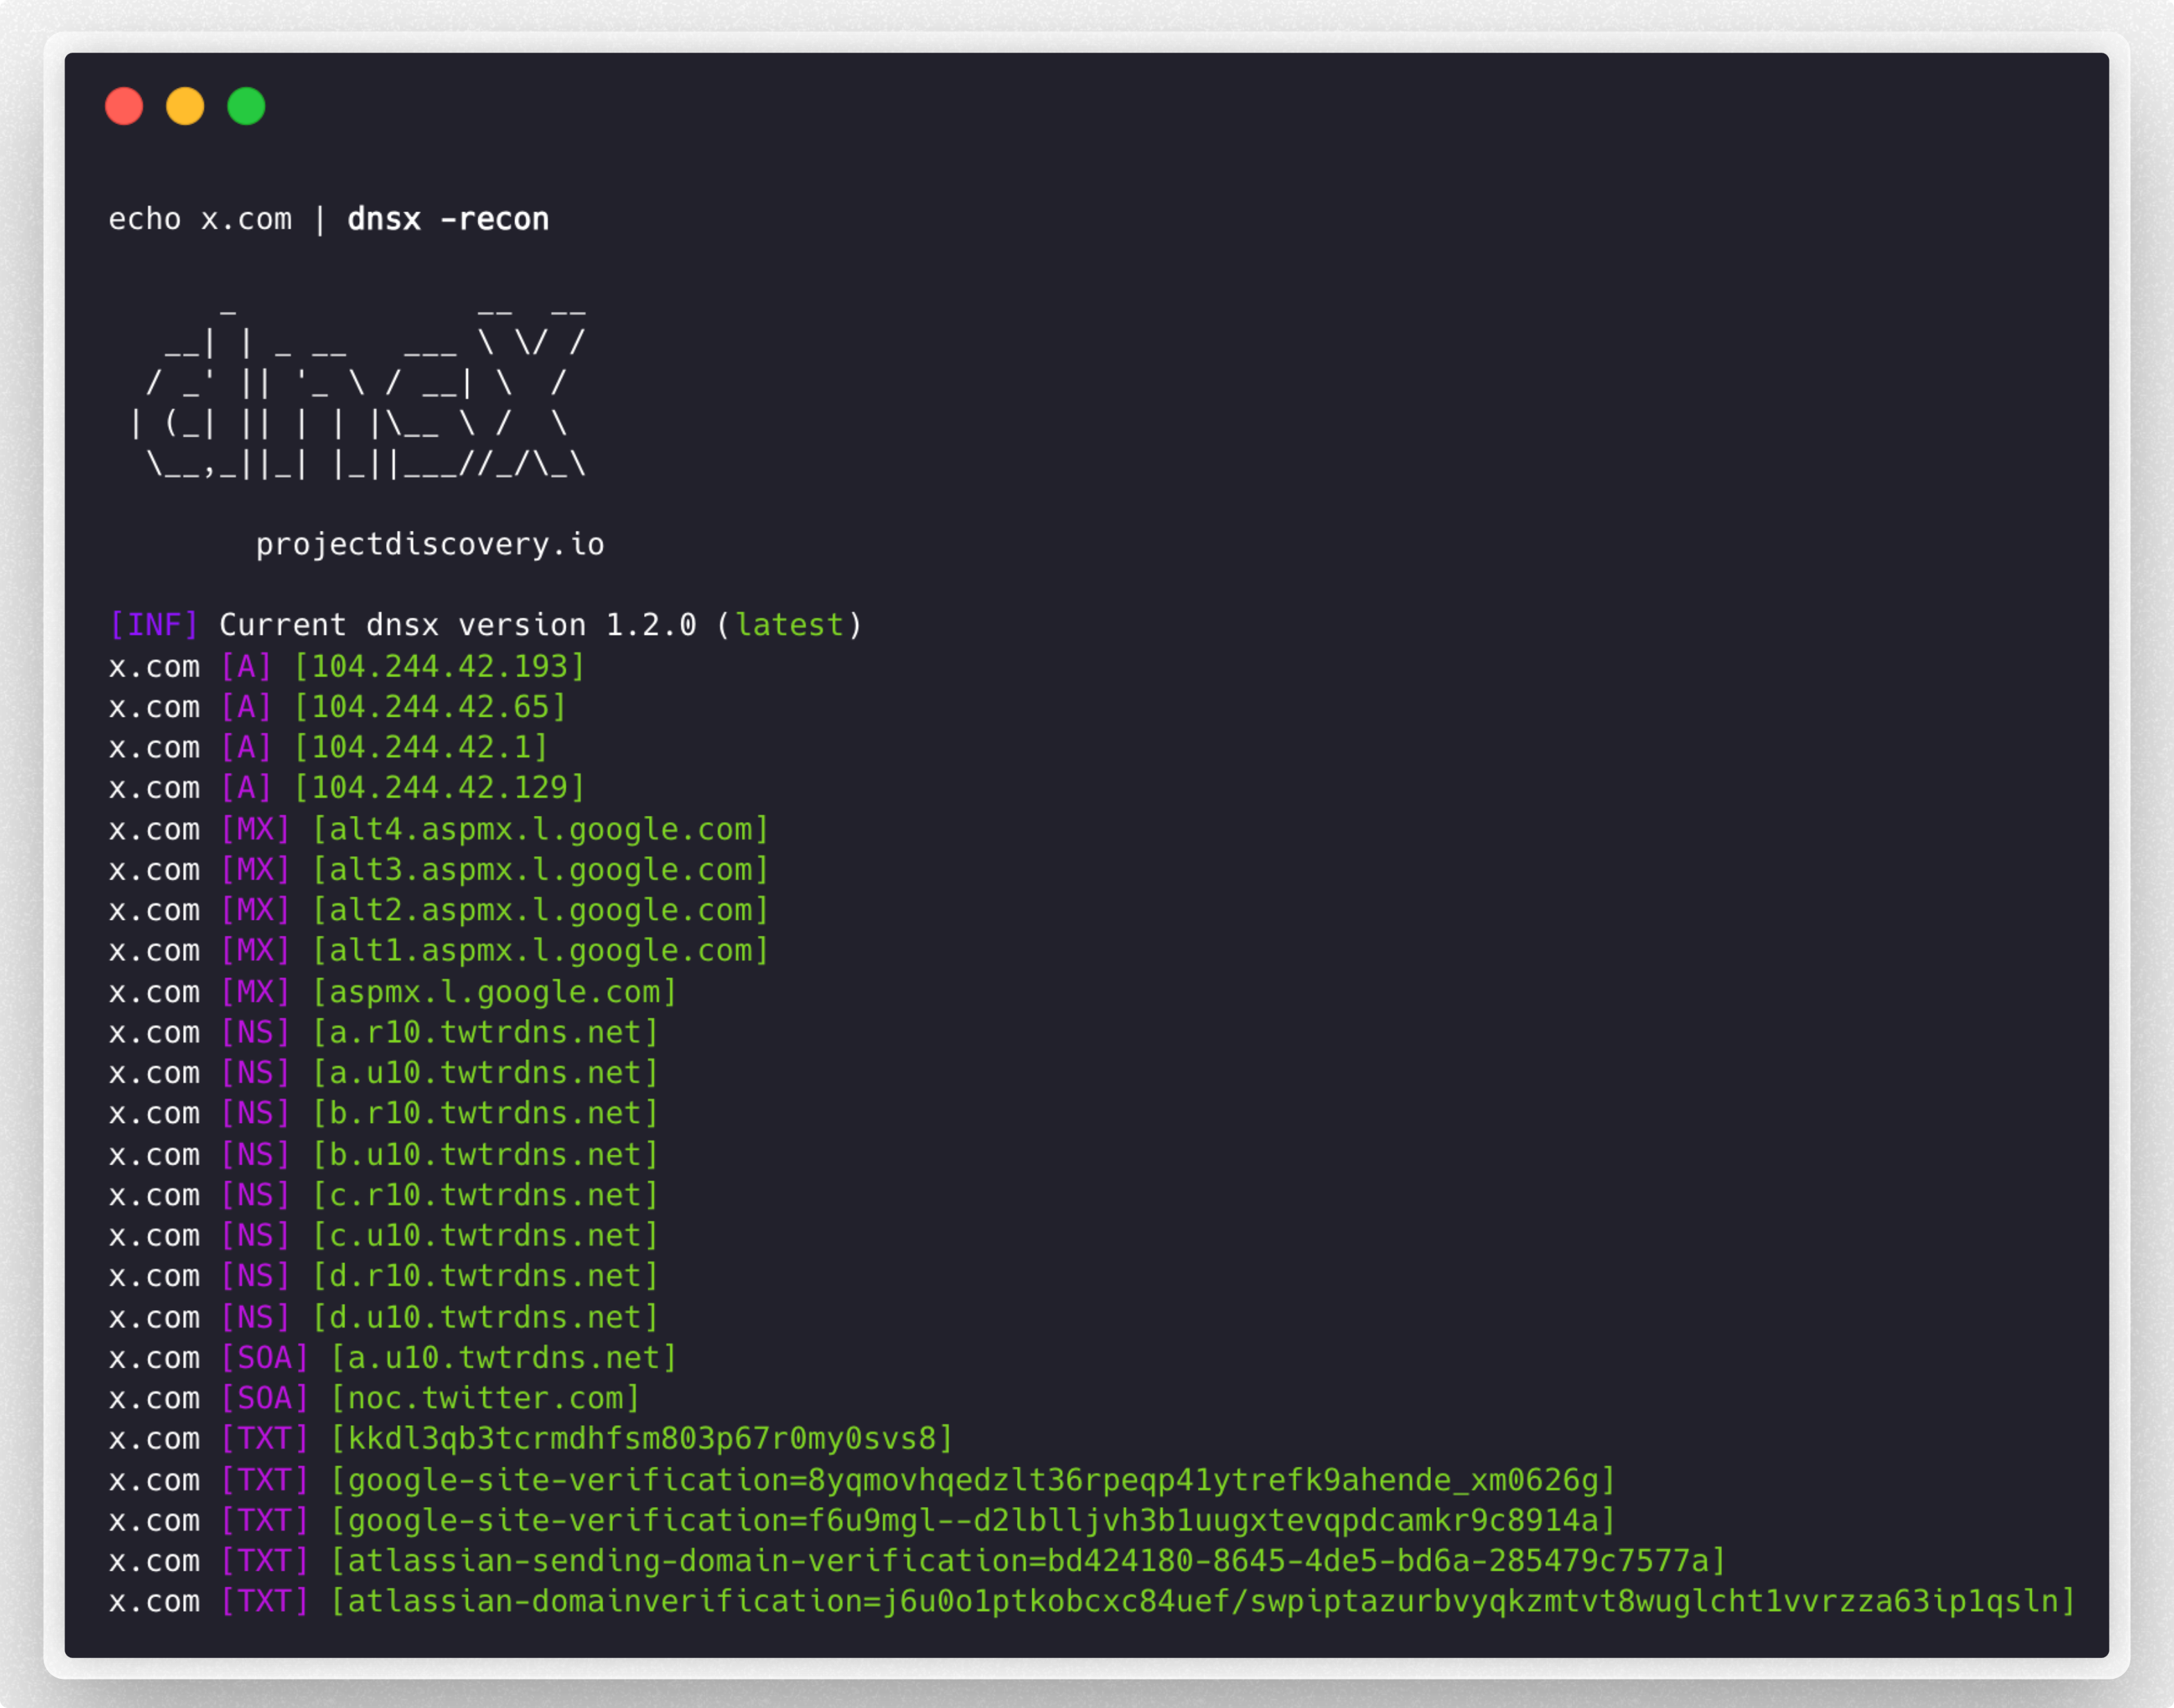 projectdiscovery/dnsx
dnsx is a fast and multi-purpose DNS toolkit allow to run multiple DNS queries of your choice with a list of user-supplied resolvers.
 infosec-au/altdns
Generates permutations, alterations and mutations of subdomains and then resolves them
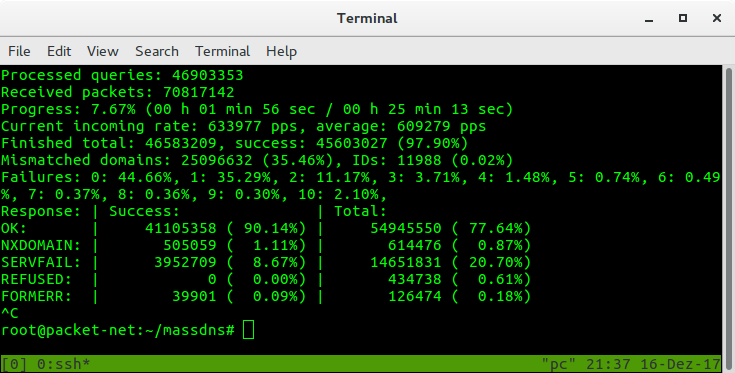 blechschmidt/massdns
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
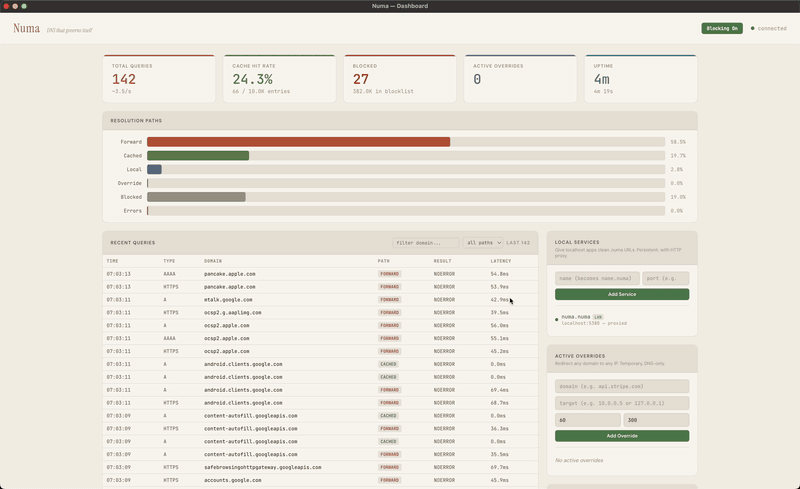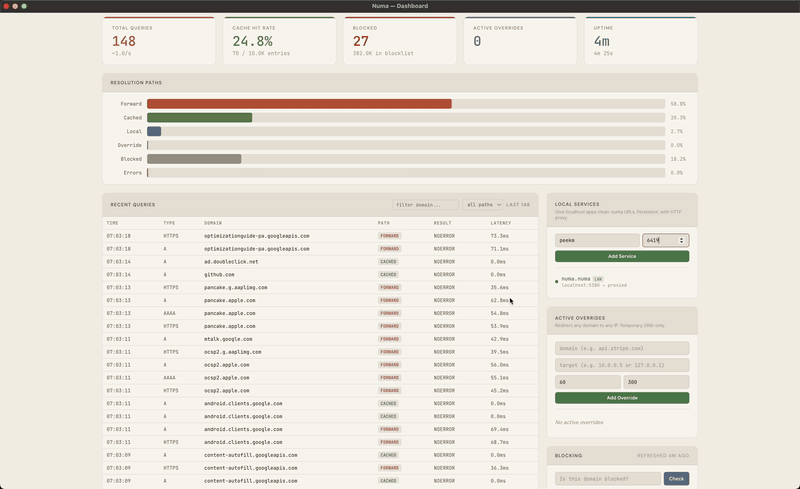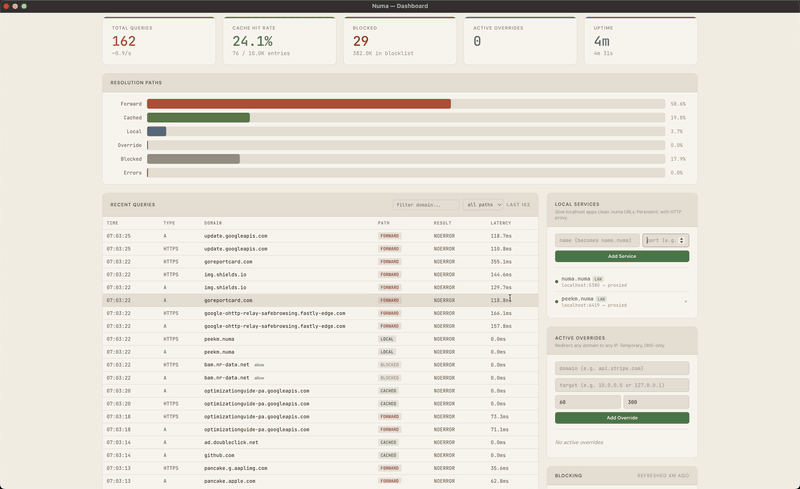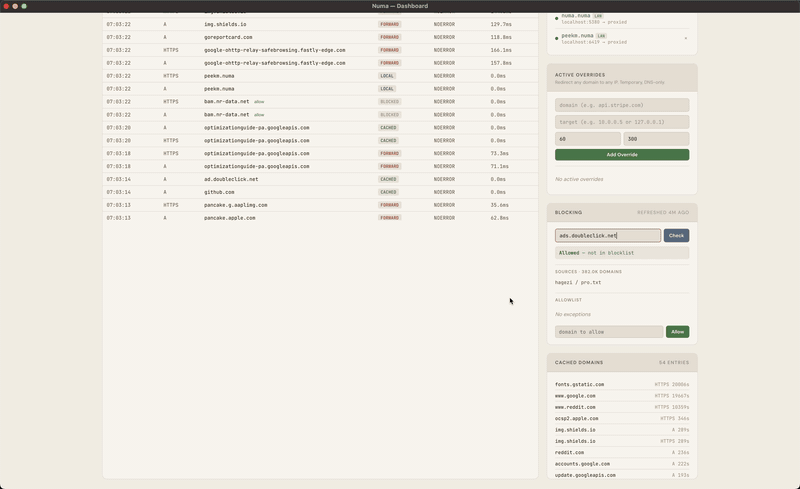 razvandimescu/numa
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides
 d3mondev/puredns
High-speed DNS resolver and subdomain bruteforcer with accurate wildcard filtering and DNS poisoning validation for precise reconnaissance.
 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.