
honggfuzz
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
dns-fuzzingdynamic-code-analysisfuzzing+1
3.4k
google/honggfuzzSecurity oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 crypt0s/fakedns
A regular-expression based python MITM DNS server with support for DNS Rebinding attacks
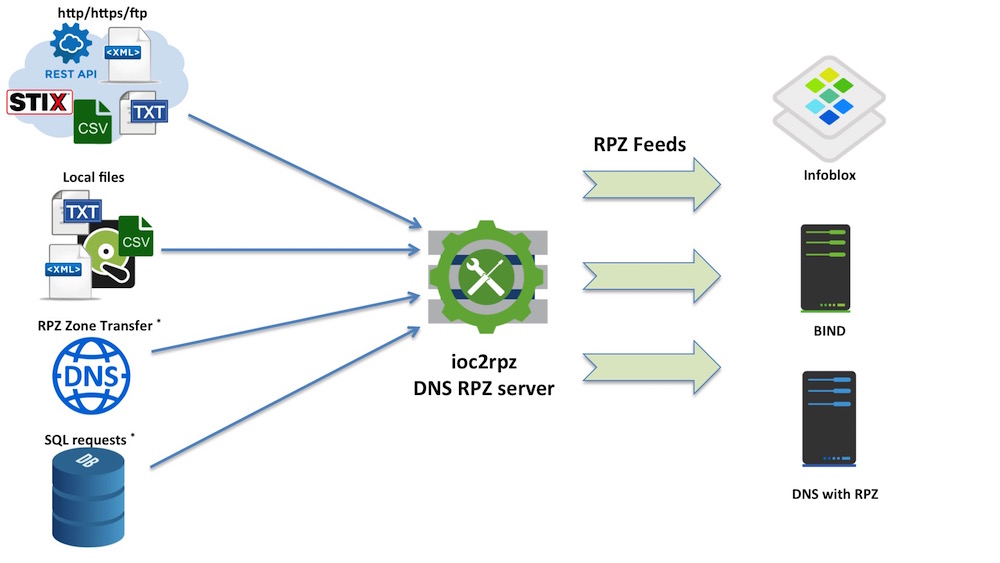 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 hackintoanetwork/cve-2023-52235-poc-spacex-starlink-dns-rebinding
Proof-of-concept exploit for CVE-2023-52235 demonstrating DNS rebinding attack against SpaceX Starlink user terminals to bypass network security…
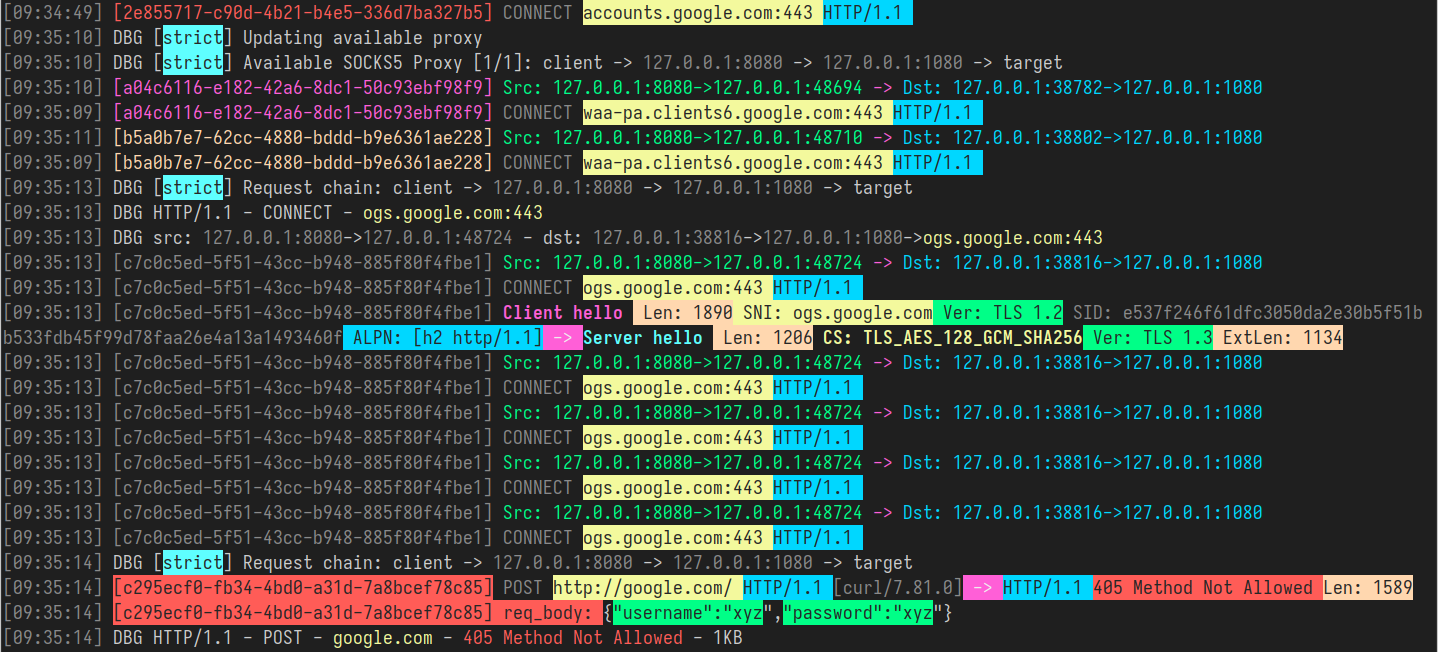 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
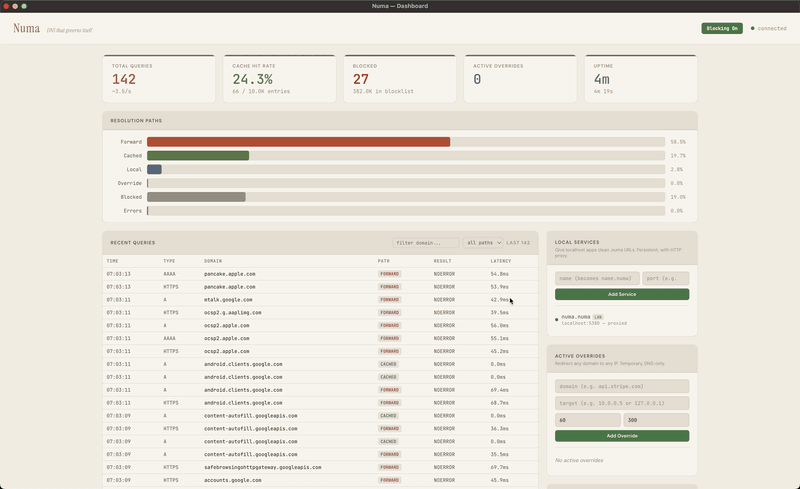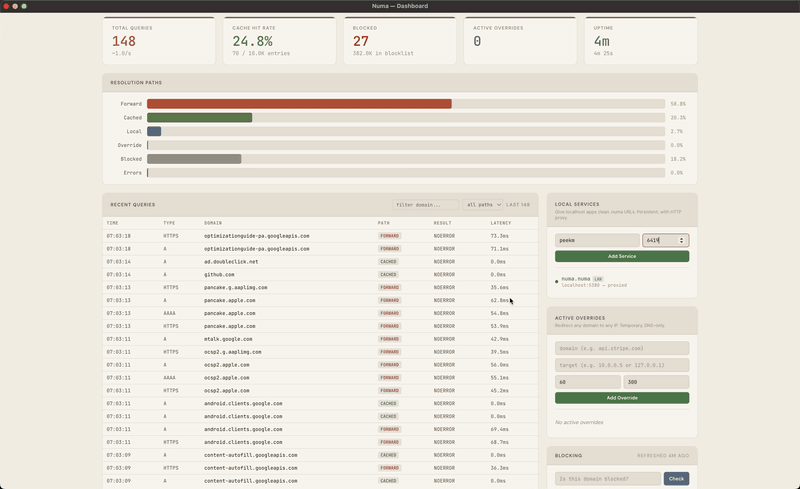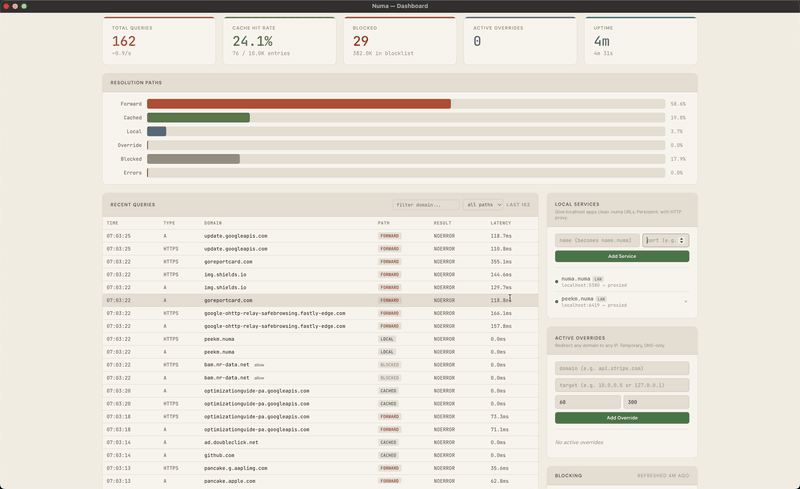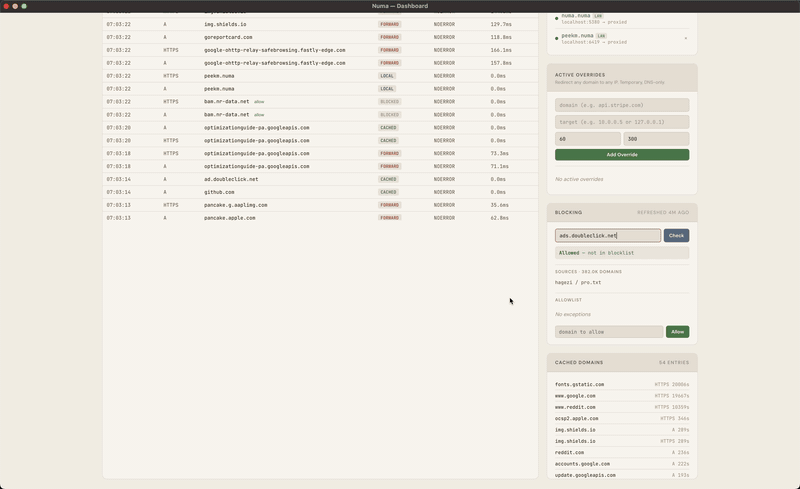 razvandimescu/numa
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides

 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
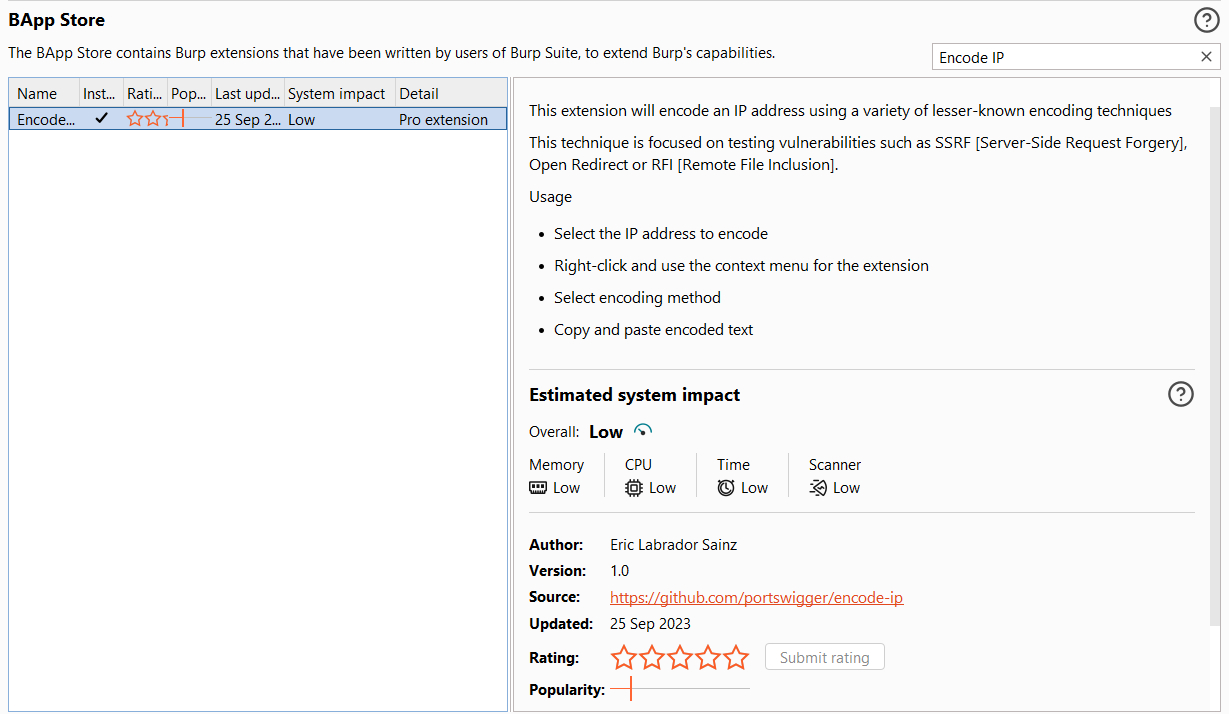 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework