
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 aflplusplus/aflplusplus
The fuzzer afl++ is afl with community patches, qemu 5.1 upgrade, collision-free coverage, enhanced laf-intel & redqueen, AFLfast++ power schedules,…
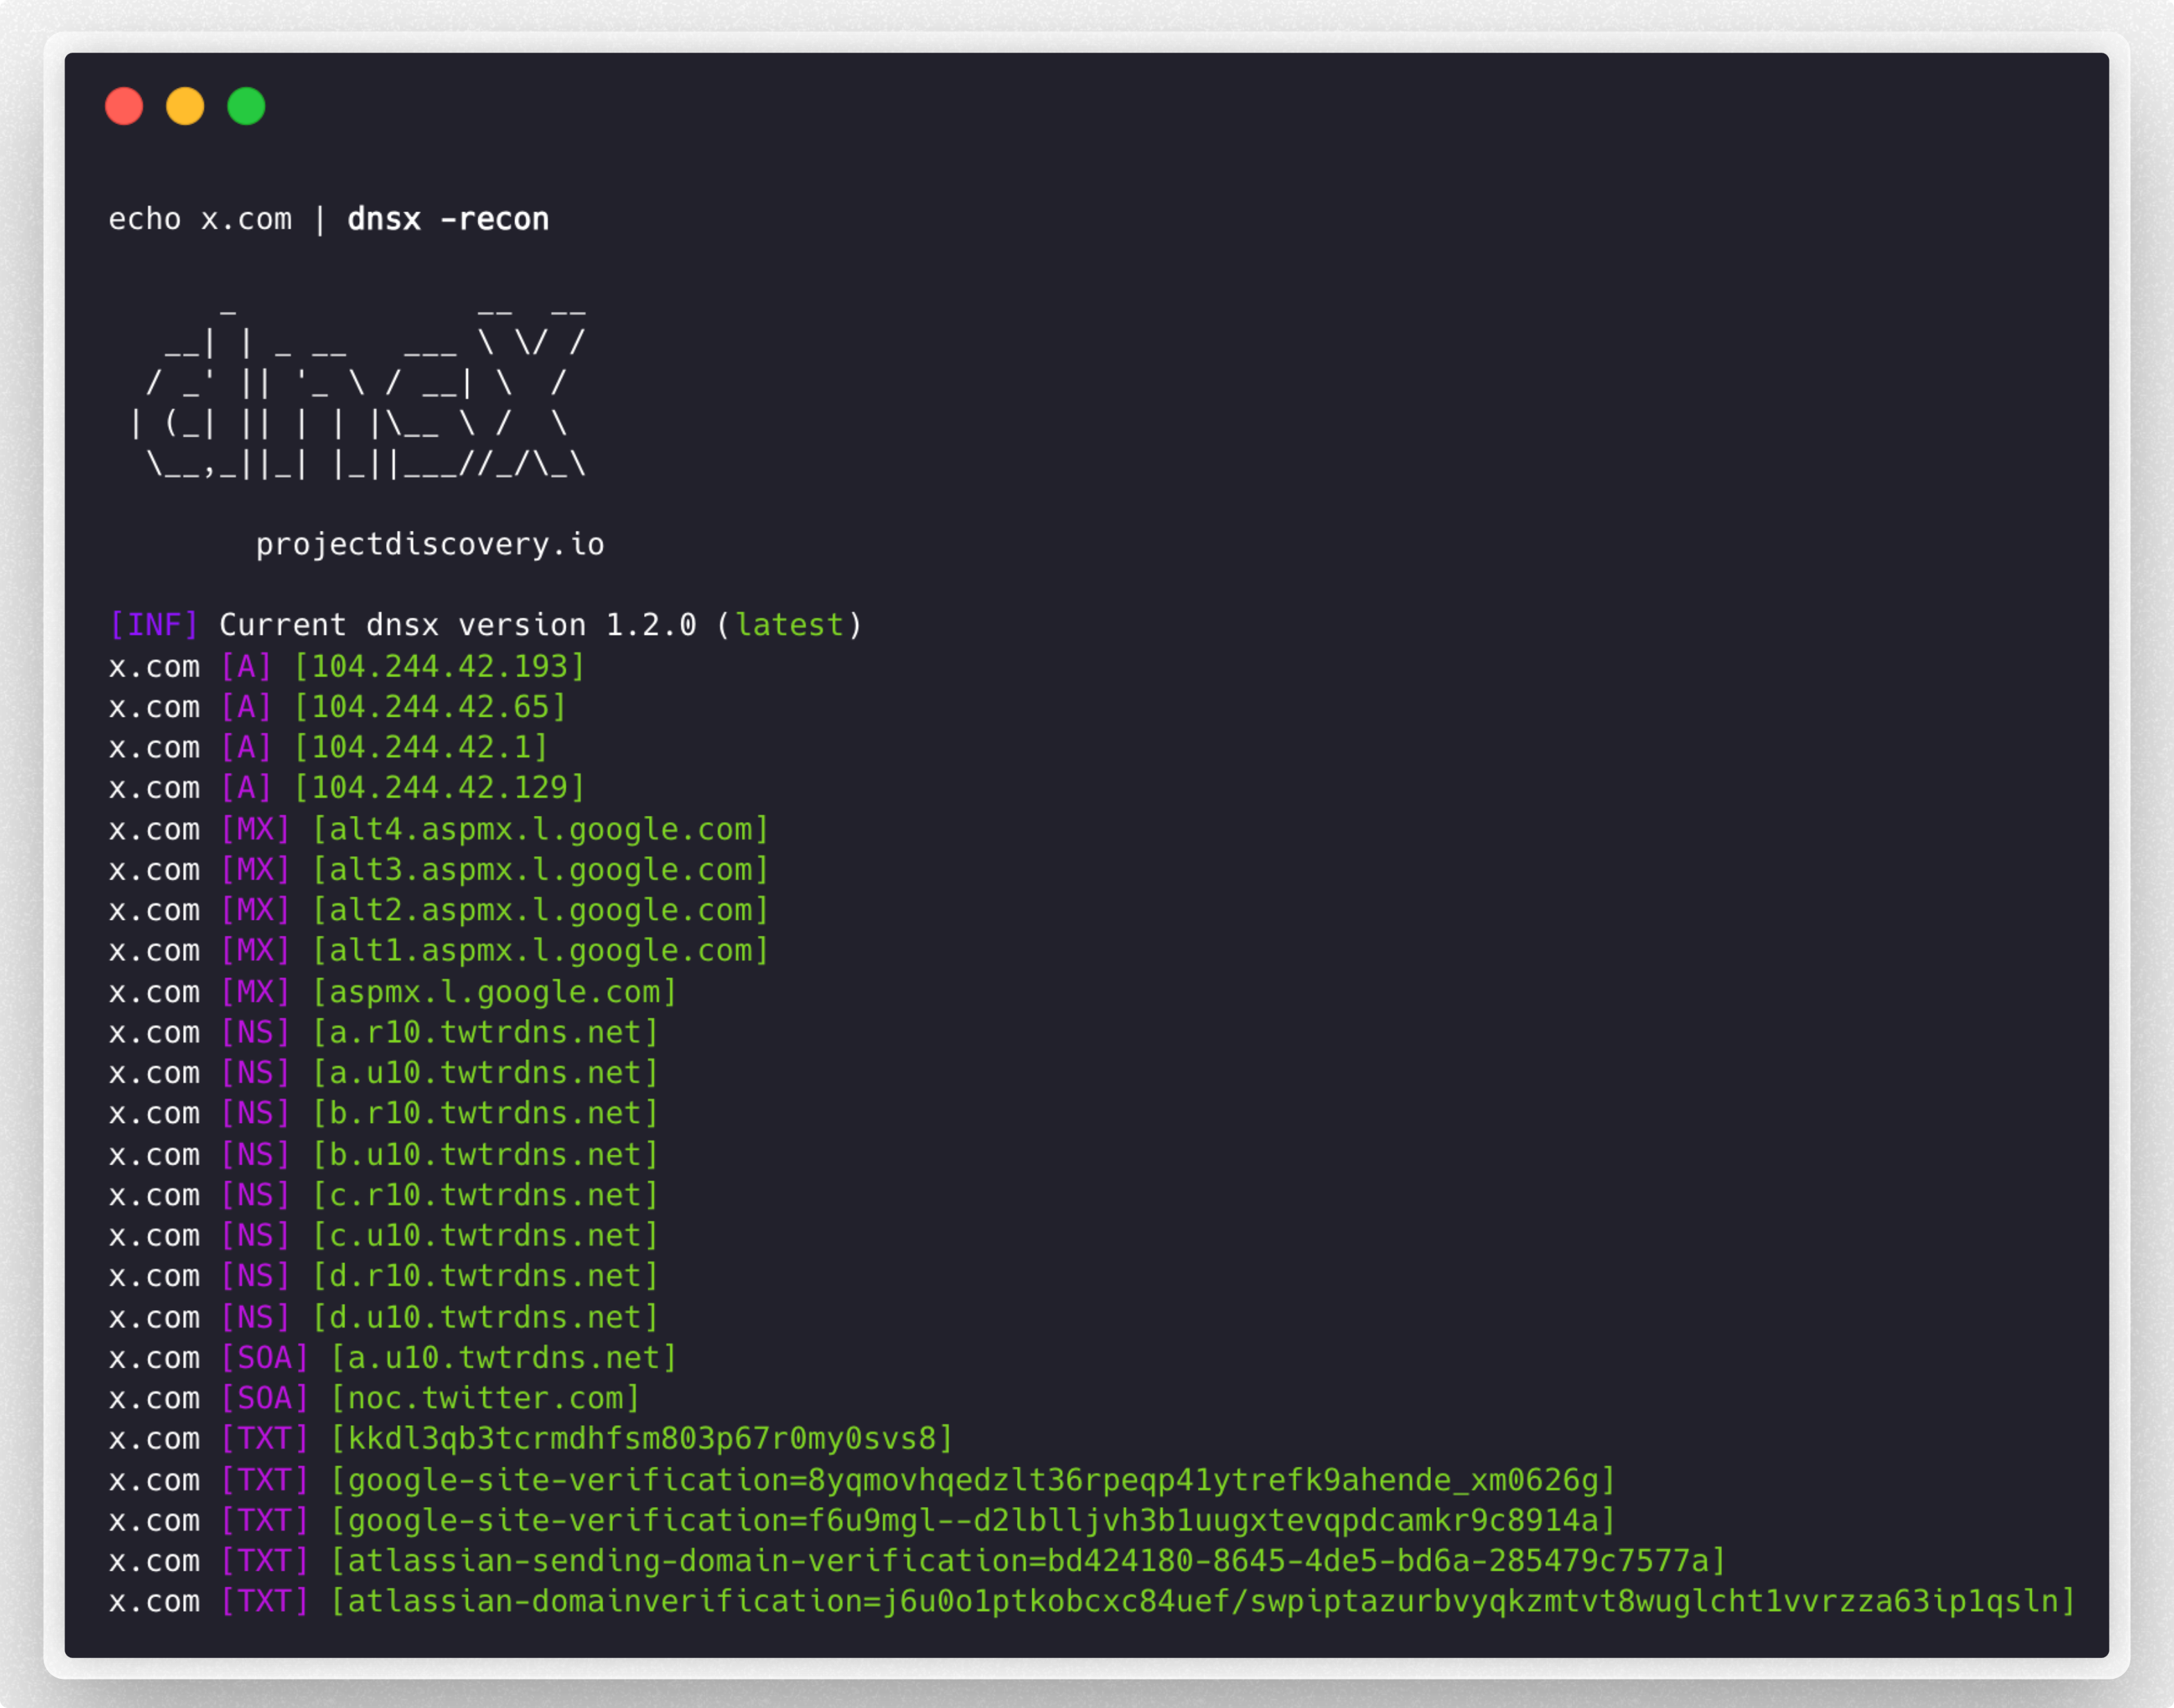 projectdiscovery/dnsx
dnsx is a fast and multi-purpose DNS toolkit allow to run multiple DNS queries of your choice with a list of user-supplied resolvers.
 d3mondev/puredns
High-speed DNS resolver and subdomain bruteforcer with accurate wildcard filtering and DNS poisoning validation for precise reconnaissance.
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
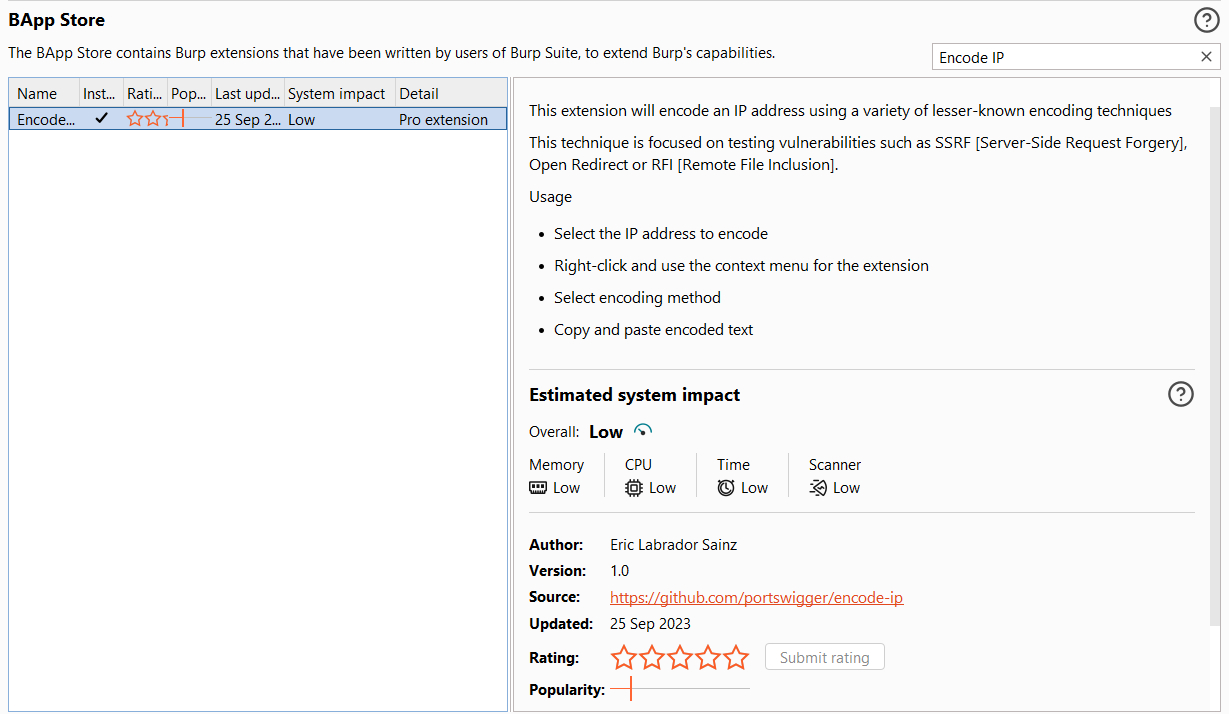 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 razvandimescu/numa
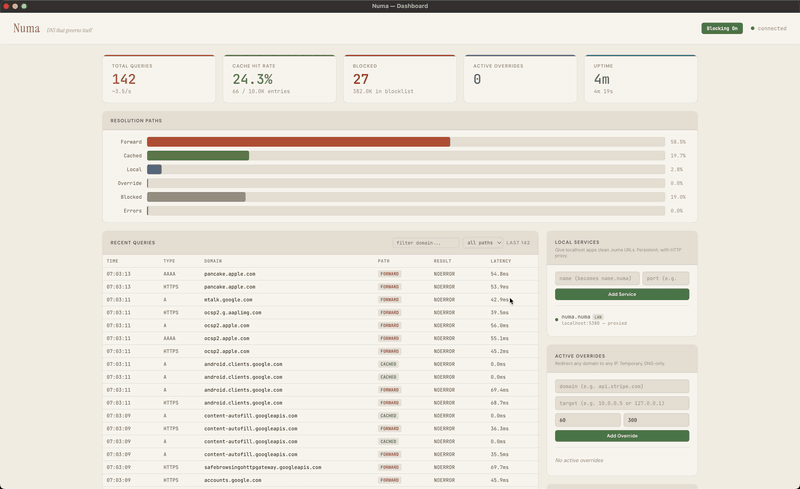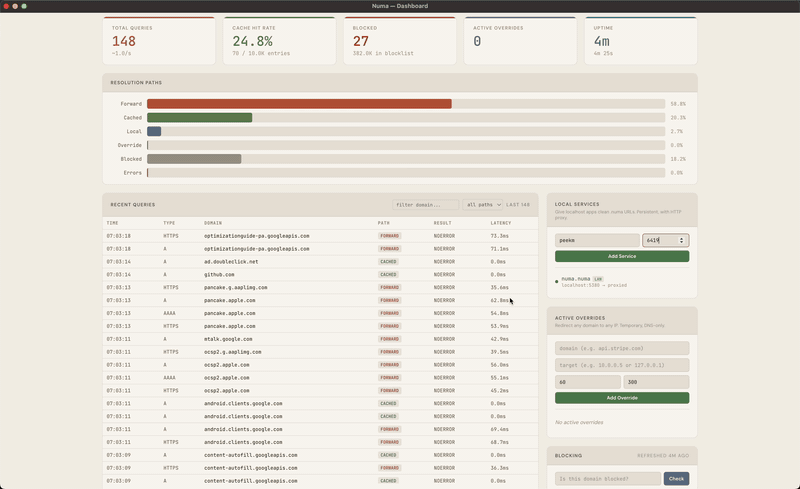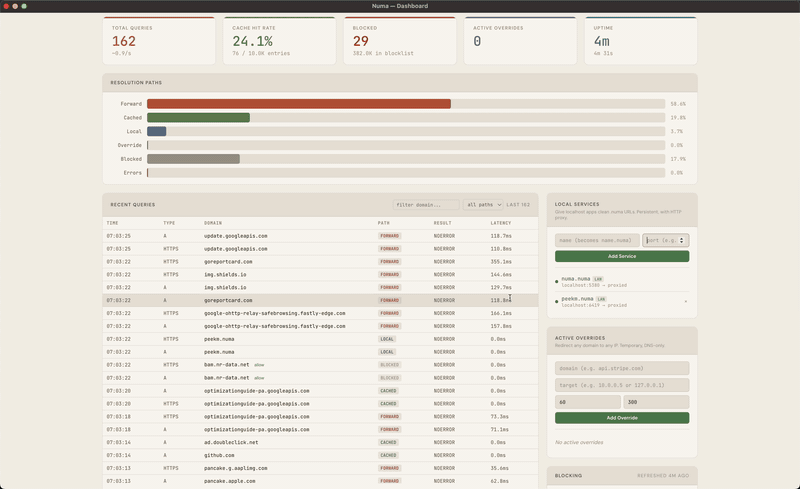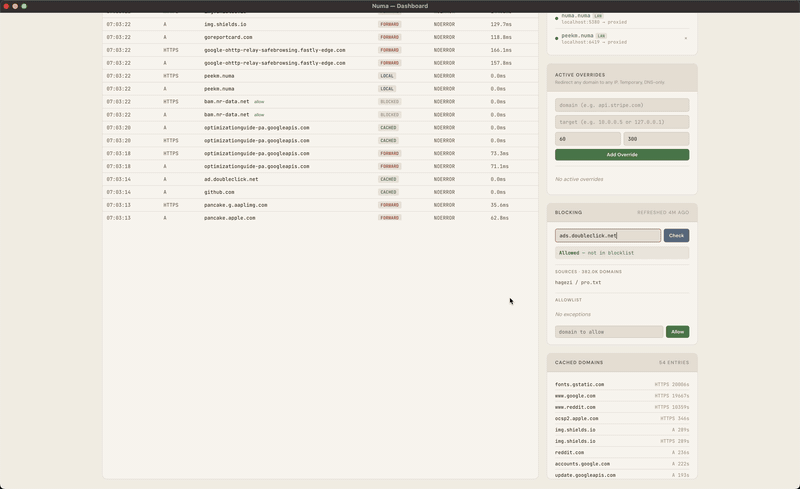
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
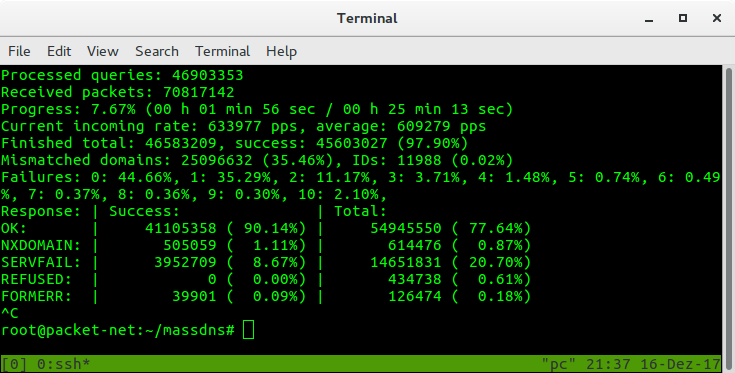 blechschmidt/massdns
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
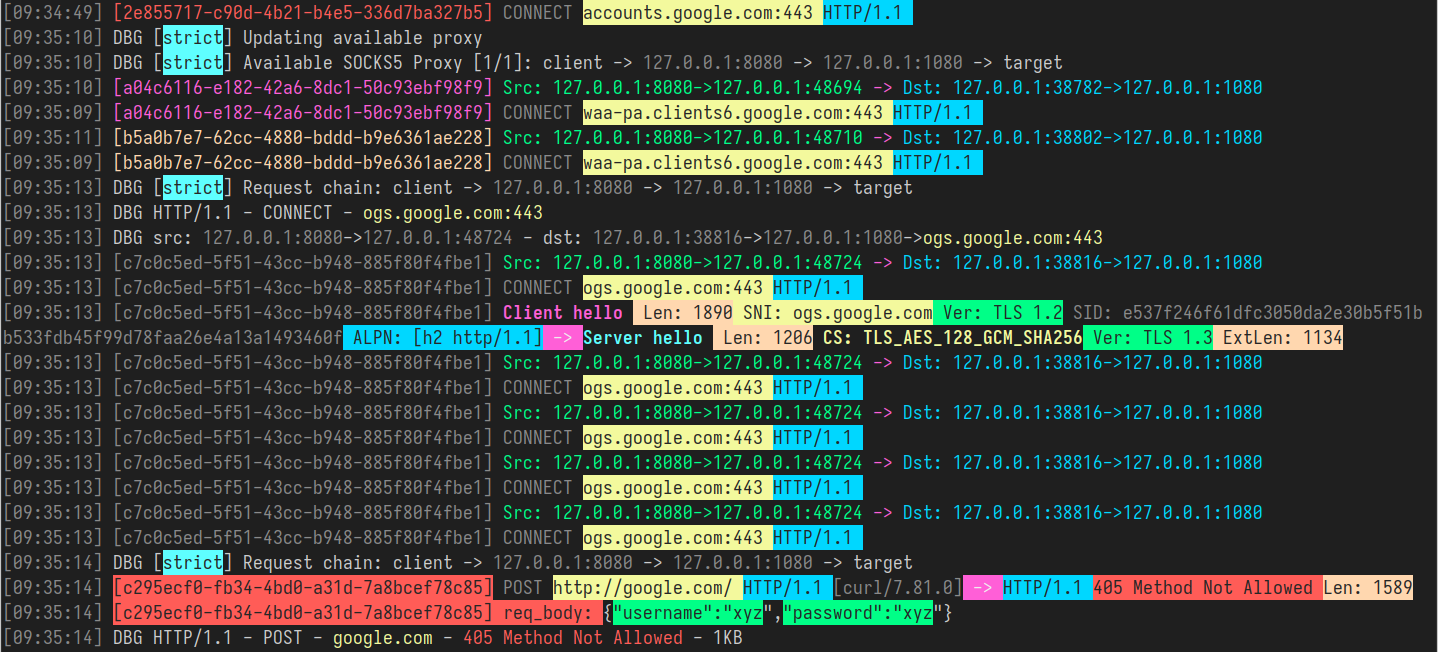 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
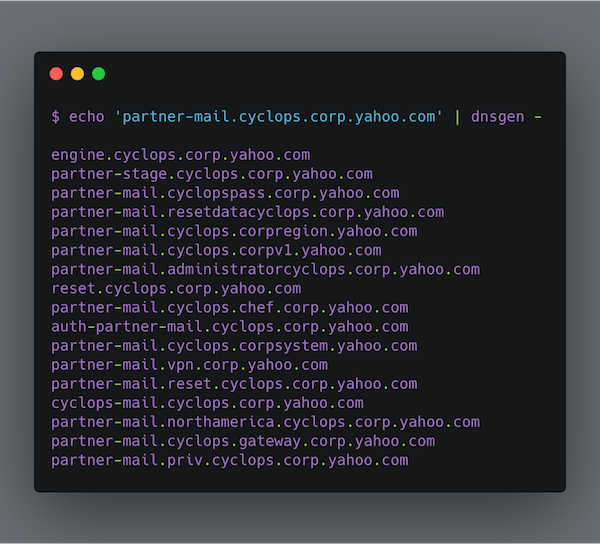 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework