
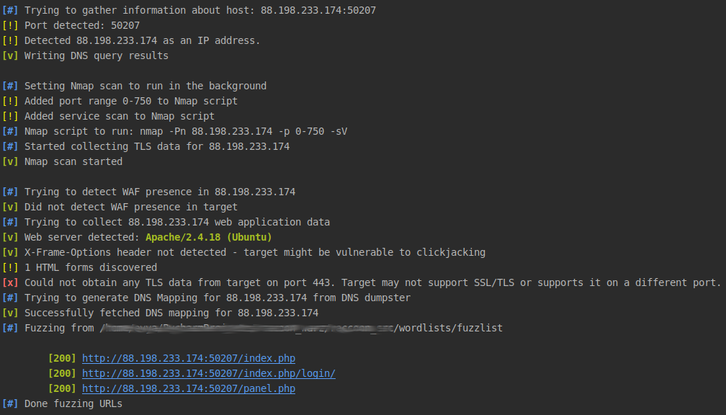
Raccoon
 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
dns-analysisfuzzinginformation-gathering+6
4.0k1 year ago
evyatarmeged/raccoonA high performance offensive security tool for reconnaissance and vulnerability scanning
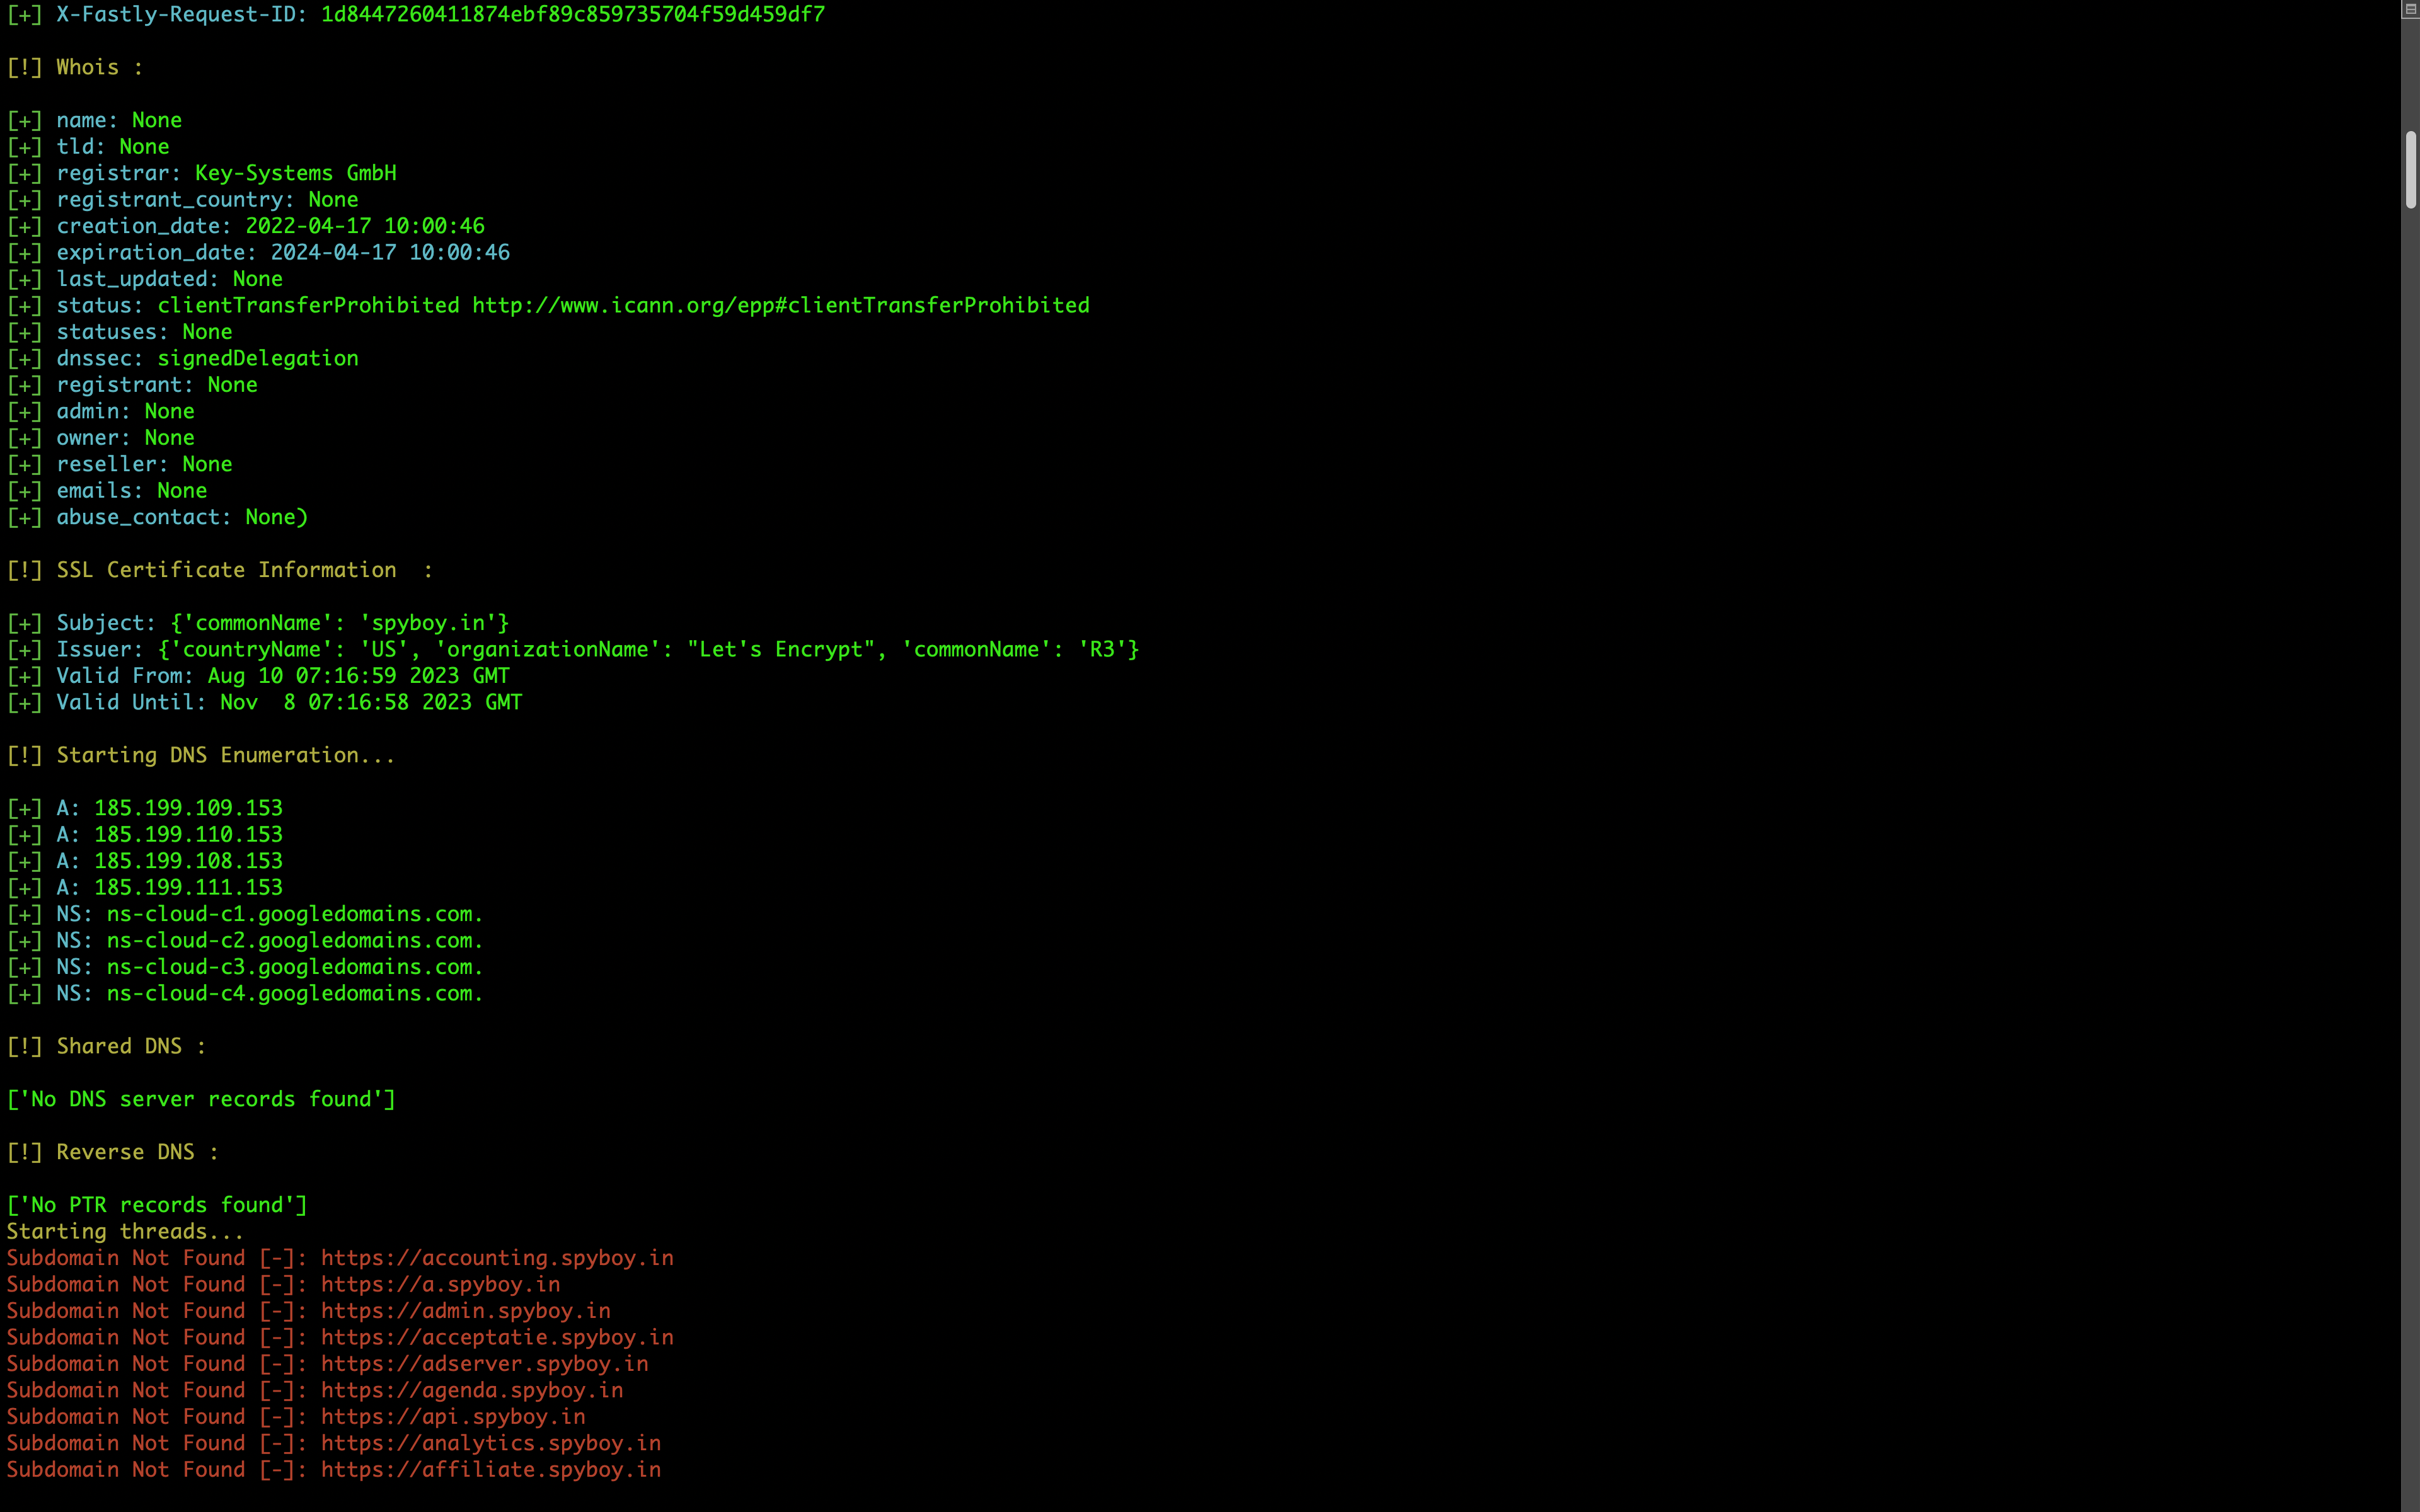 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…
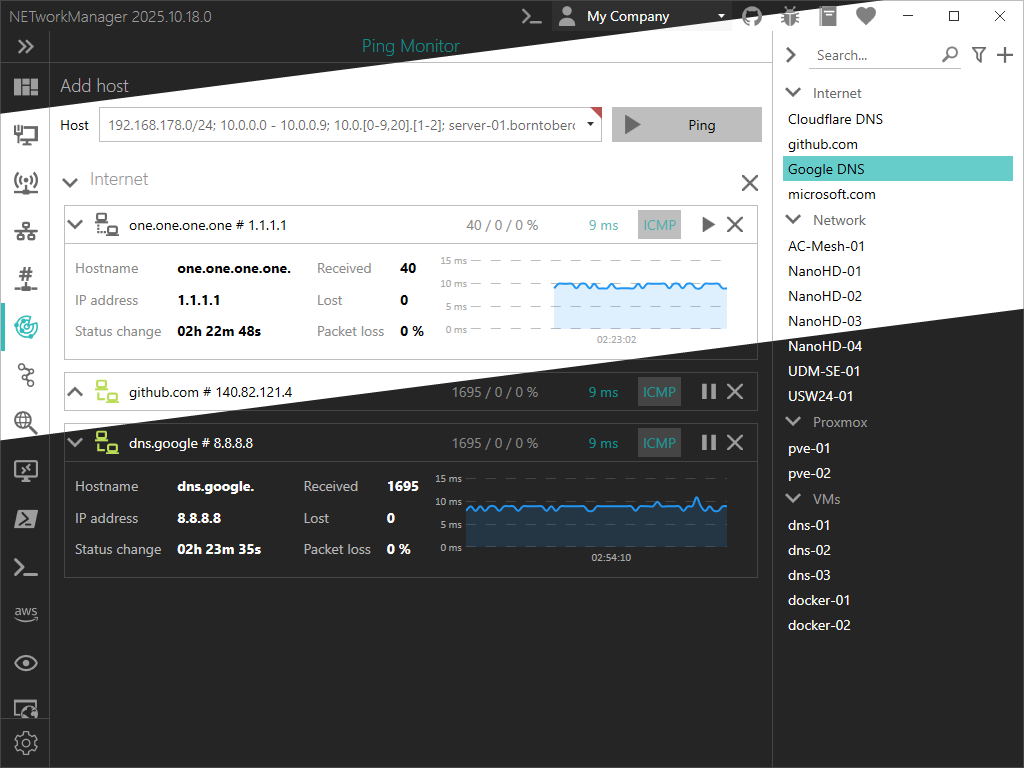 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
 te-k/harpoon
CLI tool for open source and threat intelligence
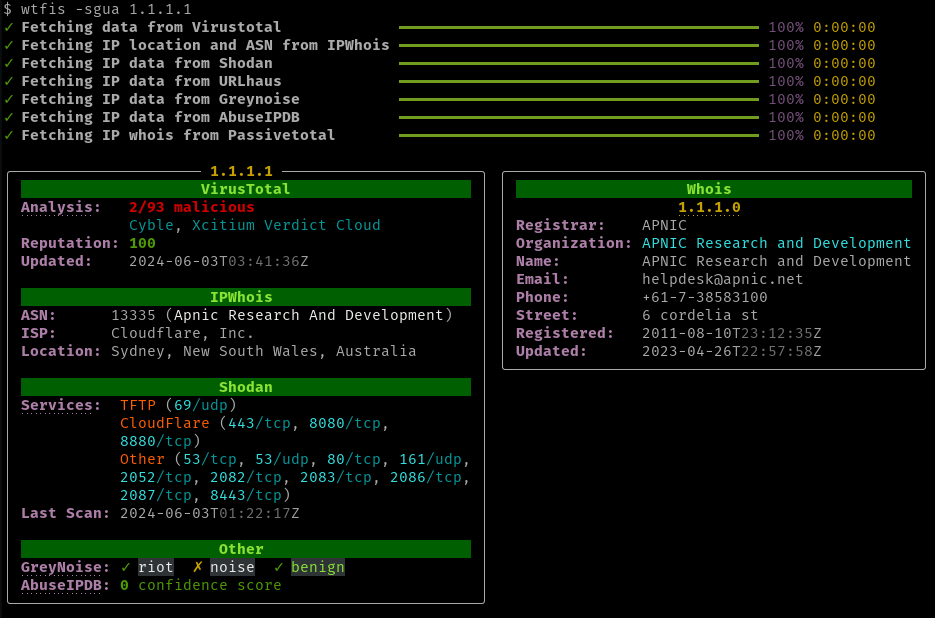 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
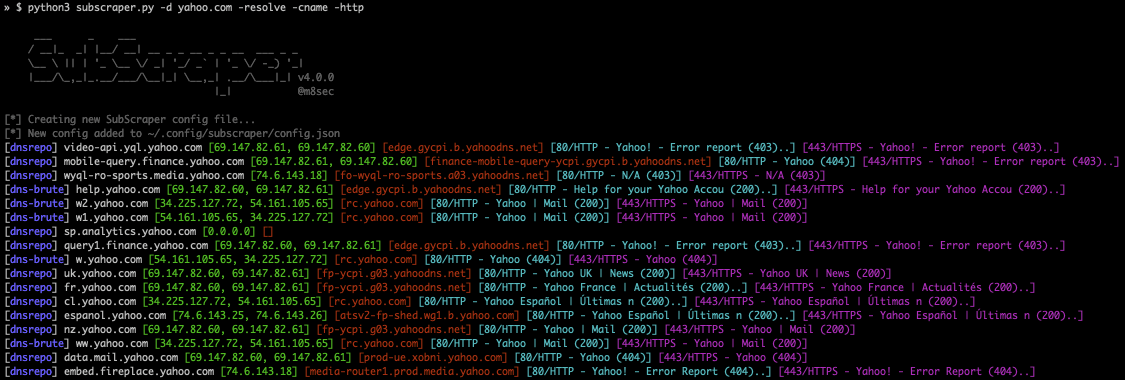 m8sec/subscraper
Subdomain and target enumeration tool built for offensive security testing
 netspi/ateam
Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…
 ntrippar/arpwner
ARP spoofing and network packet manipulation tool for man-in-the-middle attacks, traffic interception, and LAN reconnaissance using Python and pcap.
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 zu1k/nali
An offline tool for querying IP geographic information and CDN provider. 一个查询IP地理信息和CDN服务提供商的离线终端工具.
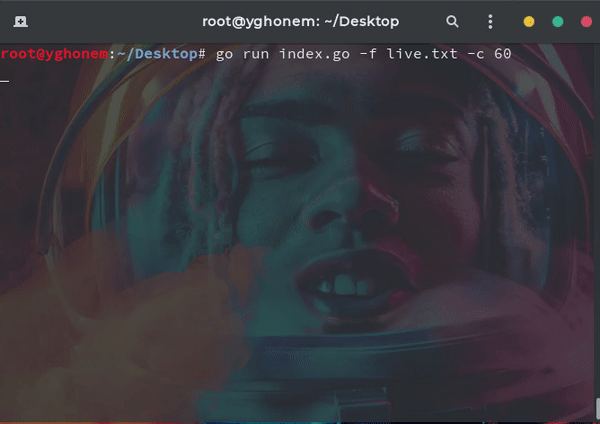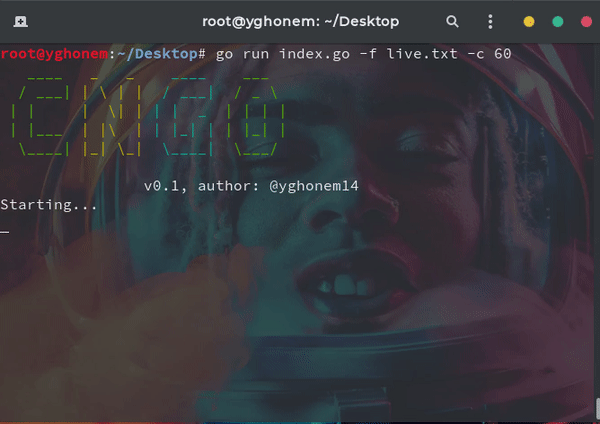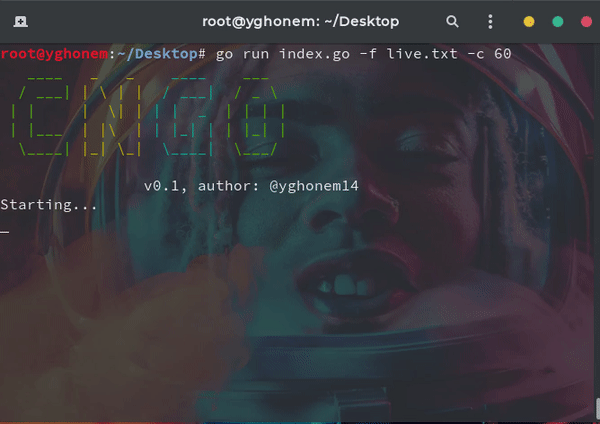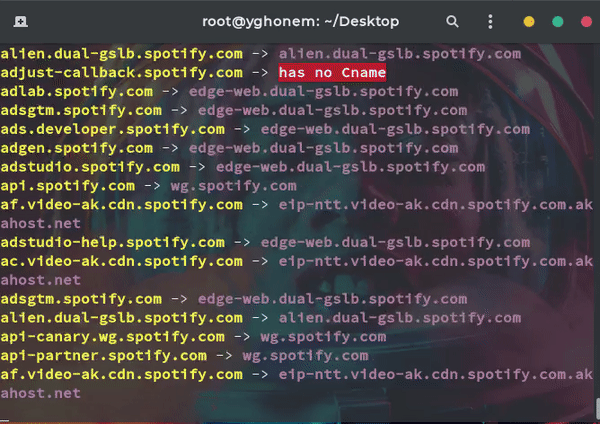 0xsnowmn/cngo
Fast Golang Tool To Get Cname For Domains and Subdomain
 koenrh/s3enum
Fast and stealthy Amazon S3 bucket enumeration tool for pentesters.
 edu0x01/sr-71
An easy-to-use Python tool for performing subdomain enumeration, endpoint recognition, and more
 jh00nbr/phishruffus
Intelligent threat hunter and phishing servers
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
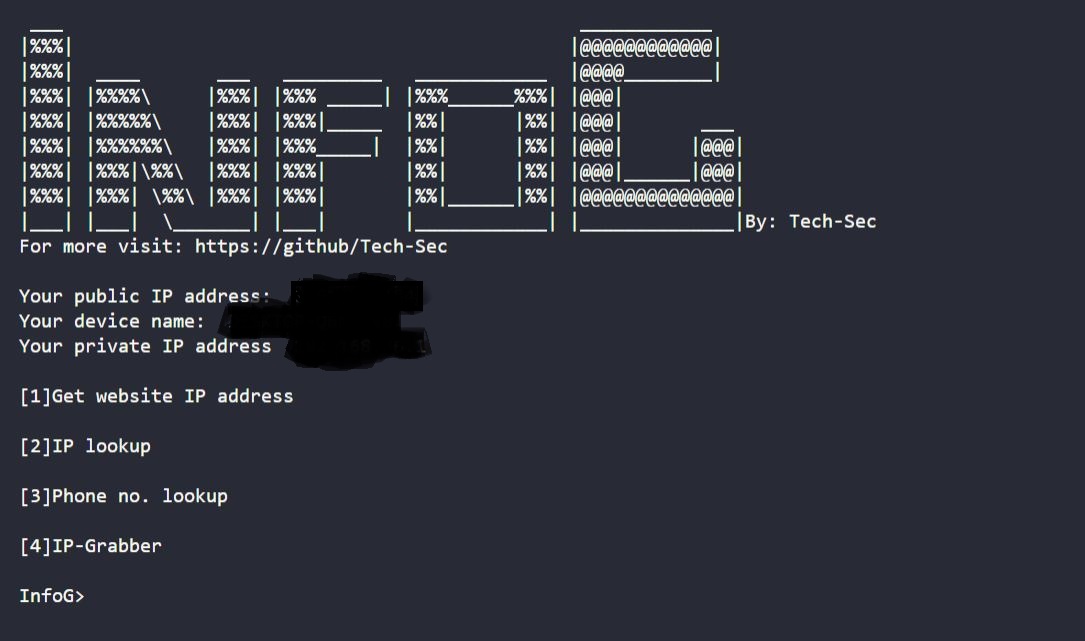 tech-sec/infog
Multi-purpose OSINT tool for IP address lookup, DNS resolution, phone number details, and IP-grabbing via lure links for reconnaissance.
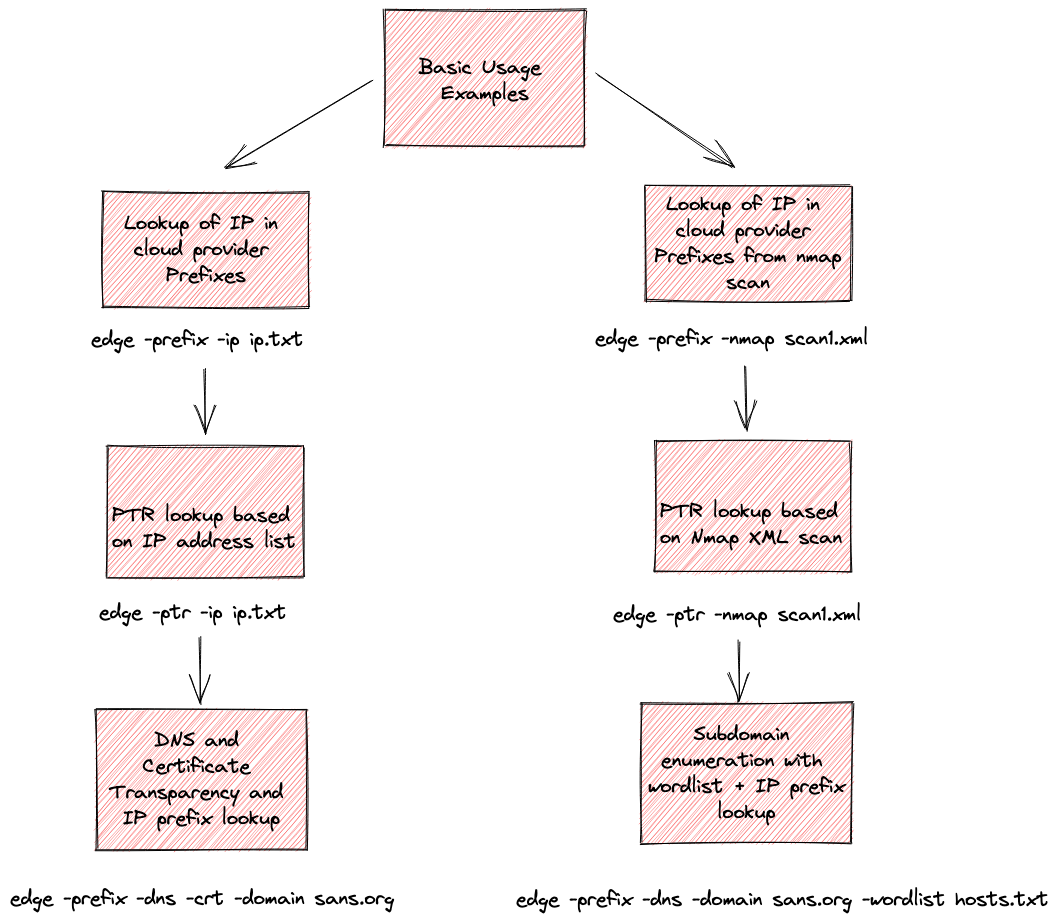 iknowjason/edge
Whois for the Cloud: Recon tool for cloud provider attribution. Supports AWS, Azure, Google, Cloudflare, and Digital Ocean.