

rita
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
663
activecm/ritaReal Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 opendns/dataviz
OpenDNS Data Visualization Framework
 n3ph0s/onionscan
Scan and analyze Tor hidden services (.onion) to extract metadata, SSH banners, email addresses, and potential IP leaks via mod_status, with a…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 incidedigital/mistica
An open source swiss army knife for arbitrary communication over application protocols
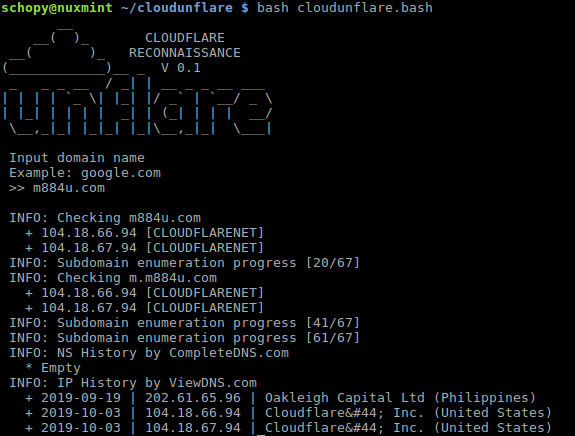 greycatz/cloudunflare
Reconnaissance Real IP address for Cloudflare Bypass
 g0ldencybersec/easyeasm
Zero-dollar attack surface management tool
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 nasroabd/zynos-attacker
ZynOS tool for automated attack on a range of IPs, find more informations at :
 samhaxr/takeover-v1
Takeover script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover…
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 nullhypothesis/exitmap
A fast and modular scanner for Tor exit relays. The canonical repository (including issue tracker) is at…
 sensepost/det
(extensible) Data Exfiltration Toolkit (DET)
 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…
 satchfunky/cve-2026-41096-poc
windows api bug
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
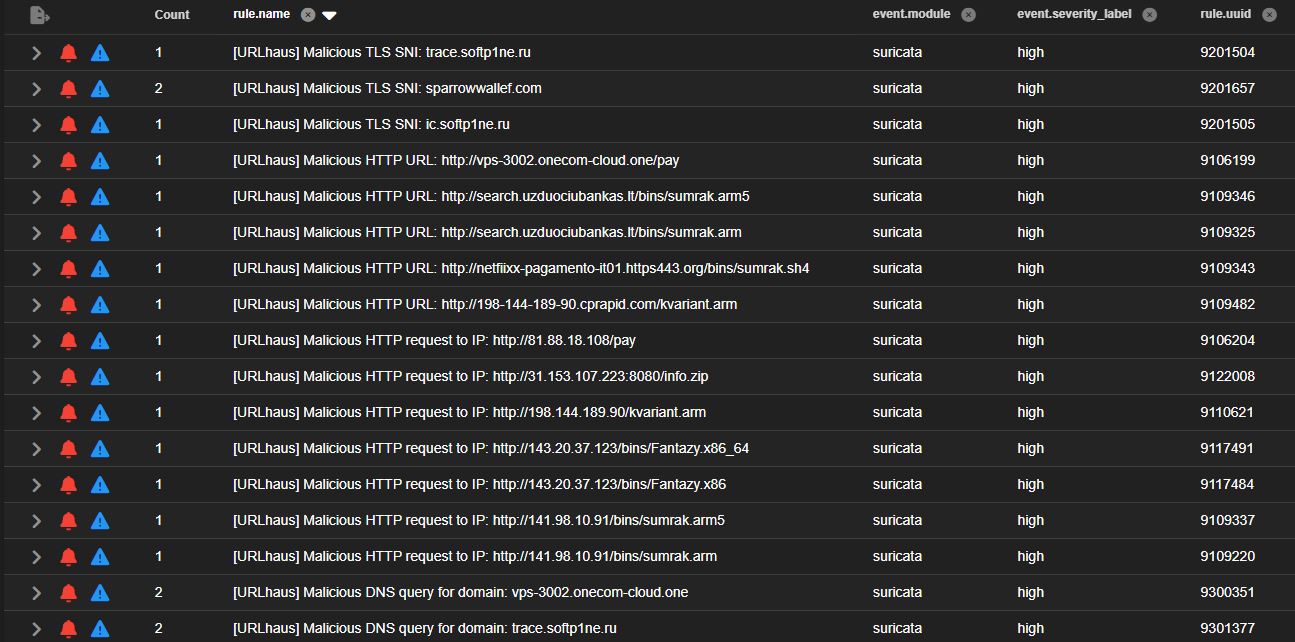 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay