
chomp-scan
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
dns-analysisinformation-gatheringpenetration-testing+6
394
solomonsklash/chomp-scanA scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
 ettic-team/dnsbin
DNS-based data exfiltration testing tool with bidirectional transfer, web UI, and client script for detecting blind RCE/XXE vulnerabilities in…
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 h43z/dns-rebinding-tool
dns rebind tool with custom scripts
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 0xxon/cve-2020-13777
Zeek script to detect servers vulnerable to CVE-2020-13777
 papamica/waf-checker
Tests your WAF with +160 payloads
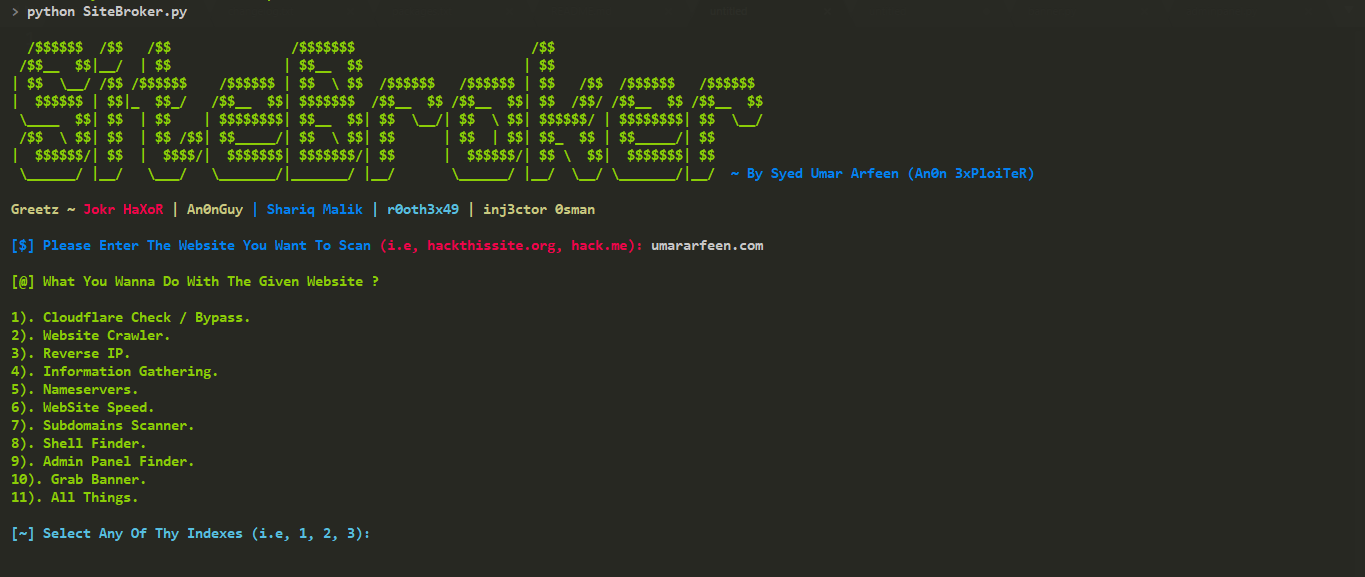 anon-exploiter/sitebroker
A cross-platform python based utility for information gathering and penetration testing automation!
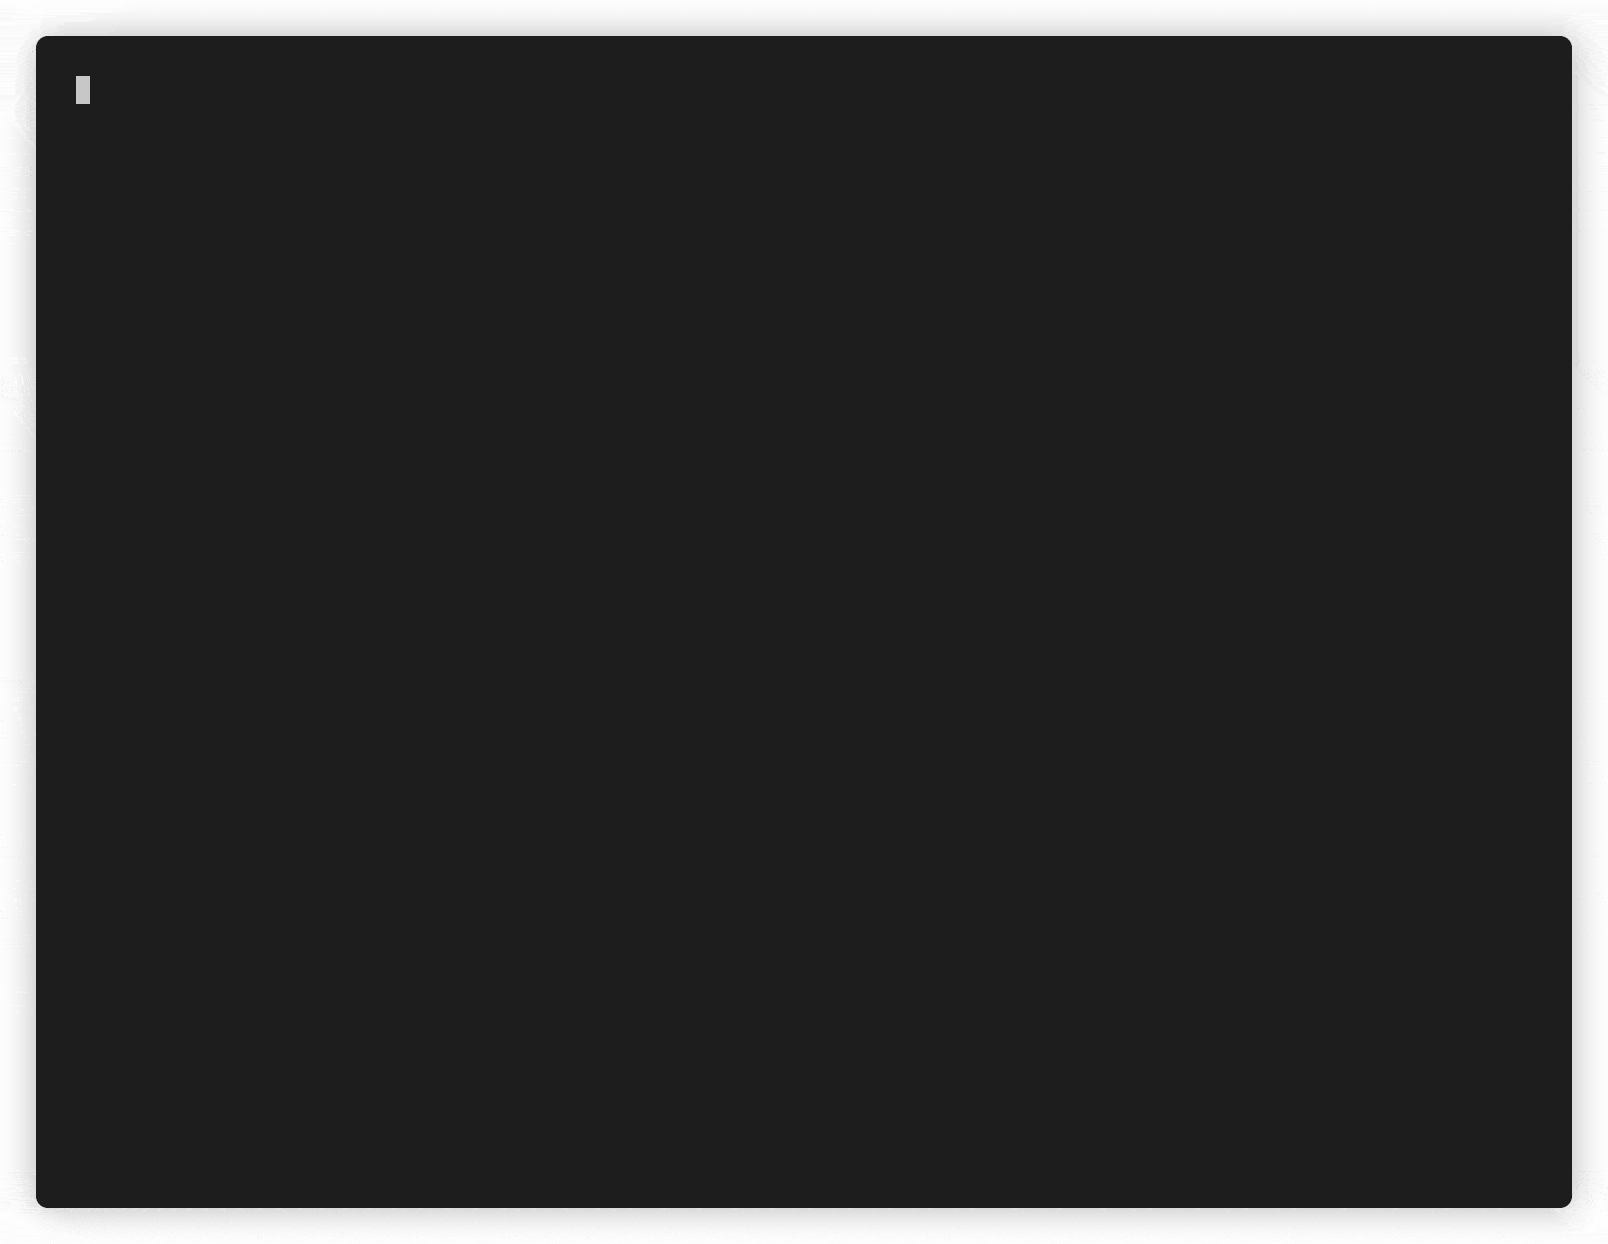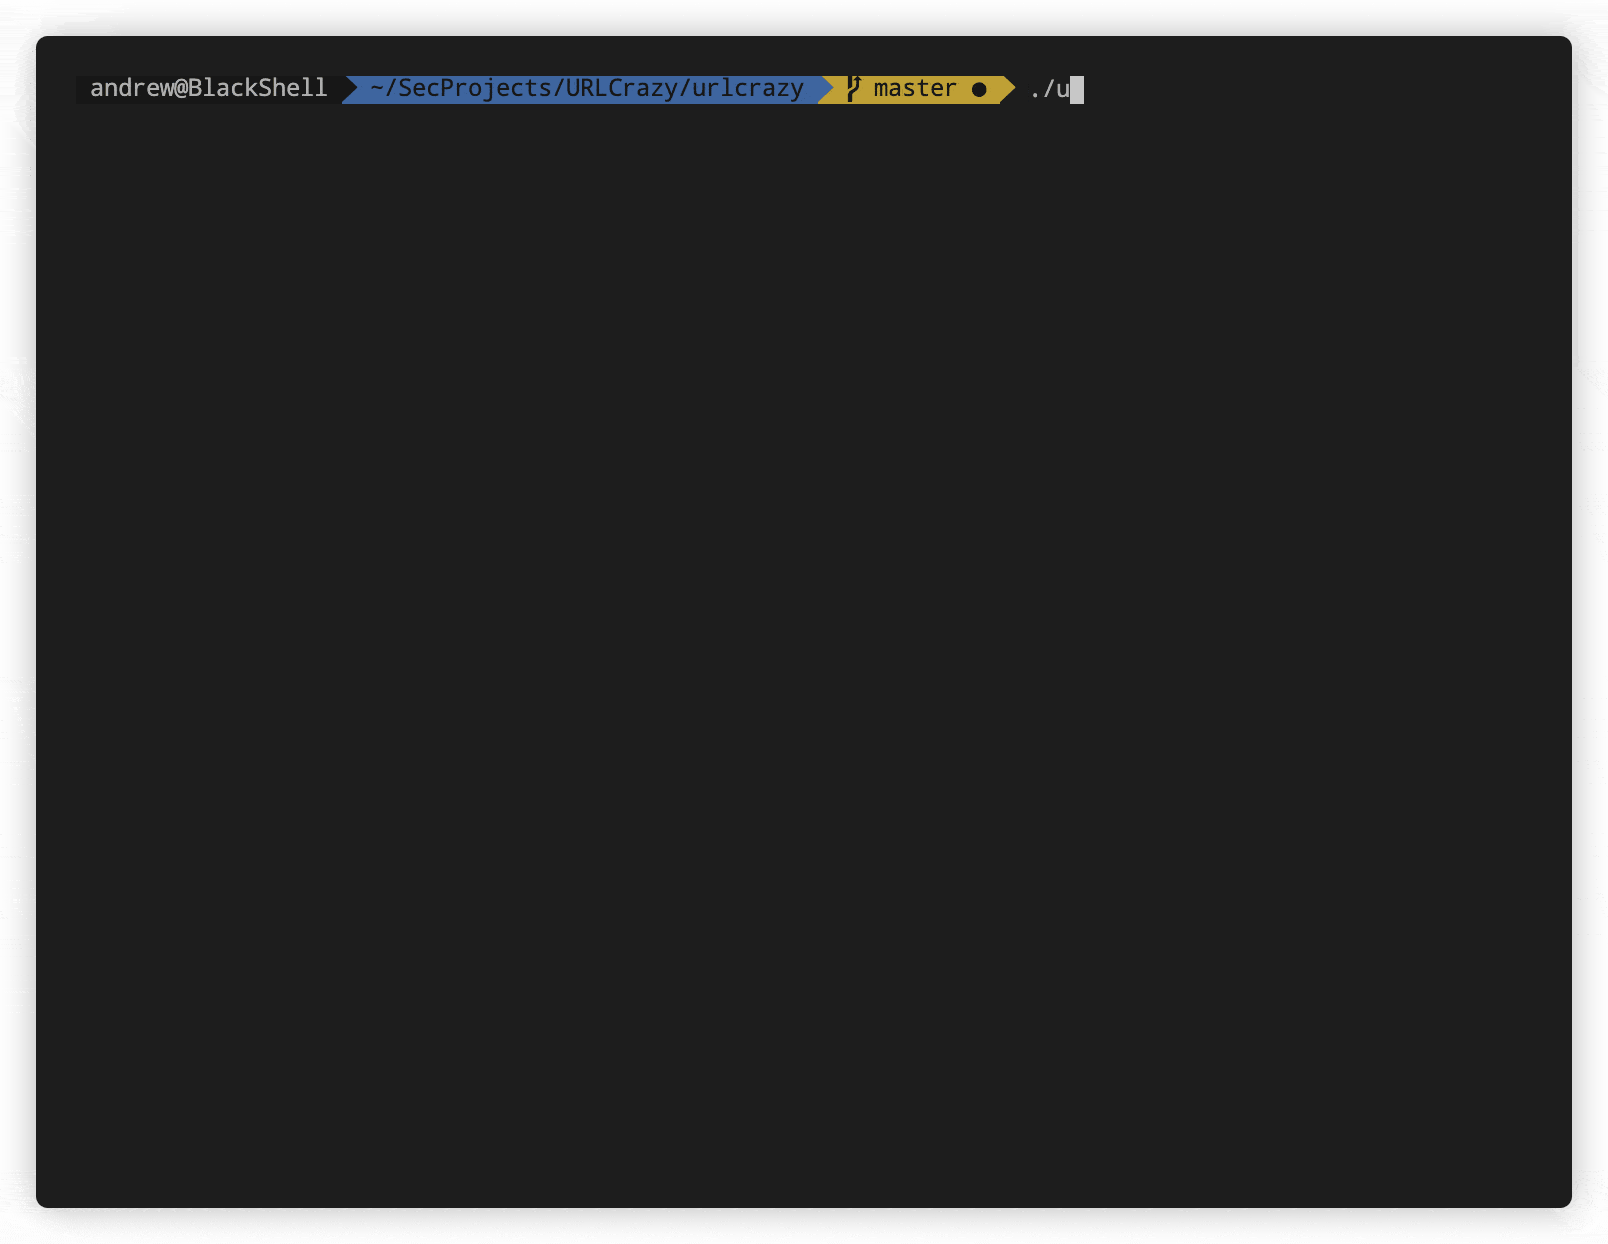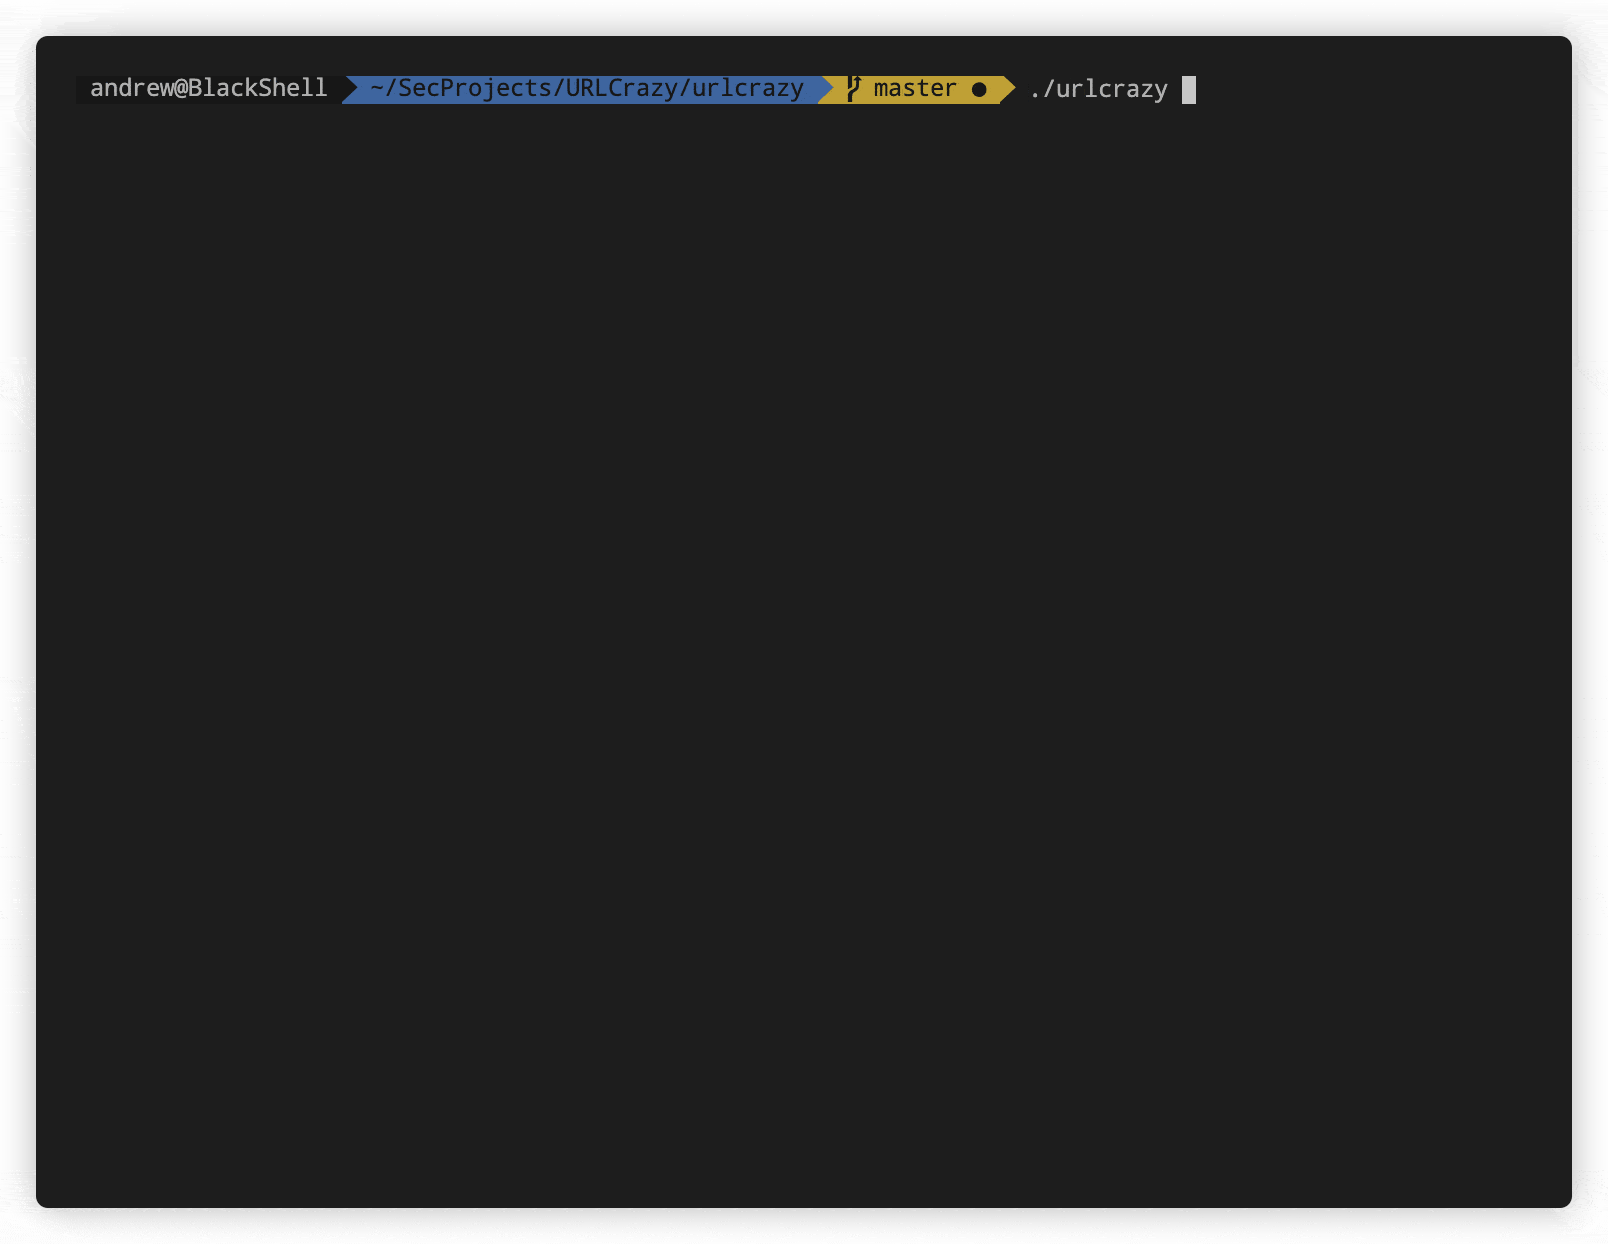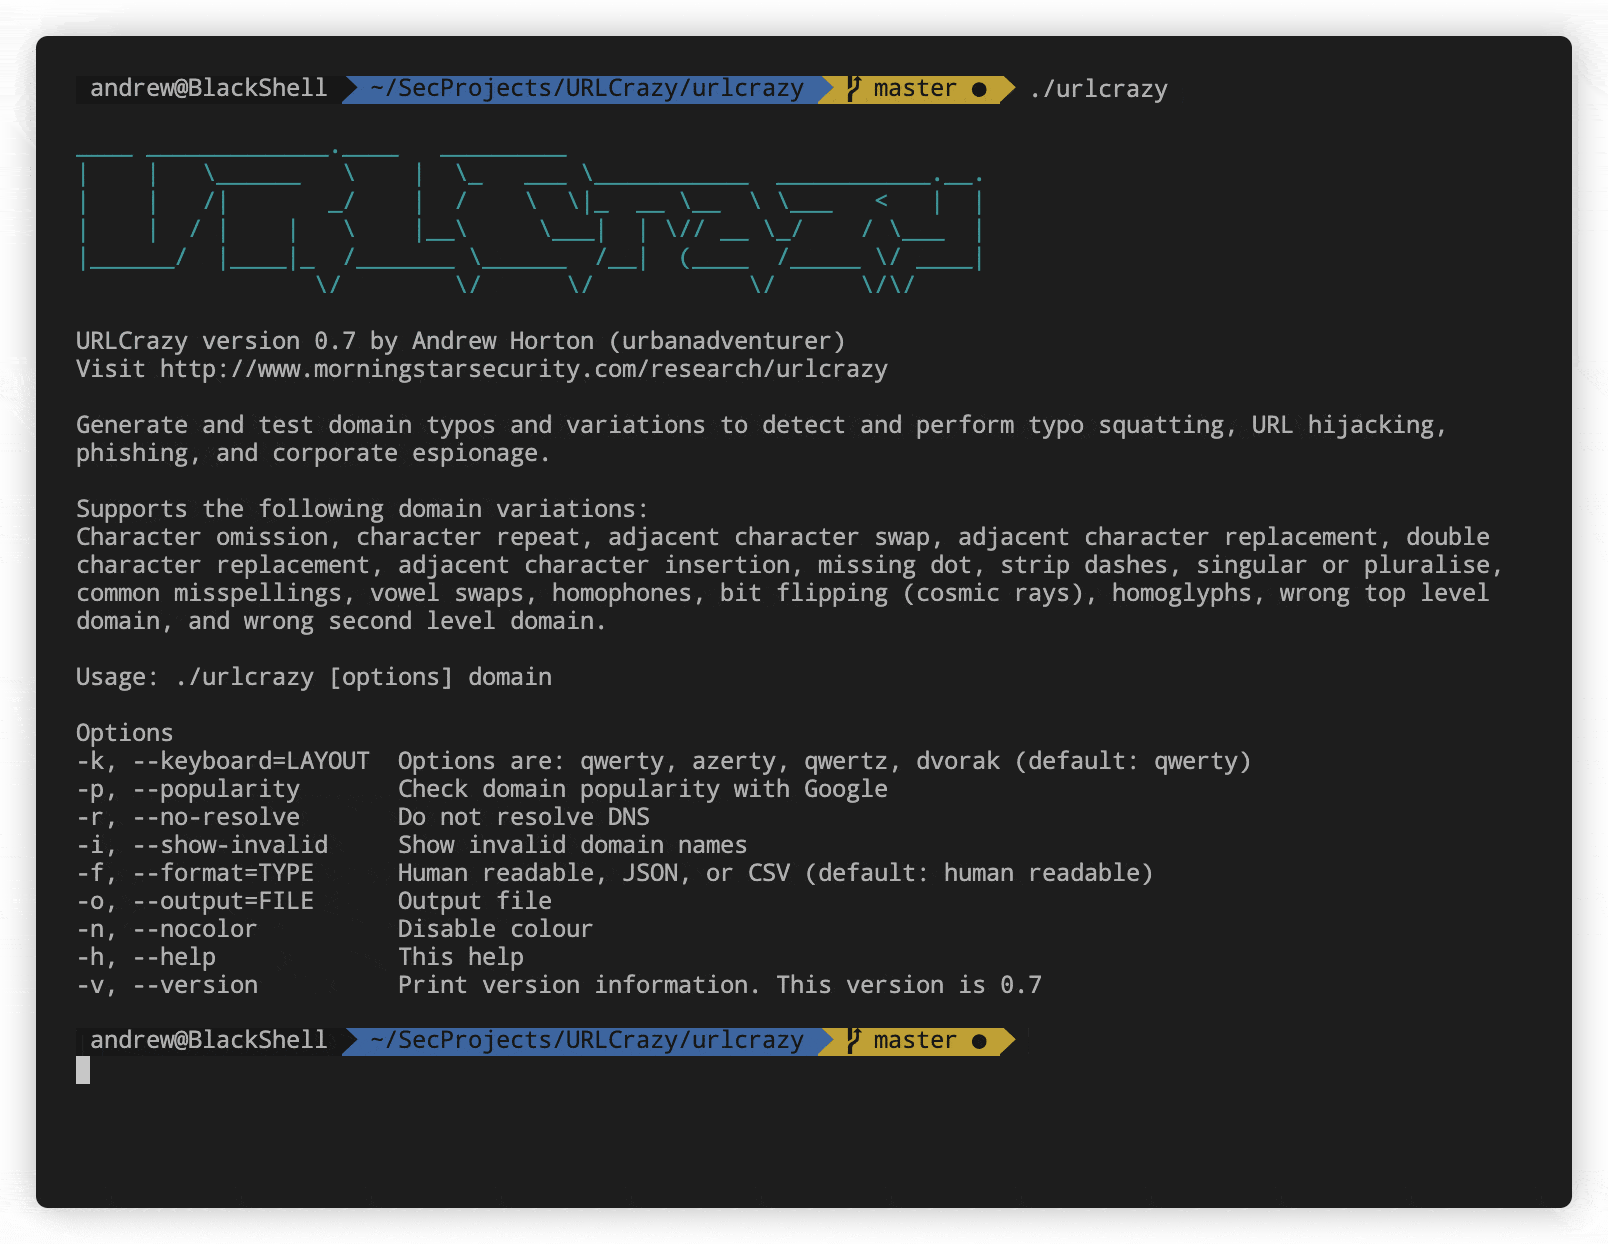 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
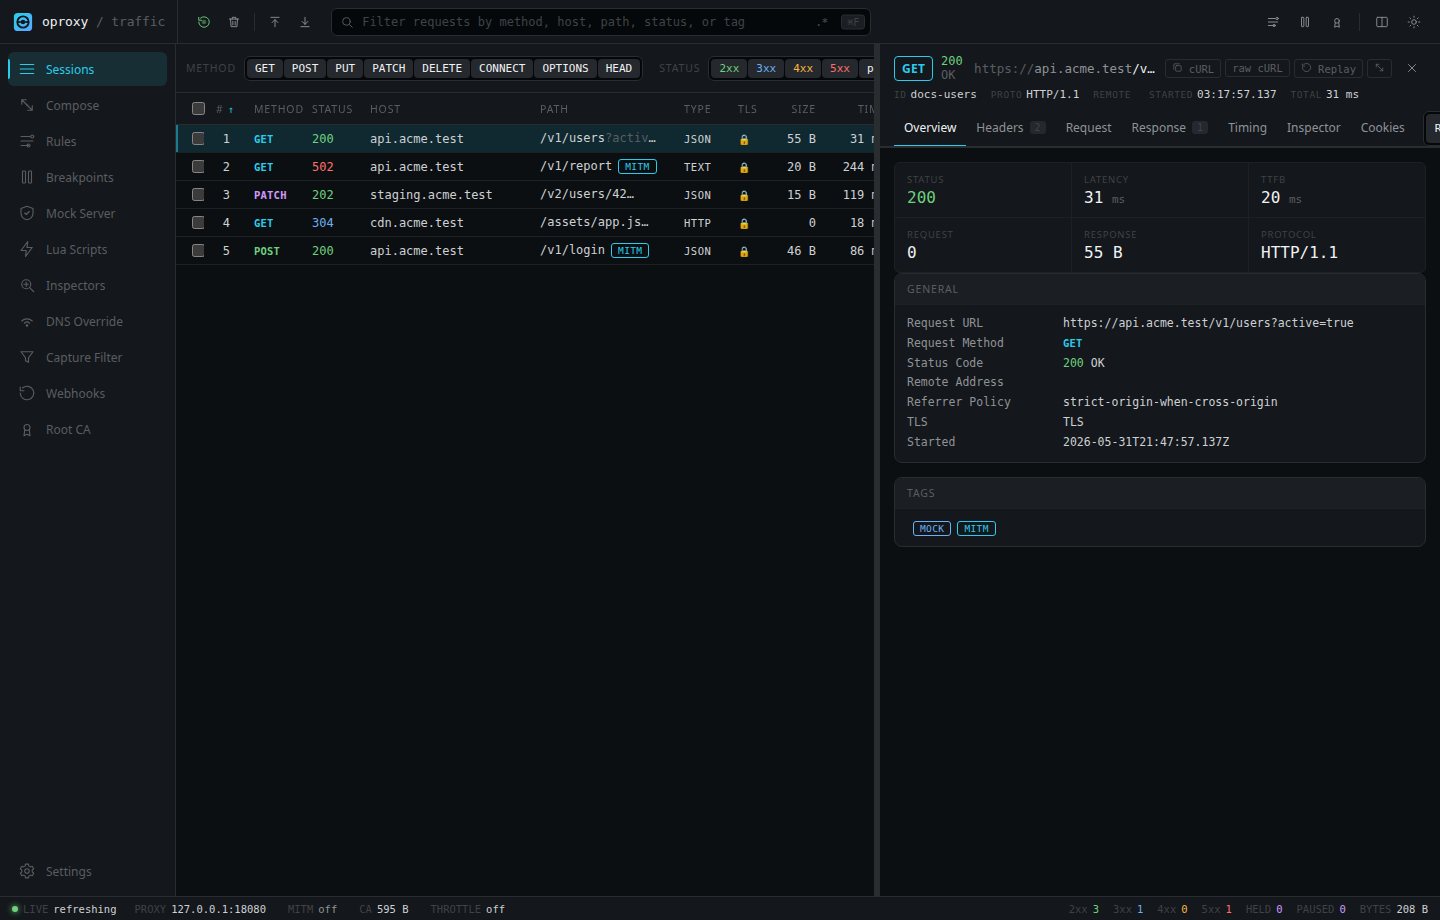 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 ank1036official/cloudcheck
Checks using a test string if a Cloudflare DNS bypass is possible using CloudFail.