
Recon-Scan
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
ai-securitydns-analysisdns-subdomain-enumeration+6
7
aarocy/recon-scanRecon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
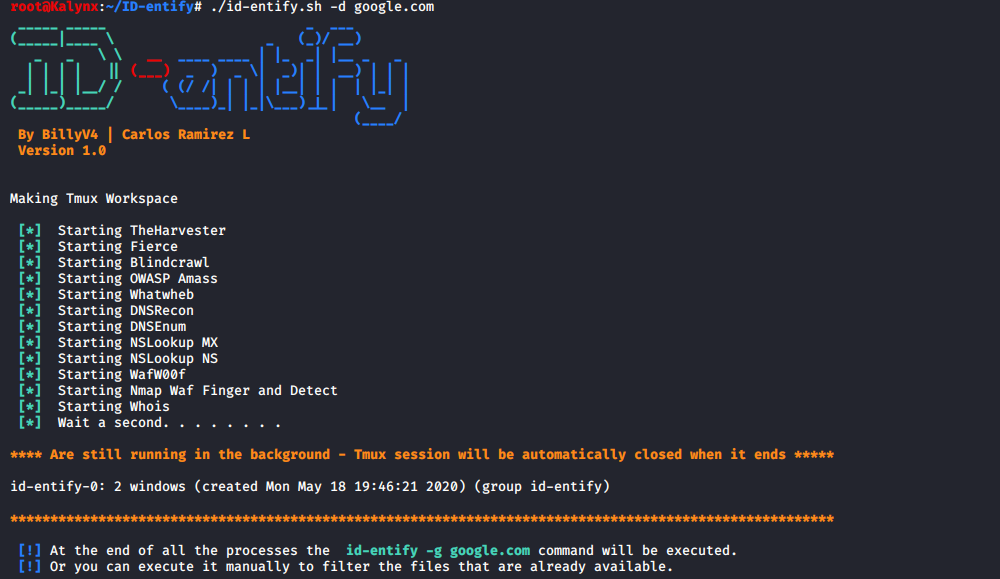 billyv4/id-entify
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…

 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 guelfoweb/knockpy
Knock Subdomain Scan
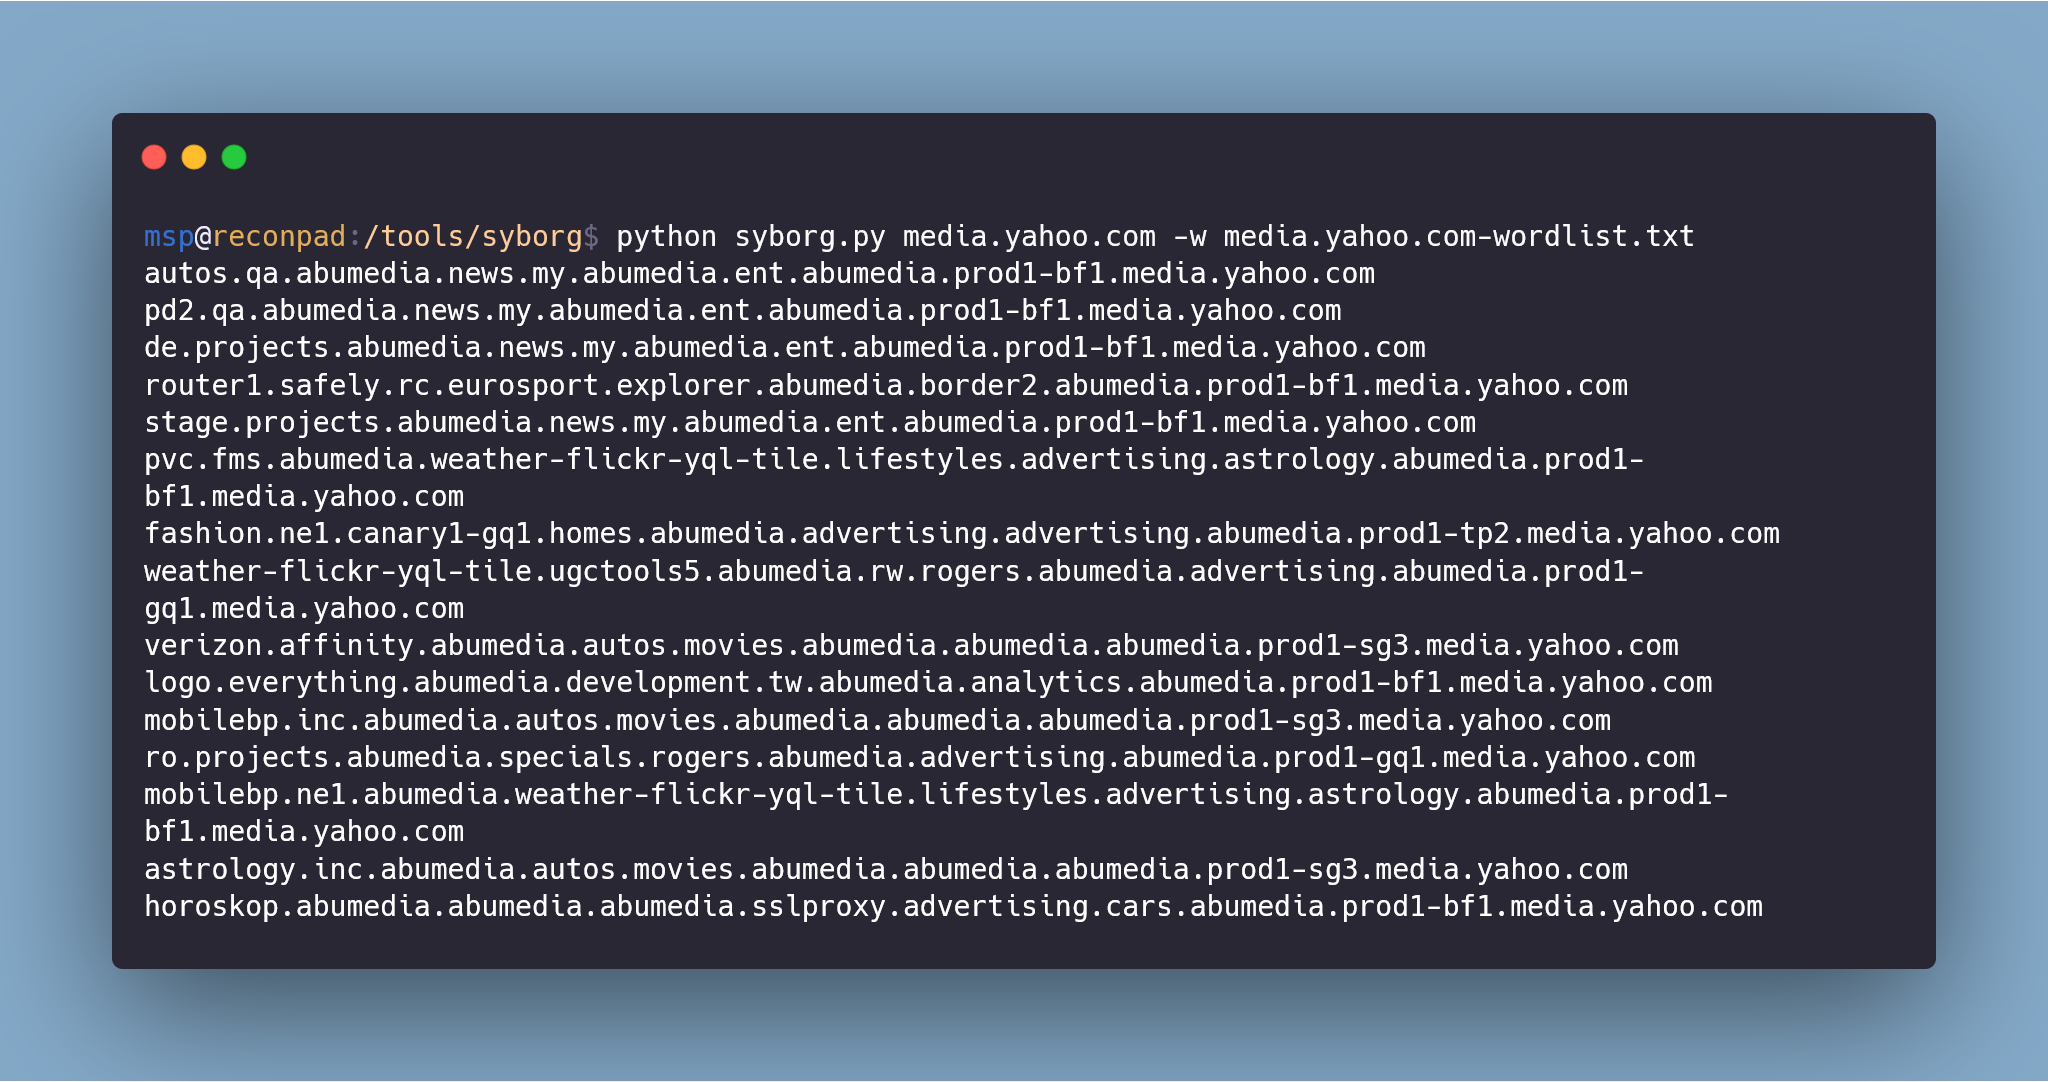 milindpurswani/syborg
Recursive DNS Subdomain Enumerator with dead-end avoidance system (BETA)
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
