
log4shell-tools
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
dns-analysisexploitationpenetration-testing+3
86
alexbakker/log4shell-toolsTool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
 jeromeyoung/log4j2burpscanner
CVE-2021-44228,log4j2 burp插件 Java版本,dnslog选取了非dnslog.cn域名
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 woahd/log4j-urlscanner
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URL with multithreading
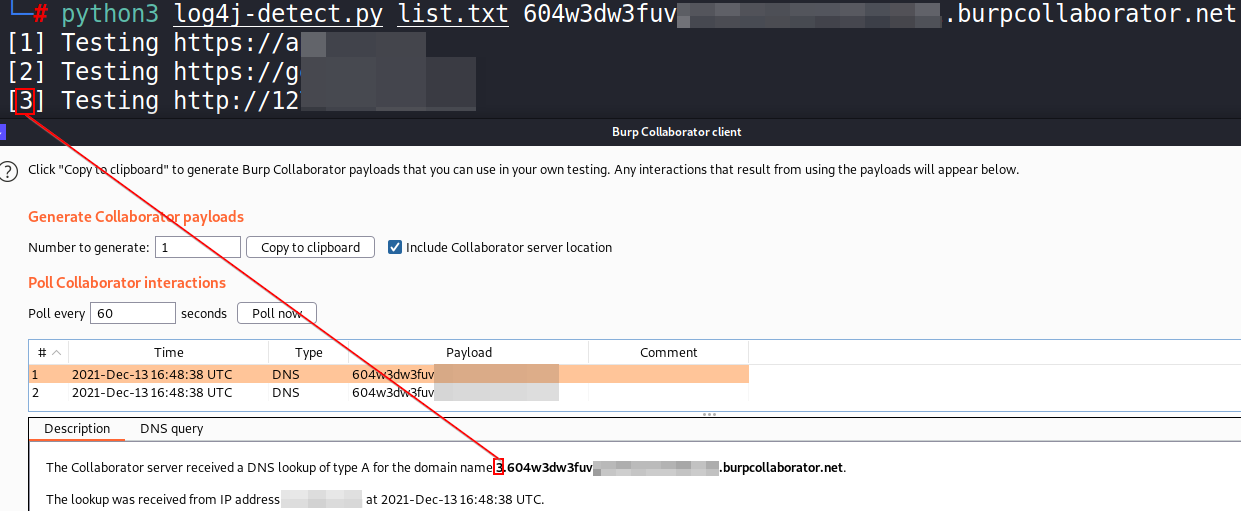 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 coolyin001/cve-2021-26295--
CVE-2021-26295-POC 利用DNSlog进行CVE-2021-26295的漏洞验证。 使用 poc:将目标放于target.txt后运行python poc.py即可。(Jdk环境需<12,否则ysoserial无法正常生成有效载荷) exp:python exp.py…
 moften/cve-2021-23017
NGINX DNS Overflow Vulnerability Check - CVE-2021-23017 PoC
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 bigsizeme/log4j-check
log4J burp被扫插件、CVE-2021-44228、支持dnclog.cn和burp内置DNS、可配合JNDIExploit生成payload