
rapidscan
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
dns-analysisinformation-gatheringpenetration-testing+5
skavngr/rapidscan:new: The Multi-Tool Web Vulnerability Scanner.
 adilsoybali/log4j-rce-scanner
Remote command execution vulnerability scanner for Log4j.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
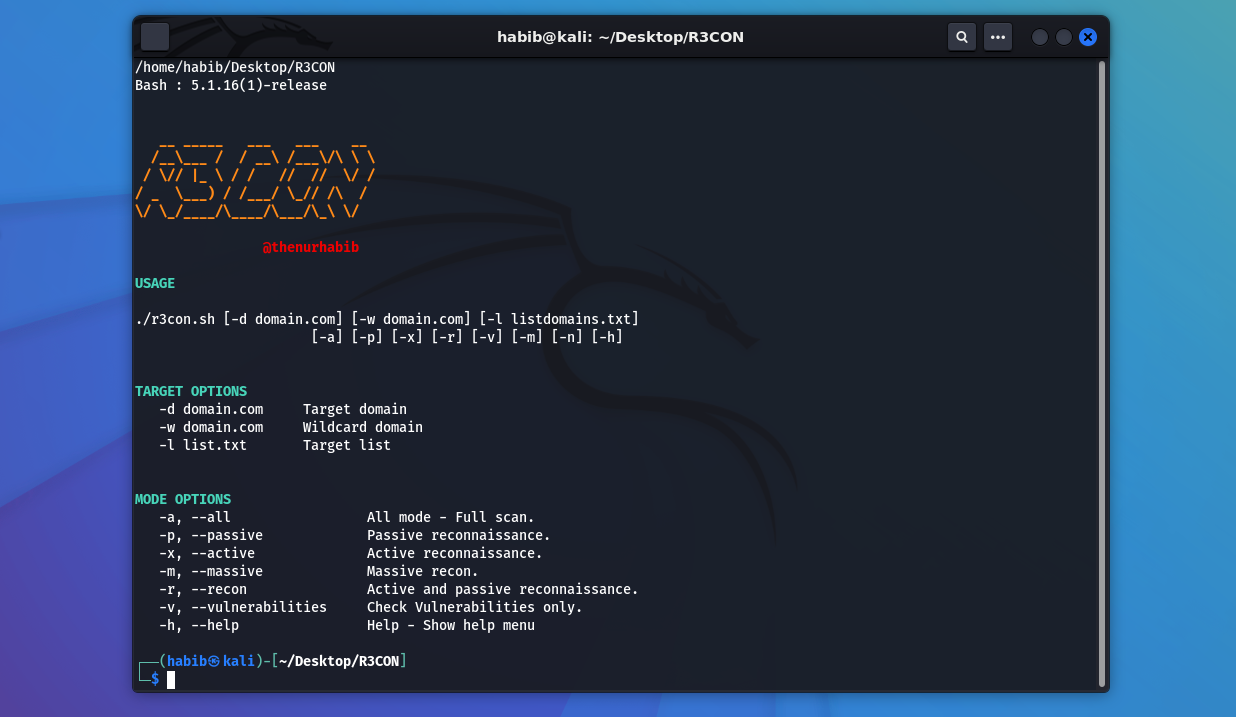 thenurhabib/r3con
Multi-functional Web Recon & Vulnerability Scanner Tool
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
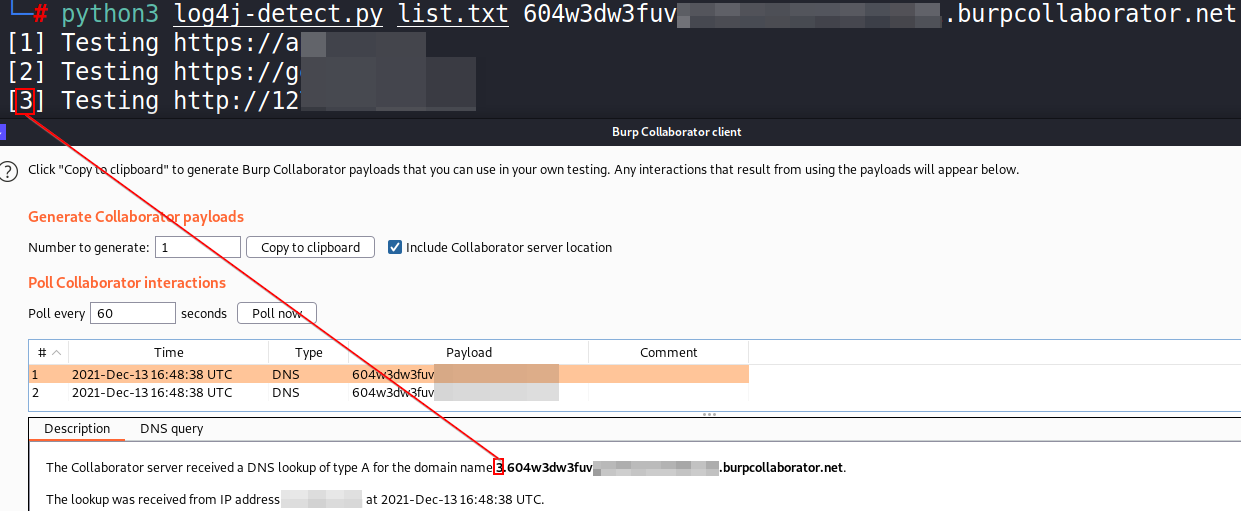 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 pwnesia/dnstake
Fast DNS takeover scanner that checks for missing hosted zones by querying nameservers and fingerprinting providers to identify vulnerable subdomains.
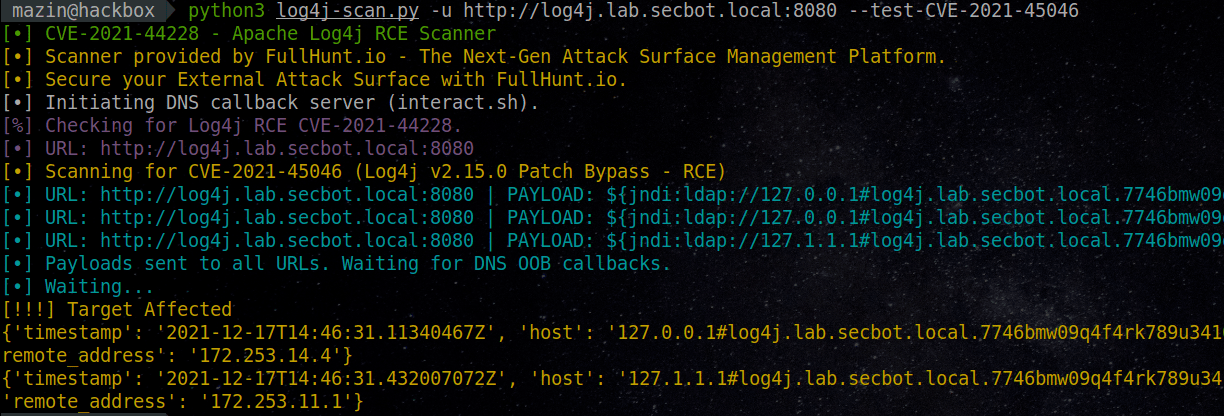 fullhunt/log4j-scan
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
 haccer/subjack
Concurrent DNS takeover scanner detecting CNAME, NS, AXFR, SPF, MX, SRV, and stale A record vulnerabilities across cloud providers, with multi-level…
 eilam-cell/cve-test-coredns-fork
Plan v3 US-6: coredns-style fork fixture for Scanner E2E (CVE-2023-39325)
 moften/cve-2021-23017
NGINX DNS Overflow Vulnerability Check - CVE-2021-23017 PoC
 whitespots/fast-security-scanners
Security checks for your researches
 f0ng/log4j2burpscanner
CVE-2021-44228 Log4j2 BurpSuite Scanner,Customize ceye.io api or other apis,including internal networks
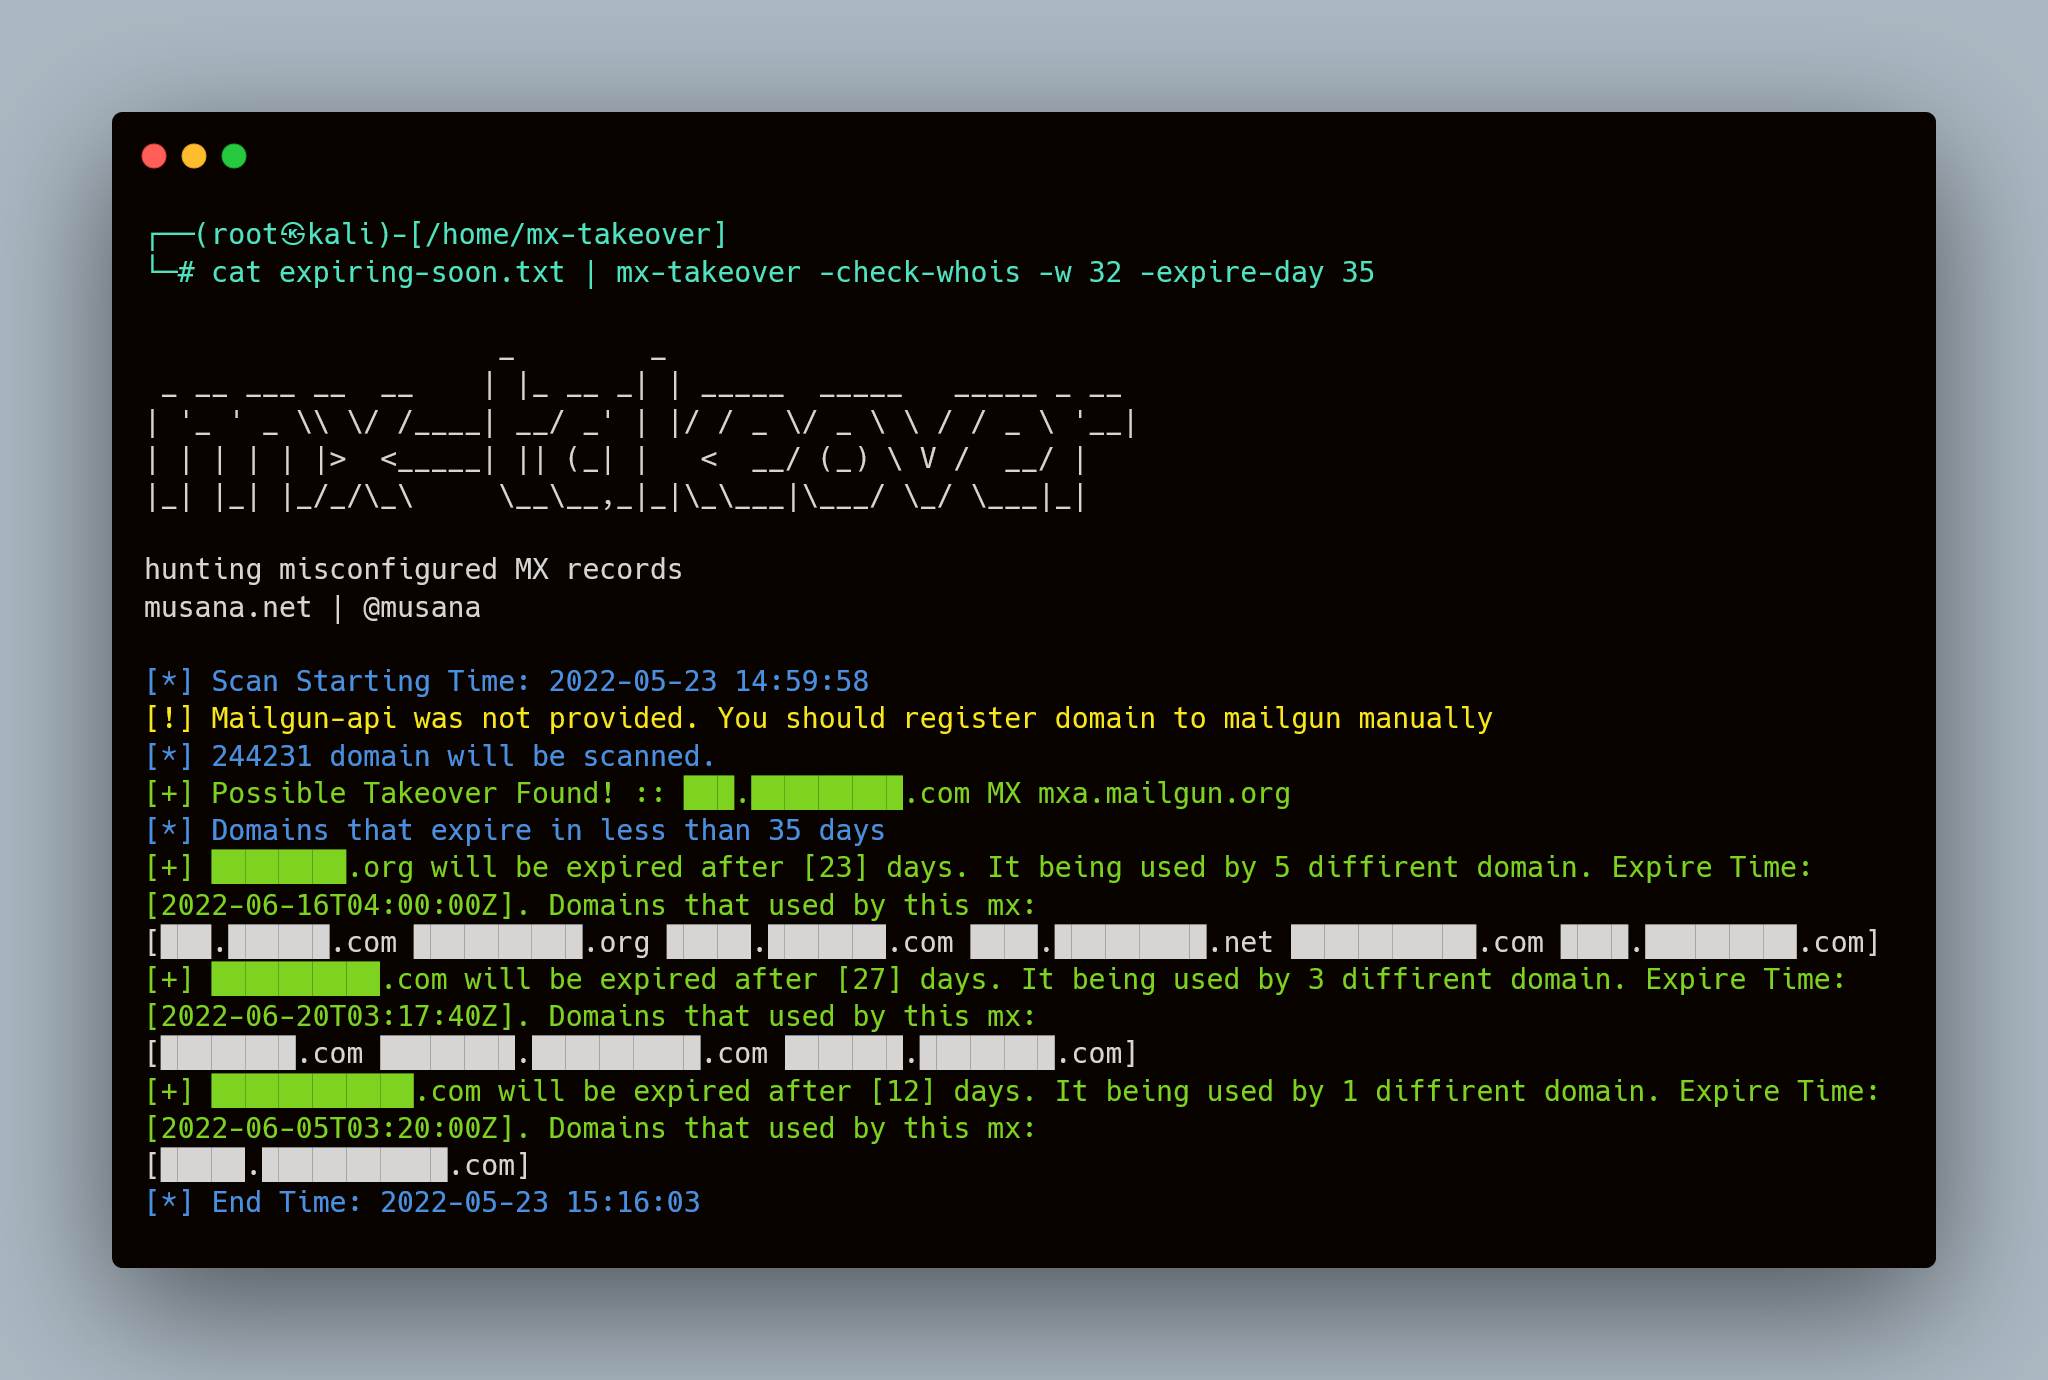 musana/mx-takeover
Scans DNS MX records to detect misconfigured, expiring, or unregistered domains vulnerable to email takeover, with automatic reclamation support for…
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046