
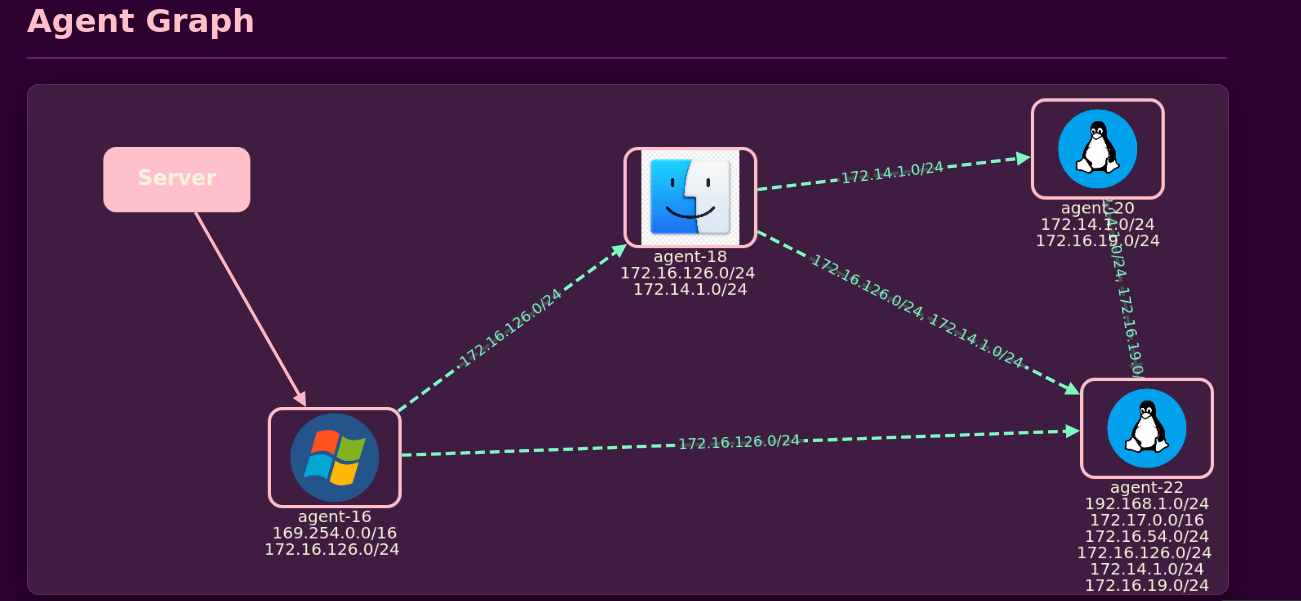
rosemary
 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
command-and-controldns-analysislateral-movement+4
123 months ago
blue0x1/rosemaryRosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 gar-re/cve-2022-24644
Proof-of-concept exploit for CVE-2022-24644, demonstrating unauthenticated remote code execution via DNS spoofing against KeyMouse Windows 3.08…
 coolyin001/cve-2021-26295--
CVE-2021-26295-POC 利用DNSlog进行CVE-2021-26295的漏洞验证。 使用 poc:将目标放于target.txt后运行python poc.py即可。(Jdk环境需<12,否则ysoserial无法正常生成有效载荷) exp:python exp.py…
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
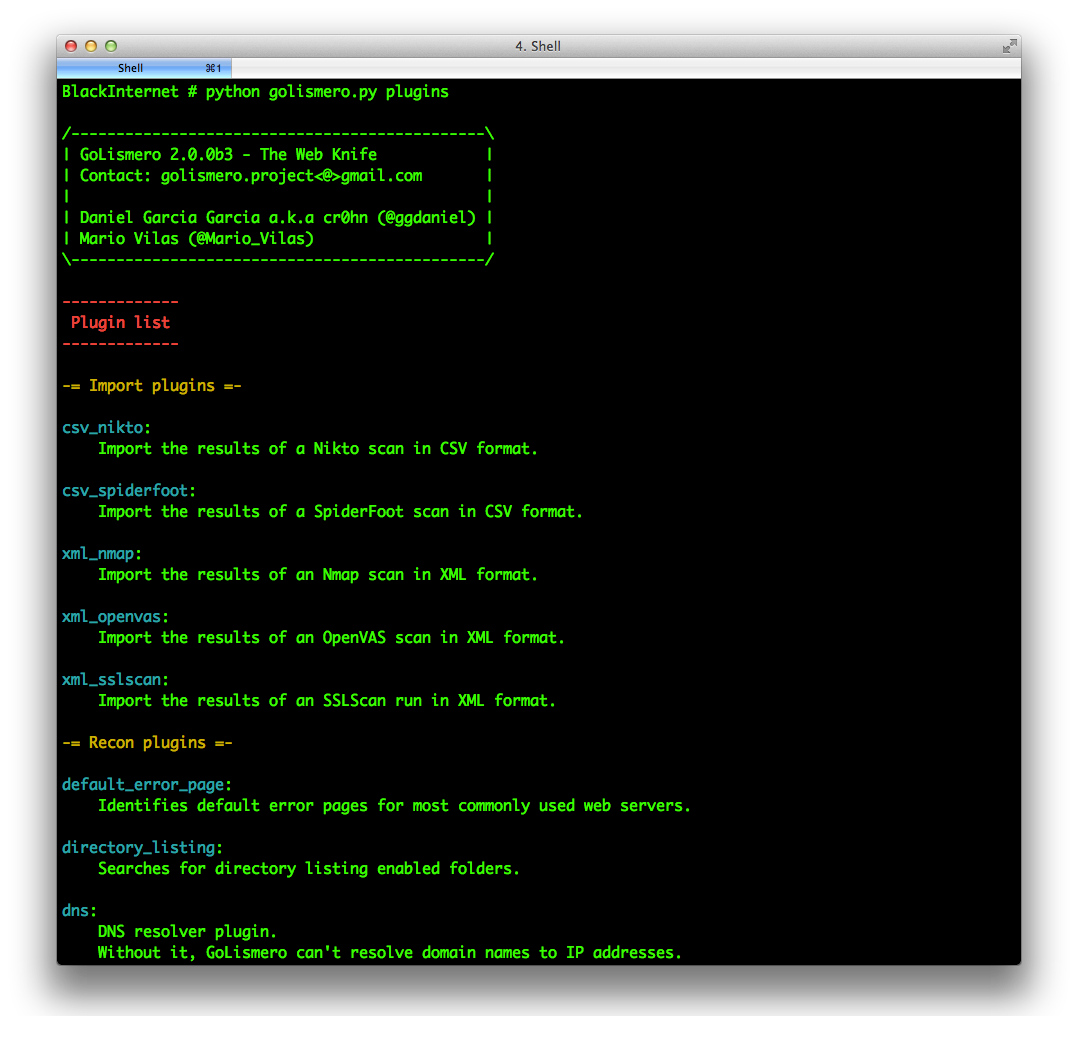 golismero/golismero
GoLismero - The Web Knife
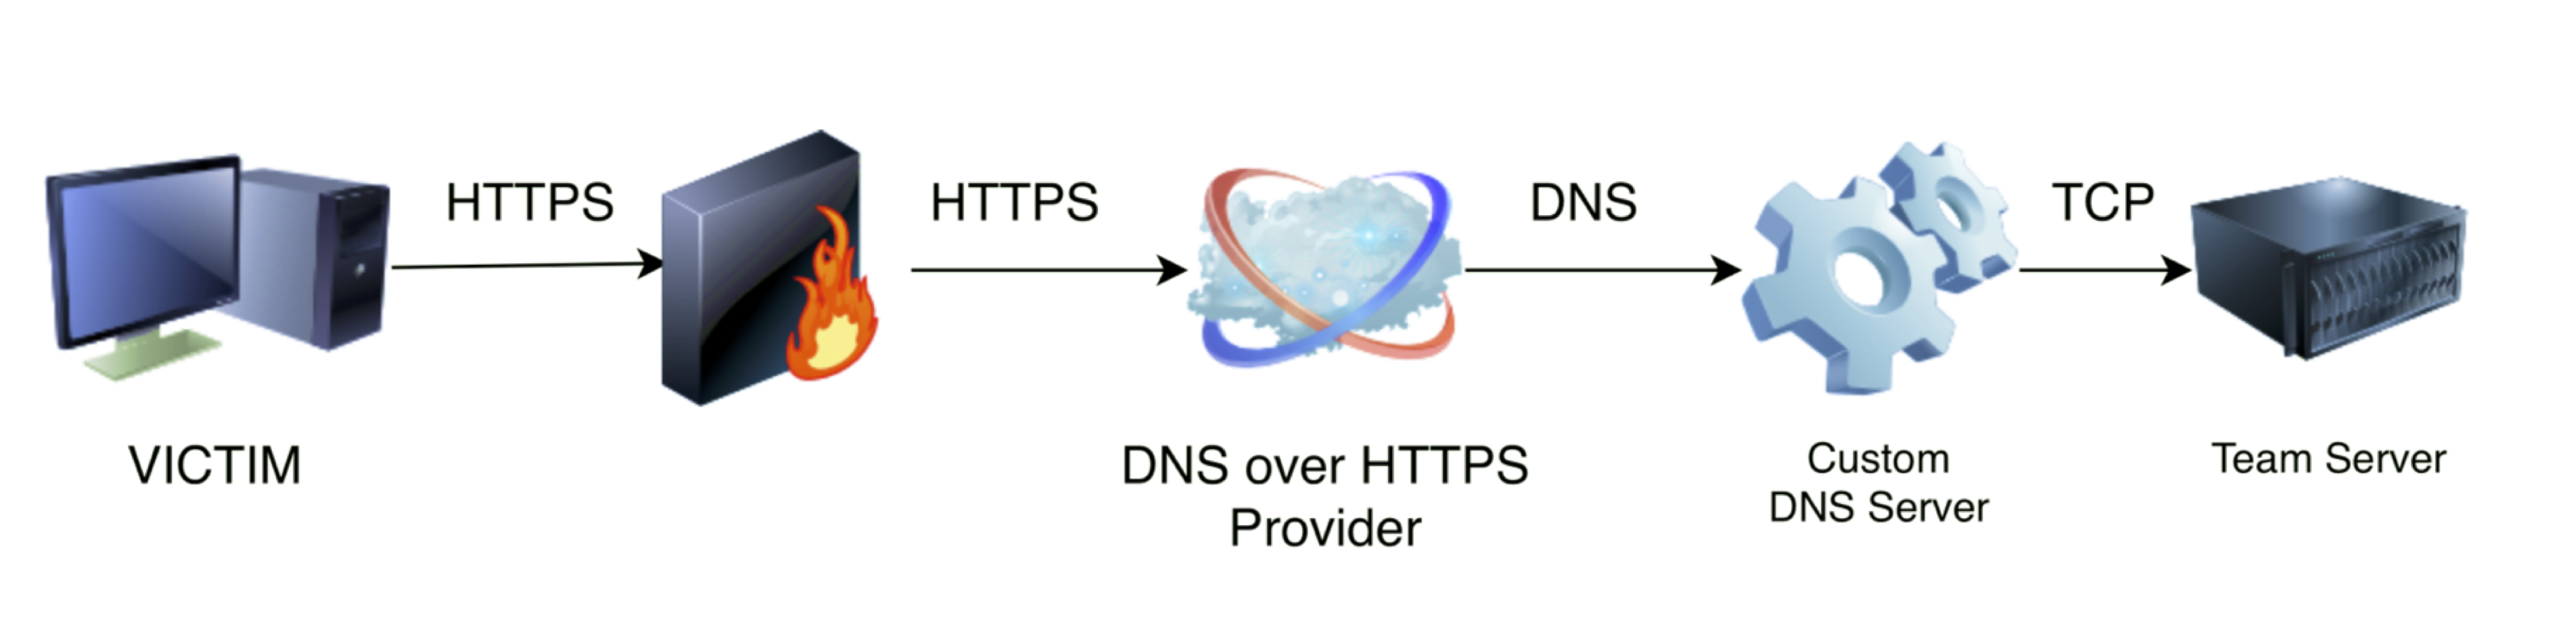 spiderlabs/dohc2
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
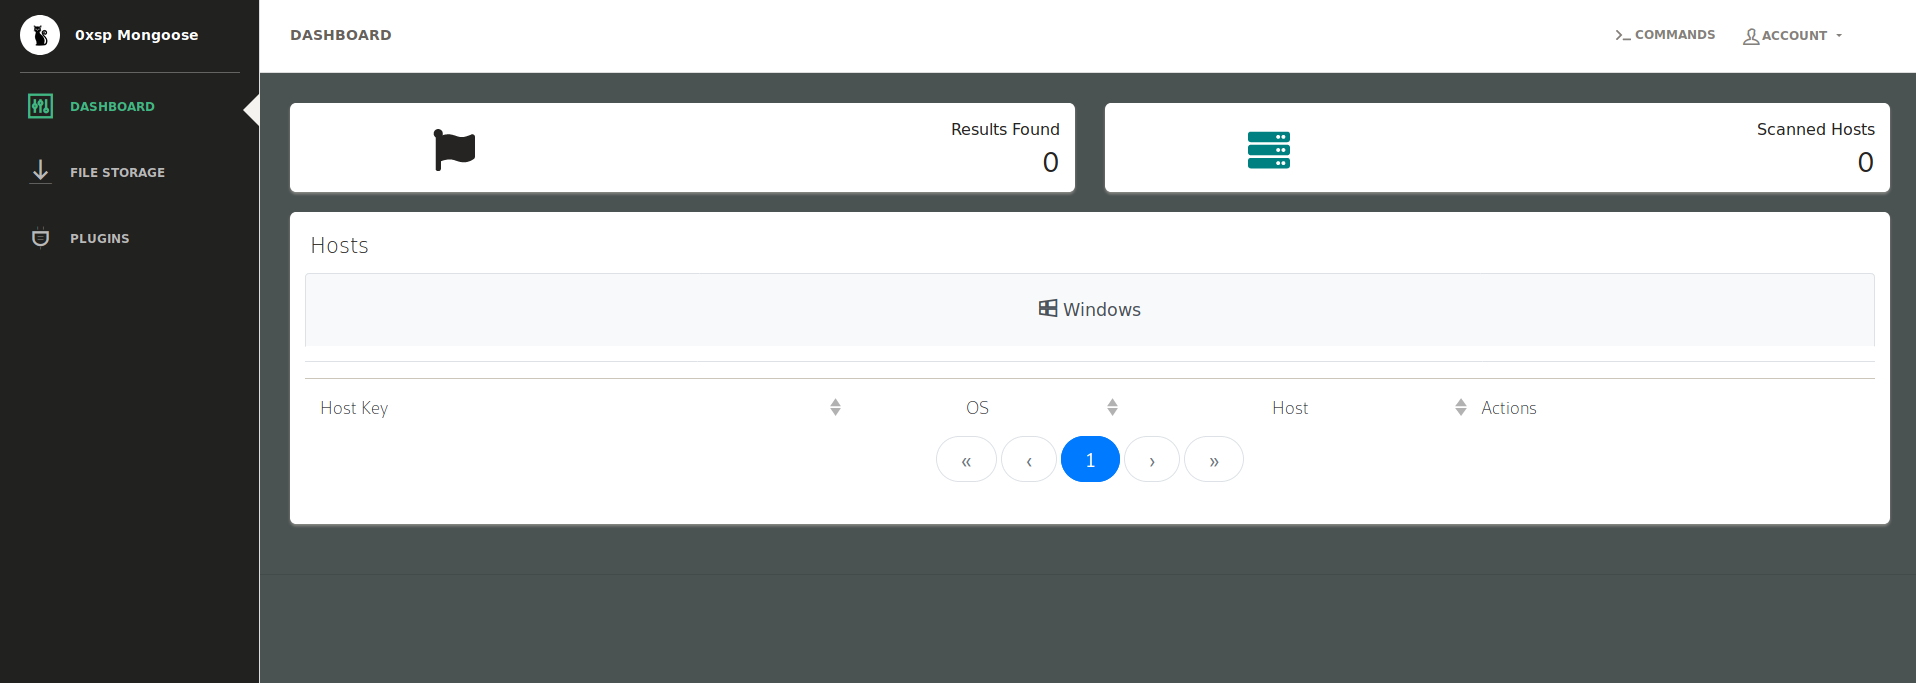 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 facebookarchive/weasel
DNS covert channel implant for Red Teams.
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.