

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
30.4k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 bromite/bromite
Android Chromium fork with built-in ad blocking, anti-fingerprinting mitigations, DNS-over-HTTPS, and hardened privacy and security defaults.
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
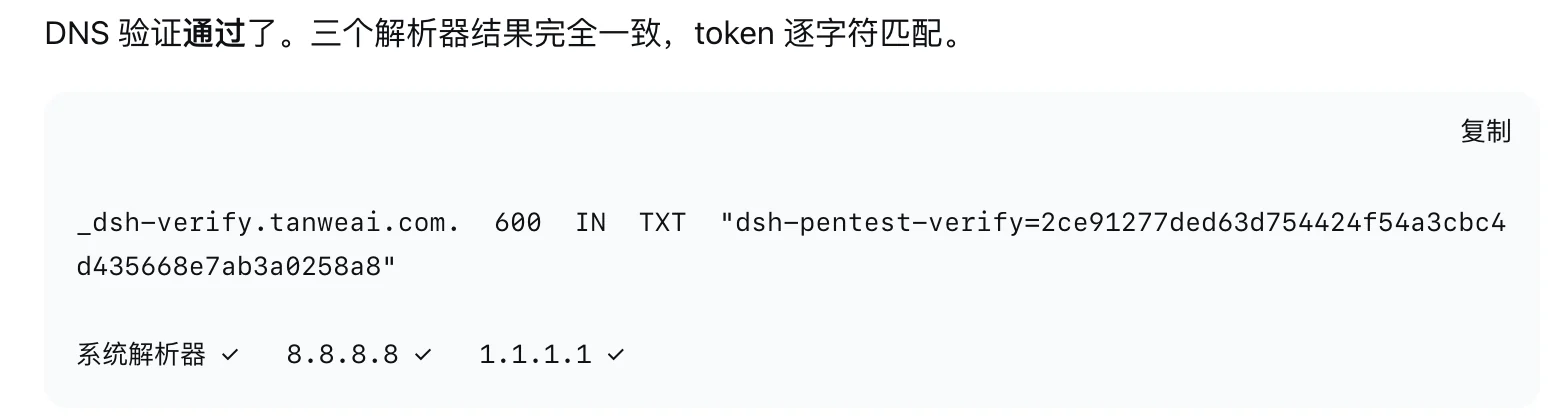 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
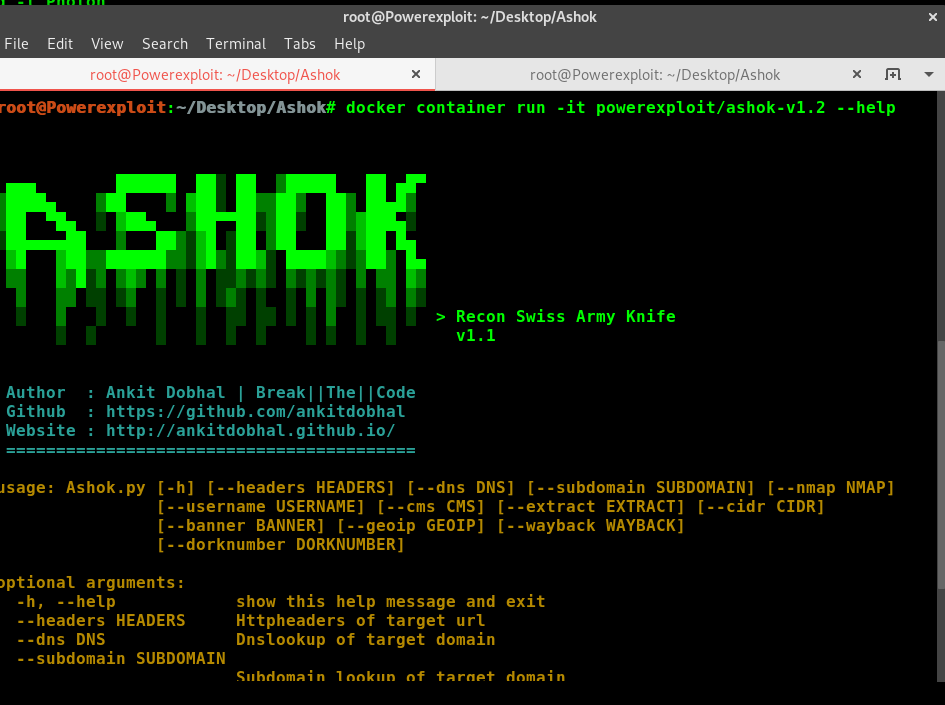 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
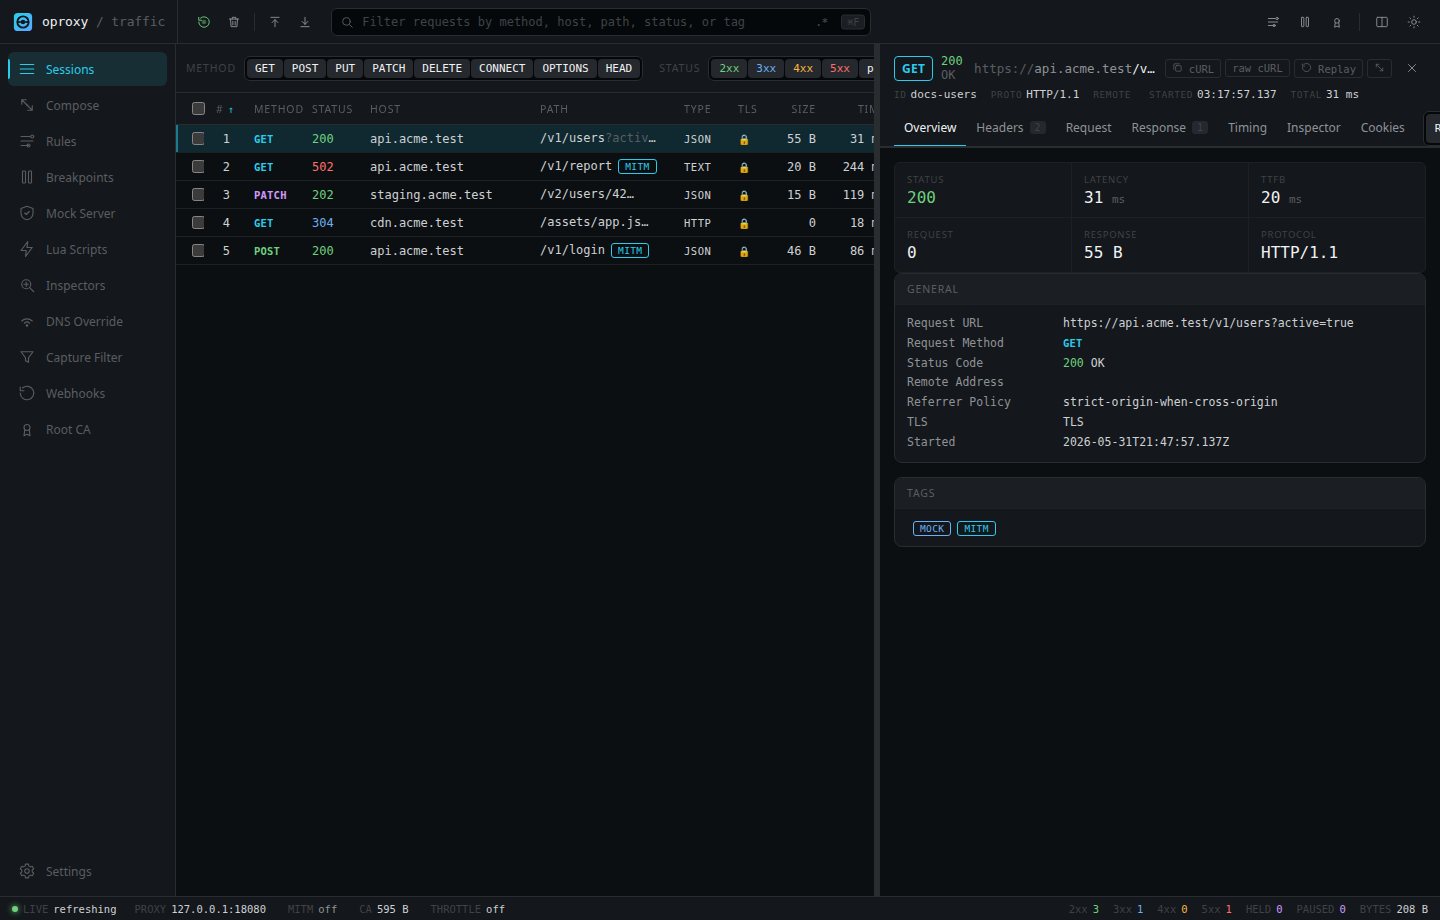 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
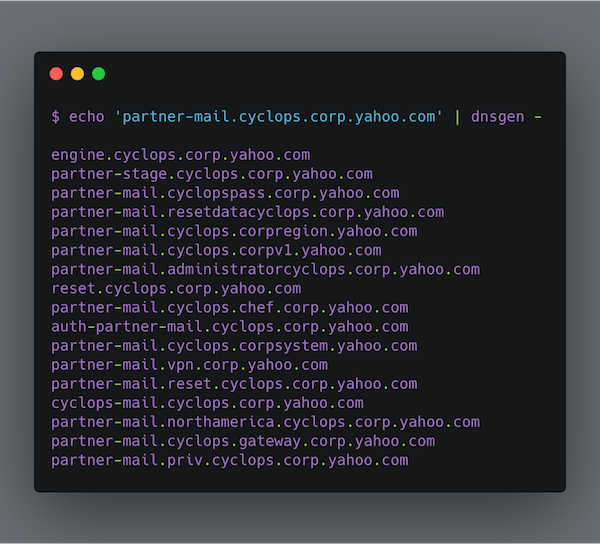 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 taviso/rbndr
Simple DNS Rebinding Service
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.