awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Free hands-on digital forensics labs for students and faculty

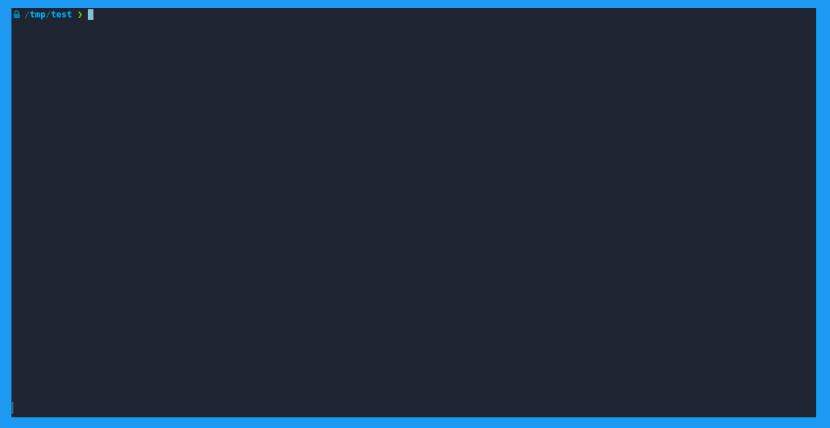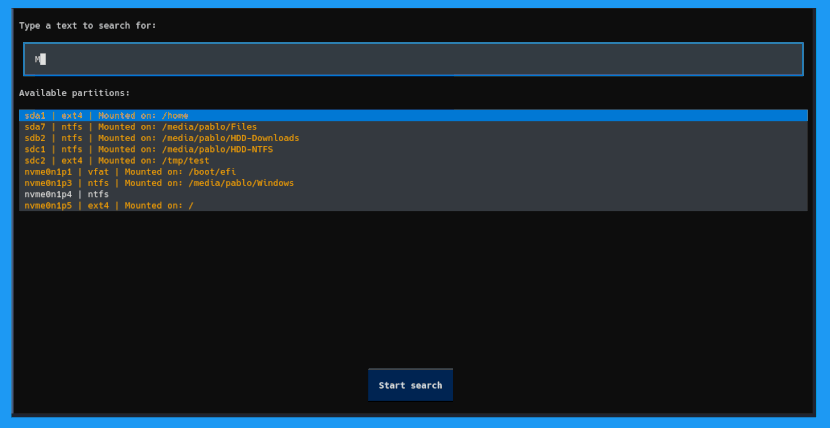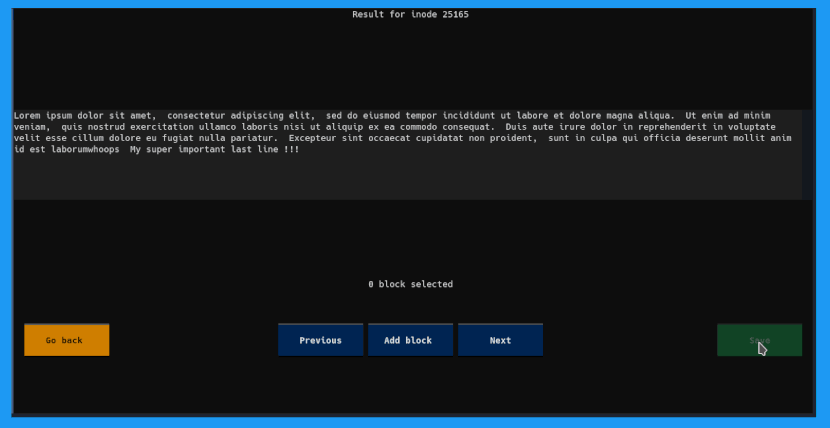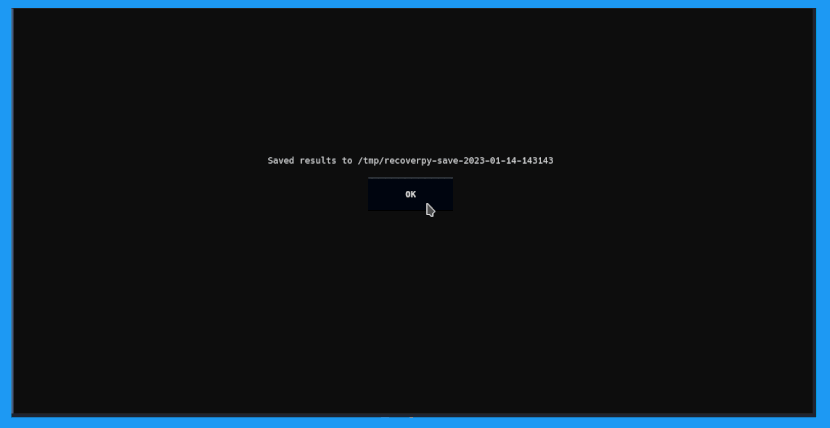
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.

A list of cyber-chef recipes and curated links

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

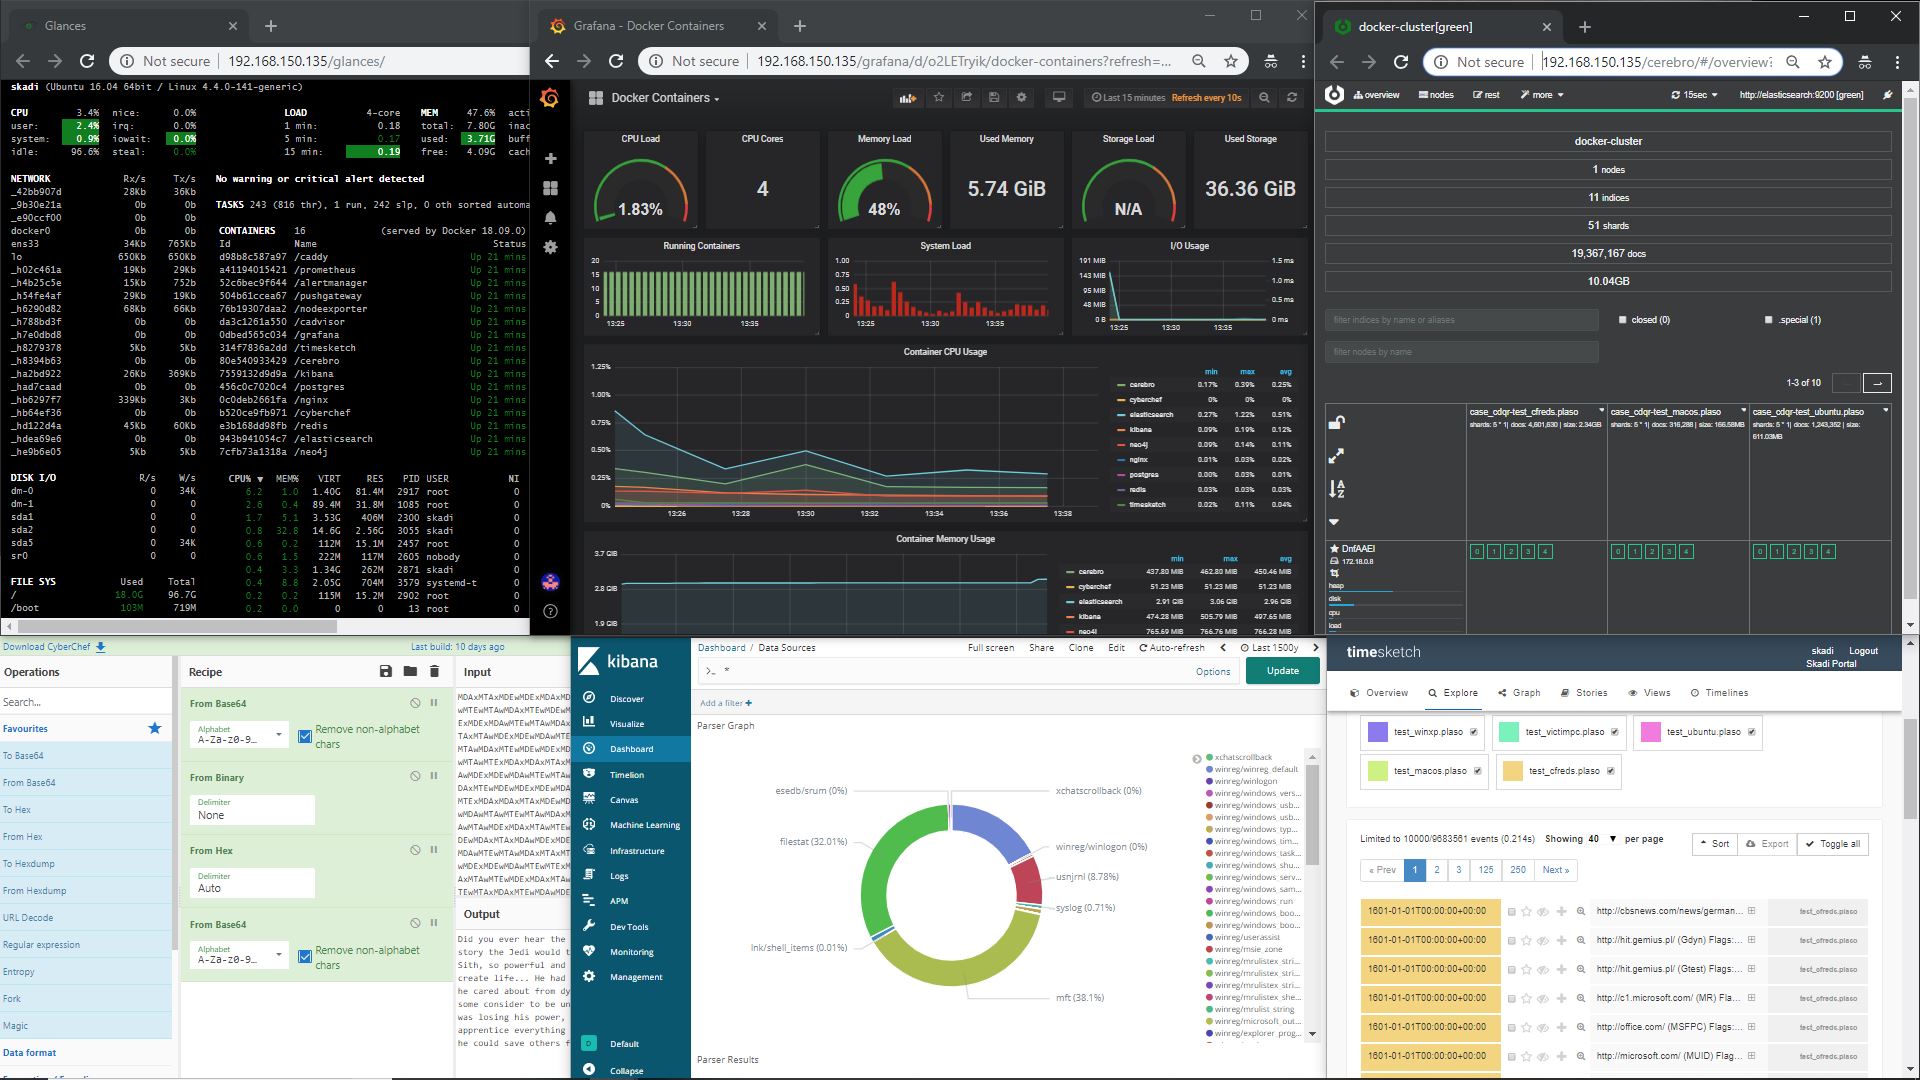
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux