

grr
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
google/grrRemote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
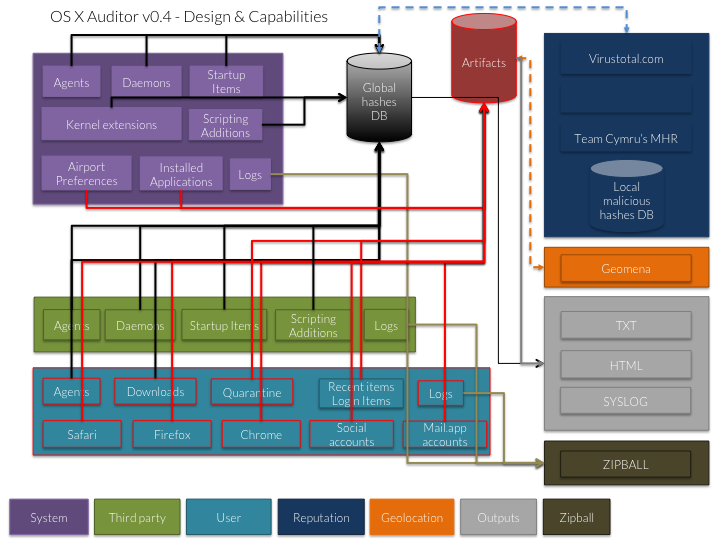 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
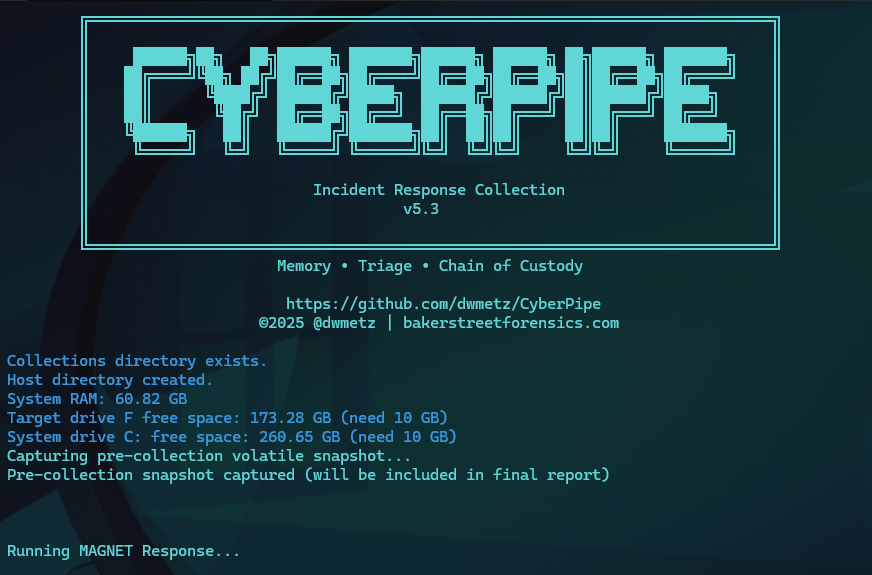 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
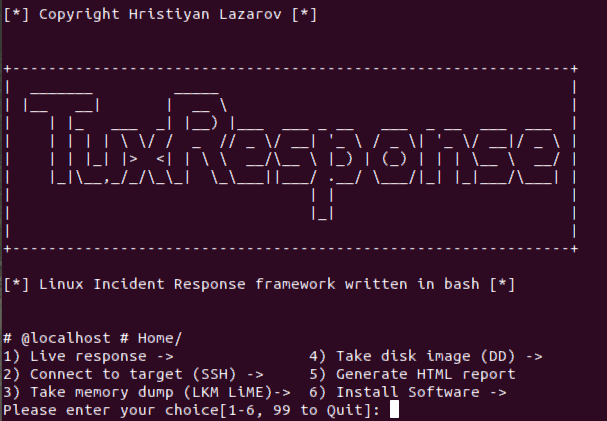 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…


 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud