Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…


Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…


IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

Collection of forensic tools

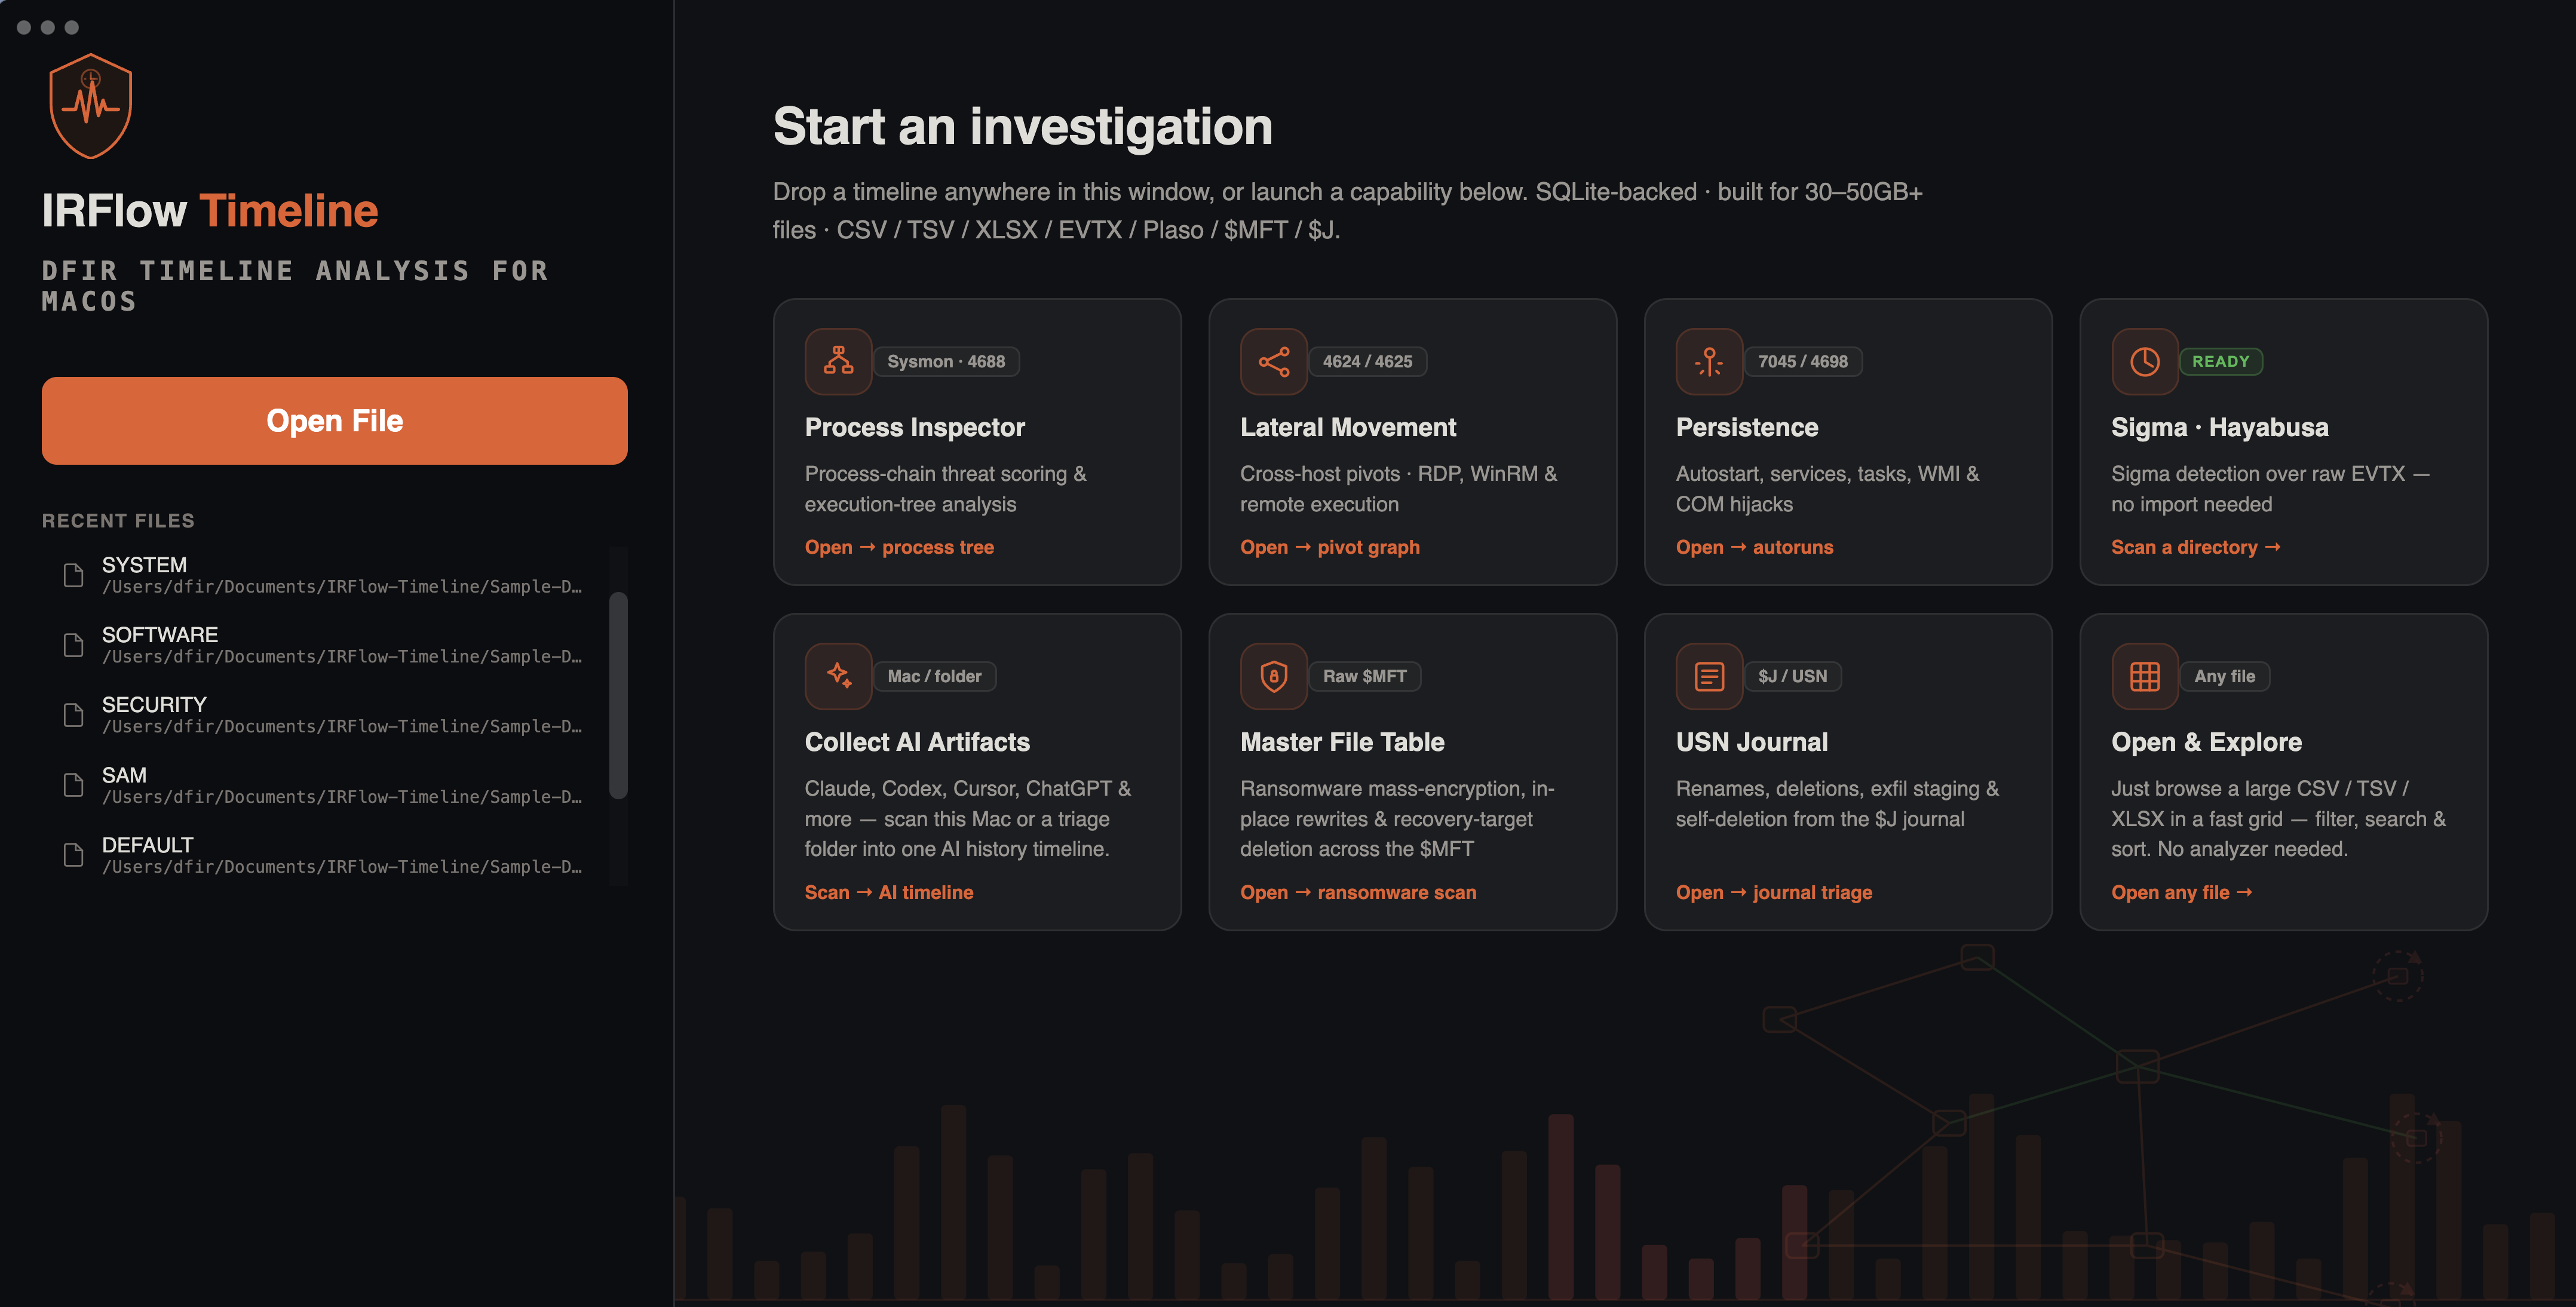
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

Free hands-on digital forensics labs for students and faculty

FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.