

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
sleuthkit preview

sleuthkit

GitHubsleuthkit/sleuthkit

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
data-recoverydigital-forensicsdisk-forensics+3
3.2k
1 day ago
RecuperaBit preview

RecuperaBit

GitHublazza/recuperabit

A tool for forensic file system reconstruction.
data-recoverydigital-forensicsdisk-forensics+1
6242 months ago
Disk-Arbitrator preview

Disk-Arbitrator

GitHubaburgh/disk-arbitrator

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
data-recoverydigital-forensicsdisk-forensics+2
7161 year ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)
data-recoverydigital-forensicsdisk-forensics+1
23916 days ago
ffs preview

ffs

GitHubdmtrkovalenko/ffs

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry

data-recoverydigital-forensicsdisk-forensics+3
2003 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
856 months ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5165 years ago
RawHive preview

RawHive

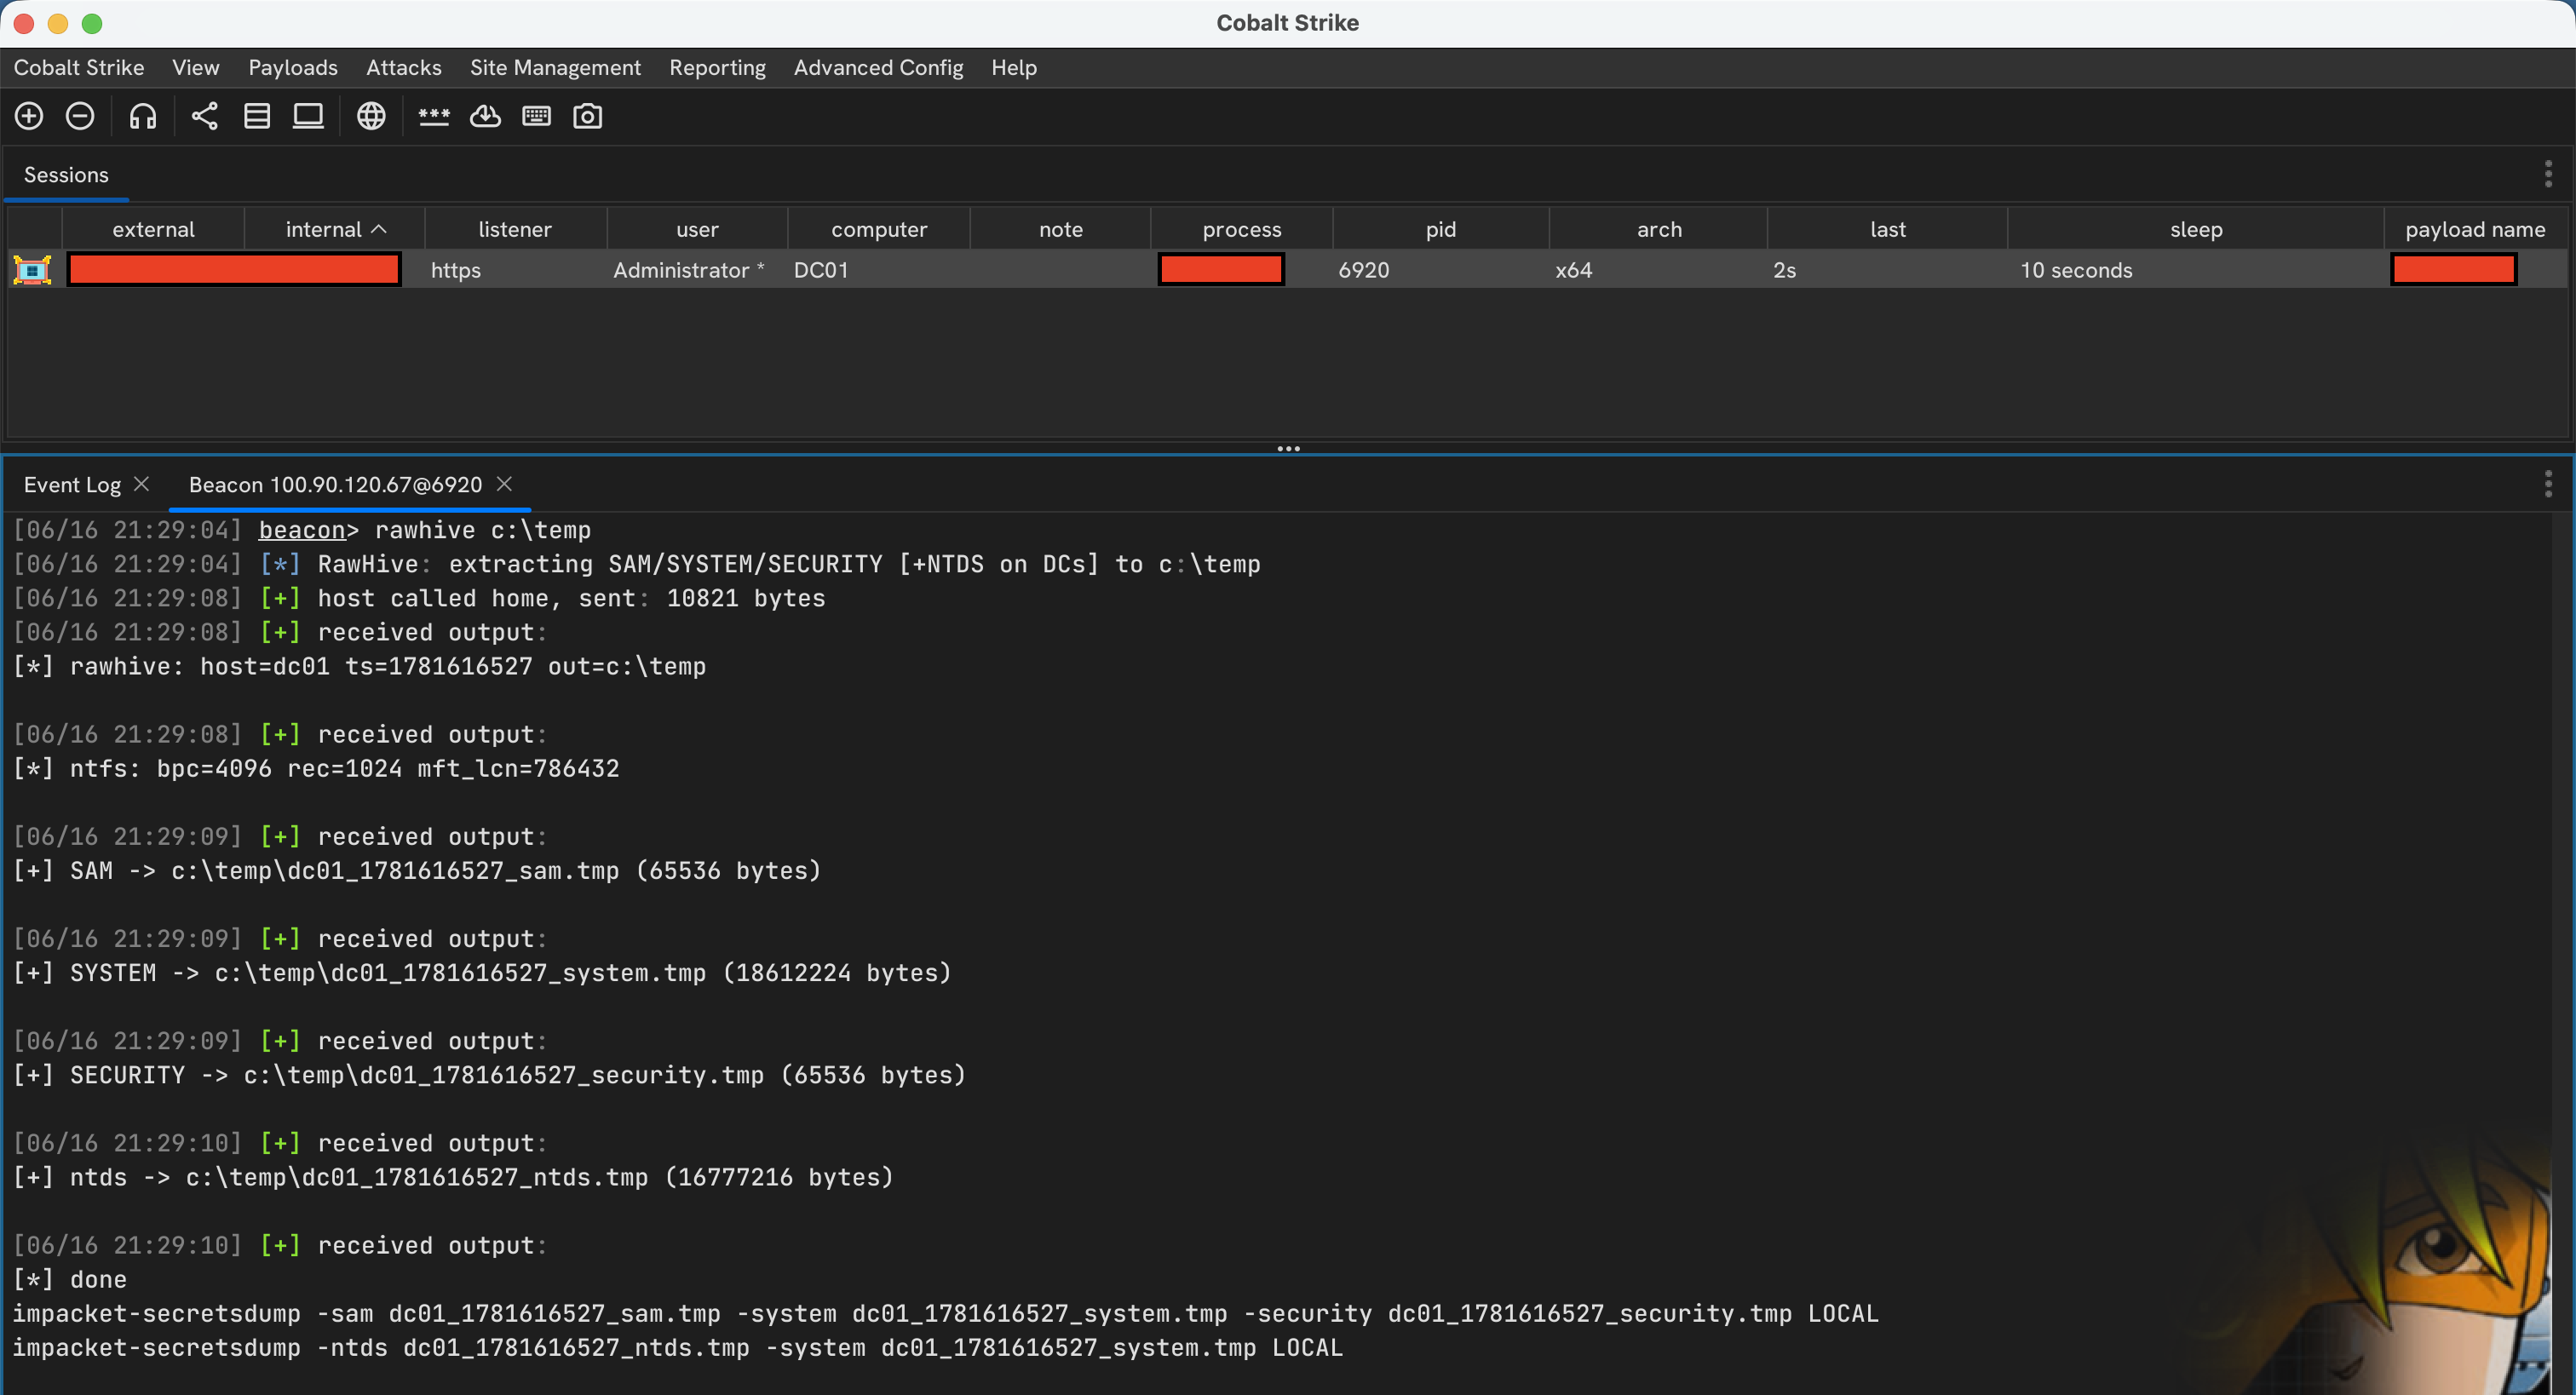
GitHubnmht3t/rawhive

Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
digital-forensicsdisk-forensicsexploitation+4
963 months ago
hashr preview

hashr

GitHubgoogle/hashr

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
digital-forensicsdisk-forensicsforensics+2
1337 months ago
ForensiX preview

ForensiX

GitHubtheevidencehunter/forensix

Digital Forensics Intelligence Framework
digital-forensicsdisk-forensicsforensics+4
5 months ago
osxcollector preview
Archived

osxcollector

GitHubyelparchive/osxcollector

A forensic evidence collection & analysis toolkit for OS X

digital-forensicsdisk-forensicsforensics+3
1.9k7 years ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k8 days ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

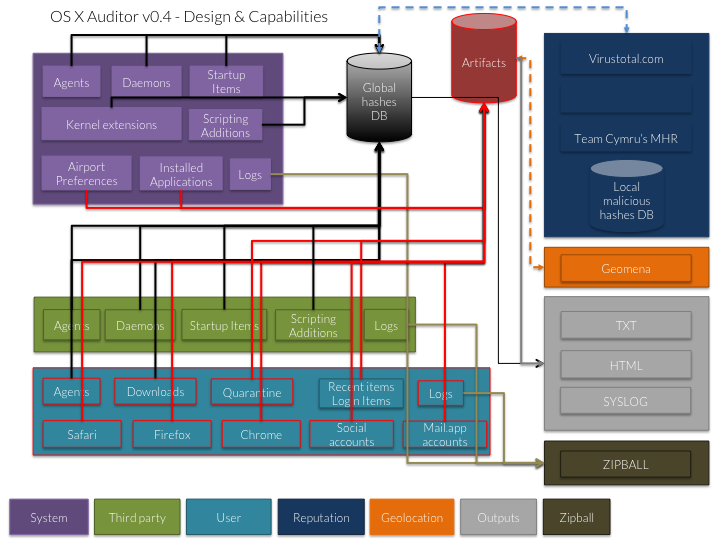
OS X Auditor is a free Mac OS X computer forensics tool

digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
KapeFiles preview

KapeFiles

GitHubericzimmerman/kapefiles

This repository serves as a place for community created Targets and Modules for use with KAPE.

digital-forensicsdisk-forensicsforensics+2
88222 days ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8204 months ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4885 years ago
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework

digital-forensicsdisk-forensicsforensics+7
6076 years ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
3731 month ago
Previous1234Next