
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework

digital-forensicsdisk-forensicsforensics+7
607
6 years ago
wxHexEditor preview

wxHexEditor

GitHubeua/wxhexeditor

wxHexEditor official GIT repo

binary-analysisdata-recoverydisk-forensics+2
6182 years ago
Disk-Arbitrator preview

Disk-Arbitrator

GitHubaburgh/disk-arbitrator

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
data-recoverydigital-forensicsdisk-forensics+2
7141 year ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5215 years ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)

data-recoverydigital-forensicsdisk-forensics+1
23824 days ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
curated-resourcesdigital-forensicsdisk-forensics+9
5174 years ago
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format
data-recoverydigital-forensicsdisk-forensics
18710 days ago
Volumiser preview

Volumiser

GitHubccob/volumiser

CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
command-and-controldata-exfiltrationdigital-forensics+3
4372 years ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format
data-recoverydigital-forensicsdisk-forensics+1
1491 month ago
foremost preview

foremost

GitHubkorczis/foremost

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
data-recoverydigital-forensicsdisk-forensics+2
3819 years ago
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
digital-forensicsdisk-forensicsforensics+2
34311 months ago
RawCopy preview

RawCopy

GitHubjschicht/rawcopy

Commandline low level file extractor for NTFS
data-recoverydigital-forensicsdisk-forensics+1
3187 years ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format
data-recoverydigital-forensicsdisk-forensics+2
12024 days ago
fatcat preview

fatcat

GitHubgregwar/fatcat

FAT filesystems explore, extract, repair, and forensic tool
data-recoverydigital-forensicsdisk-forensics+1
3251 year ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
data-recoverydigital-forensicsdisk-forensics+3
2581 year ago
LogFileParser preview

LogFileParser

GitHubjschicht/logfileparser

Parser for $LogFile on NTFS
binary-analysisdata-recoverydigital-forensics+3
2185 months ago
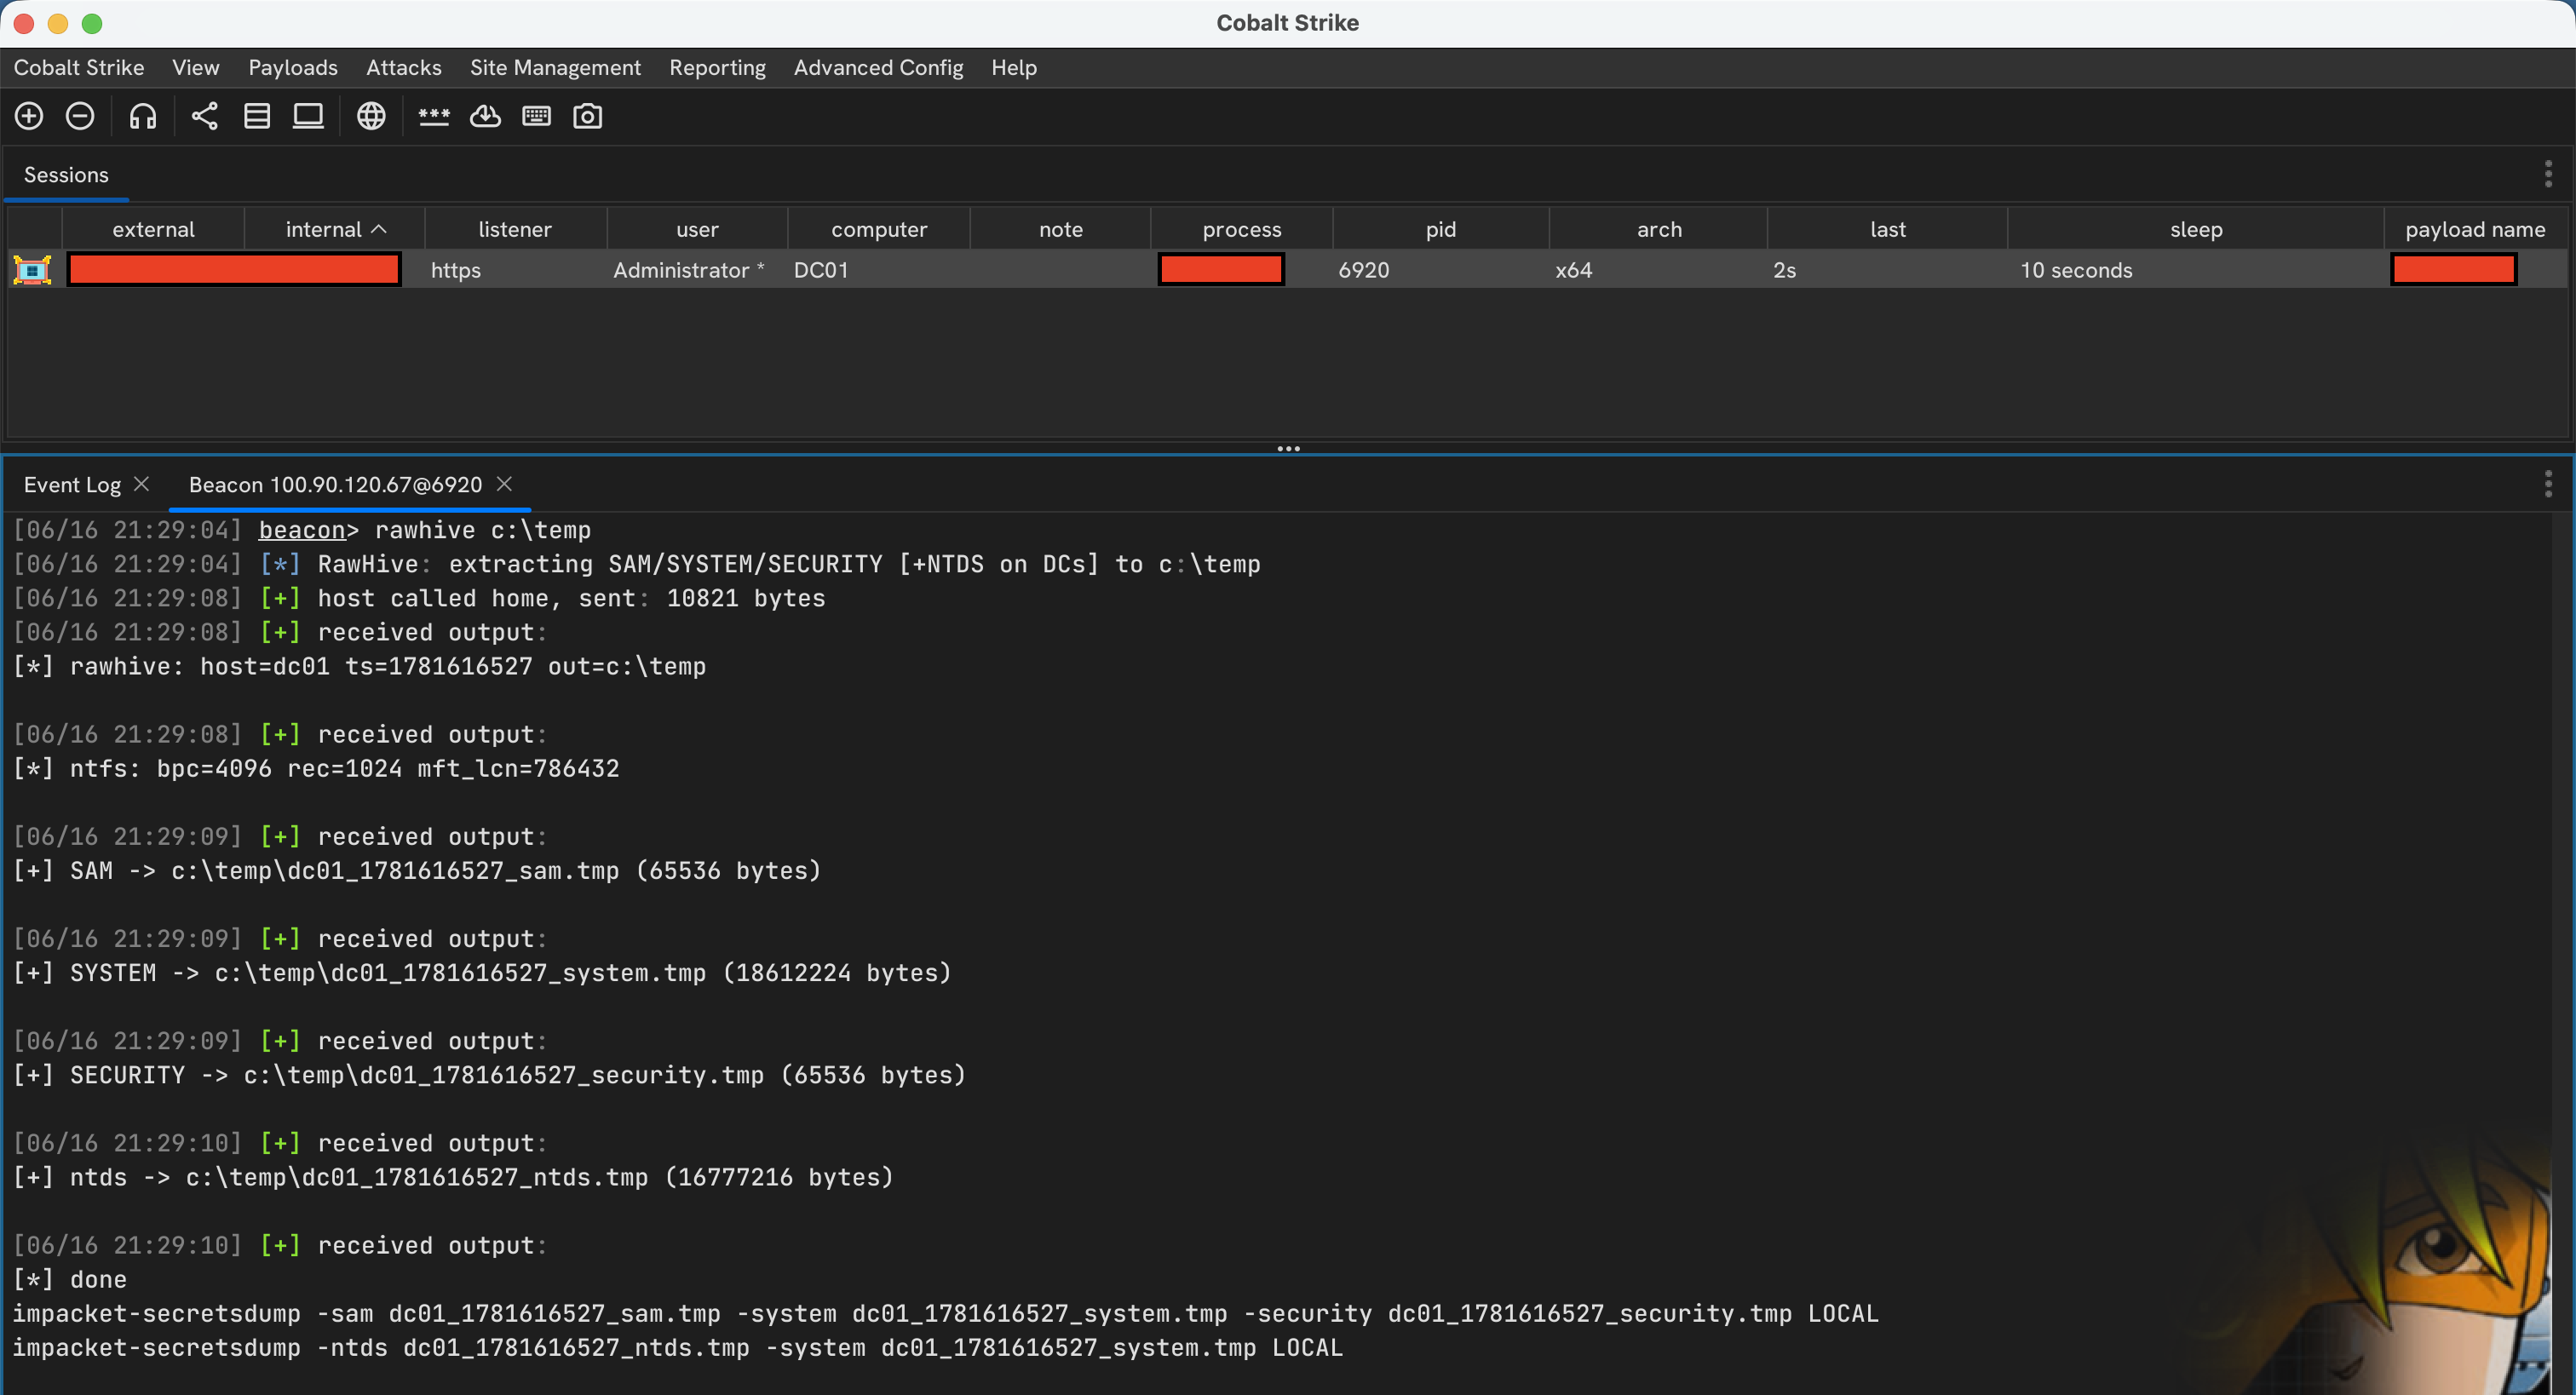
RawHive preview

RawHive

GitHubnmht3t/rawhive

Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
digital-forensicsdisk-forensicsexploitation+4
9324 days ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
Previous12345Next