
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
73 results
analyzeMFT preview

analyzeMFT

GitHubrowingdude/analyzemft

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
data-recoverydigital-forensicsdisk-forensics+1
533
1 year ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
data-recoverydigital-forensicsdisk-forensics+3
25611 months ago
ffs preview

ffs

GitHubdmtrkovalenko/ffs

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
data-recoverydigital-forensicsdisk-forensics+3
1983 months ago
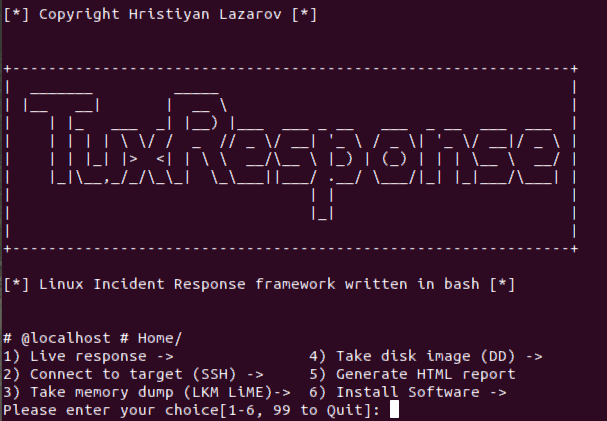
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
915 months ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1211 year ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
RawHive preview

RawHive

GitHubnmht3t/rawhive

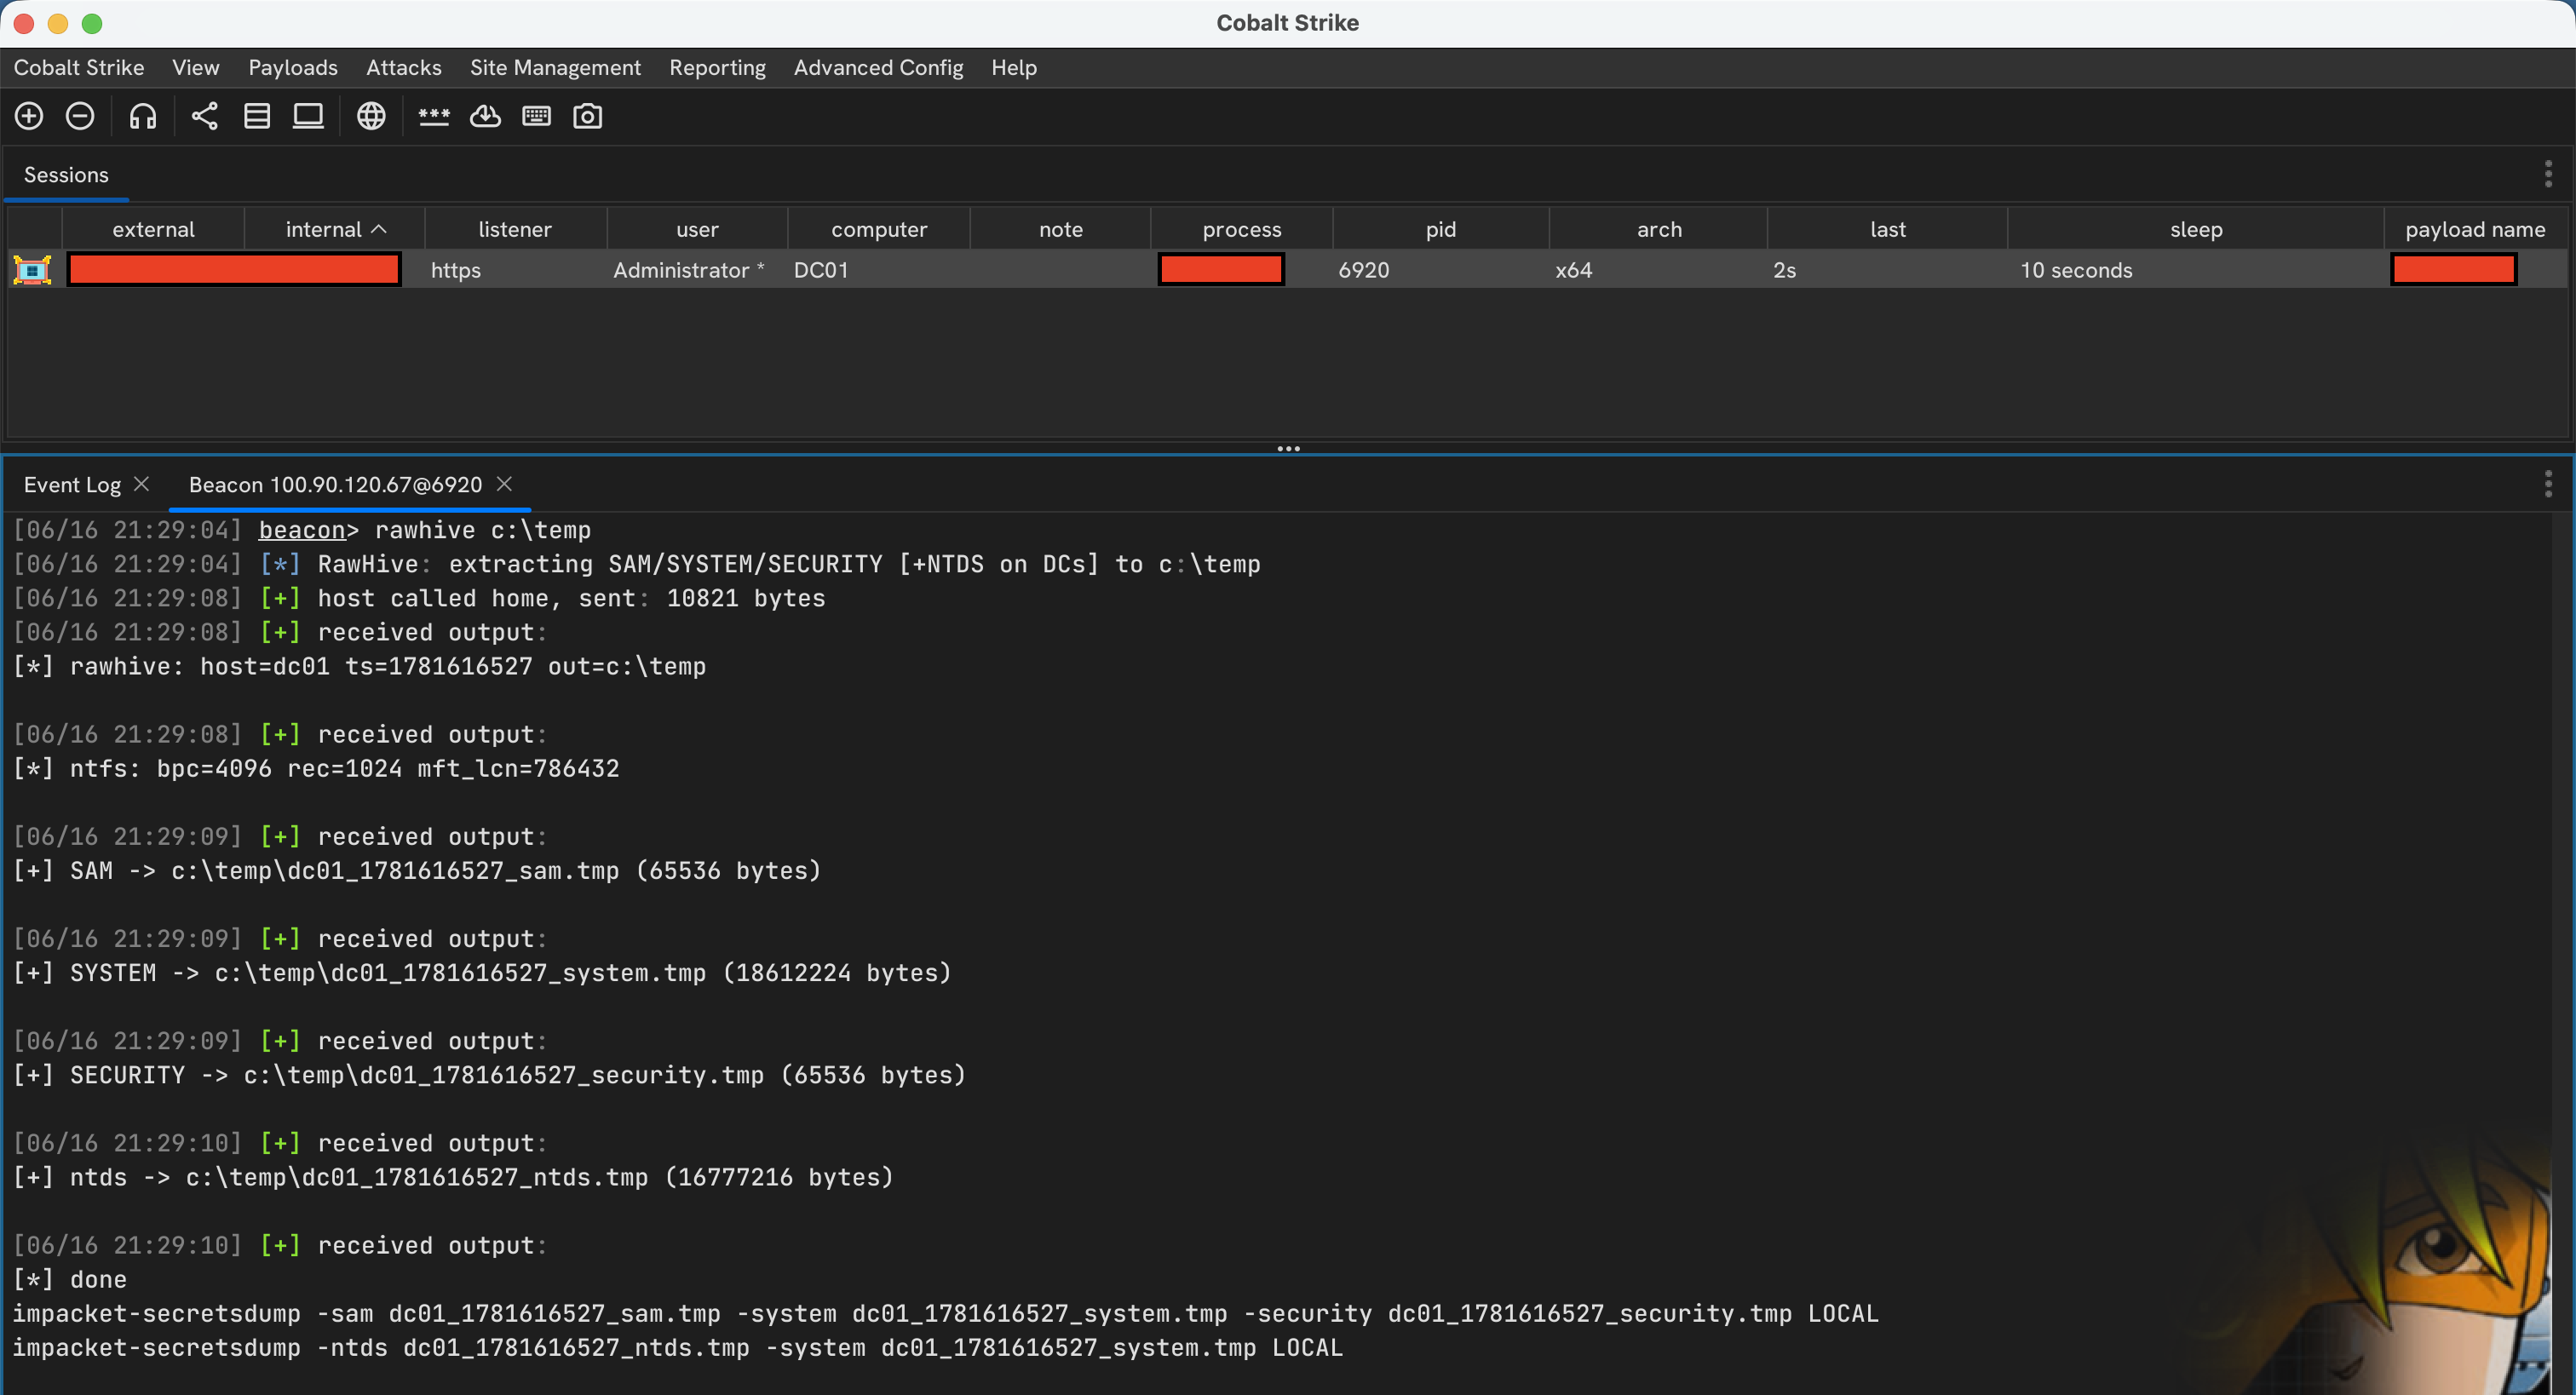
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…


digital-forensicsdisk-forensicsexploitation+4
963 months ago
truehunter preview

truehunter

GitHubadoreste/truehunter

Truehunter

data-recoverydigital-forensicsdisk-forensics+2
317 years ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

binary-analysisdata-recoverydigital-forensics+8
431 month ago
veeam-velociraptor preview

veeam-velociraptor

GitHubsynacktiv/veeam-velociraptor

Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.

digital-forensicsdisk-forensicsforensics+1
12 years ago
mig preview
Archived

mig

GitHubmozilla/mig

Distributed & real time digital forensics at the speed of the cloud

configuration-auditingdigital-forensicsdisk-forensics+6
1.2k7 years ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.0k1 day ago
autopsy preview

autopsy

GitHubsleuthkit/autopsy

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

data-recoverydigital-forensicsdisk-forensics+3
3.4k4 months ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor is a free Mac OS X computer forensics tool

digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:

data-recoverydigital-forensicsdisk-forensics+9
1.4k26 days ago
cyberchef-recipes preview

cyberchef-recipes

GitHubmattnotmax/cyberchef-recipes

A list of cyber-chef recipes and curated links

curated-resourcesdigital-forensicsdisk-forensics+8
2.2k2 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k2 days ago
RecoverPy preview

RecoverPy

GitHubpablolec/recoverpy

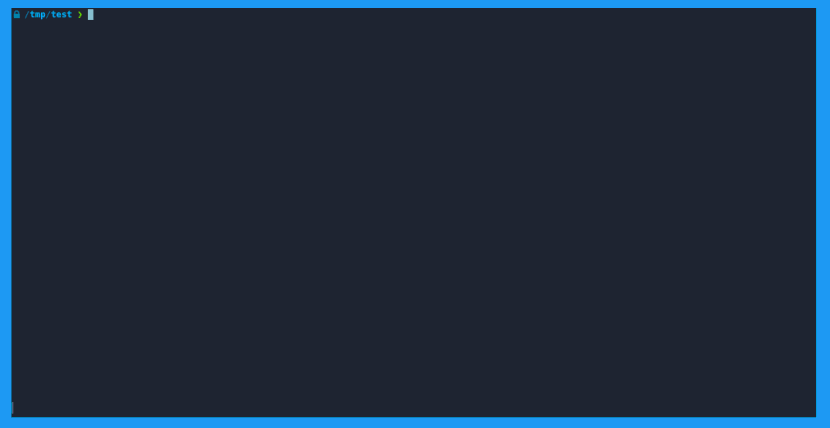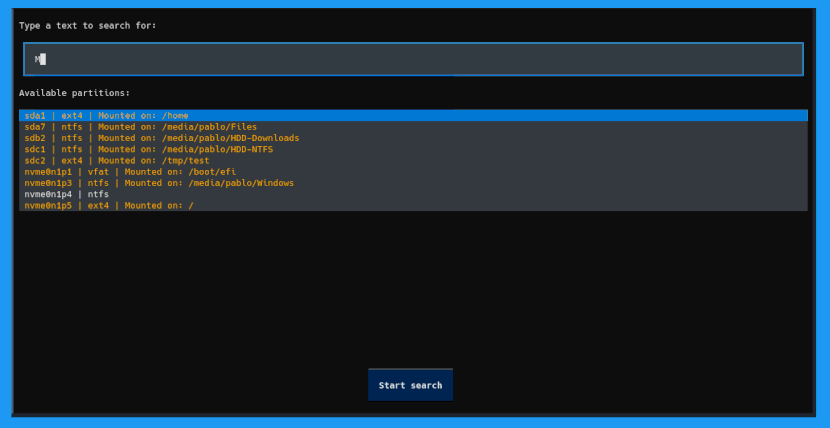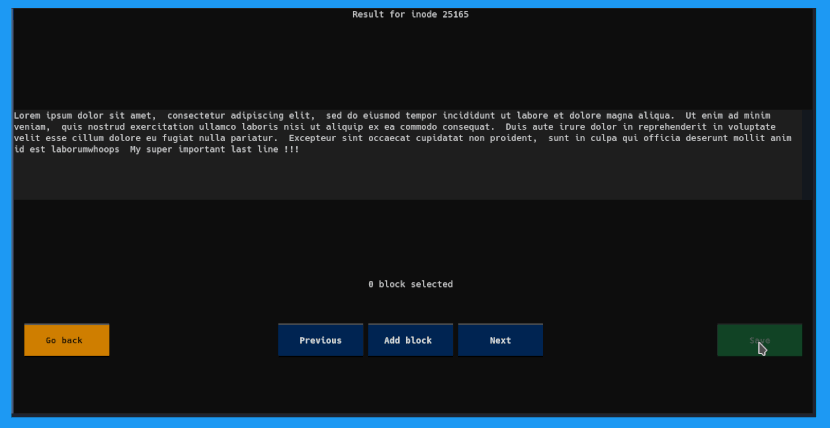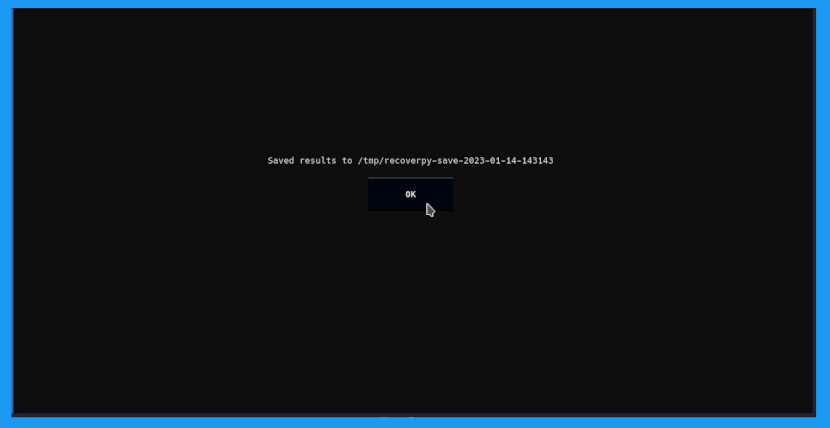
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal

data-recoverydigital-forensicsdisk-forensics+1
1.8k2 months ago
Previous12345Next