Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

A tool for forensic file system reconstruction.

Incident Response Forensic Framework

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

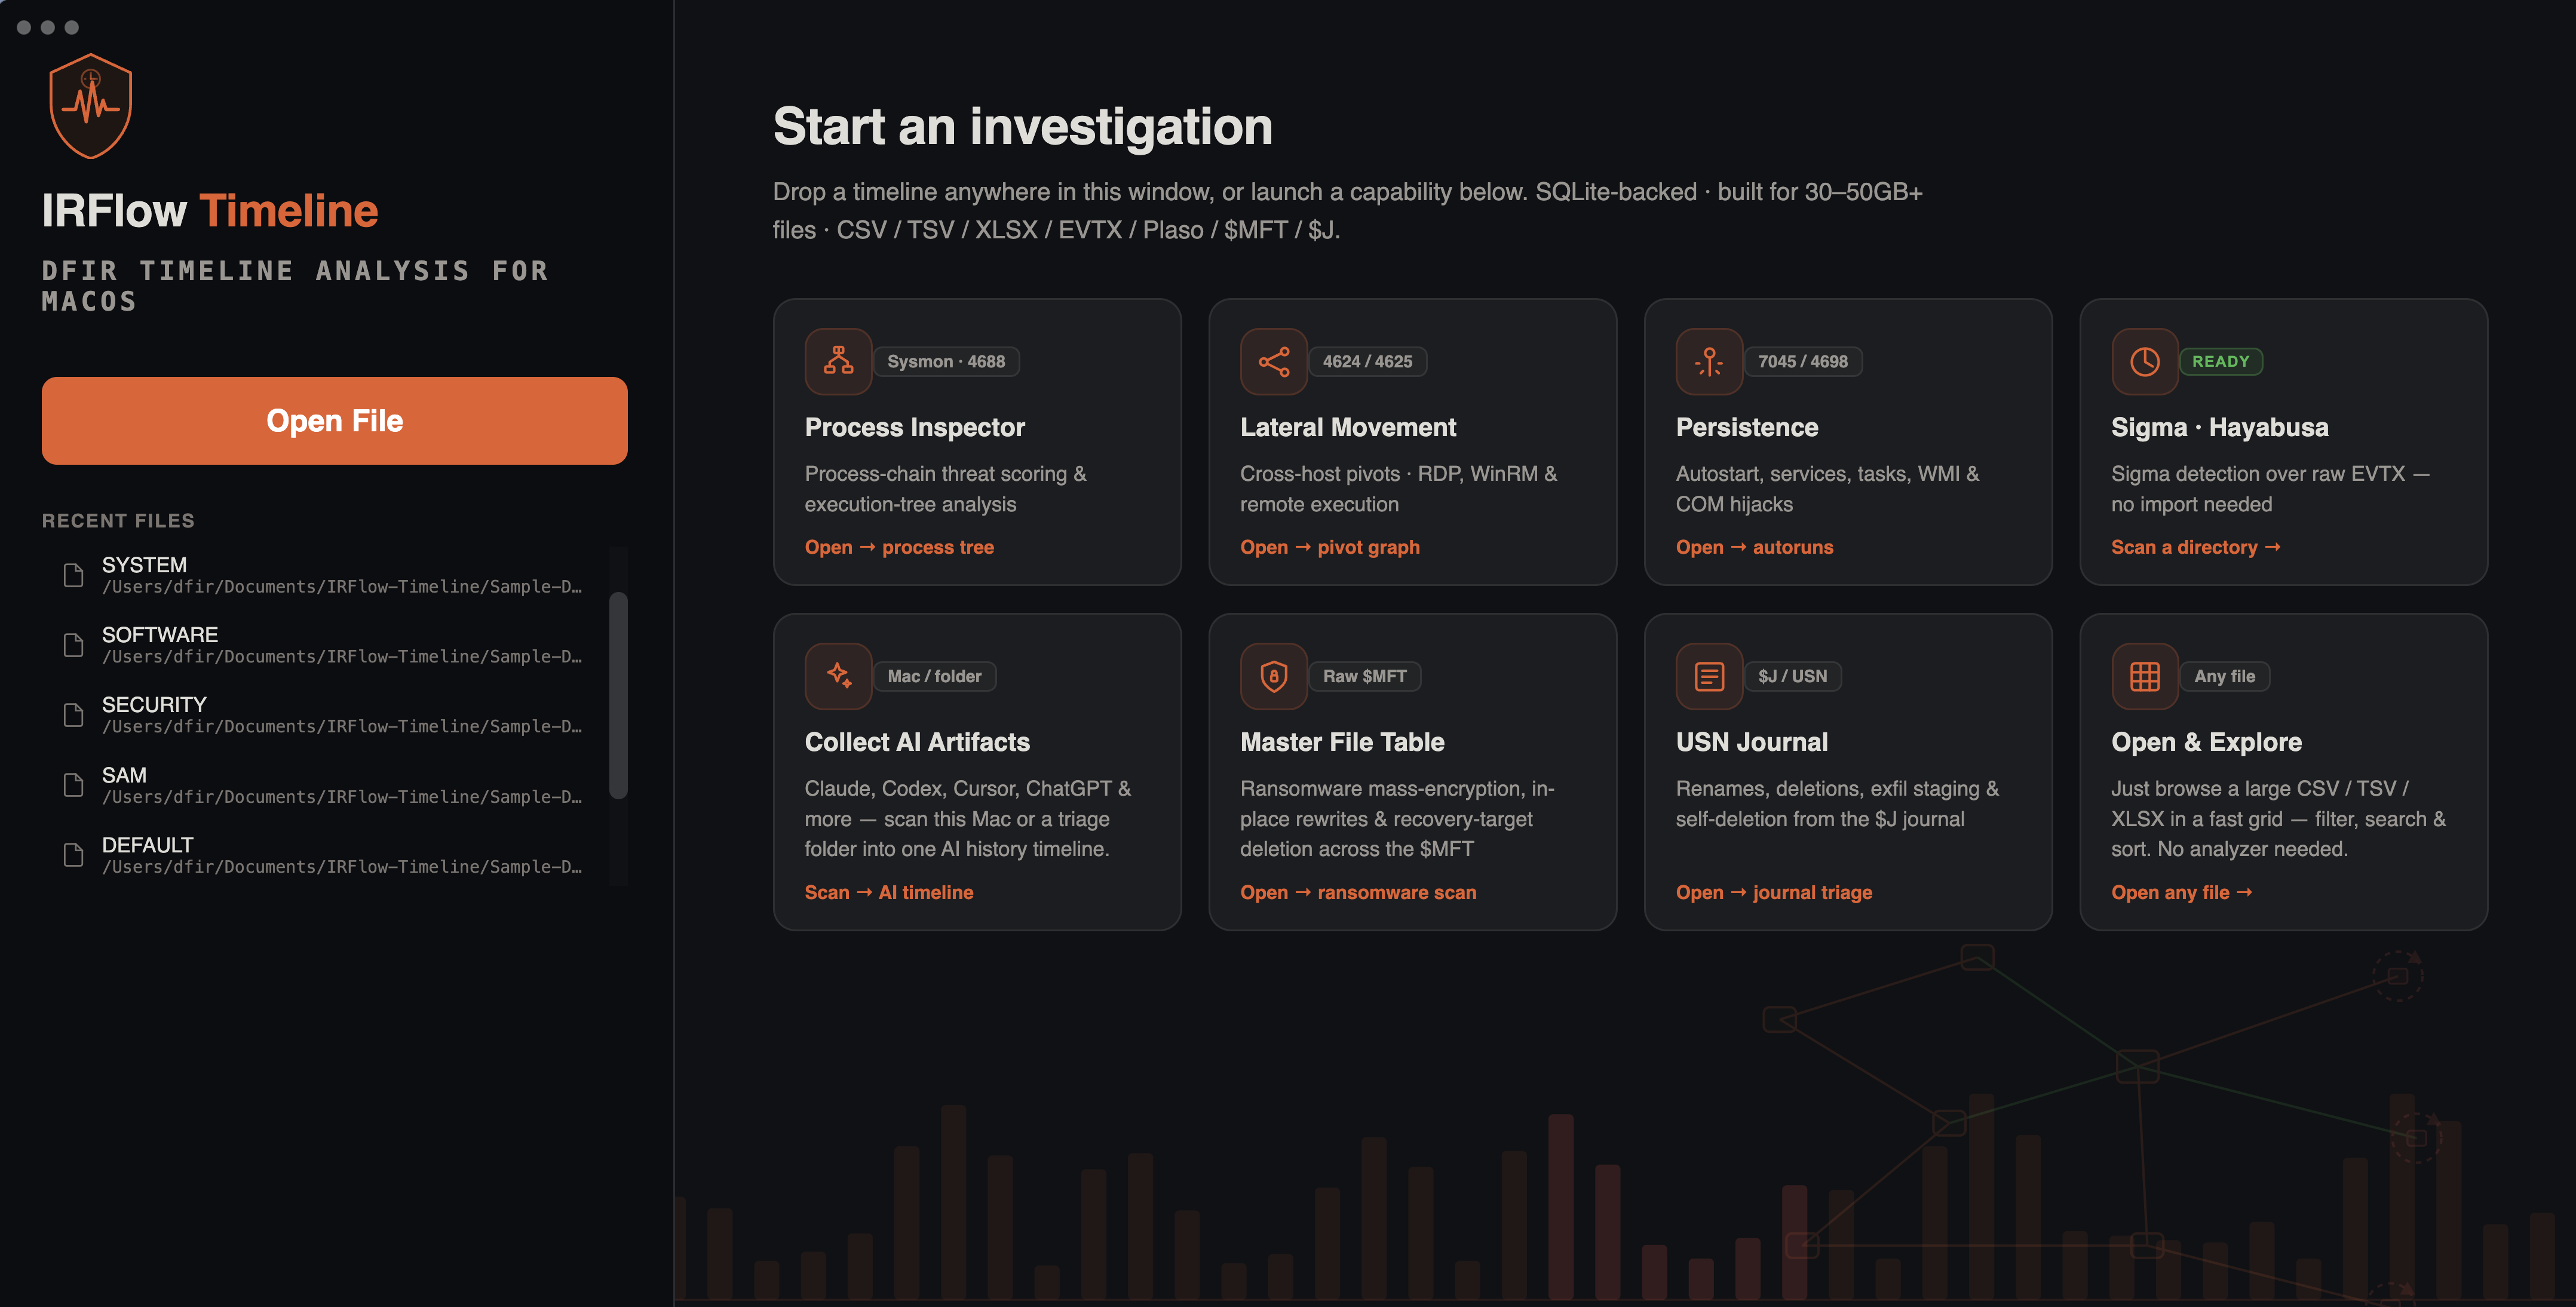
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

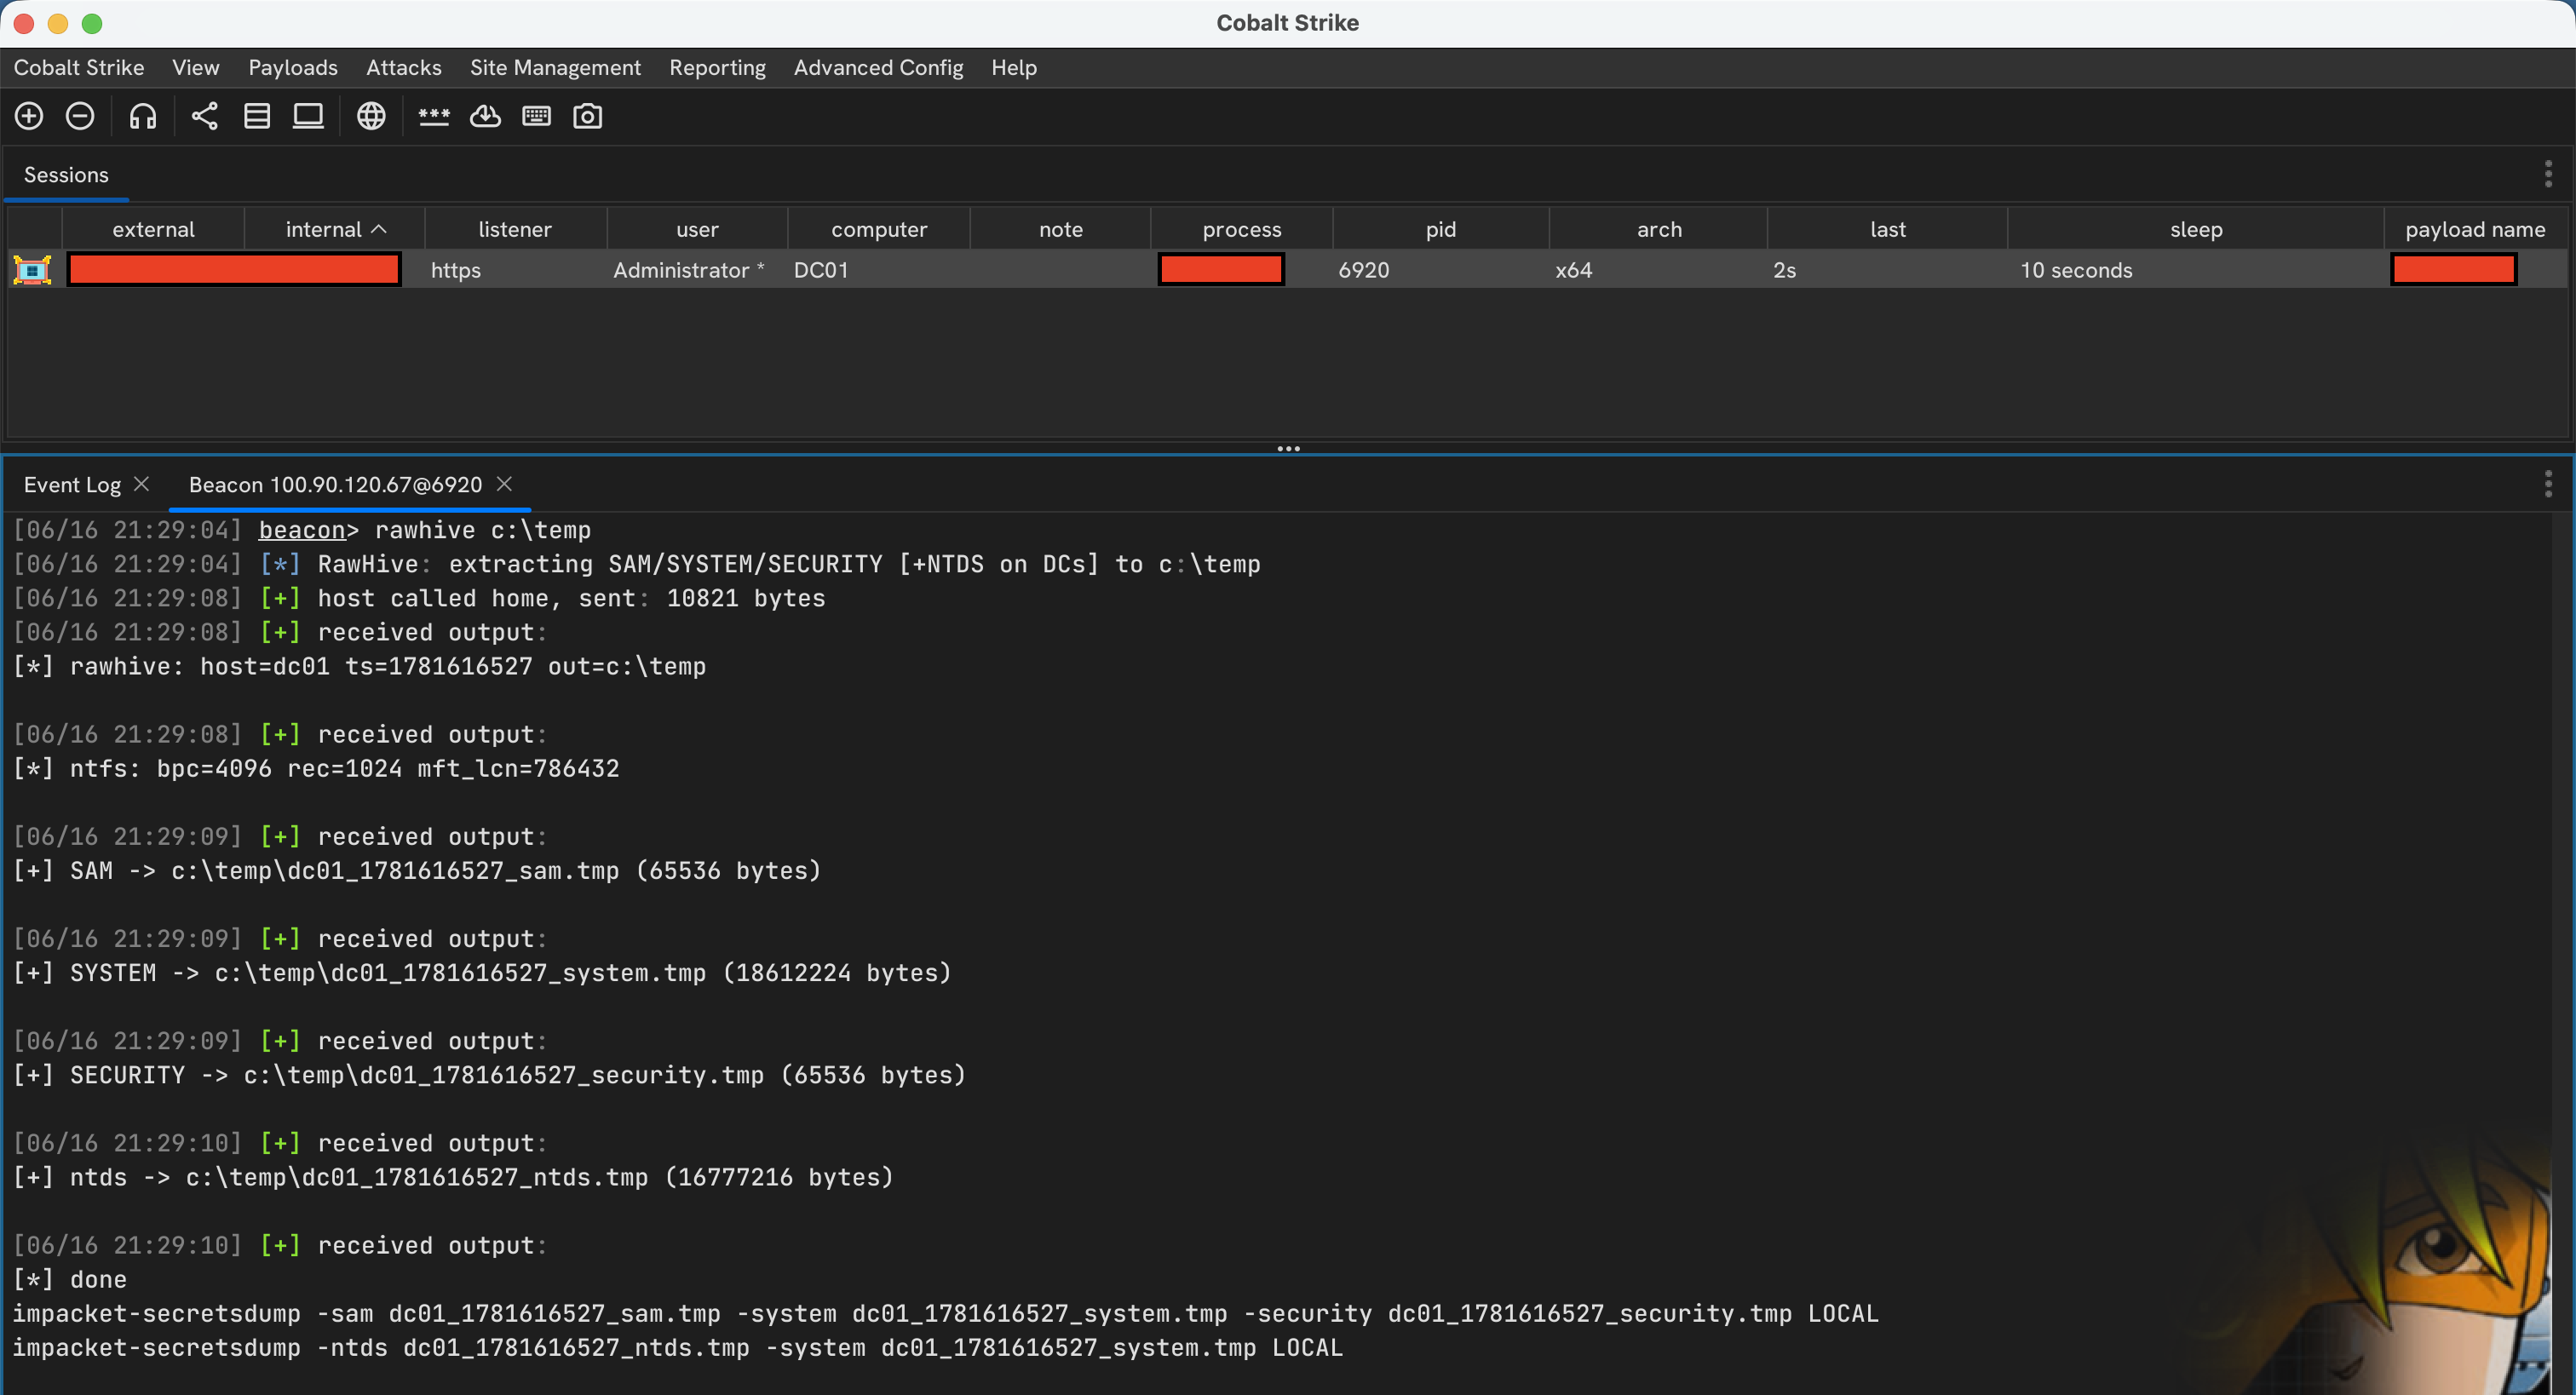
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.


Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

Digital Forensics Intelligence Framework