
libfsntfs
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
data-recoverydigital-forensicsdisk-forensics+1
237
libyal/libfsntfsLibrary and tools to access the Windows New Technology File System (NTFS)
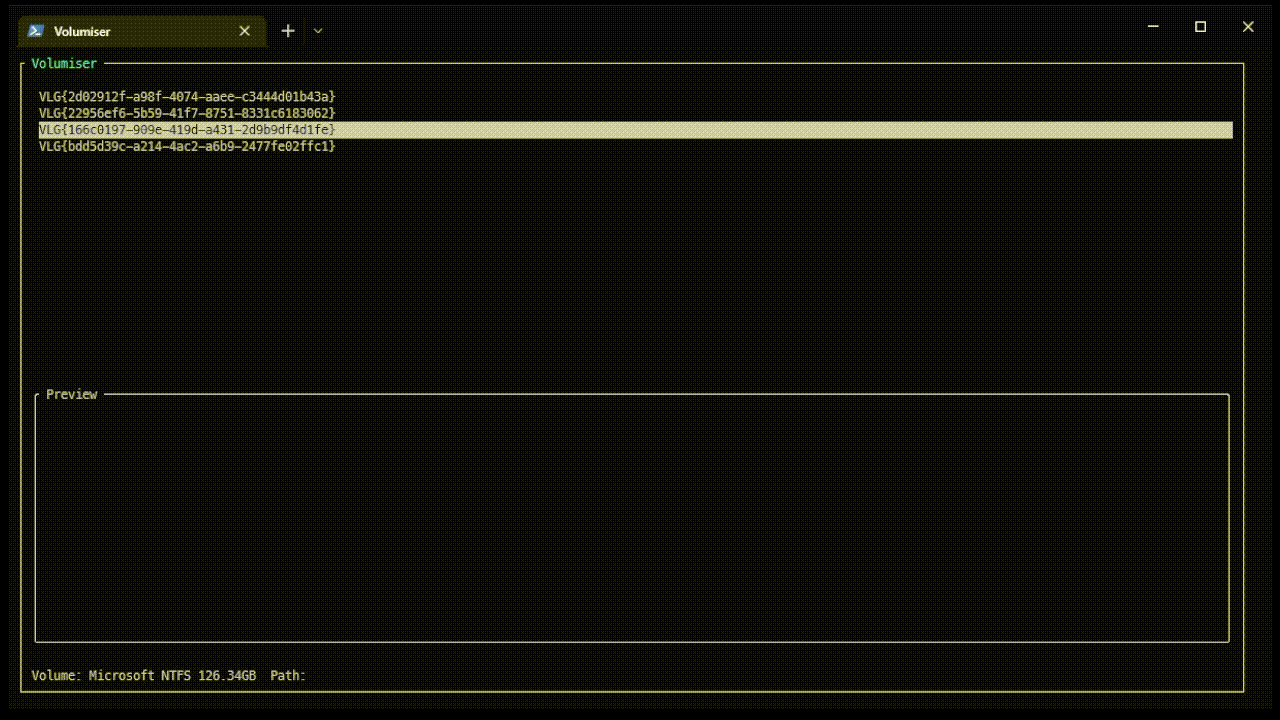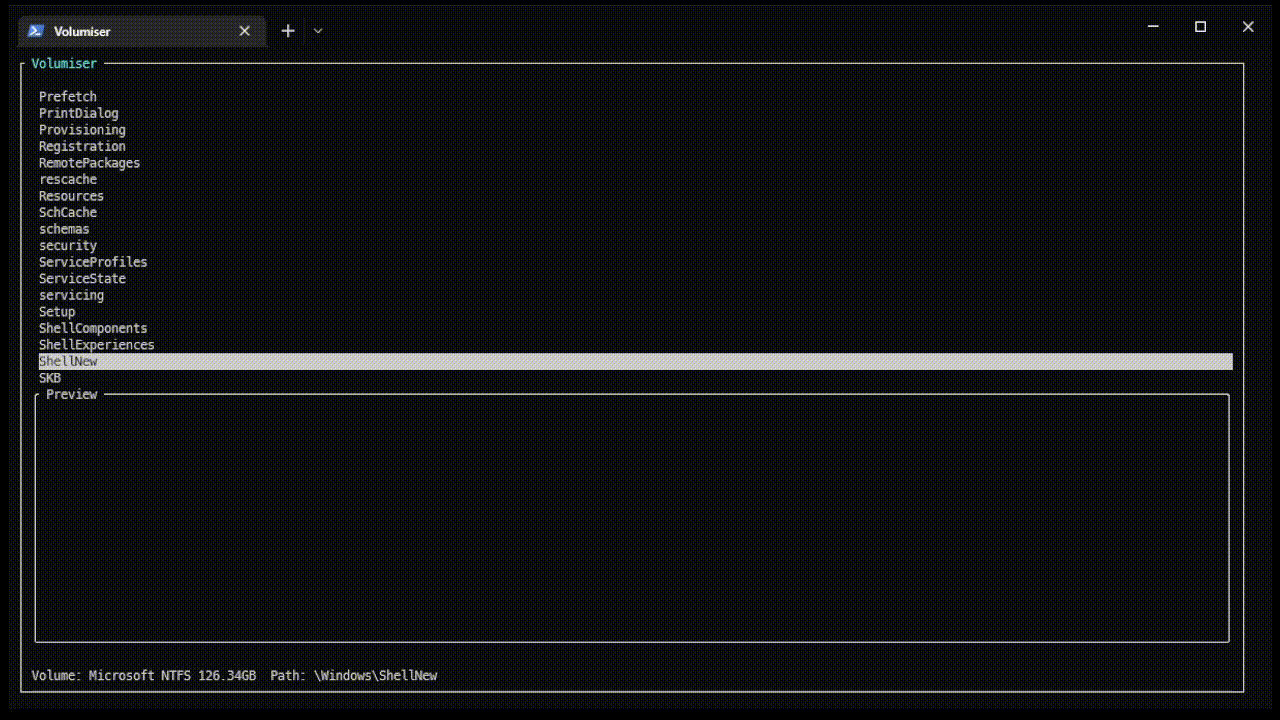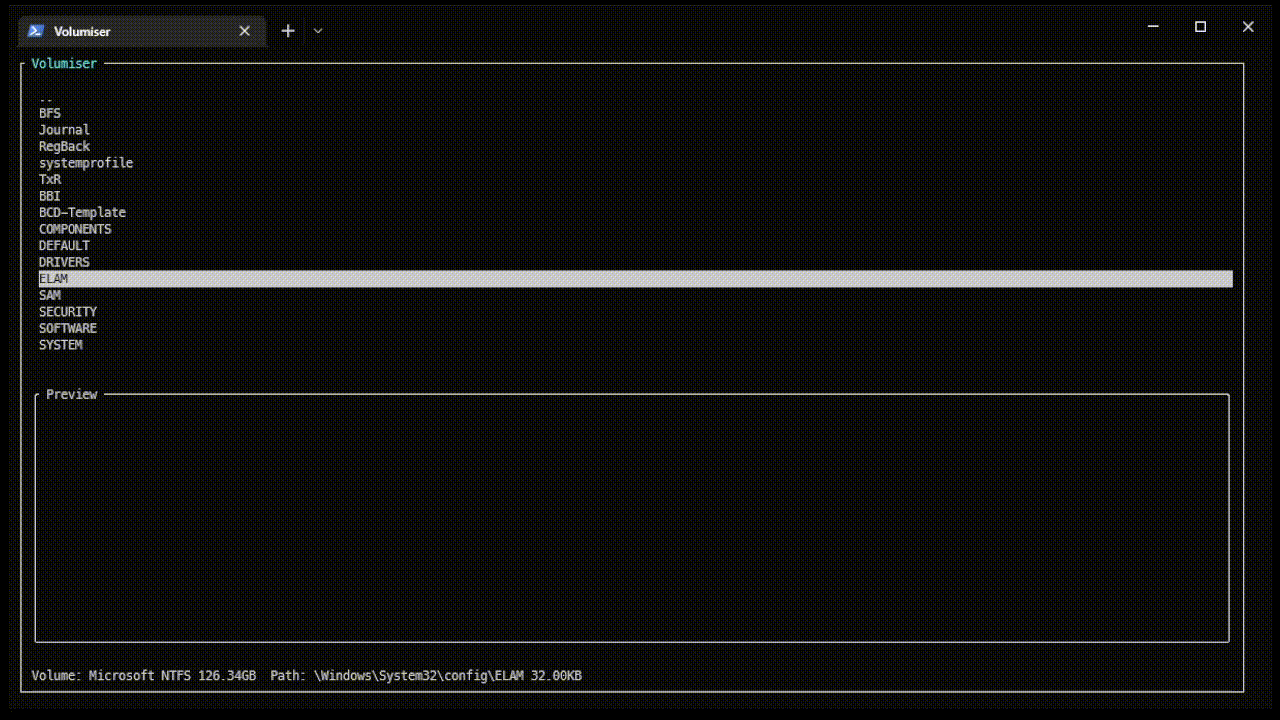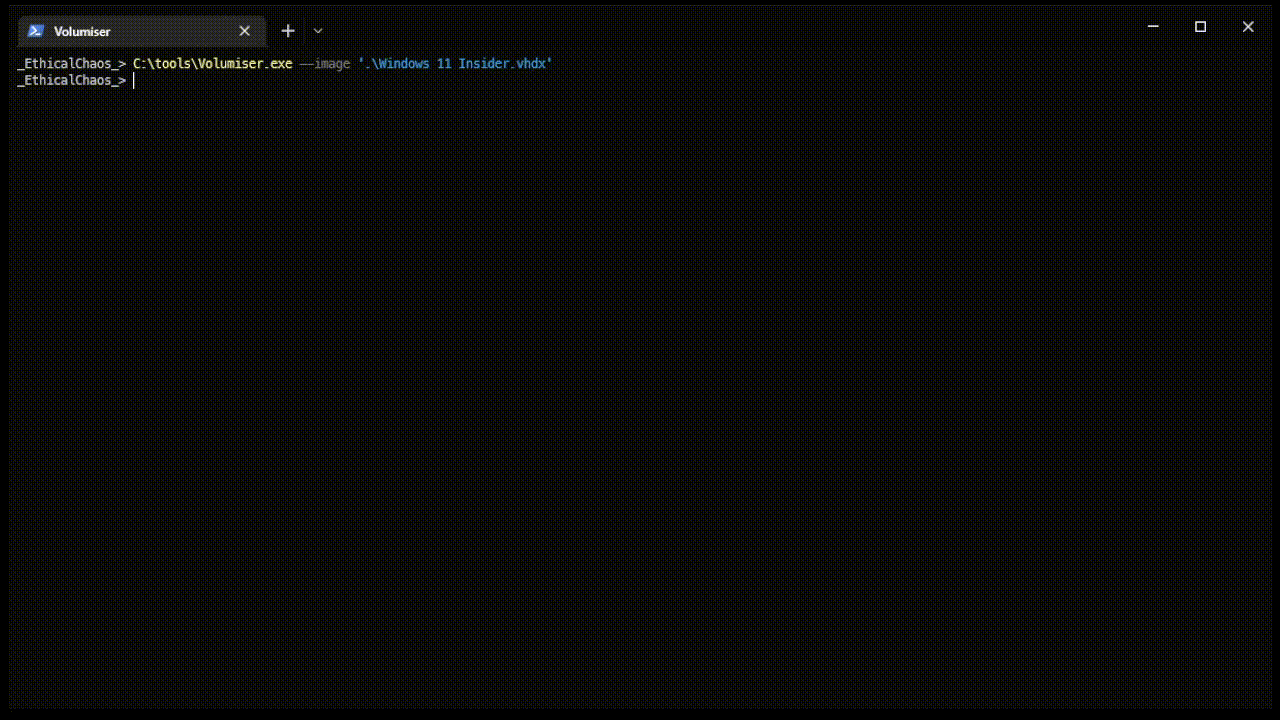 ccob/volumiser
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 jschicht/logfileparser
Parser for $LogFile on NTFS
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X

 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.