
LogFileParser
 jschicht/logfileparser
Parser for $LogFile on NTFS
binary-analysisdata-recoverydigital-forensics+3
jschicht/logfileparserParser for $LogFile on NTFS
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 cherojeong/extundelete
Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty

 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 cristianzsh/forensictools
Collection of forensic tools
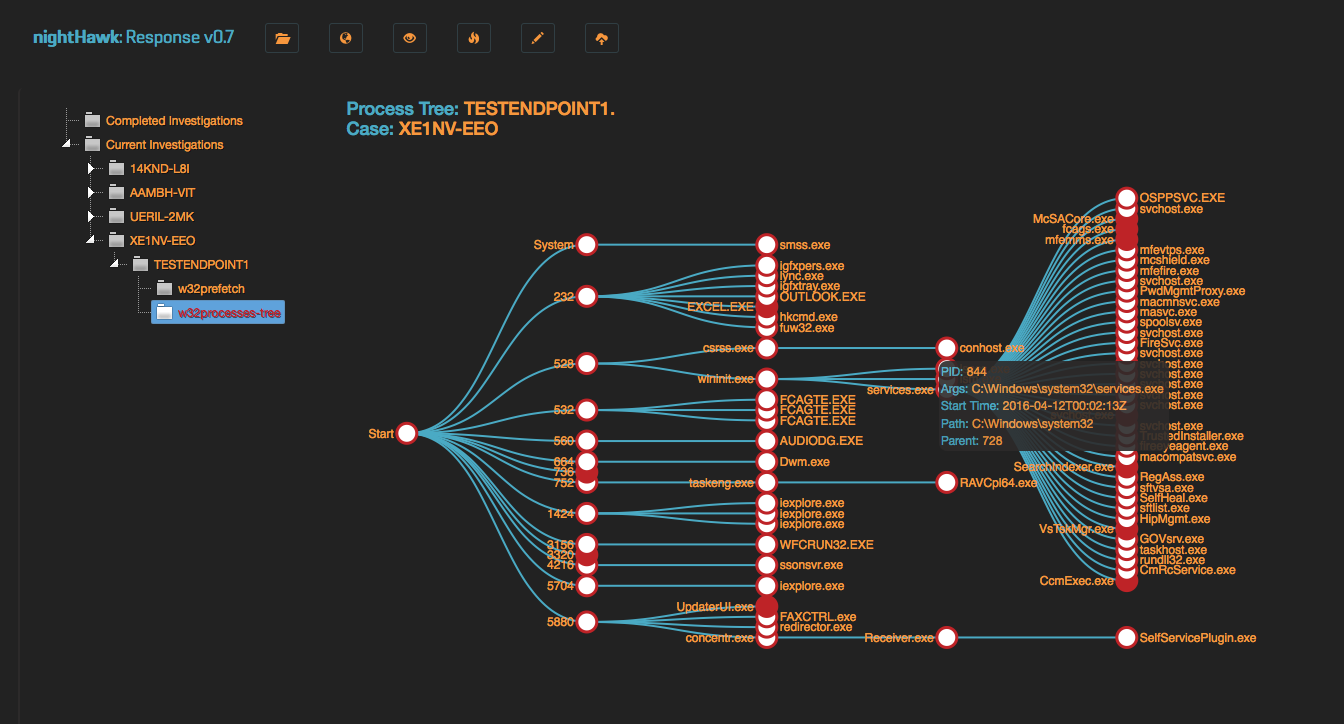 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
