


 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 gnu-mirror-unofficial/ddrescue
Copies data from damaged or failing storage devices, handles read errors, and performs efficient rescue operations to recover as much data as…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
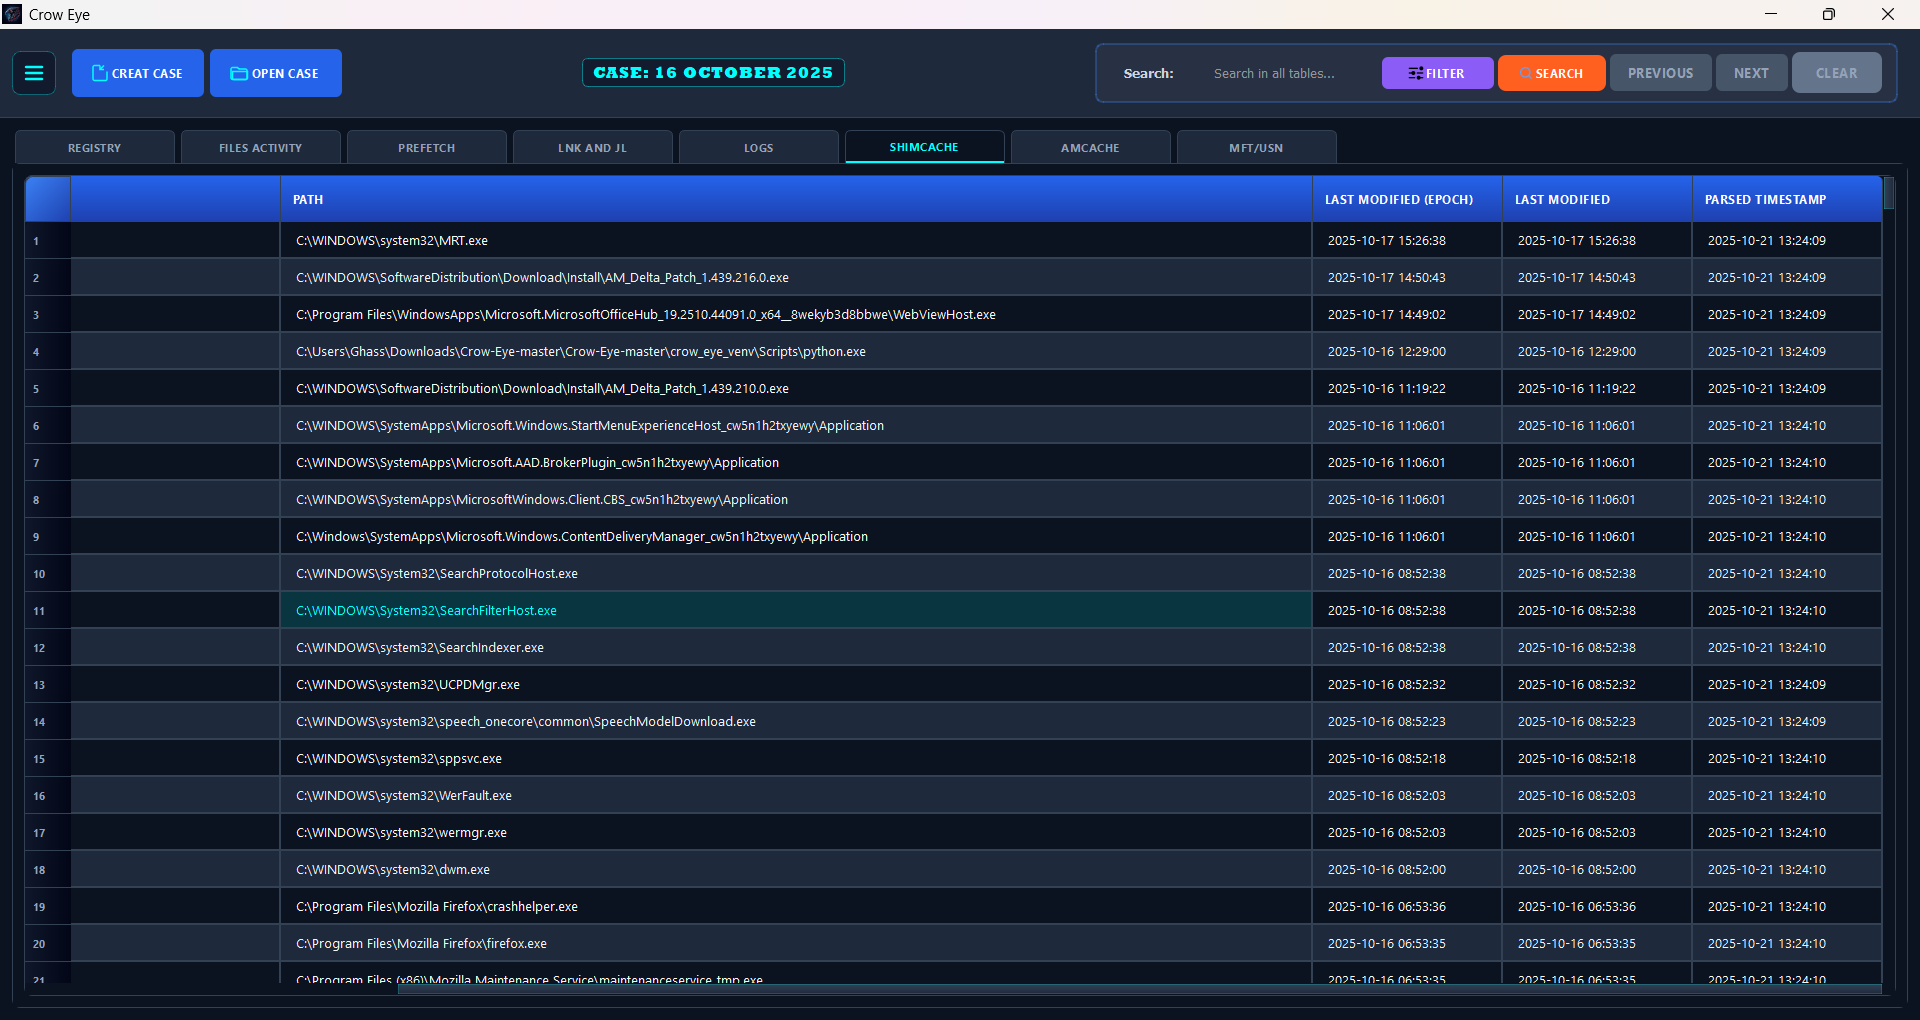 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.