aws-firmware-dump
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
cloud-infrastructure-securitycloud-securitydata-recovery+5
28
radkawar/aws-firmware-dumpAcquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links

 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
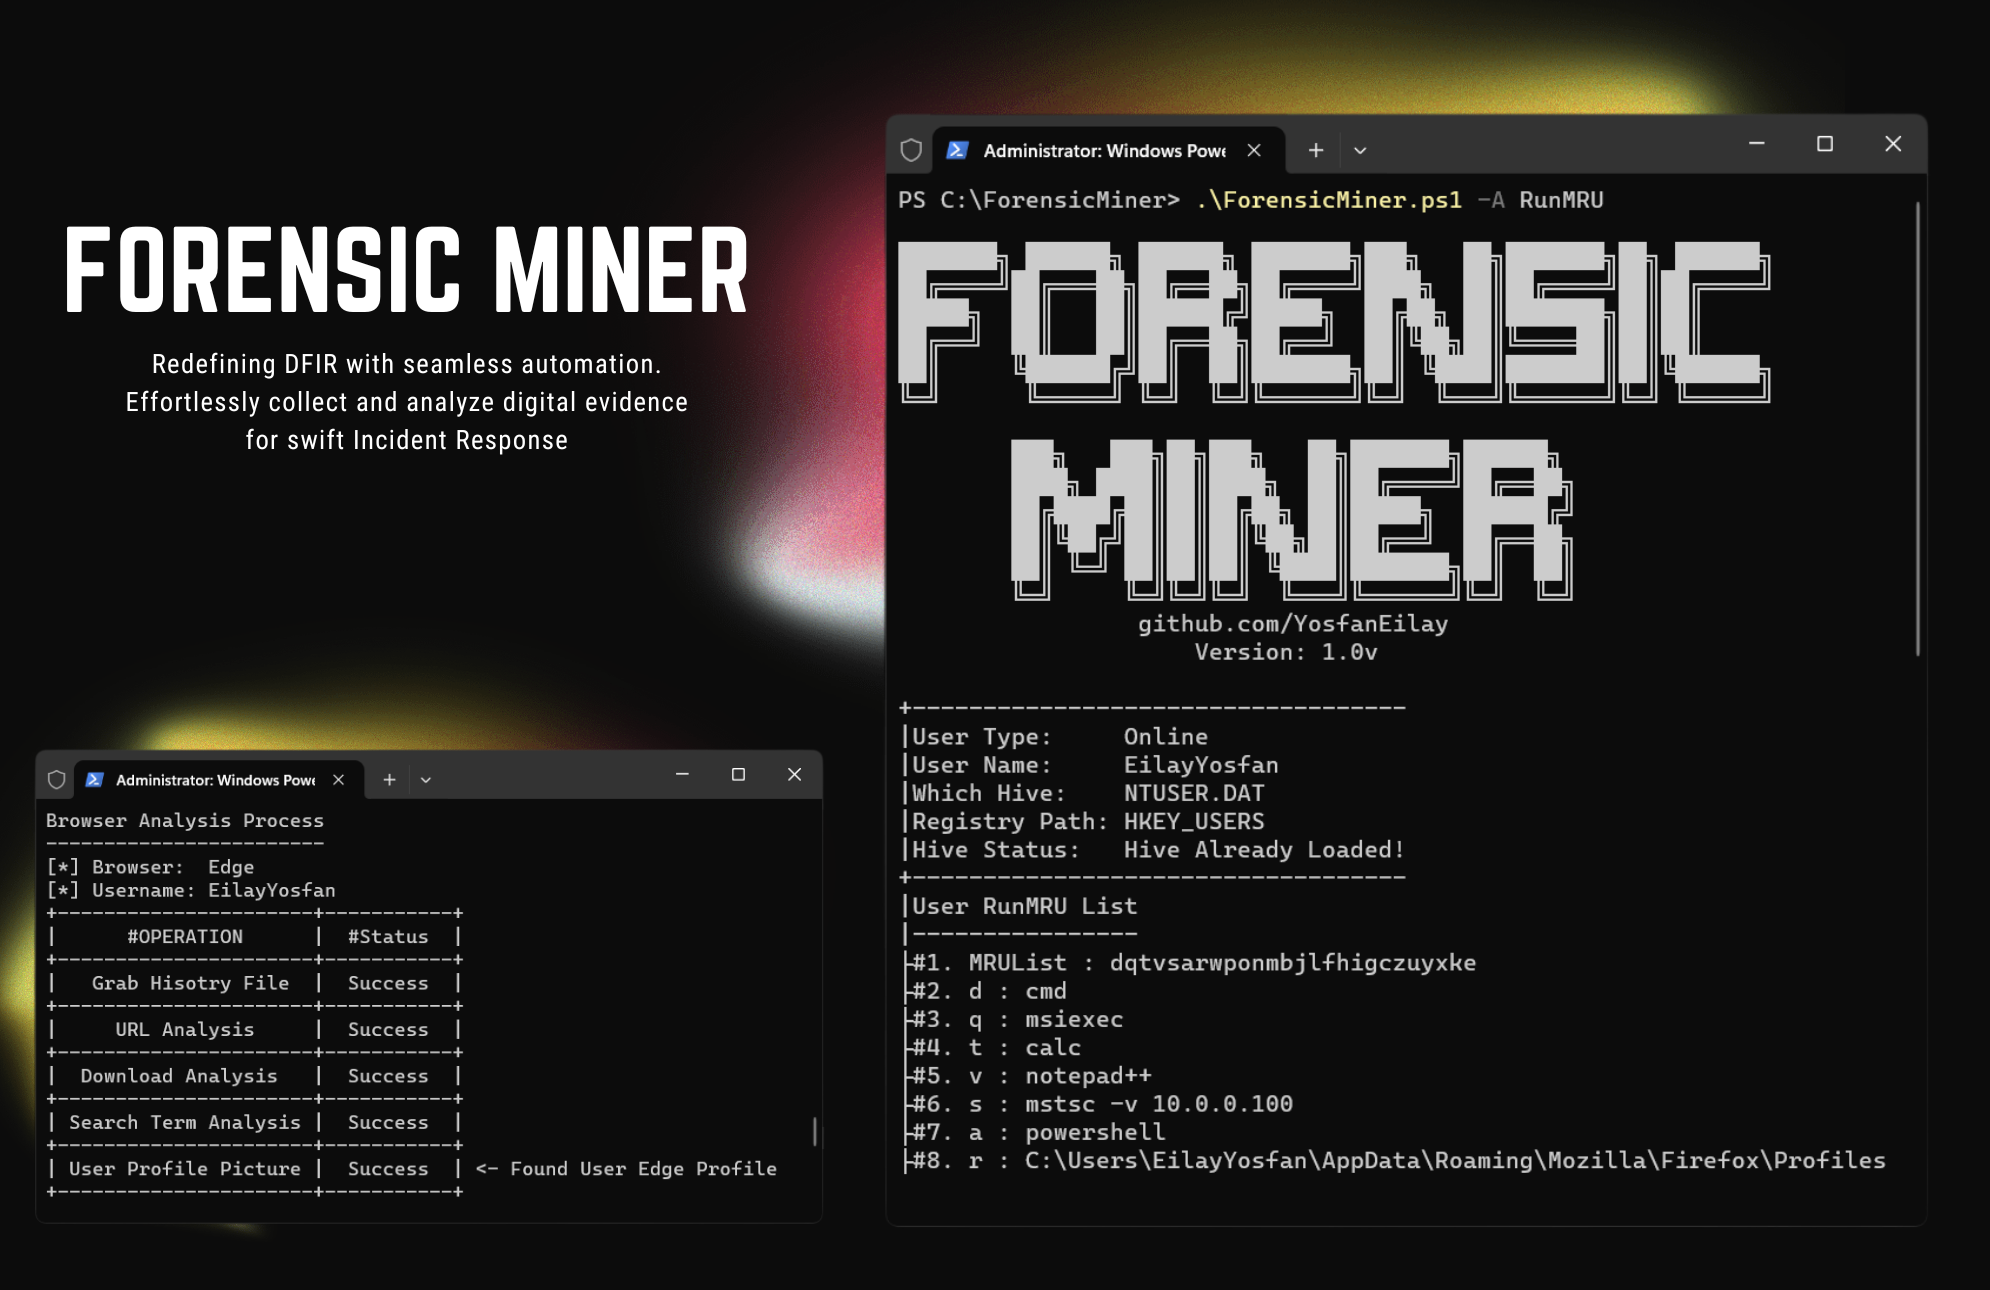 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 cristianzsh/forensictools
Collection of forensic tools
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…