
pict
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
digital-forensicsforensicsincident-response+2
95
thomasareed/pictModular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
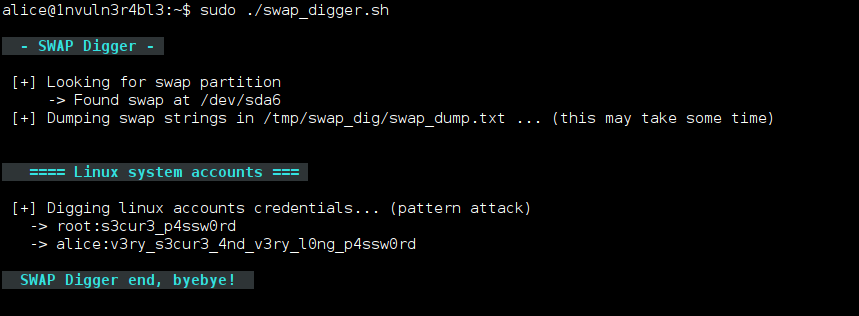 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
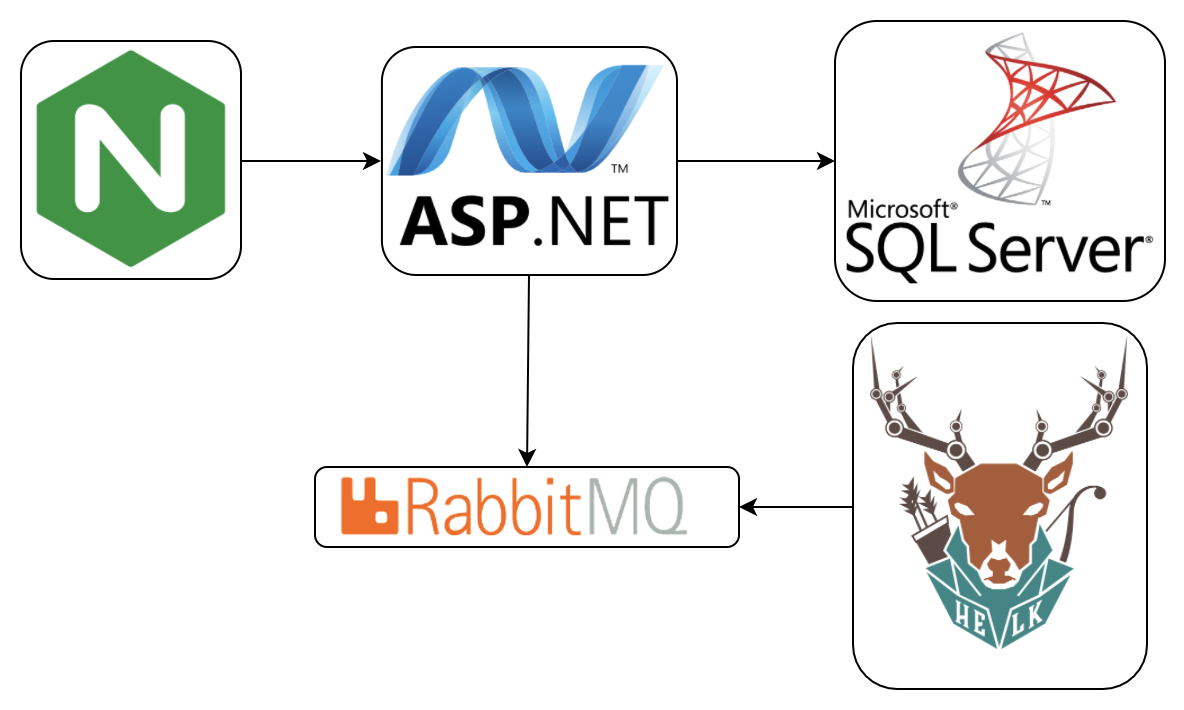 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
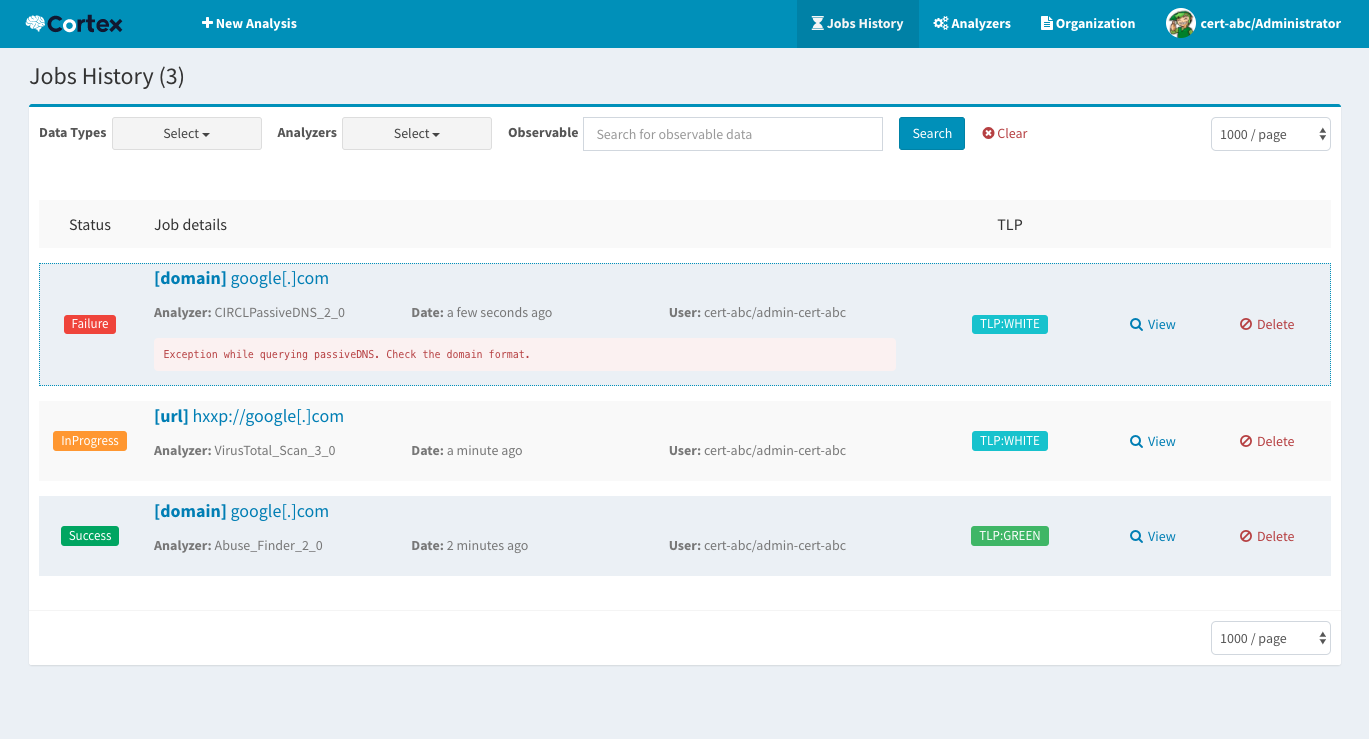 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
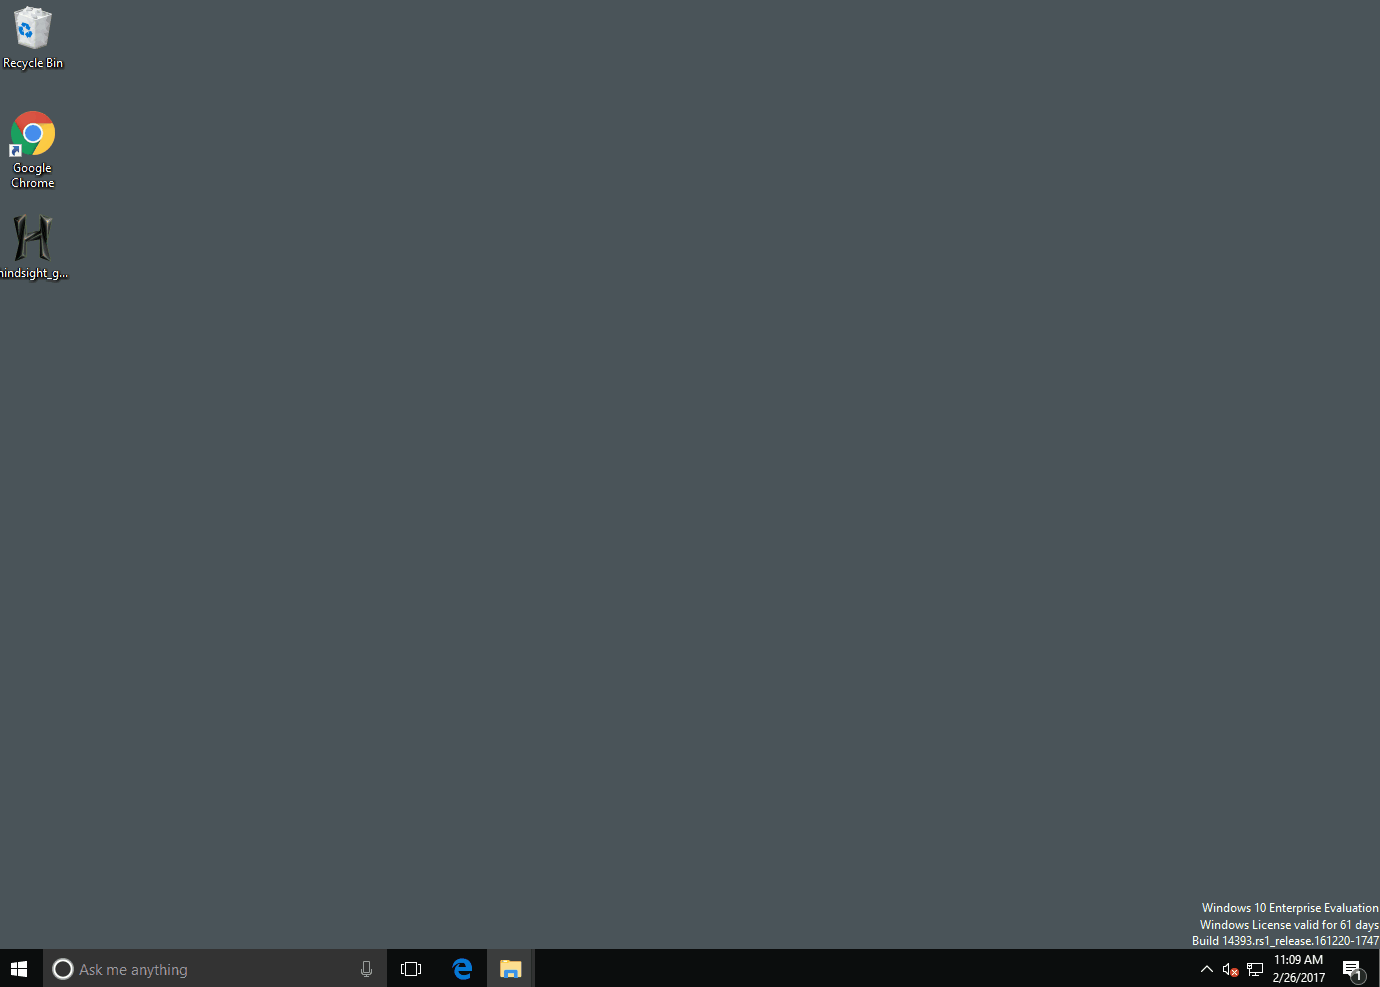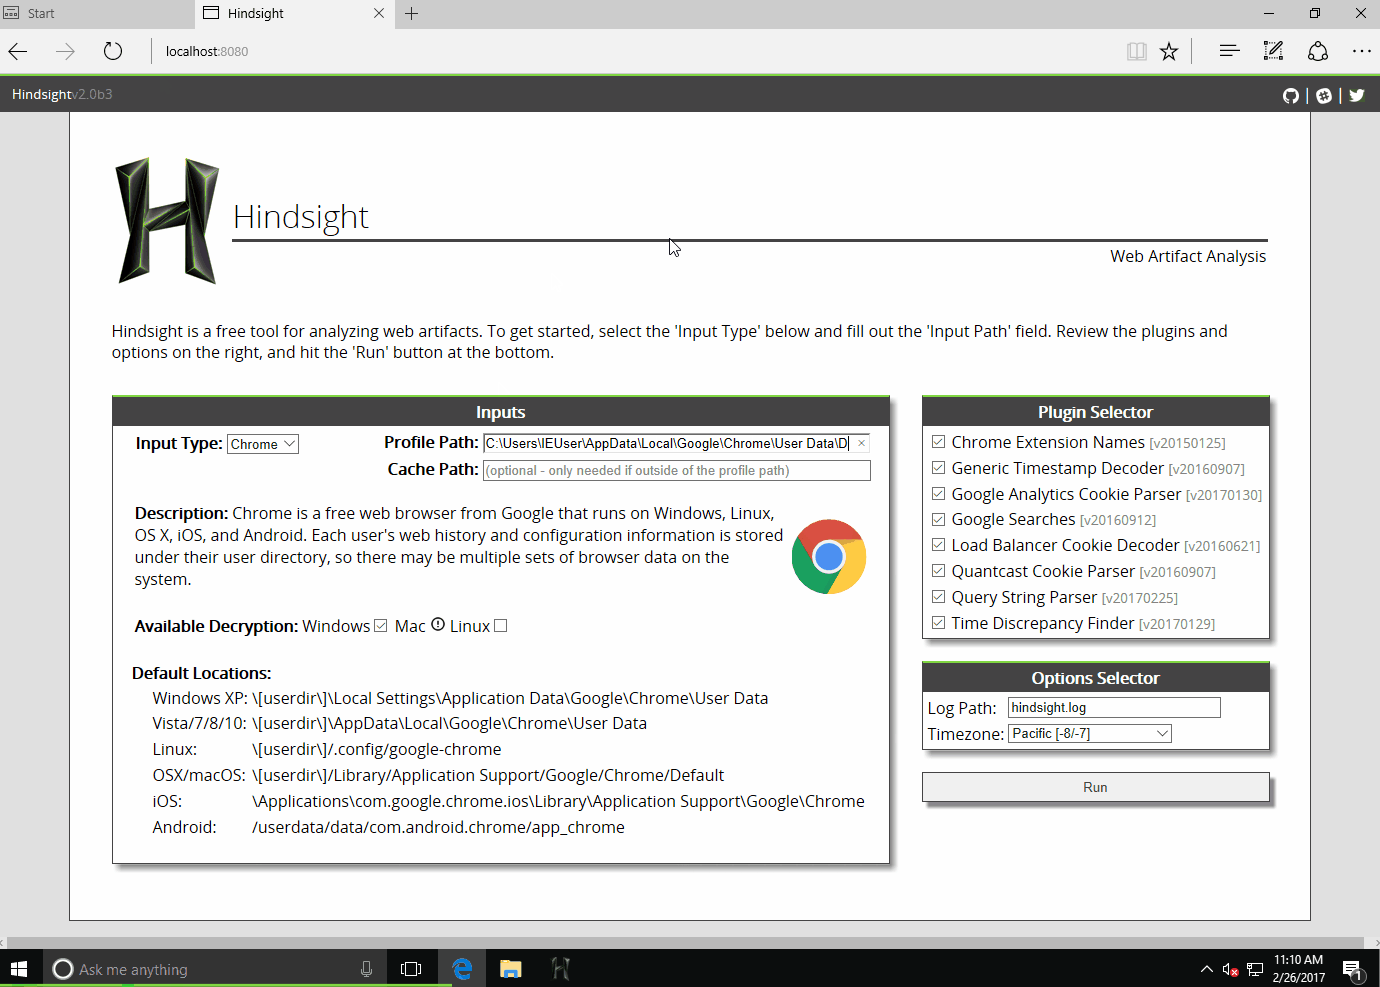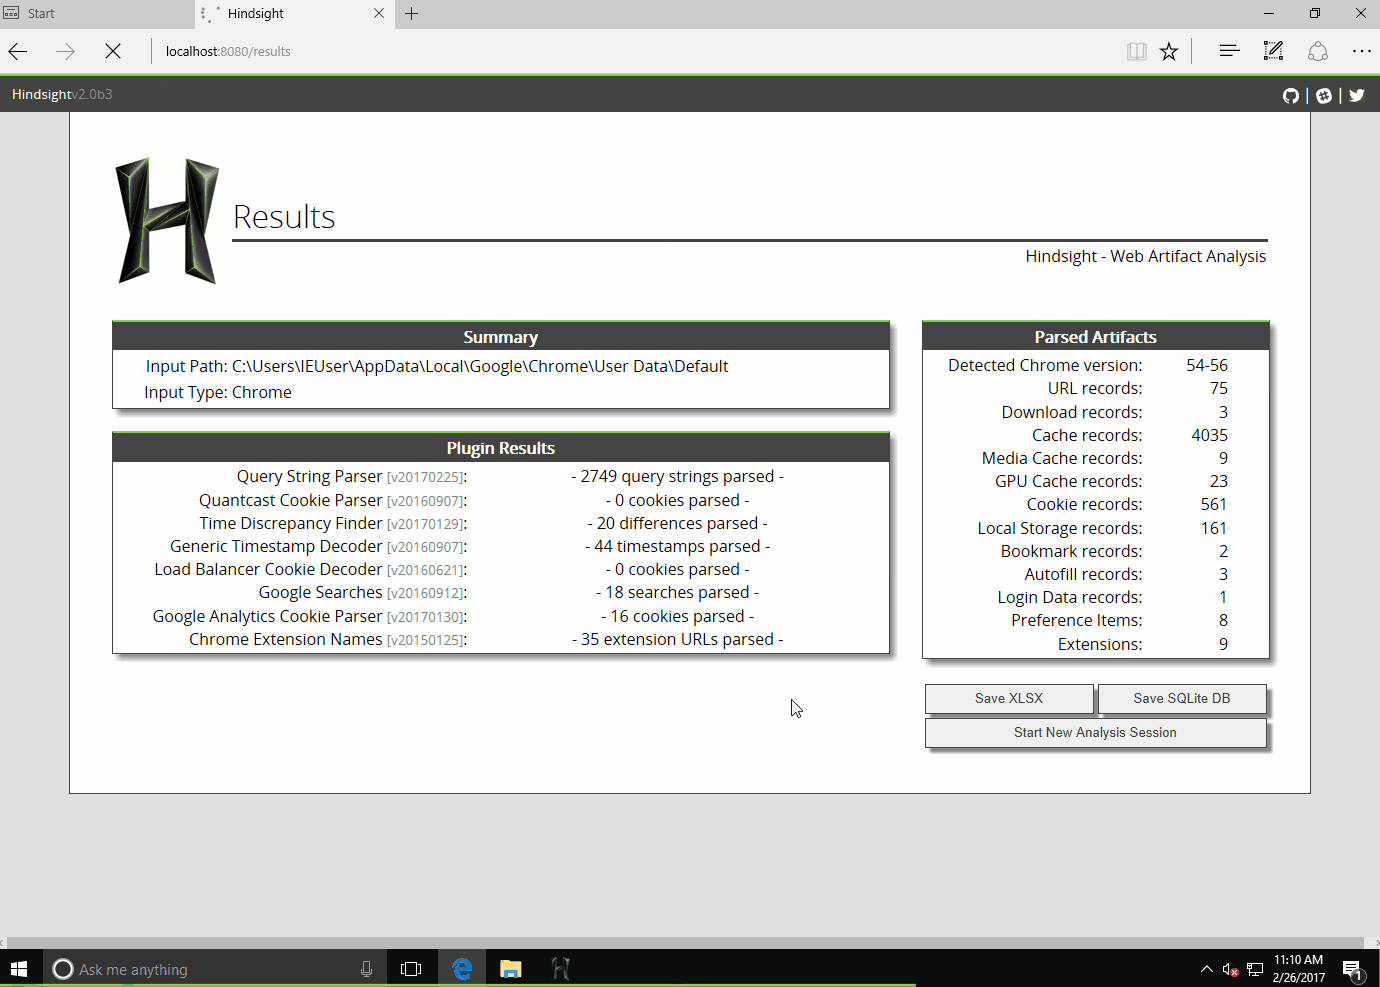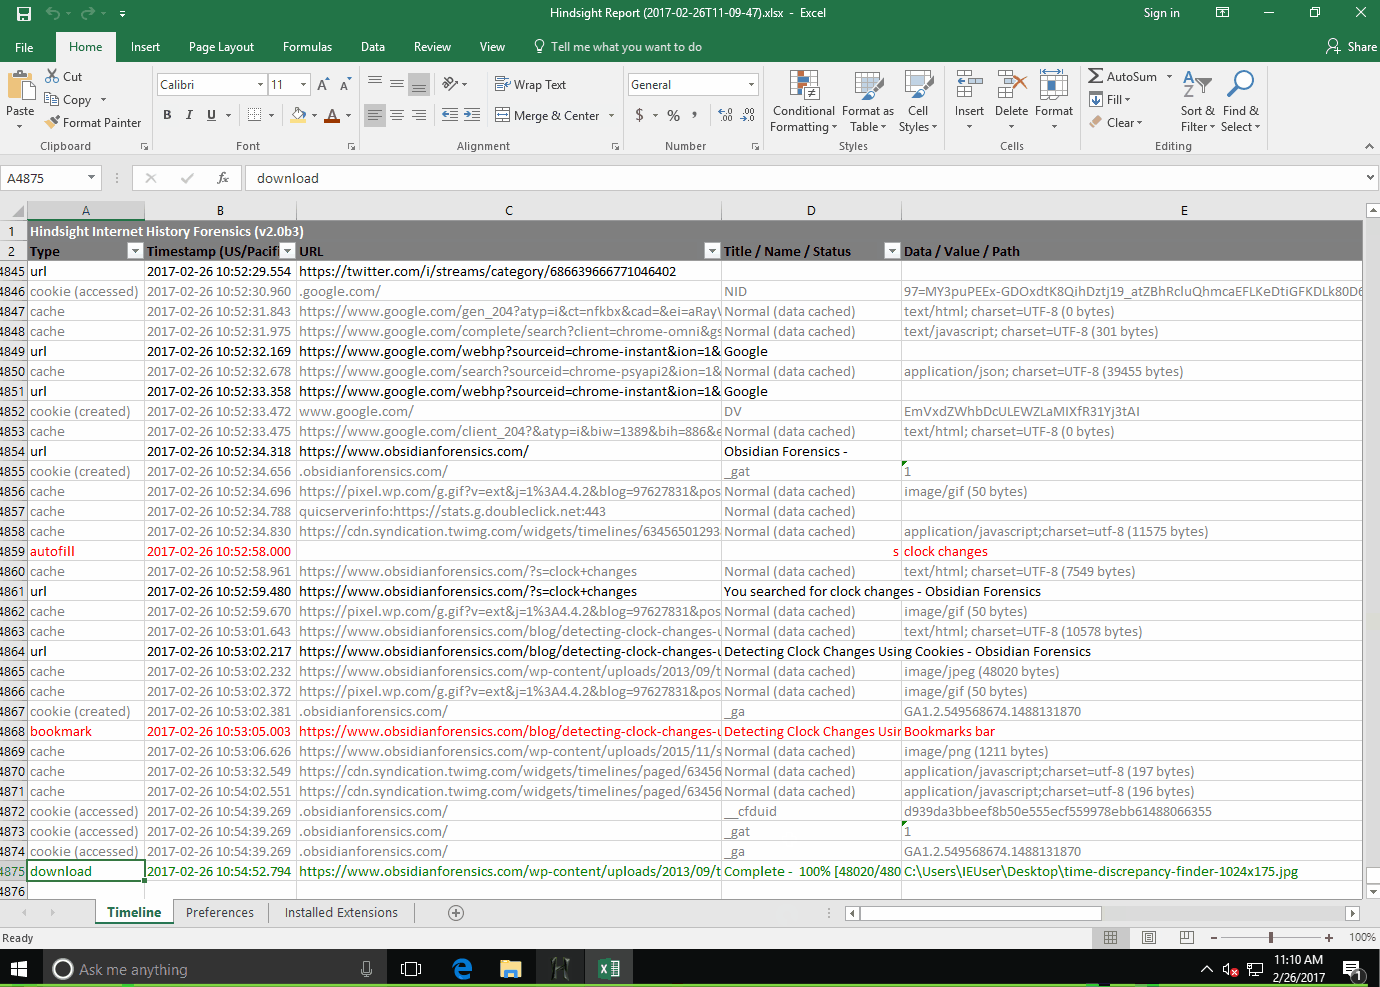 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
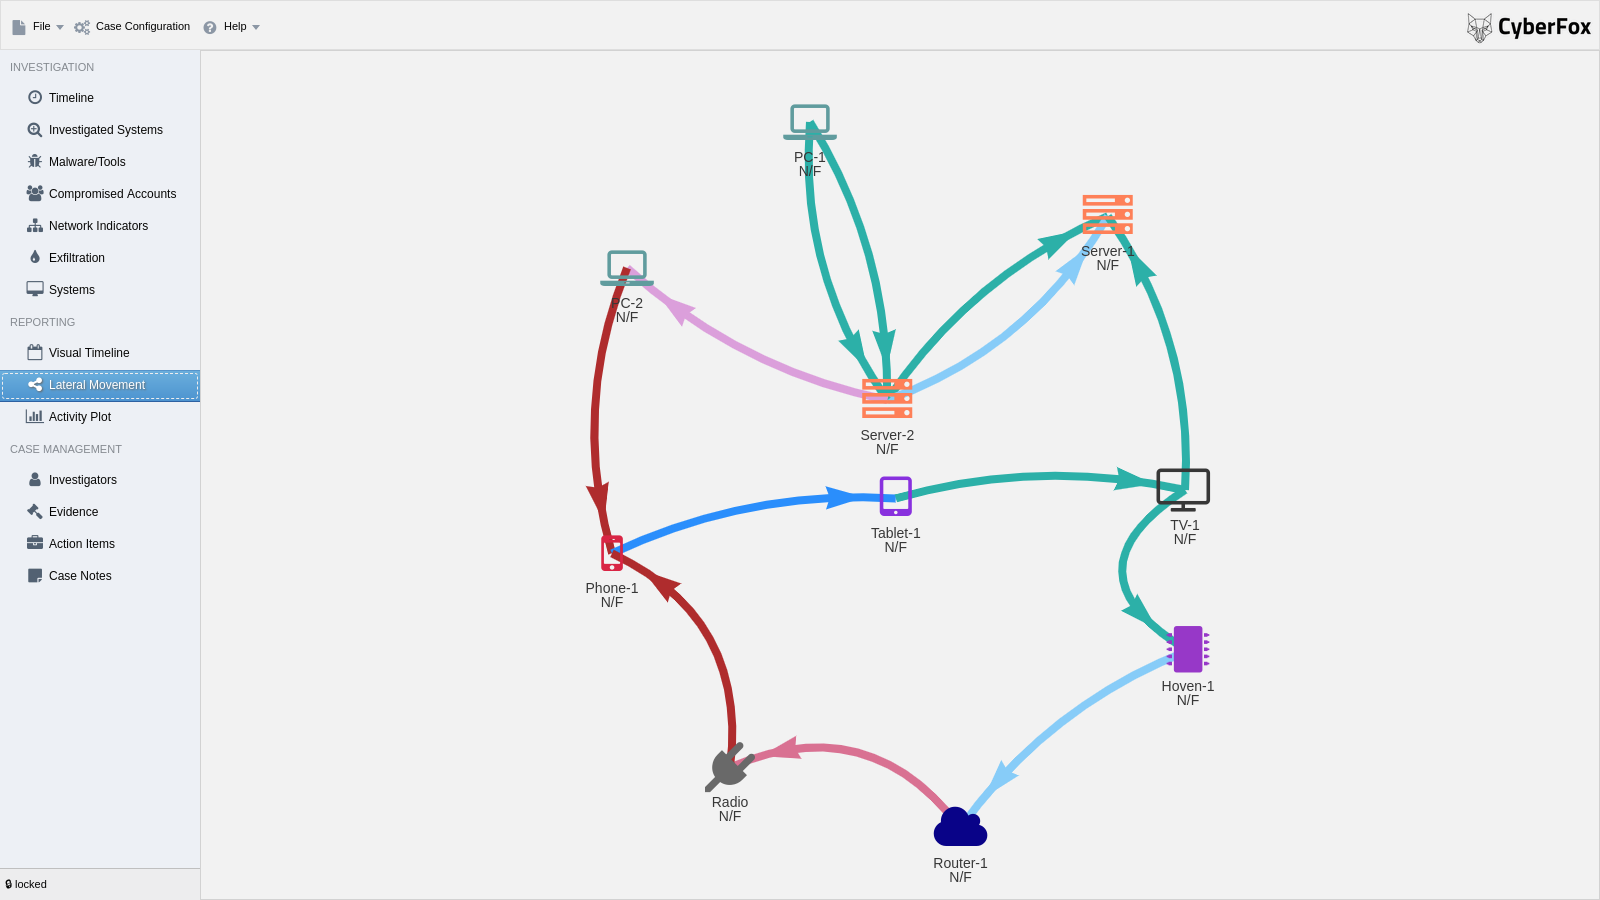 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
