
packetsifterTool
 packetsifter/packetsiftertool
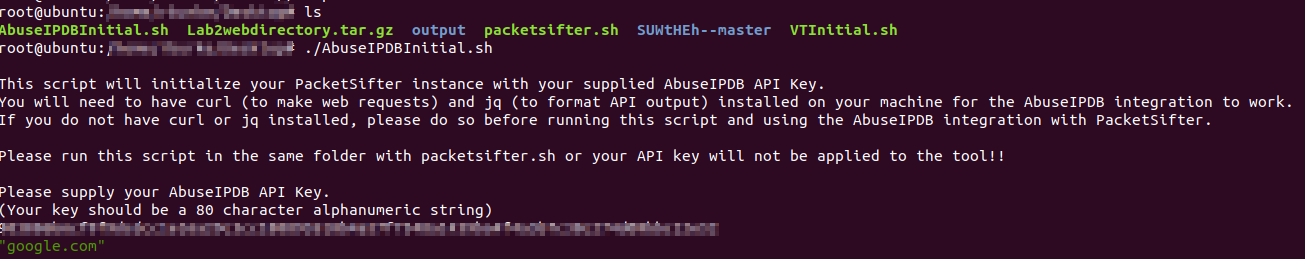
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
93
packetsifter/packetsiftertoolPacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 kulkansecurity/gitxray
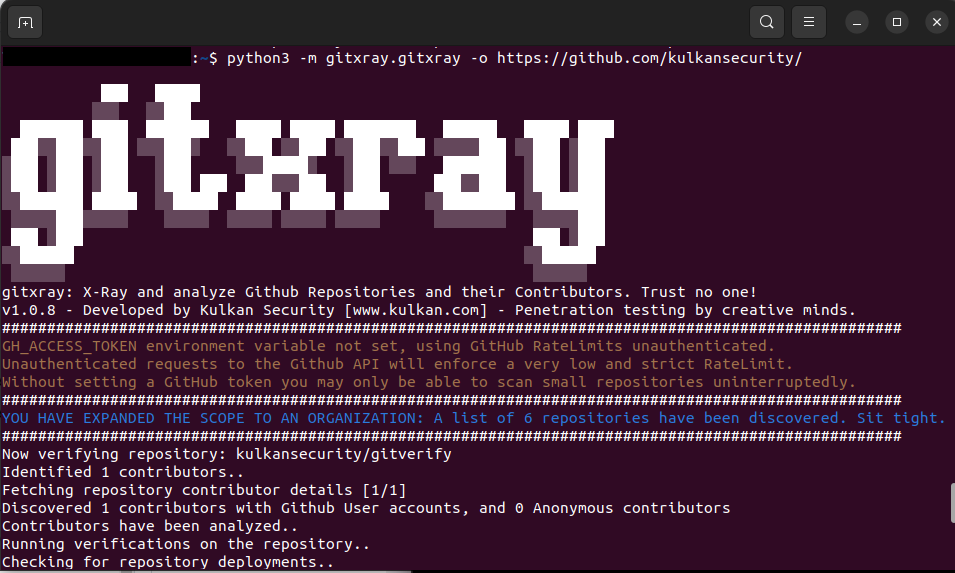
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
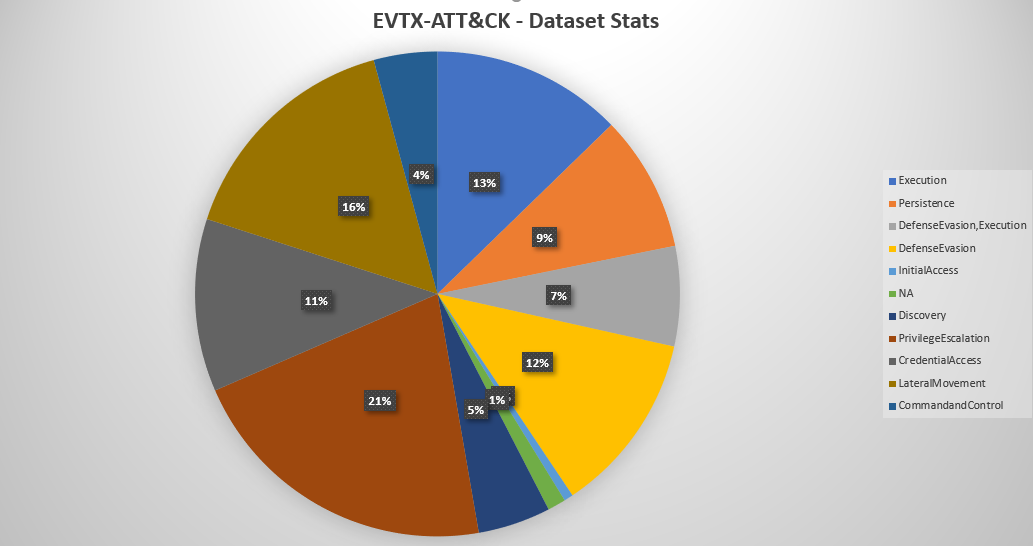 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…
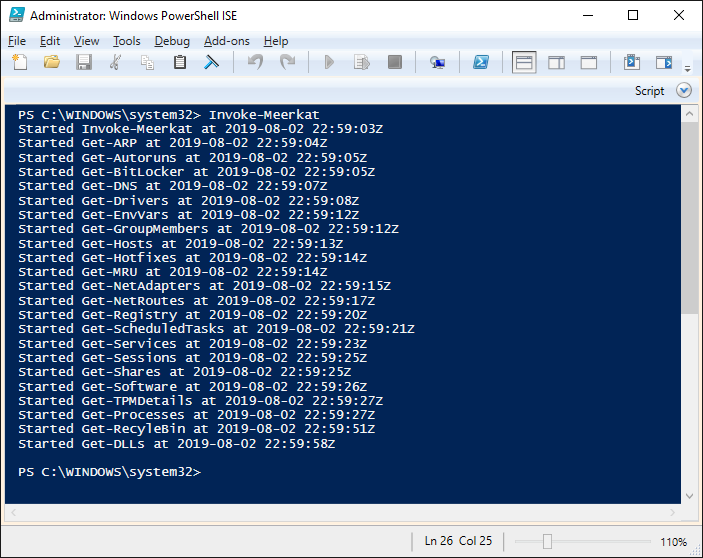 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 kd8bny/limeaide
A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
 matthw/malware_analysis
Python toolkit for malware analysis, designed to inspect suspicious files and extract indicators of compromise for security investigations.
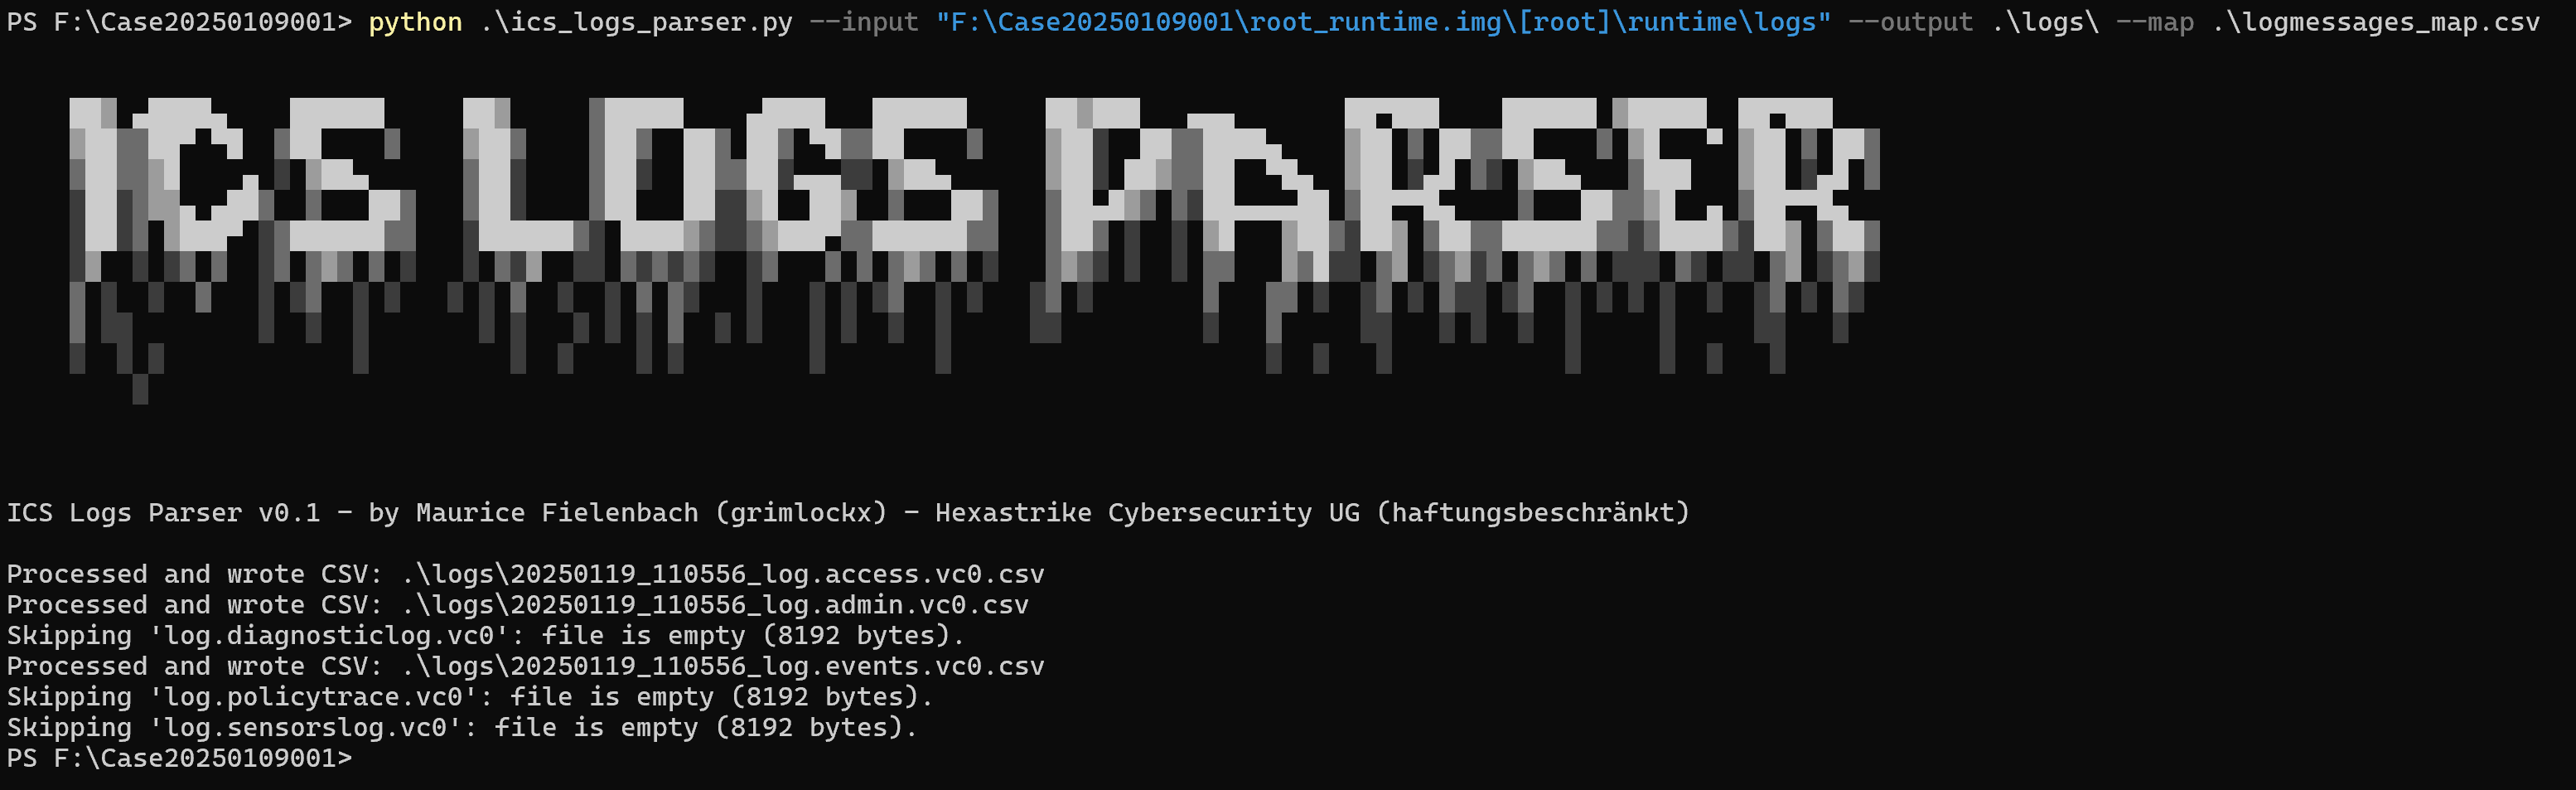 hexastrike/ivanti-connect-secure-logs-parser
A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 cristianzsh/forensictools
Collection of forensic tools