
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
59 results
AIL-framework preview

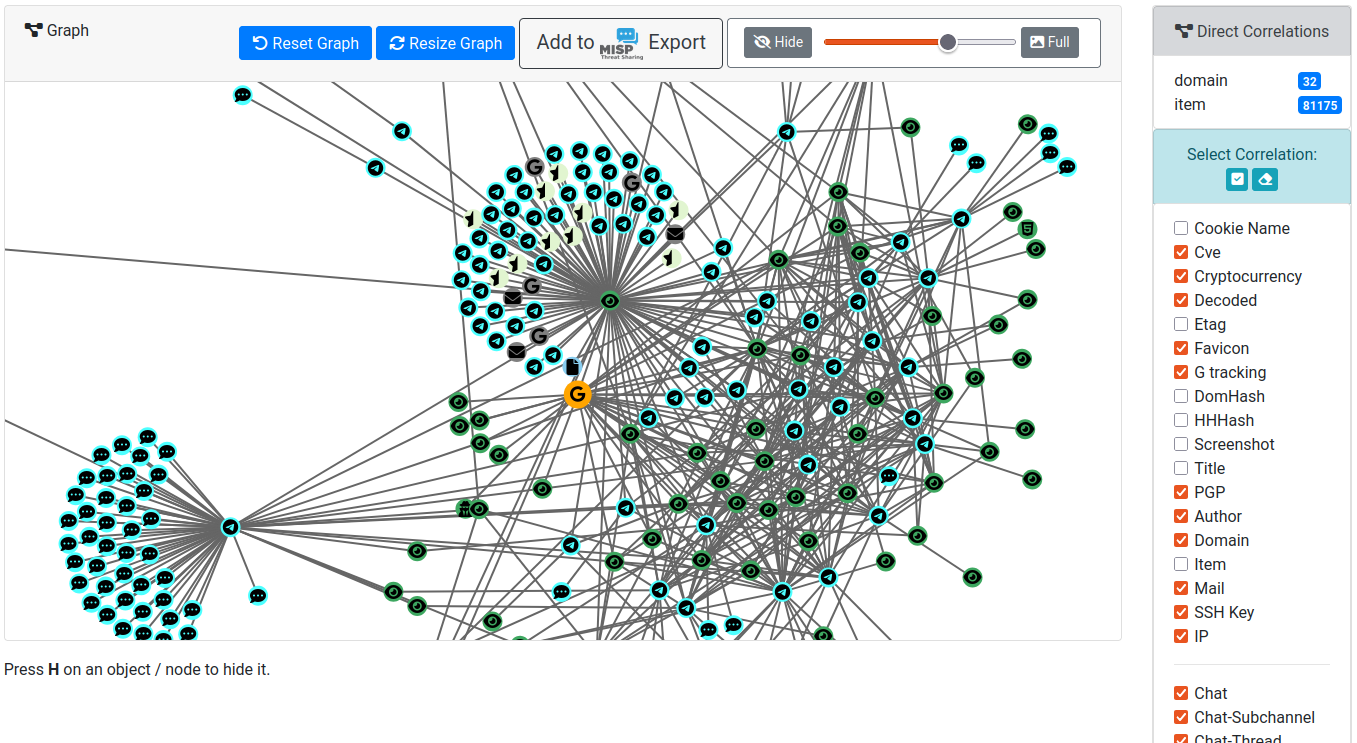
AIL-framework

GitHubcircl/ail-framework

AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
crawlerdata-exfiltrationdigital-forensics+8
1.4k
1 day ago
netlas-cookbook preview

netlas-cookbook

GitHubnetlas-io/netlas-cookbook

The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…

curated-resourcesdigital-forensicseducation+9
89020 days ago
hawk preview

hawk

GitHubt0pcyber/hawk

Powershell Based tool for gathering information related to O365 intrusions and potential Breaches

cloud-infrastructure-securitycloud-securitydigital-forensics+3
9561 year ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8637 years ago
untitledgoosetool preview

untitledgoosetool

GitHubcisagov/untitledgoosetool

Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
cloud-securitydefensive-toolsdigital-forensics+4
9657 months ago
AzureHunter preview

AzureHunter

GitHubdarkquasar/azurehunter

A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365

cloud-securitydigital-forensicsincident-response+3
7923 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
TCPViewer preview

TCPViewer

GitHubproxymanapp/tcpviewer

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
digital-forensicsforensicsinformation-gathering+3
44214h 52m ago
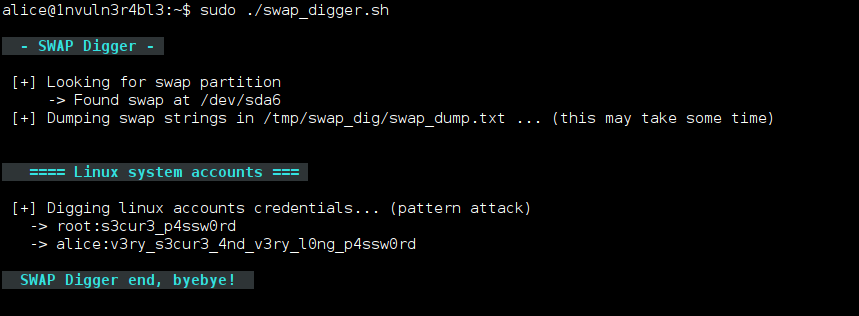
swap_digger preview

swap_digger

GitHubsevagas/swap_digger

Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
digital-forensicsforensicsinformation-gathering+2
5345 years ago
ntdissector preview

ntdissector

GitHubsynacktiv/ntdissector

Active Directory NTDS database parser that dumps records to JSON, supports object filtering, and decrypts encrypted columns using SYSTEM hive or…
digital-forensicsencryption-decryption-toolsinformation-gathering+1
1856 months ago
the-art-of-pivoting preview

the-art-of-pivoting

GitHubadulau/the-art-of-pivoting

The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World

curated-resourcesdigital-forensicseducation+8
1905 months ago
factual-rules-generator preview

factual-rules-generator

GitHubcircl/factual-rules-generator

Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
digital-forensicsforensicsinformation-gathering+1
754 years ago
exif-gps-tracer preview

exif-gps-tracer

GitHubm0n1x90/exif-gps-tracer

A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
digital-forensicsforensicsinformation-gathering+2
445 years ago
linux_screenshot_xwindows preview

linux_screenshot_xwindows

GitHubeurecom-s3/linux_screenshot_xwindows

Volatility plugin to extract X screenshots from a memory dump

digital-forensicsforensicsinformation-gathering+1
378 years ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
421 month ago
MetadataPlus preview

MetadataPlus

GitHubnccgroup/metadataplus

A tool to use novel locations to extract metadata from Office documents.
digital-forensicsforensicsinformation-gathering+1
643 years ago
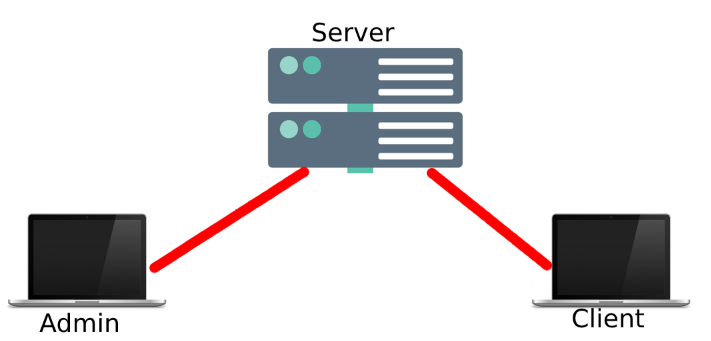
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
digital-forensicsforensicsincident-response+1
226 years ago
ALPC-Enumerator preview

ALPC-Enumerator

GitHubtalha-nazeef-ahmed/alpc-enumerator

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

digital-forensicsinformation-gatheringmalware-analysis+4
301 month ago
Previous1234Next