

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
MESH preview

MESH

GitHubbarghest-ngo/mesh

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
android-securitydigital-forensicsencryption-decryption-tools+8
211
7 days ago
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
digital-forensicsdns-analysisforensics+9
2.6k16h 22m ago
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
digital-forensicsids-ips-evasioninformation-gathering+4
12 months ago
security-onion preview
Archived

security-onion

GitHubsecurity-onion-solutions/security-onion

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
digital-forensicsdns-analysisids-ips-evasion+5
3.1k5 years ago
DetectRaptor preview

DetectRaptor

GitHubmgreen27/detectraptor

A repository to share publicly available Velociraptor detection content
digital-forensicsincident-responseintrusion-detection+4
2094 days ago
community-id-spec preview

community-id-spec

GitHubcorelight/community-id-spec

An open standard for hashing network flows into identifiers, a.k.a "Community IDs".

digital-forensicsincident-responseintrusion-detection+4
1982 years ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

anomaly-detectiondigital-forensicsincident-response+5
42 months ago
SentinelThread-Forensics preview

SentinelThread-Forensics

GitHubadham504/sentinelthread-forensics

High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
digital-forensicsforensicsincident-response+5
36 months ago
sysmon-modular preview

sysmon-modular

GitHubolafhartong/sysmon-modular

A repository of sysmon configuration modules
defensive-toolsdigital-forensicsincident-response+2
3.2k16 days ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
digital-forensicsincident-responseintrusion-detection+2
2.4k3 years ago
py preview

py

GitHubantiwar3/py

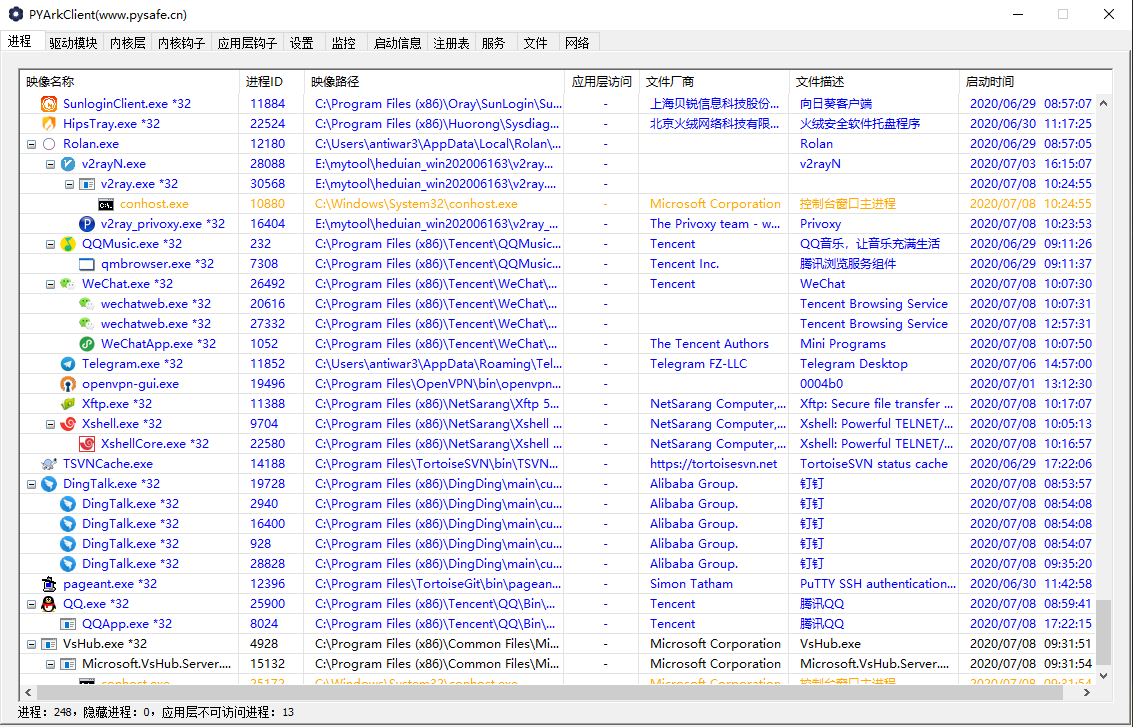
飘云ark(pyark)

defensive-toolsdigital-forensicsincident-response+3
5372 months ago
Yara-rules preview

Yara-rules

GitHubbartblaze/yara-rules

Collection of private Yara rules.
defensive-toolsdigital-forensicsincident-response+3
3929 months ago
Loki-RS preview

Loki-RS

GitHubneo23x0/loki-rs

🐍 High-performance, multi-threaded YARA & IOC scanner
digital-forensicsforensicsincident-response+7
3641 month ago
citrix-2025 preview

citrix-2025

GitHubncsc-nl/citrix-2025

Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
digital-forensicsforensicsincident-response+2
551 year ago
yaml2yara preview

yaml2yara

GitHubnccgroup/yaml2yara

Generate bulk YARA rules from YAML input
digital-forensicsincident-responseintrusion-detection+4
226 years ago
Security_incident_report preview

Security_incident_report

GitHubkevin9480/security_incident_report

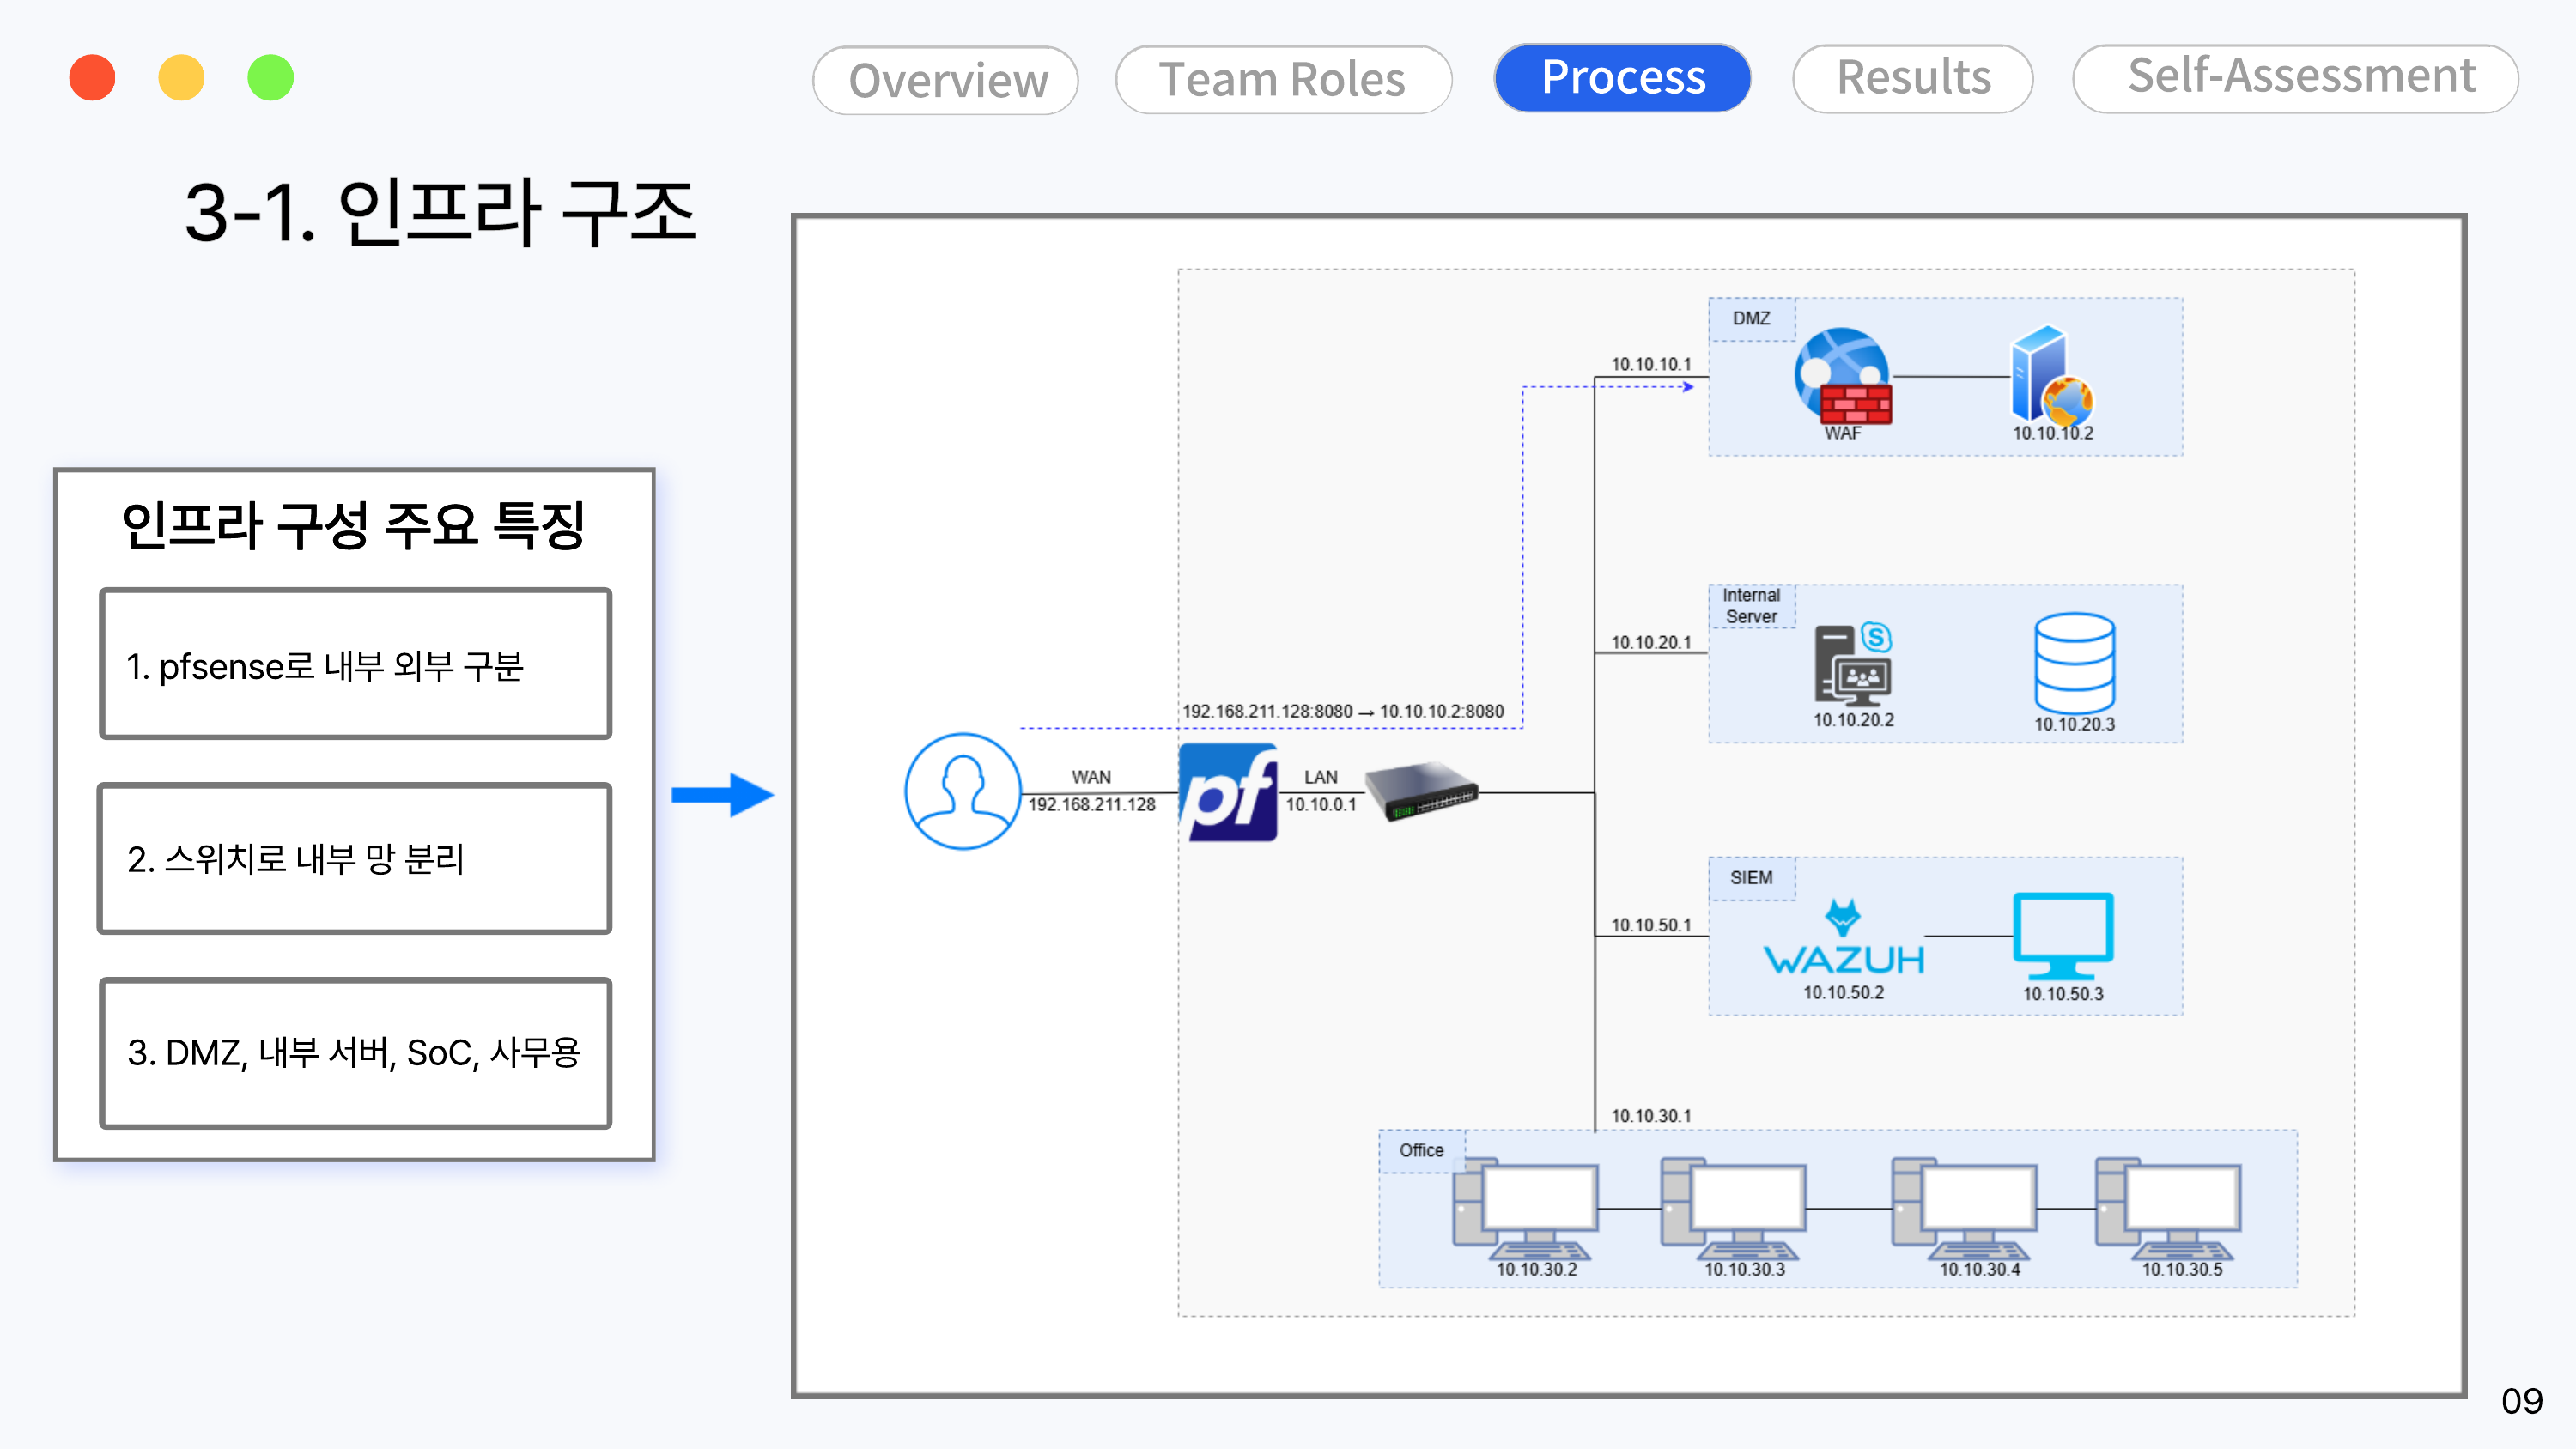
React2Shell(CVE-2025-55182) 취약점 기반 침해 시나리오를 재현하고, Wazuh/Sysmon/Coraza WAF 로그로 침해사고를 분석·대응한 DFIR 프로젝트
digital-forensicsincident-responseintrusion-detection+5
2 months ago
cpanel-cve-41940-detector preview

cpanel-cve-41940-detector

GitHublimo57640-crypto/cpanel-cve-41940-detector

Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
digital-forensicsforensicsincident-response+6
4 months ago
Detection preview

Detection

GitHubsifalcon/detection

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…

curated-resourcesdigital-forensicsincident-response+4
243 years ago
Previous12Next