
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
androidqf preview

androidqf

GitHubbotherder/androidqf

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
android-securitydigital-forensicsforensics+2
310
7 months ago
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
digital-forensicsforensicshash-analysis+4
292 years ago
dfir-malware-investigation preview

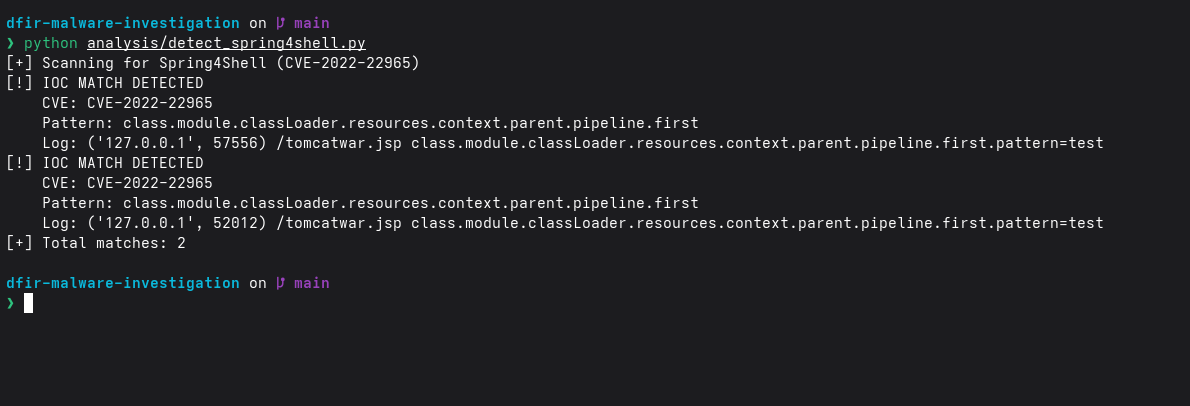
dfir-malware-investigation

GitHubsuyash-r-k/dfir-malware-investigation

Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
digital-forensicseducationincident-response+9
7 months ago
kirjuri preview
Archived

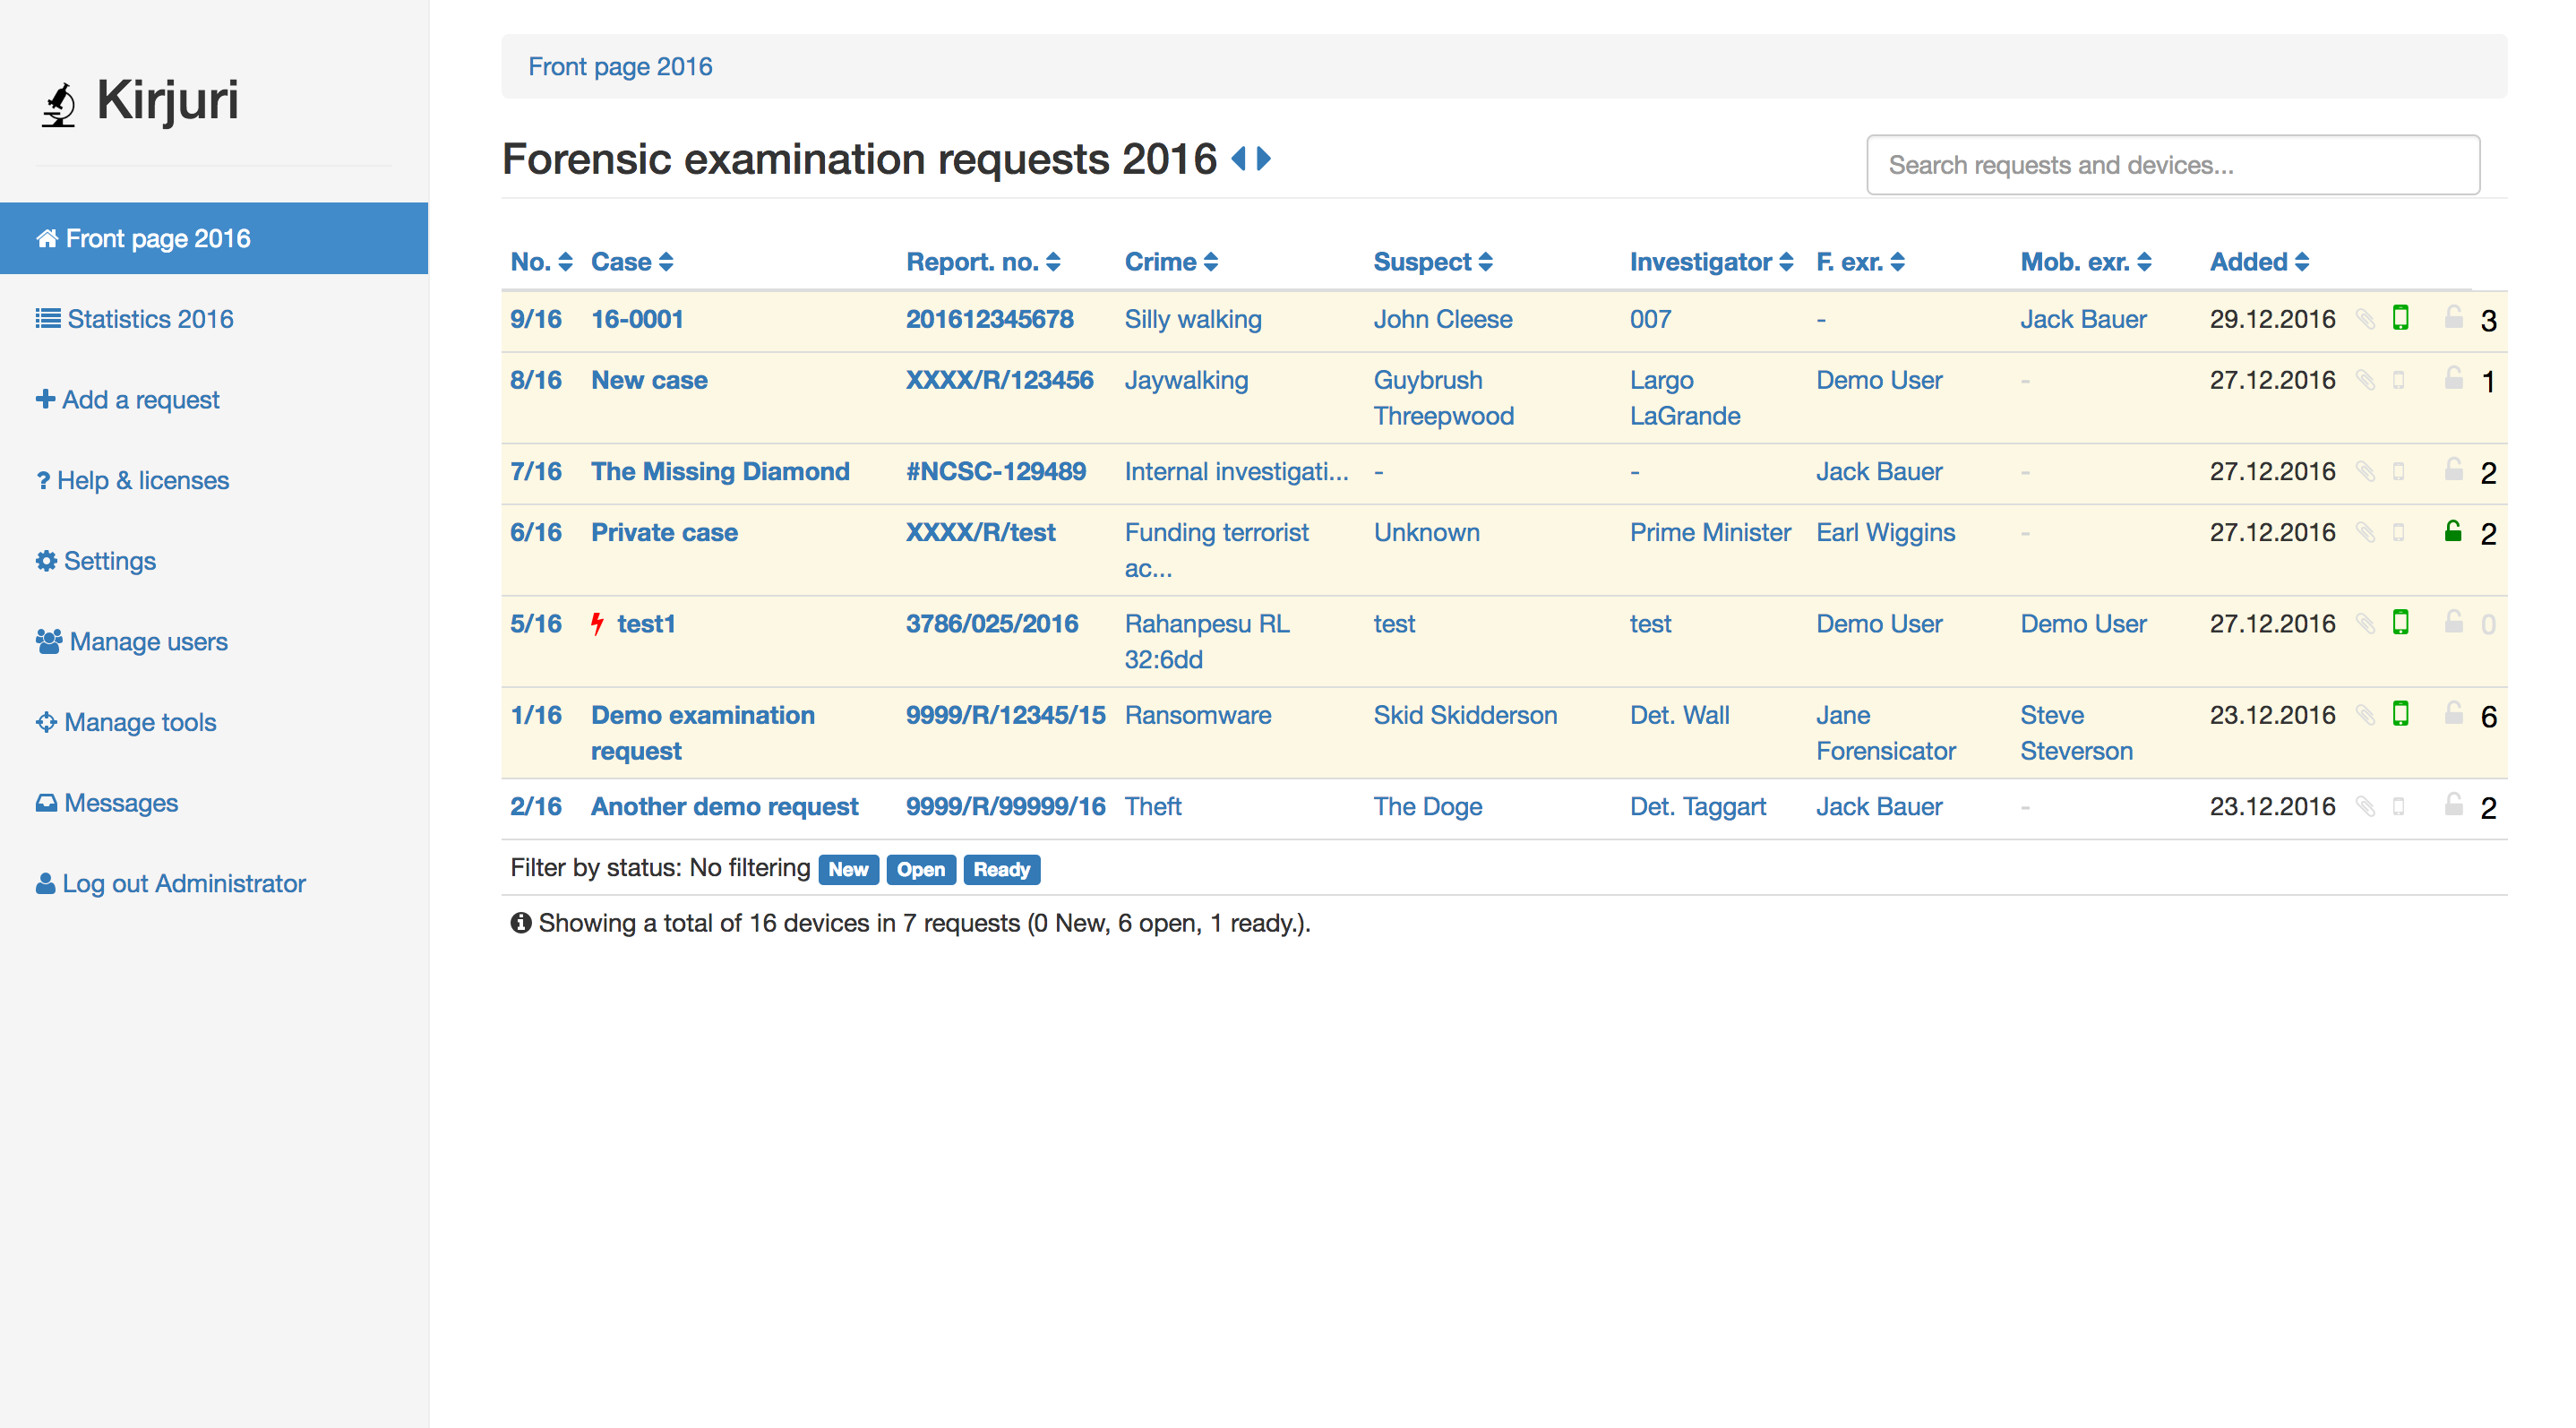
kirjuri

GitHubanttikurittu/kirjuri

Kirjuri is a web application for managing cases and physical forensic evidence items.
digital-forensicsforensicsincident-response
1094 months ago
Security-Datasets preview

Security-Datasets

GitHubotrf/security-datasets

Re-play Security Events
ctfcurated-resourcesdigital-forensics+4
1.8k3 years ago
KNX-Bus-Dump preview

KNX-Bus-Dump

GitHubchrism09/knx-bus-dump

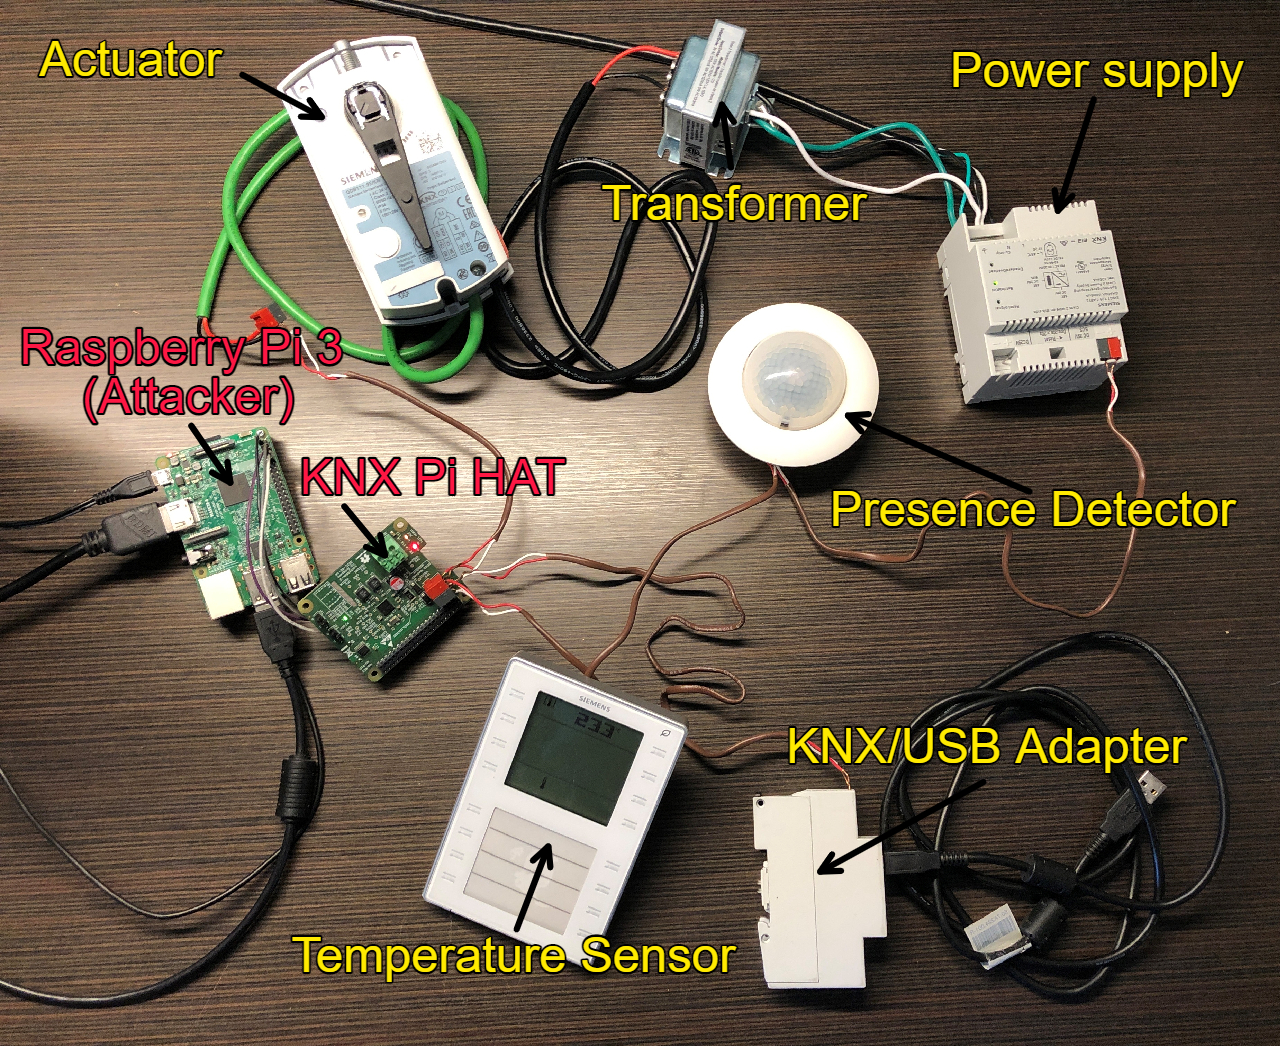
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
digital-forensicsforensicshardware-iot-security+3
124 years ago
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

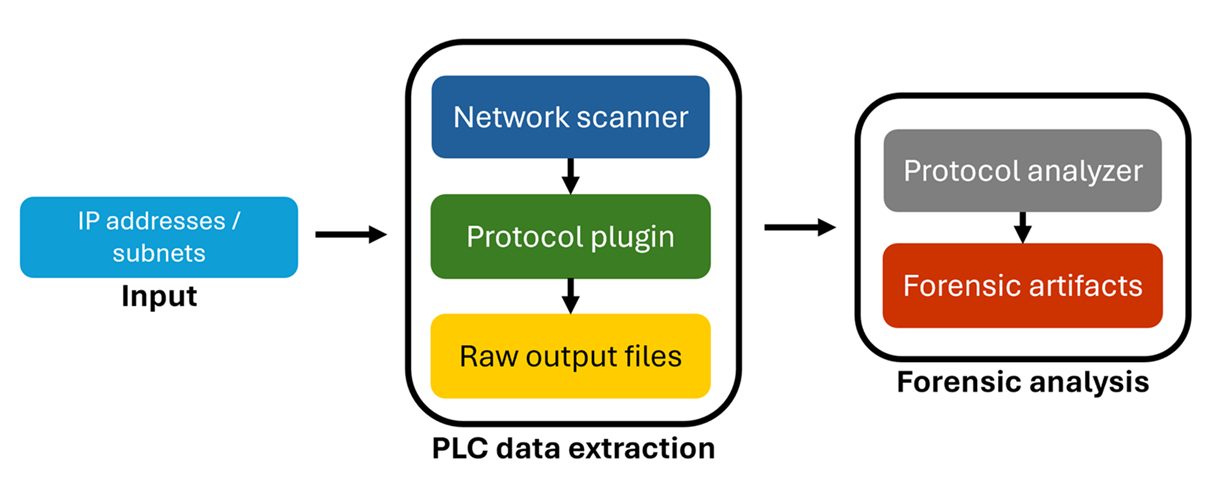
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
digital-forensicsforensicsincident-response+2
3741 year ago
AIL-framework preview

AIL-framework

GitHubcircl/ail-framework

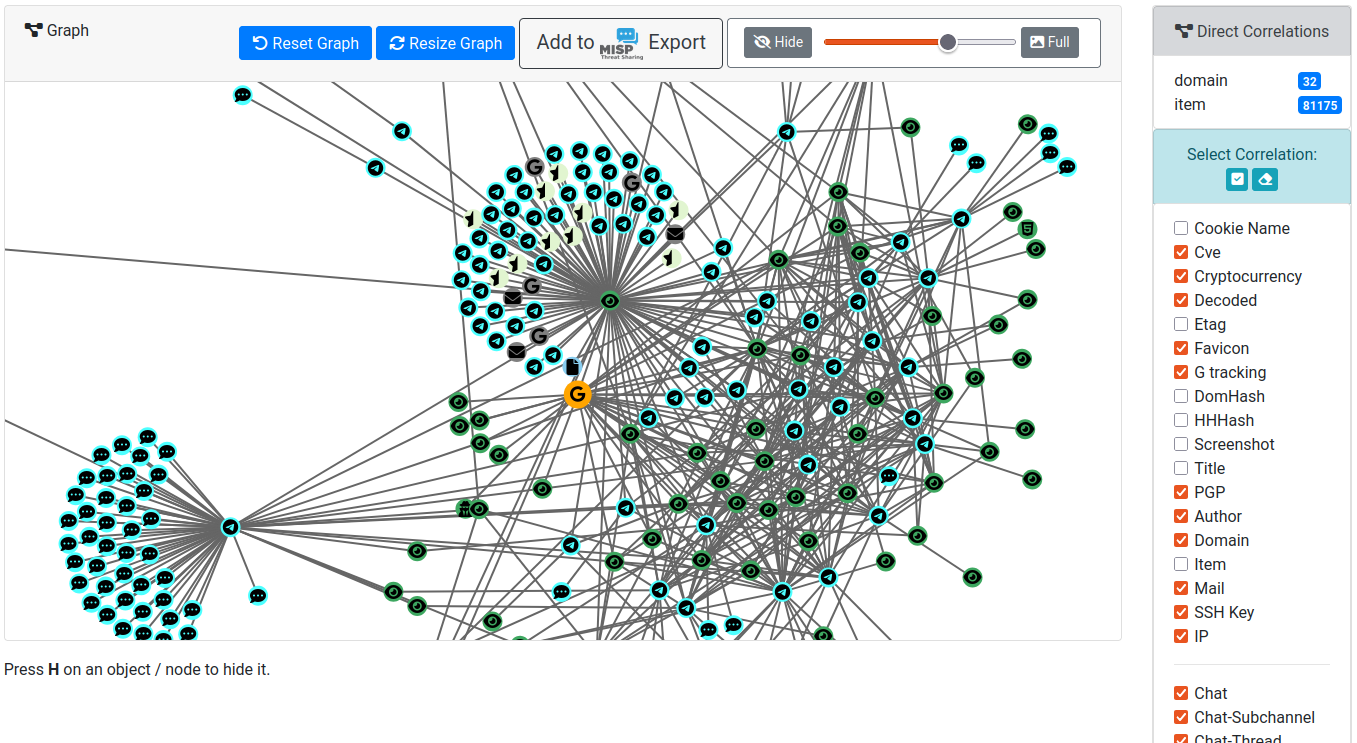
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
crawlerdata-exfiltrationdigital-forensics+8
1.4k2 days ago
OSINT_Inception-links preview

OSINT_Inception-links

GitHubc3n7ral051nt4g3ncy/osint_inception-links

Current links from the OSINT Inception start-me project
curated-resourcesdigital-forensicseducation+3
2223 years ago
cybersecurity-projects preview

cybersecurity-projects

GitHubosxninja/cybersecurity-projects

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…


ai-securitycurated-resourcesdigital-forensics+7
289 days ago
ParrotSec-Linux-Hardening-Project preview

ParrotSec-Linux-Hardening-Project

GitLabxe1phix/parrotlinux-public-kiosk-project

Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…

configuration-auditingdigital-forensicsforensics+3
31 month ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3232 years ago
dumpzilla preview

dumpzilla

GitHubbusindre/dumpzilla

Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
digital-forensicsforensicsinformation-gathering+1
1489 months ago
BlueTeam.Lab preview

BlueTeam.Lab

GitHubop7ic/blueteam.lab

Blue Team detection lab created with Terraform and Ansible in Azure.

cloud-securityconfiguration-auditingdefensive-tools+7
1911 year ago
factual-rules-generator preview

factual-rules-generator

GitHubcircl/factual-rules-generator

Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
digital-forensicsforensicsinformation-gathering+1
754 years ago
yaml2yara preview

yaml2yara

GitHubnccgroup/yaml2yara

Generate bulk YARA rules from YAML input

digital-forensicsincident-responseintrusion-detection+4
226 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
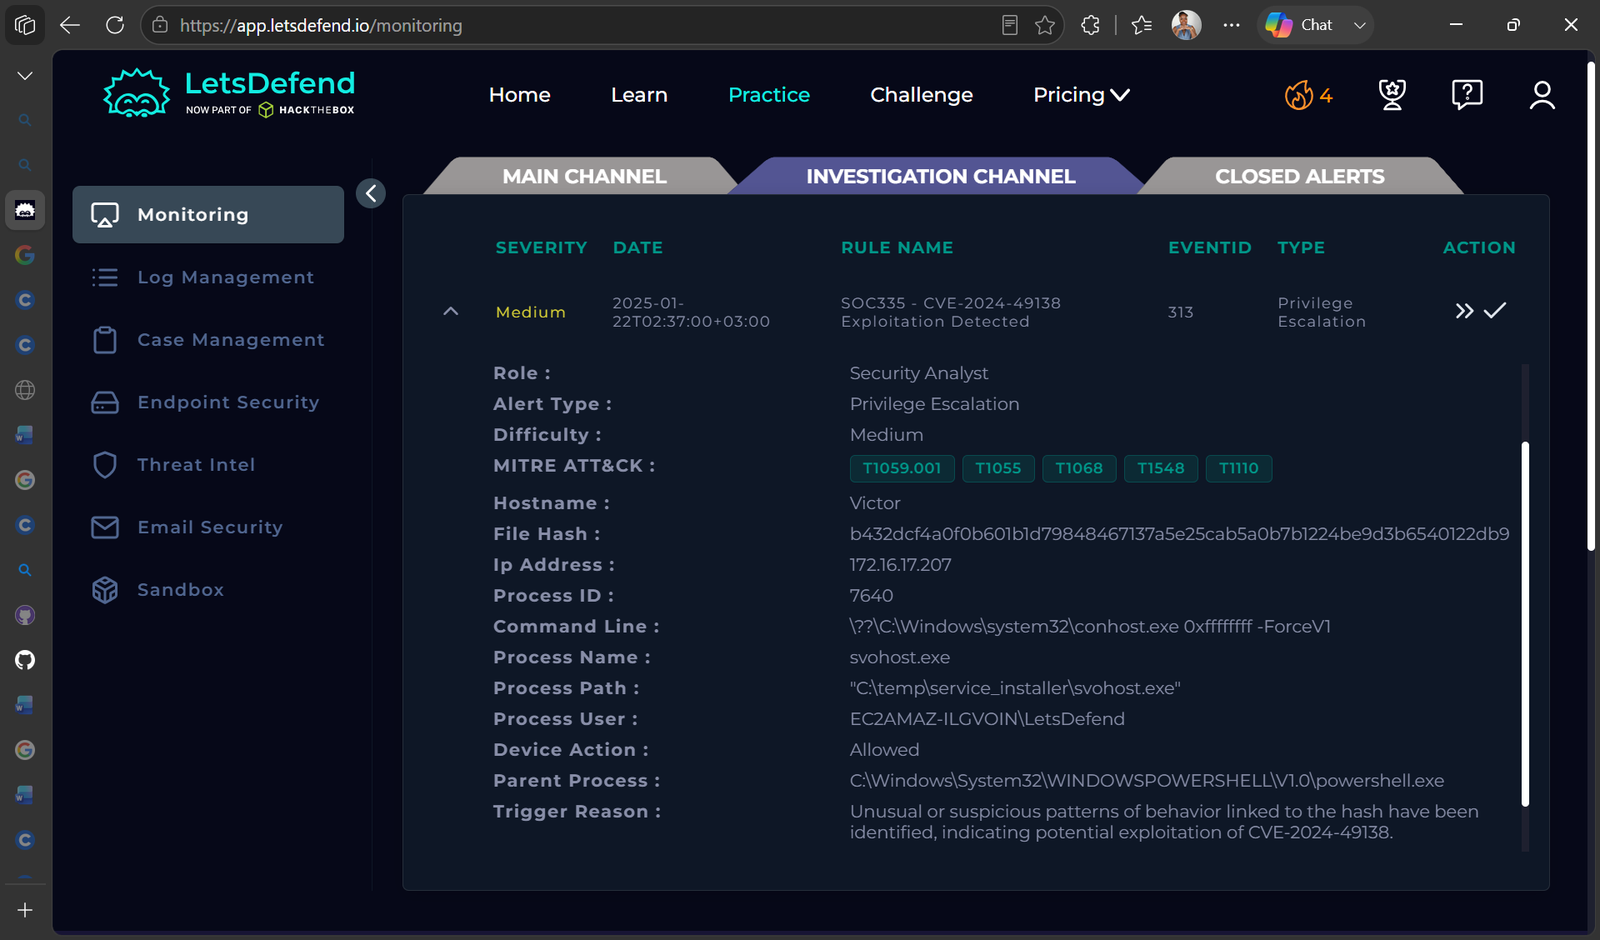
SOC335-CVE-2024-49138-Investigation preview

SOC335-CVE-2024-49138-Investigation

GitHubnadineelliottcyber/soc335-cve-2024-49138-investigation

SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.

curated-resourcesdigital-forensicseducation+3
28 days ago
Previous12Next