
ntfstool
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
data-recoverydigital-forensicsdisk-forensics+3
thewhiteninja/ntfstoolForensics tool for NTFS (parser, mft, bitlocker, deleted files)
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
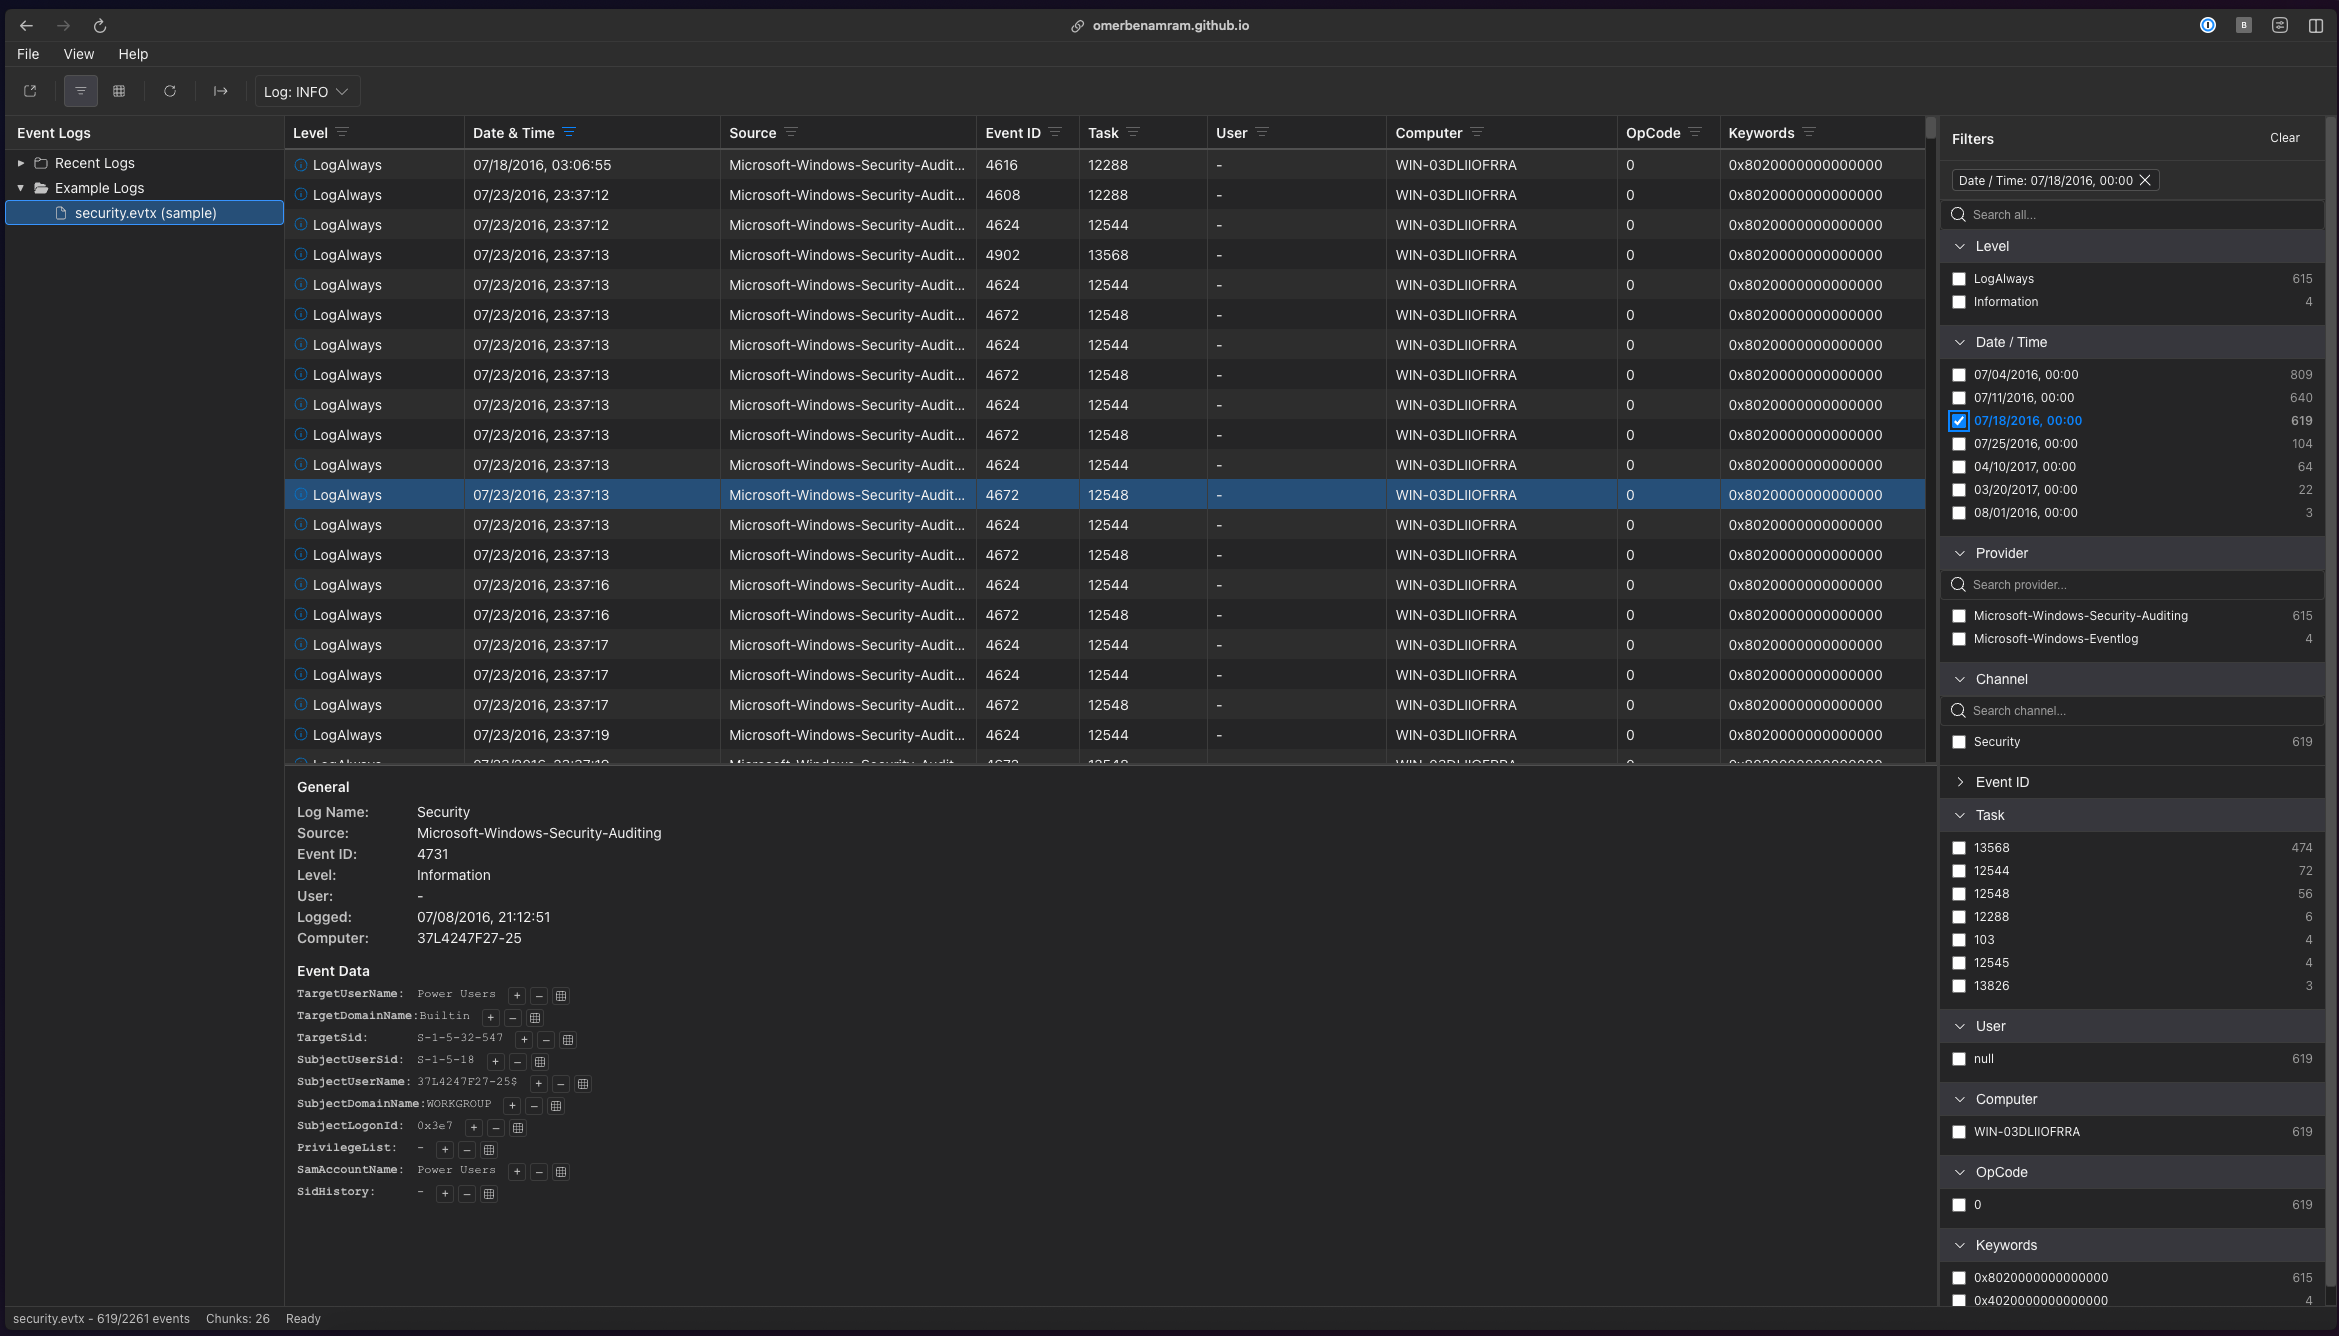 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
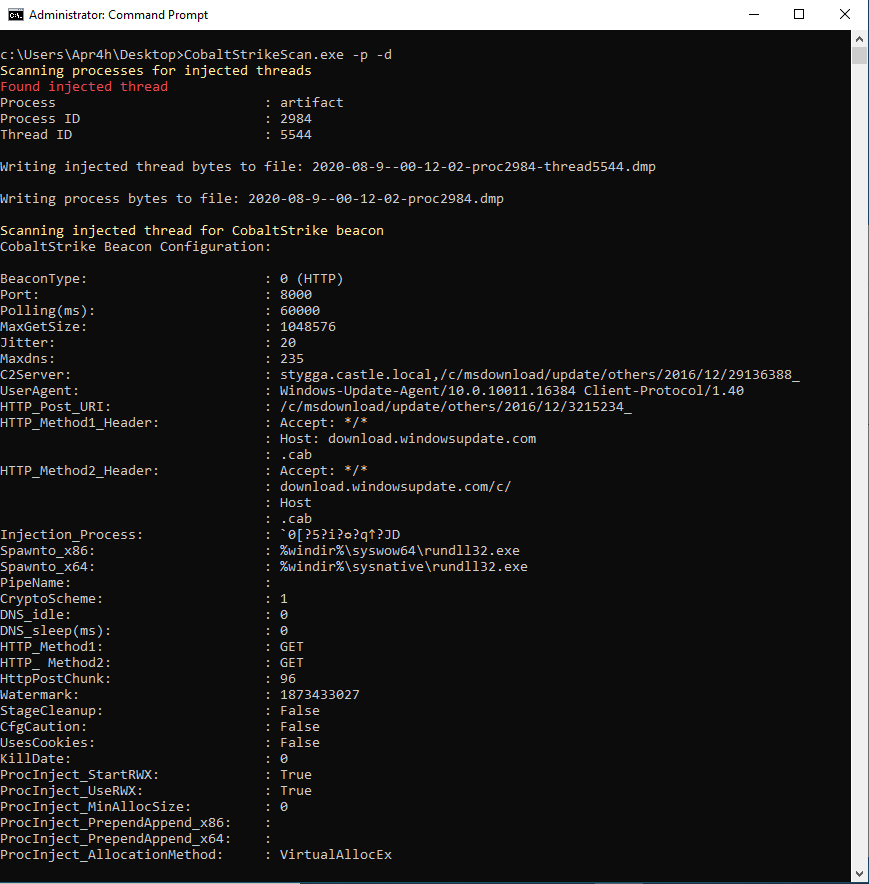 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 synacktiv/ntdissector
Active Directory NTDS database parser that dumps records to JSON, supports object filtering, and decrypts encrypted columns using SYSTEM hive or…
 jschicht/logfileparser
Parser for $LogFile on NTFS
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
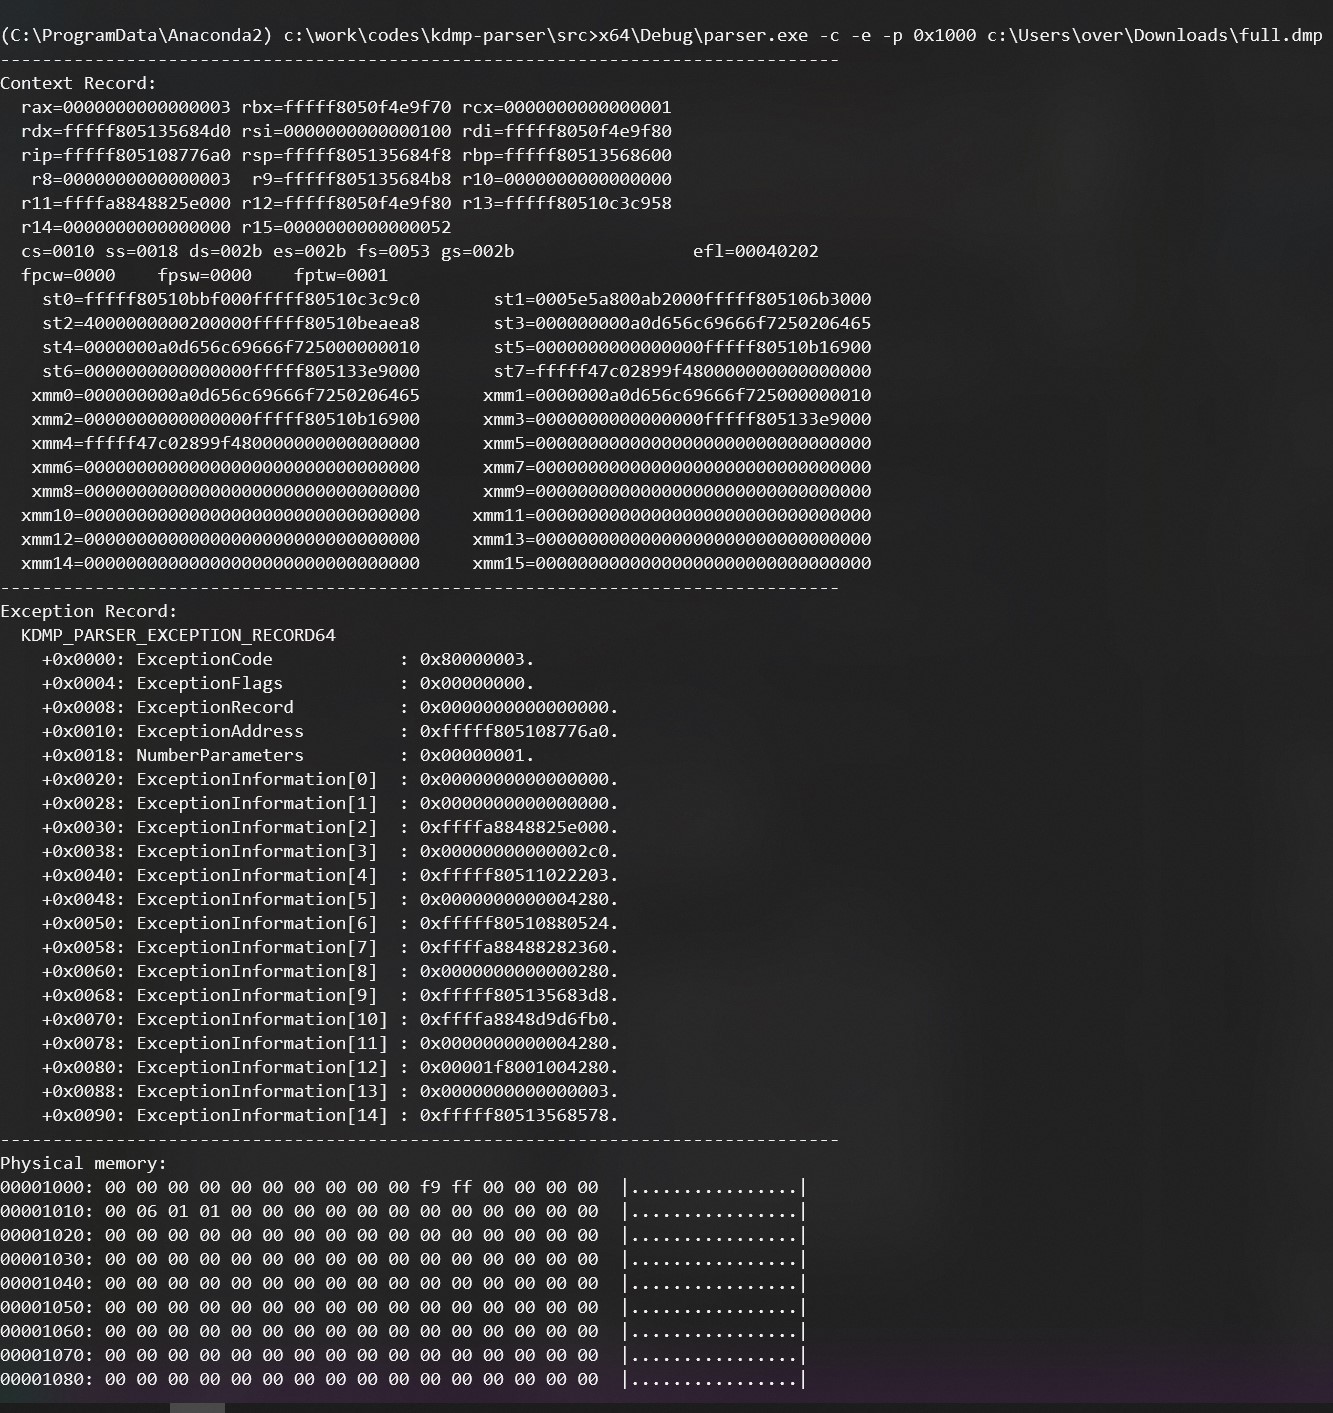 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
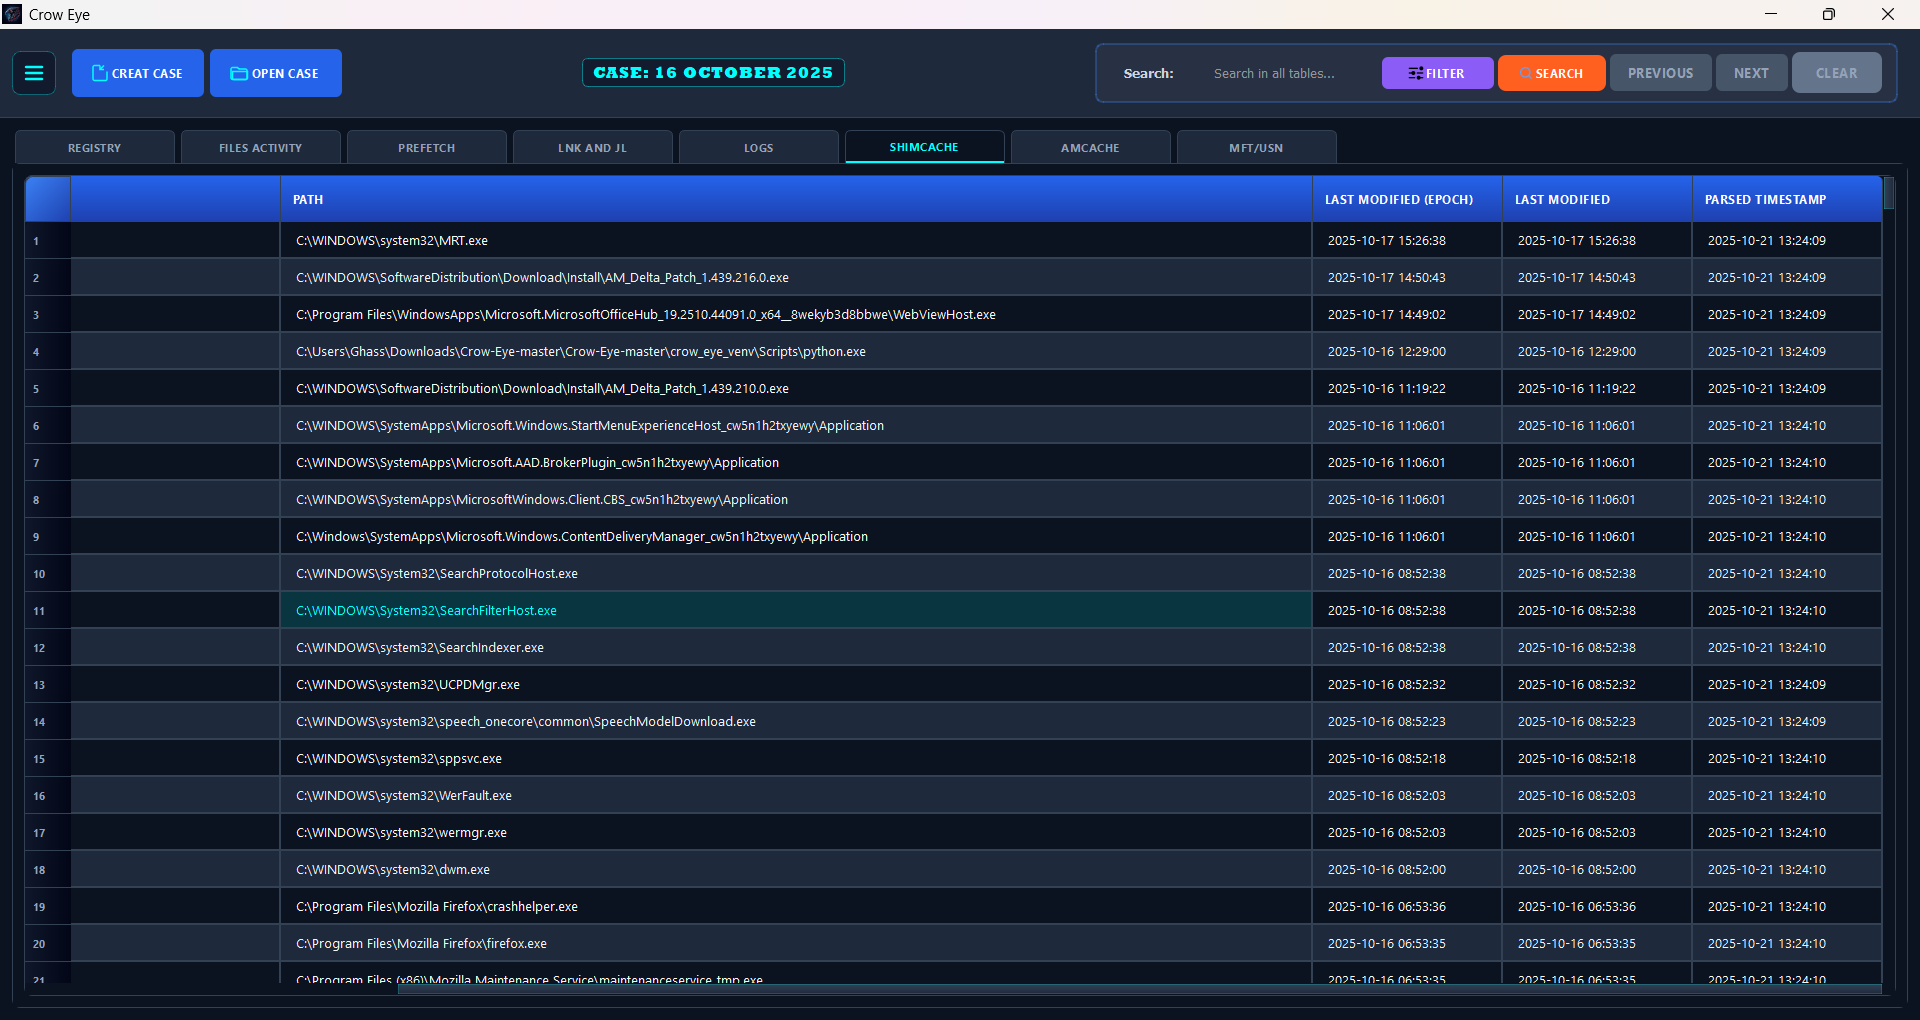 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…