soc-investigation-powershell-edrfreeze

SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

Kalim backdooe Malware Report

Data from a BRAWL Automated Adversary Emulation Exercise

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

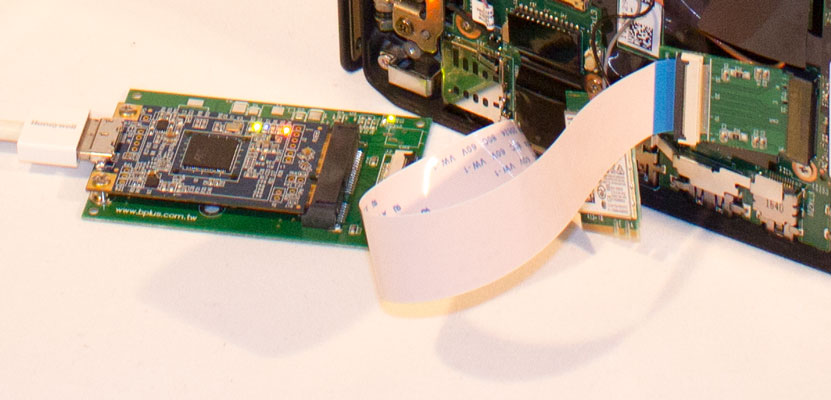
Direct Memory Access (DMA) Attack Software

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

Mimikatz implementation in pure Python

Some usefull Scripts and Executables for Pentest & Forensics

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…

Malicious HTTP traffic explorer

Extract Windows credentials directly from VM memory snapshots and virtual disks

Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…

[Linux] Two Privilege Escalation techniques abusing sudo token

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

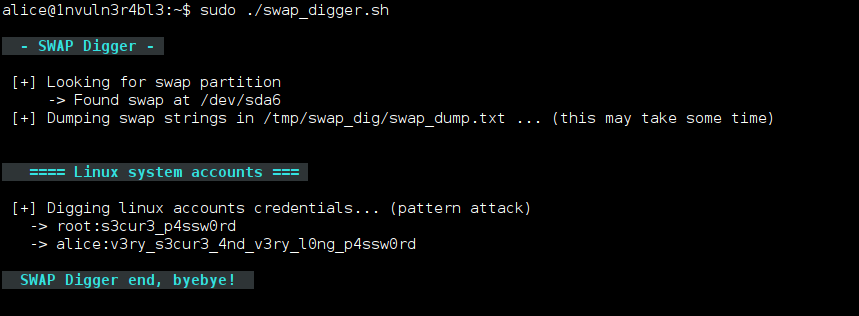
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

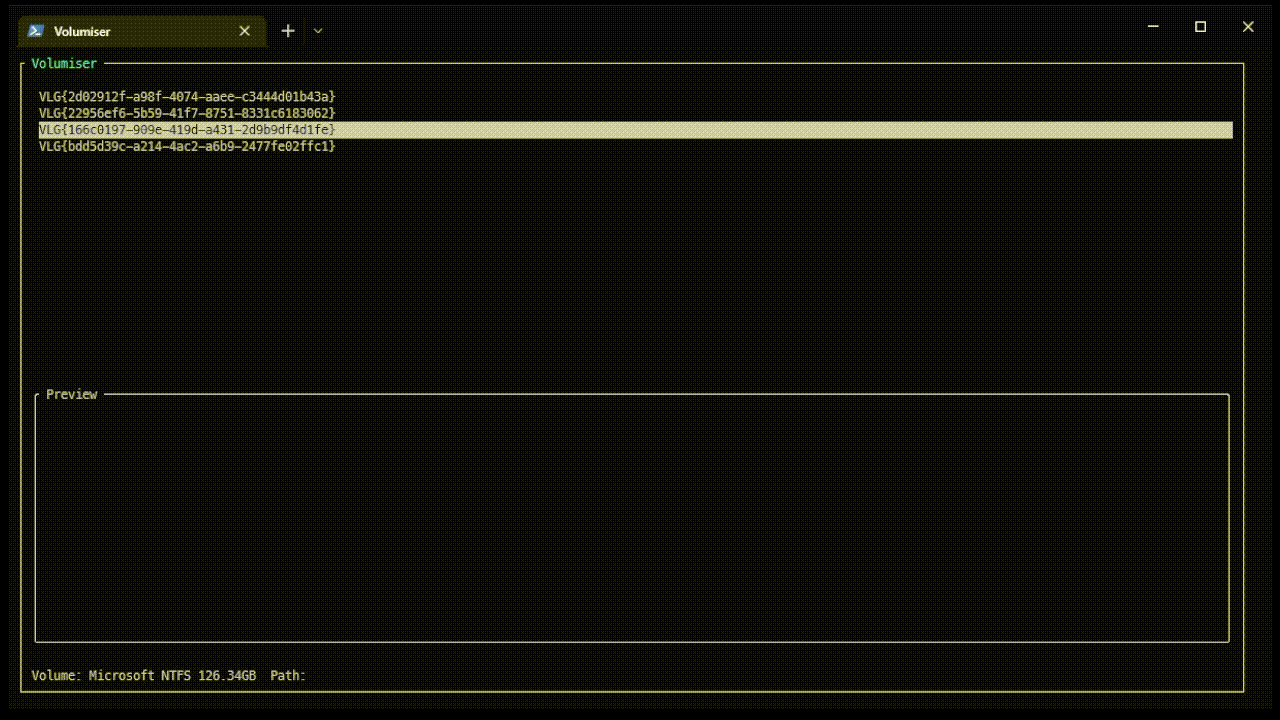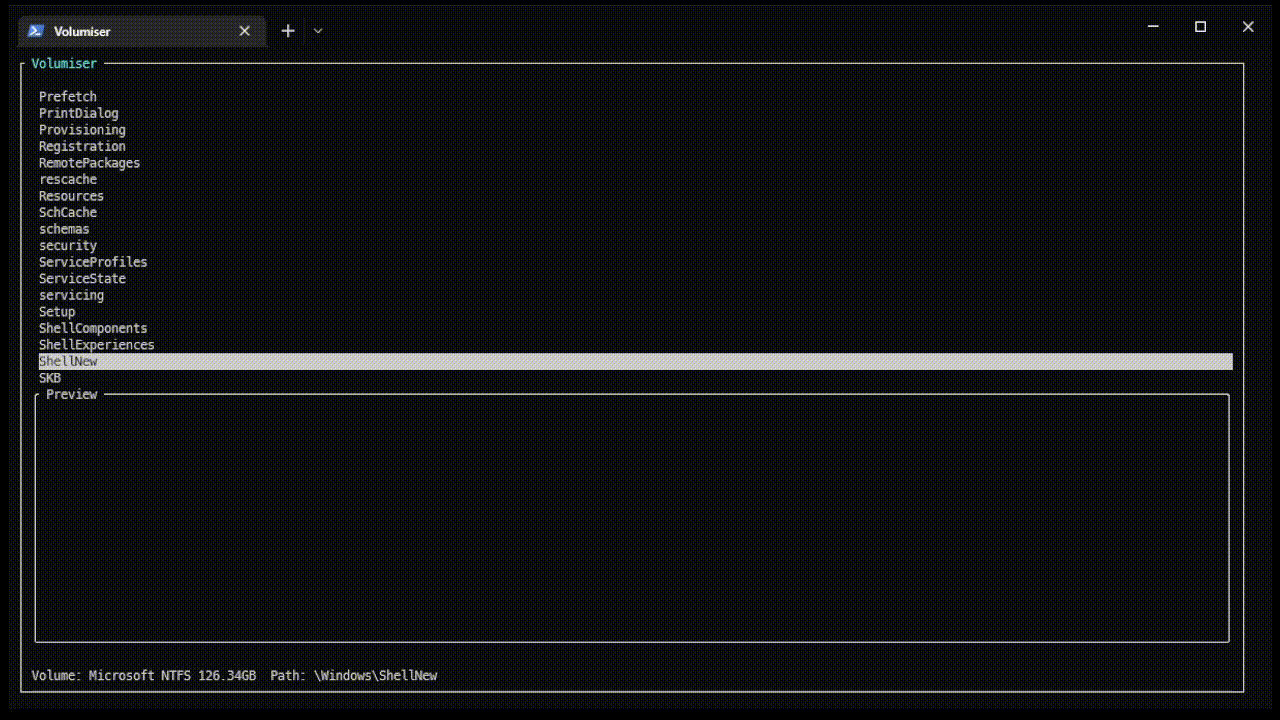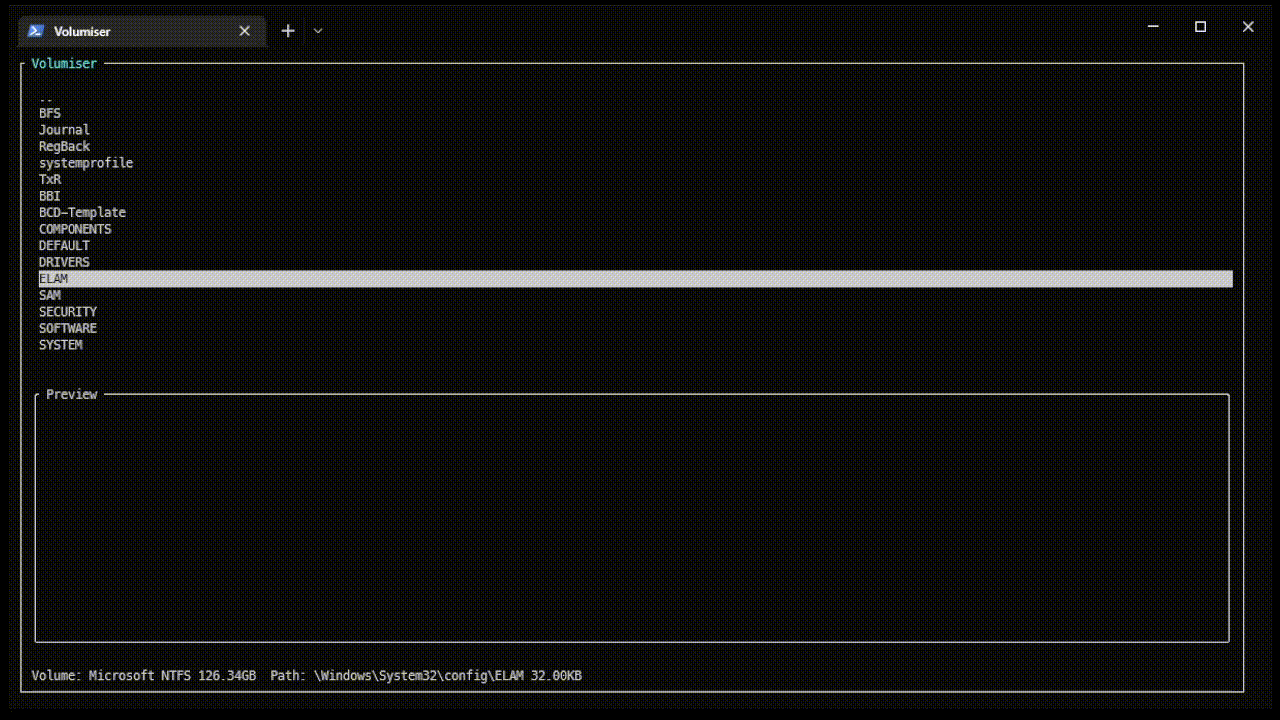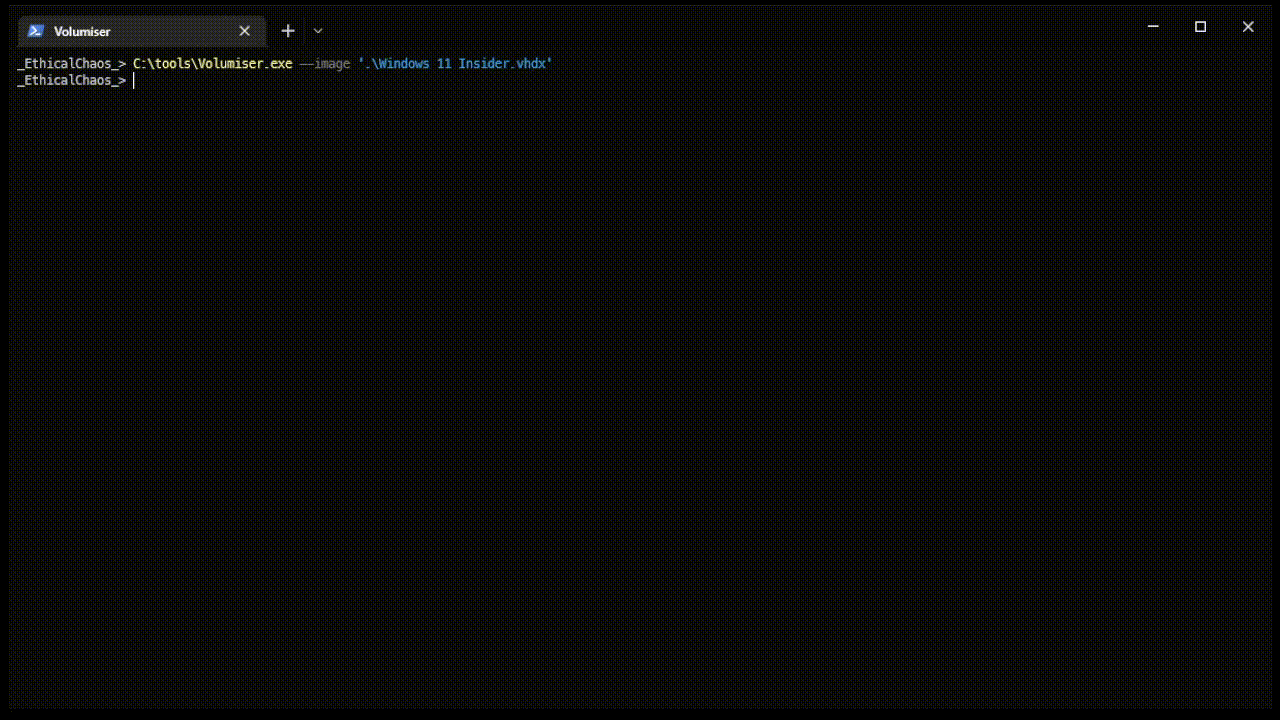
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…