
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
sudo_inject preview

sudo_inject

GitHubnongiach/sudo_inject

[Linux] Two Privilege Escalation techniques abusing sudo token

ctfdigital-forensicseducation+4
7347 years ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

container-escapedigital-forensicseducation+7
33 months ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
cve-2026-31431 preview

cve-2026-31431

GitHubvasyapokemon/cve-2026-31431

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
curated-resourcesdigital-forensicseducation+8
5 months ago
joomla-cve-2015-8562-exploit-and-linux-forensic-analysis preview

joomla-cve-2015-8562-exploit-and-linux-forensic-analysis

GitHubdrolley919/joomla-cve-2015-8562-exploit-and-linux-forensic-analysis

Exploit for Joomla CVE-2015-8562 combined with Linux forensic analysis capabilities for post-exploitation investigation and evidence collection.
digital-forensicsexploitationforensics+3
3 months ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
1901 month ago
persisthunt preview

persisthunt

GitHubraj3shp/persisthunt

Linux Persistence Detection, Hunting and Artifact Collection script

container-securitydigital-forensicsforensics+6
263 months ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.8k6h 45m ago
swap_digger preview

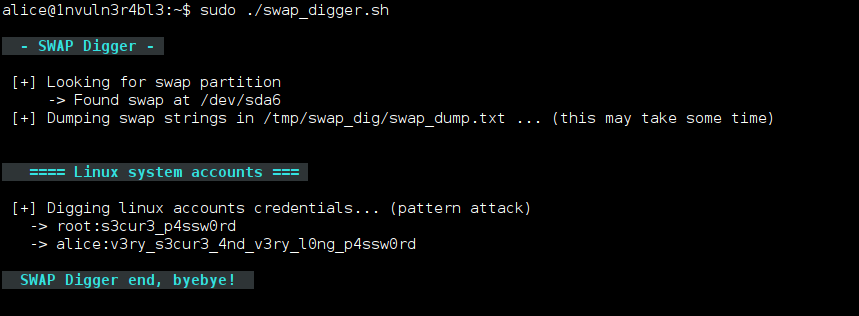
swap_digger

GitHubsevagas/swap_digger

Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…

digital-forensicsforensicsinformation-gathering+2
5345 years ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…

digital-forensicsdynamic-analysis-sandboxingforensics+5
1195 days ago
OshoosiClaw preview

OshoosiClaw

GitHuboyesanyf/oshoosiclaw

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

ai-securityanomaly-detectioncommand-and-control+8
3 days ago
MemTools preview

MemTools

GitHubgmh5225/memtools

Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
binary-analysisdebuggersdigital-forensics+5
52 years ago
Linux-Kodachi preview

Linux-Kodachi

GitHubwmal/linux-kodachi

Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…

cryptographydigital-forensicseducation+9
5047 days ago
dwarf2json preview

dwarf2json

GitHubvolatilityfoundation/dwarf2json

convert ELF/DWARF symbol and type information into vol3's intermediate JSON
binary-analysisdigital-forensicsmemory-forensics+2
1602 years ago
mongobleed-detector preview

mongobleed-detector

GitHubneo23x0/mongobleed-detector

Detection Script for MongoBleed Exploitation
database-securitydigital-forensicsforensics+5
829 months ago
BiBi-Windows-Wiper-Analysis preview

BiBi-Windows-Wiper-Analysis

GitHubknight0x07/bibi-windows-wiper-analysis

Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
binary-analysisdigital-forensicsincident-response+3
92 years ago
copyfail-dfir preview

copyfail-dfir

GitHubledlight33/copyfail-dfir

Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
digital-forensicseducationincident-response+2
216 days ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

binary-analysisbinary-exploitationctf+8
9323 days ago
Previous123Next