

h4cker
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
ai-securityctfcurated-resources+8
29.9k
the-art-of-hacking/h4ckerCurated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
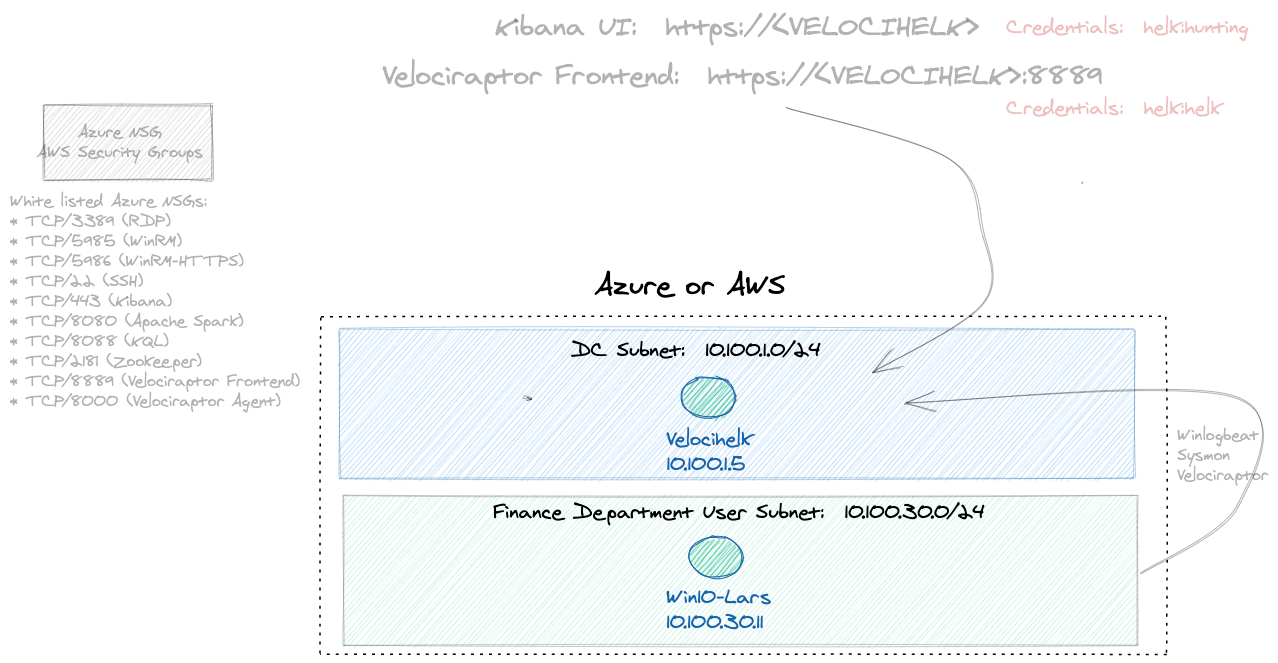 iknowjason/bluecloud
Cyber Range including Velociraptor + HELK system with a Windows VM for security testing and R&D. Azure and AWS terraform support.

 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 mukul975/anthropic-cybersecurity-skills
817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
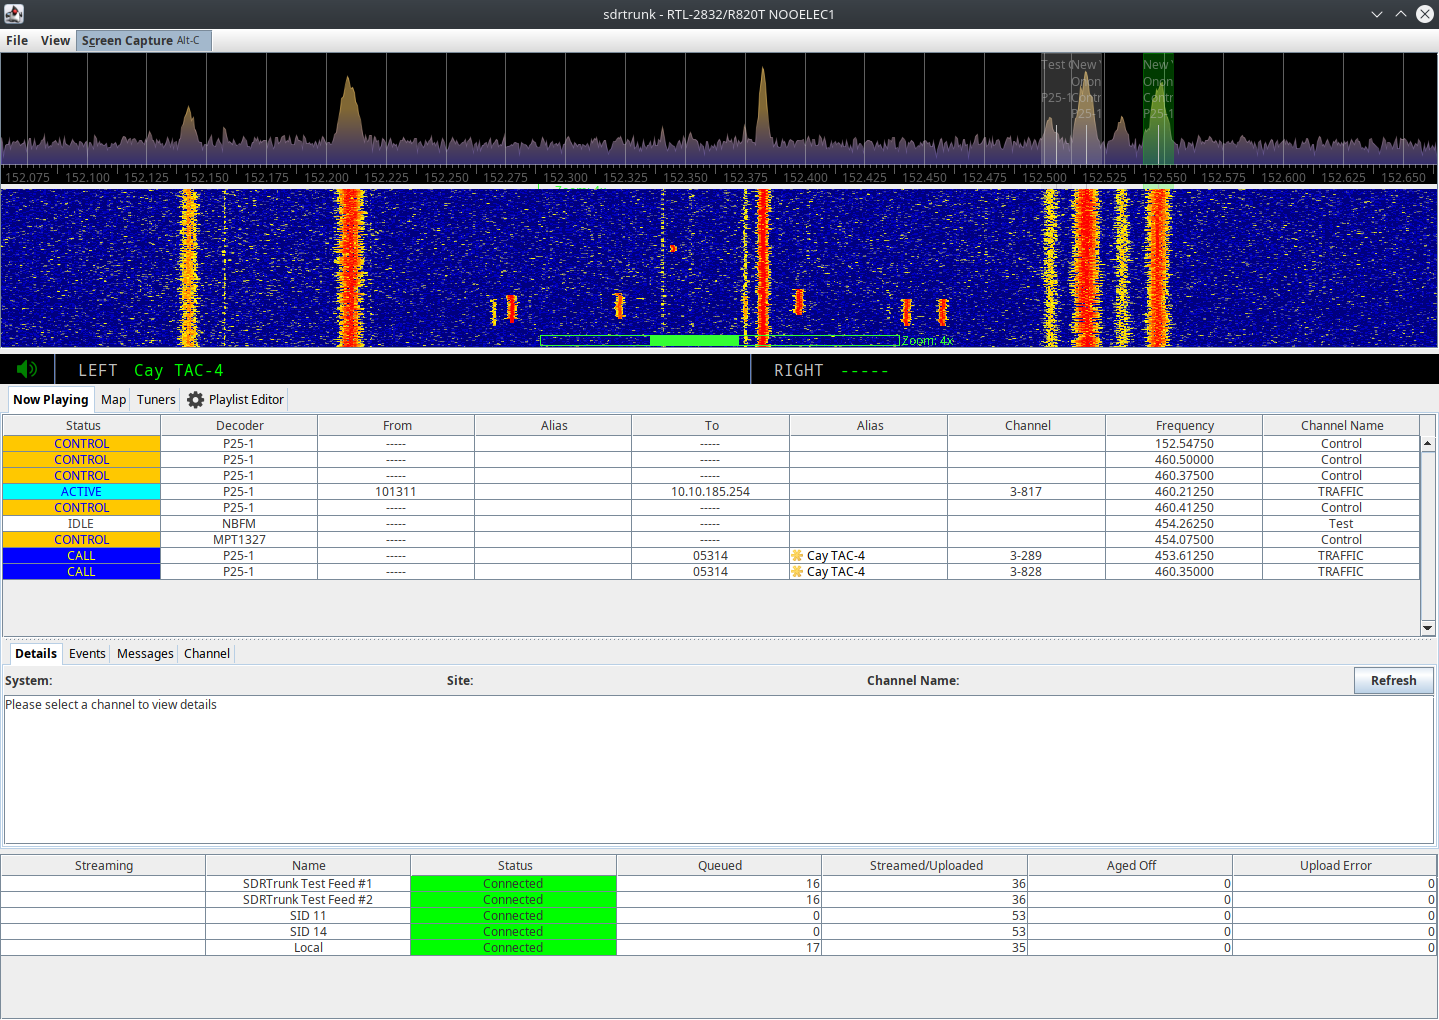 dsheirer/sdrtrunk
A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 trunkrecorder/trunk-recorder
Records calls from a Trunked Radio System (P25 & SmartNet)
 s3cur3th1ssh1t/creds
Some usefull Scripts and Executables for Pentest & Forensics
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.