
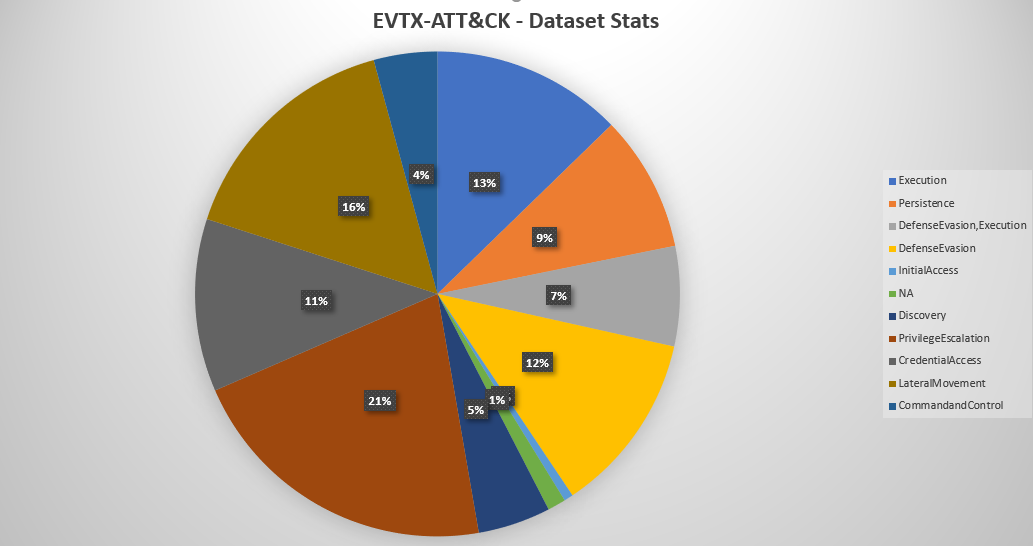
EVTX-ATTACK-SAMPLES
 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
curated-resourcesdigital-forensicseducation+2
2.6k
sbousseaden/evtx-attack-samplesCurated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
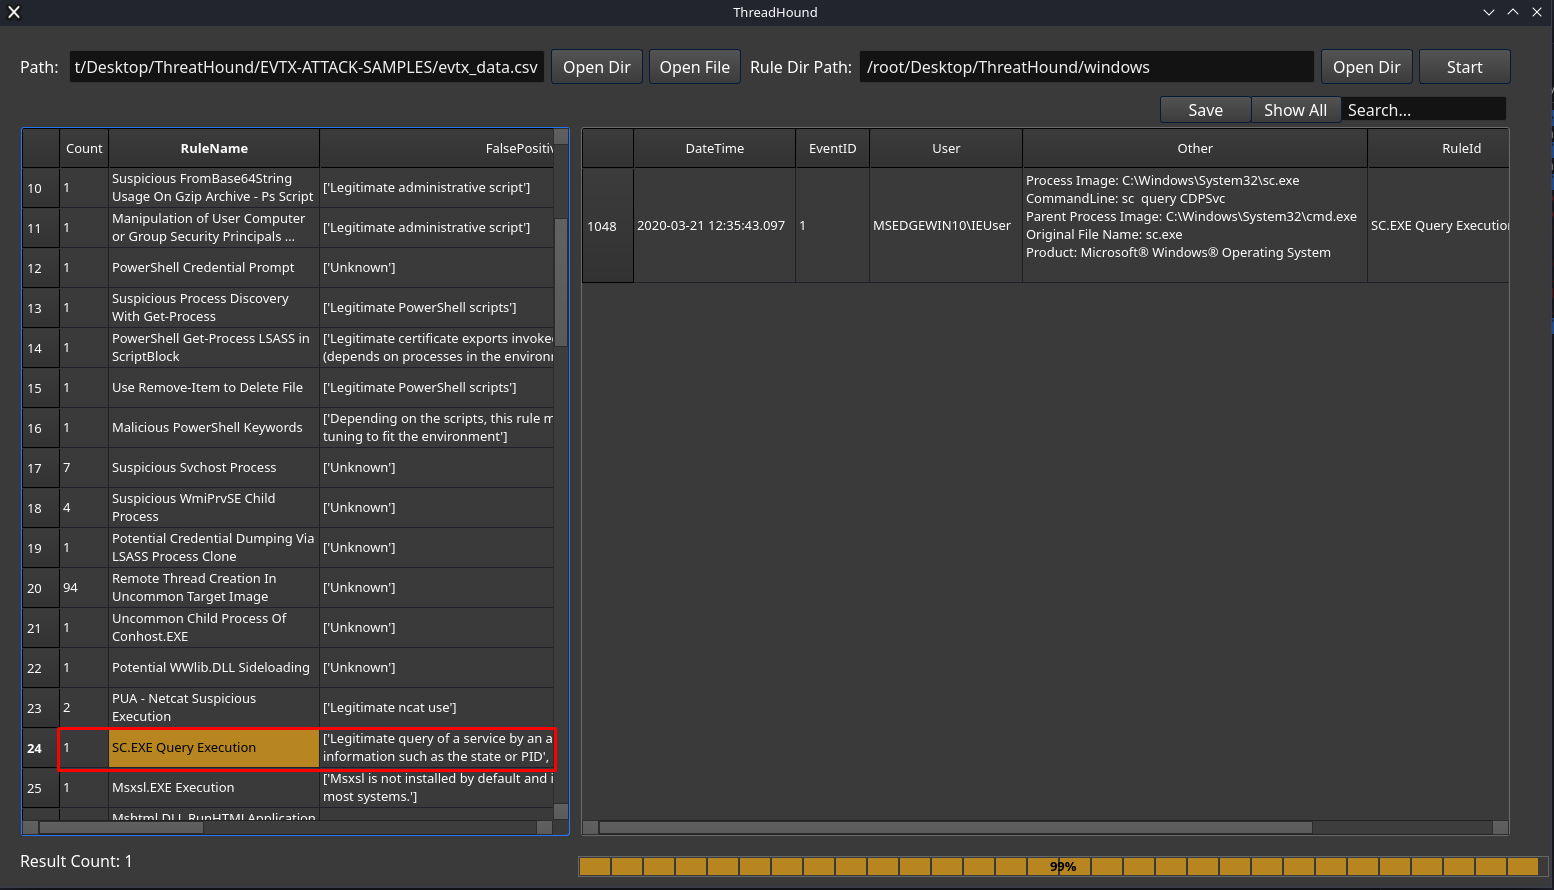 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…

 emalderson/thephish
ThePhish: an automated phishing email analysis tool
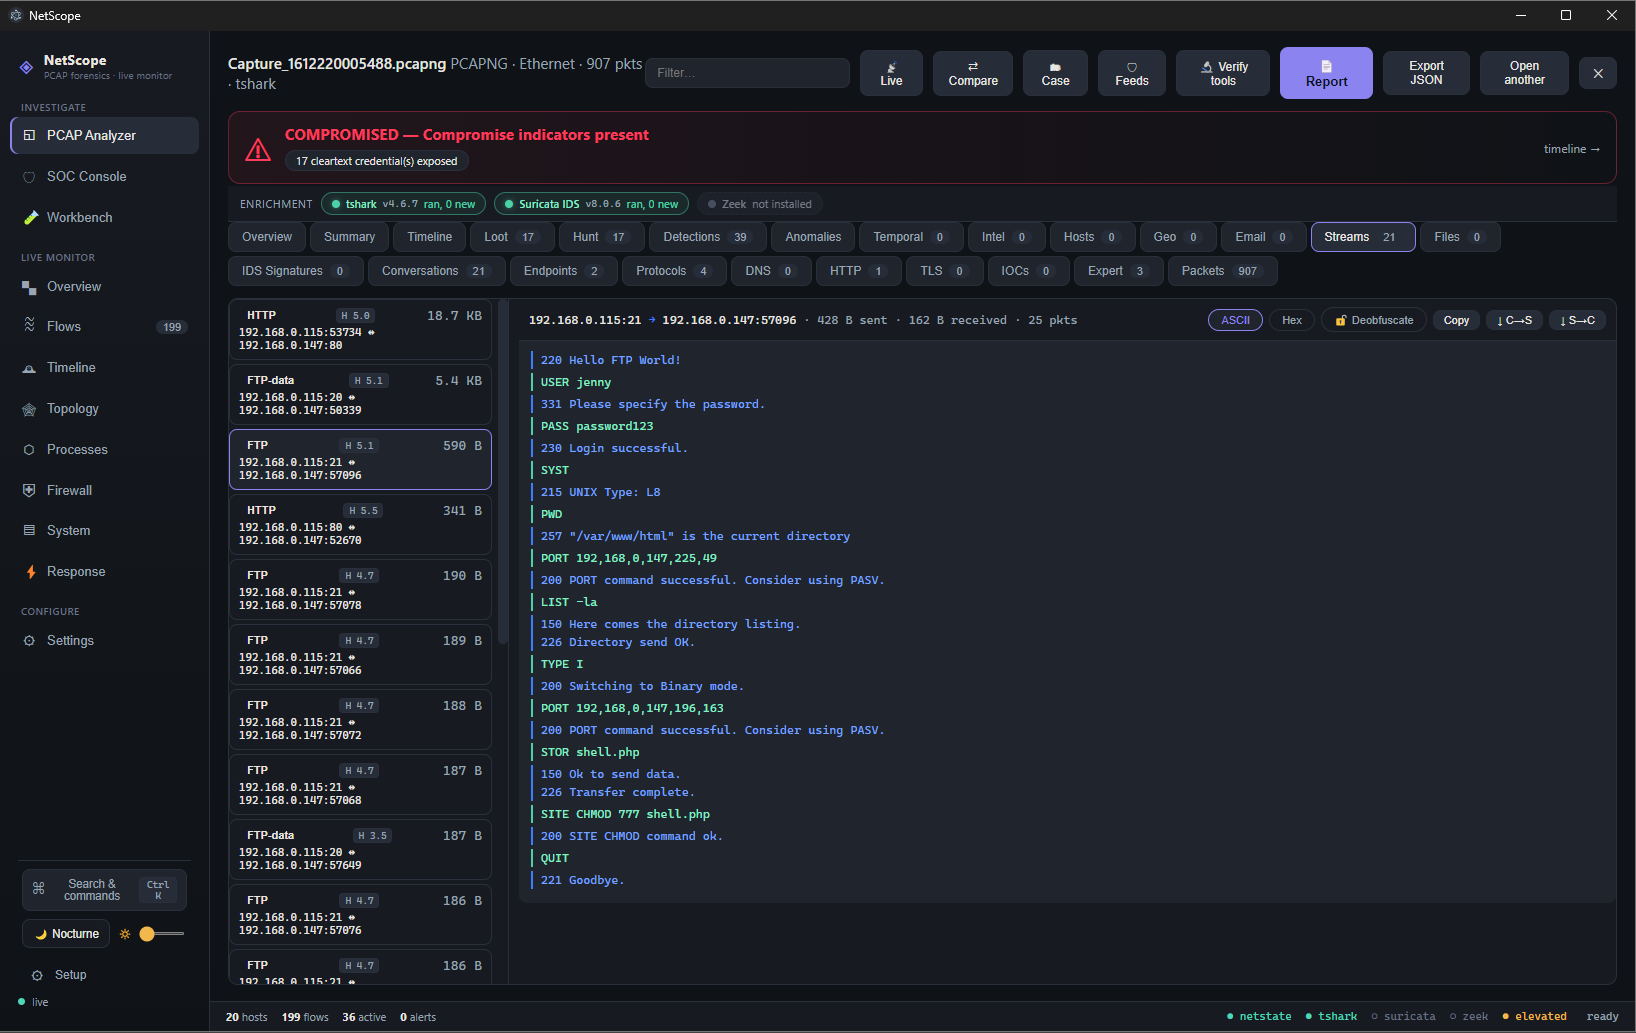 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 cado-security/dfir_resources_revil_kaseya
Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…