

ForensiX-Studio
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
anomaly-detectiondigital-forensicsforensics+4
1
aquibpro/forensix-studioForensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
 graphworlok/cve-2021-35394-ecosystem
Tracking the family of unrelated IoT botnets sharing CVE-2021-35394 as a delivery vector — findings, relationships, methodology.
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 barnew-st/ecdsa-private-key-recovery
A cryptographic research tool for analyzing signature vulnerabilities
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 apr4h/cobaltstrikescan
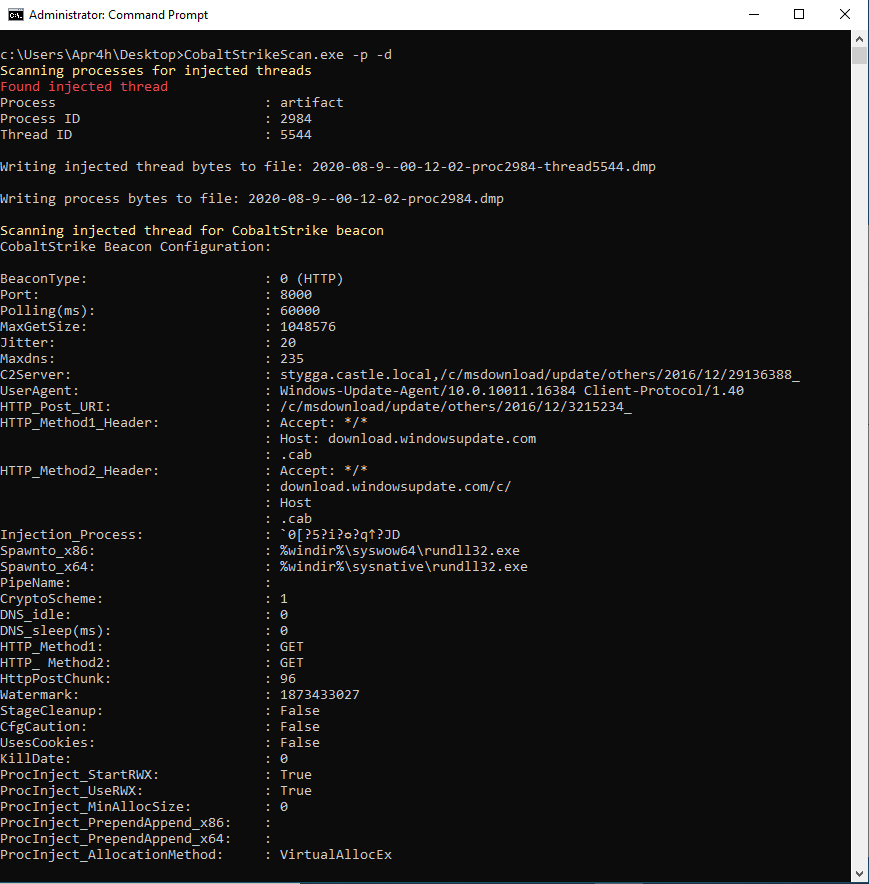
Scan files or process memory for CobaltStrike beacons and parse their configuration
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 packetsifter/packetsiftertool
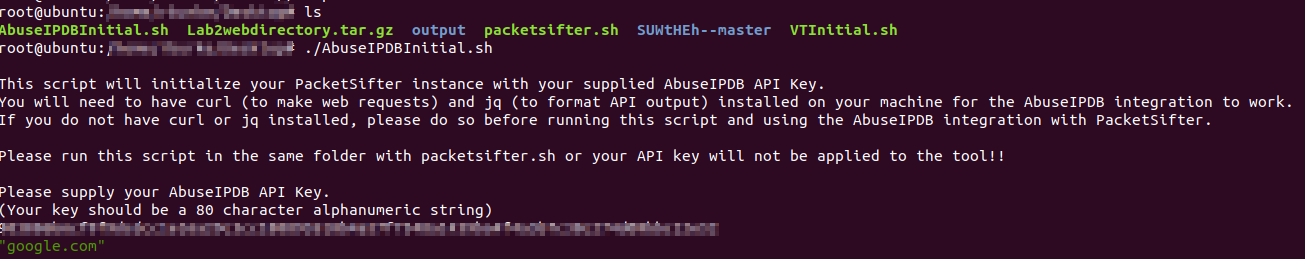
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 concinnity-risks/ransomcoinpublic
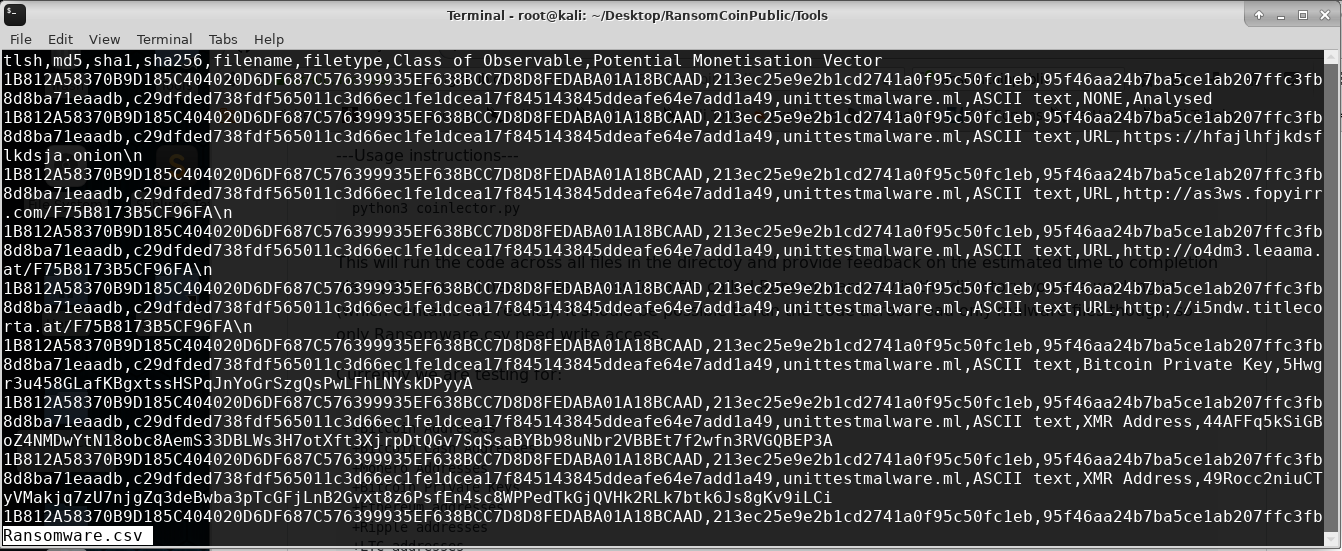
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 sgnls/exchange-0days-202103
IoC determination for exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858 and CVE-2021-27065.
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…
 dahnutz/zimbra-cve-2026-73570-ir
Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints