

guasap-whatsapp-foresincs-tool
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
data-recoverydigital-forensicsforensics+1
176
quantika14/guasap-whatsapp-foresincs-toolWhatsApp Forensic Tool
 ashemery/anti-forensics
A Repository to Track Anti-Forensic Techniques
 cybercentrecanada/cart
Python implementation of the CaRT library for (un)inerting files.
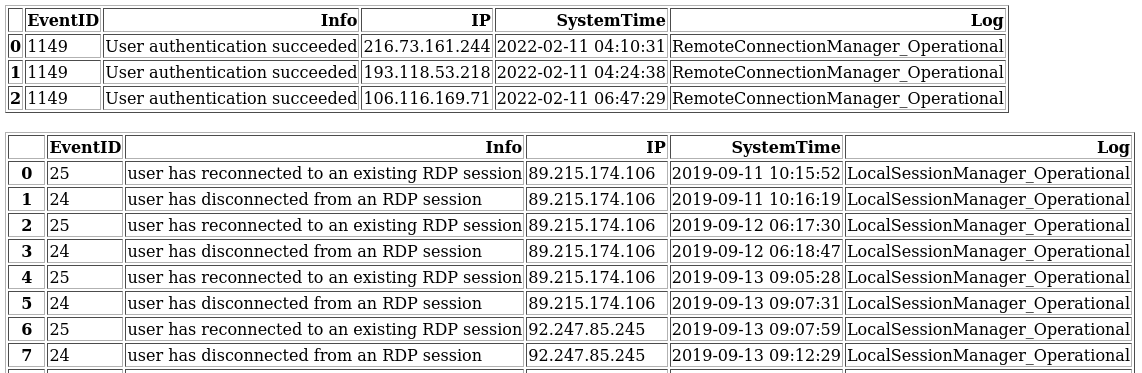 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 synacktiv/forensic-msvpn
This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 graphworlok/cve-2021-35394-ecosystem
Tracking the family of unrelated IoT botnets sharing CVE-2021-35394 as a delivery vector — findings, relationships, methodology.
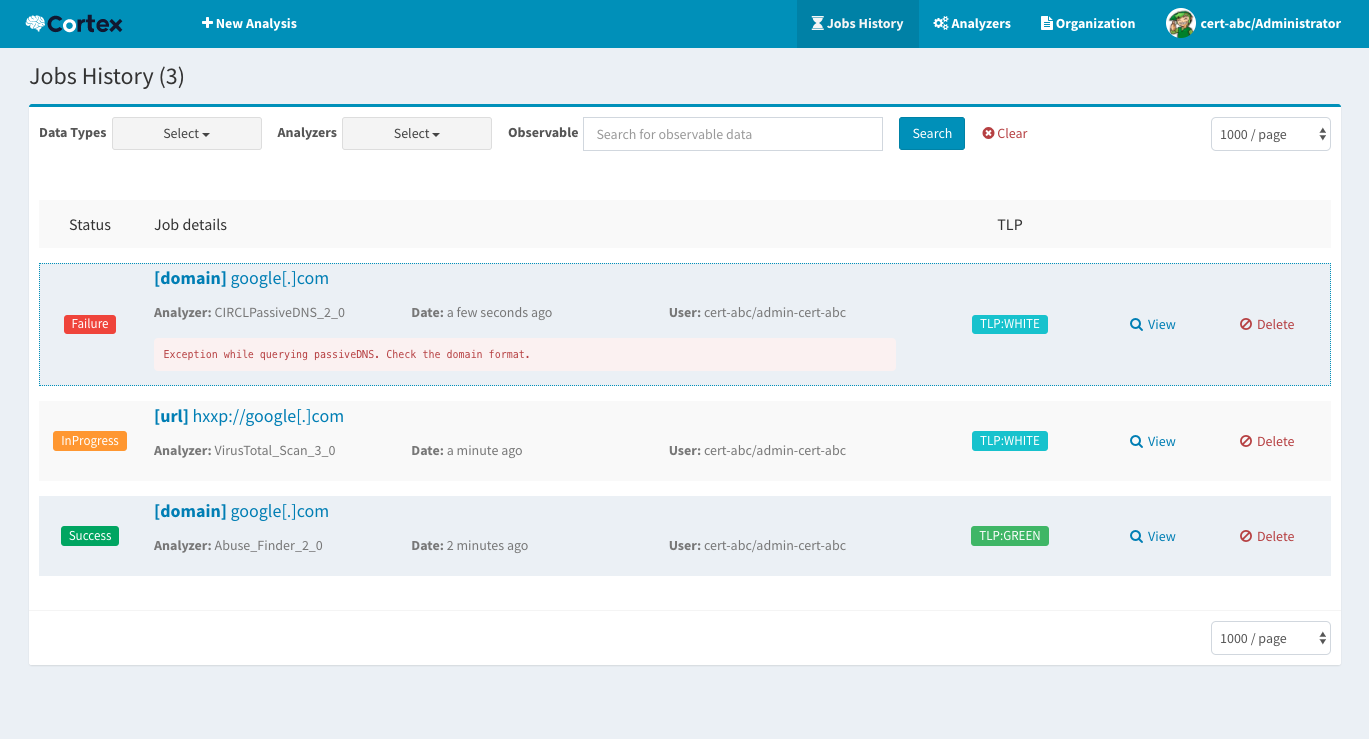 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
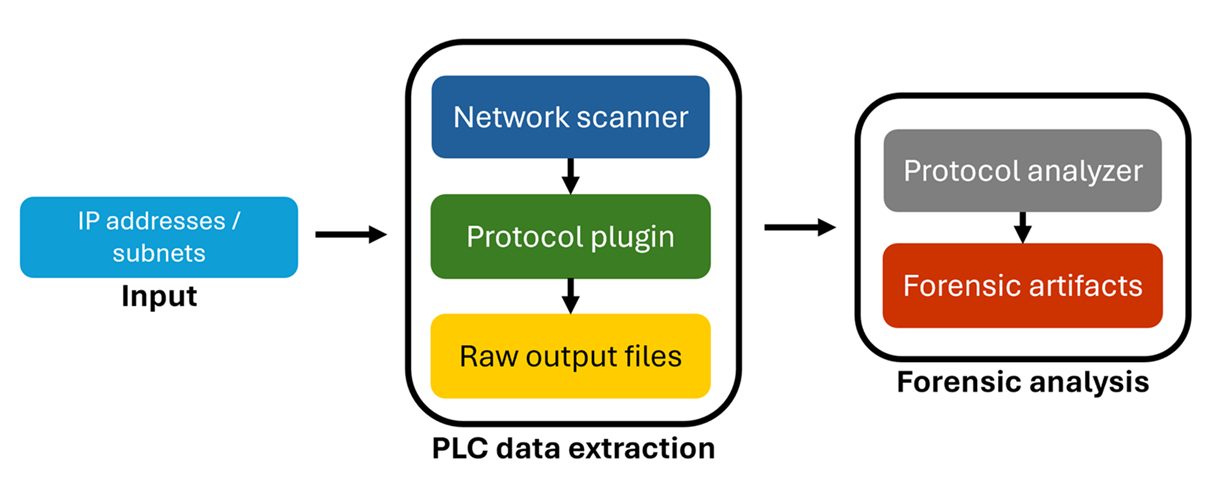 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
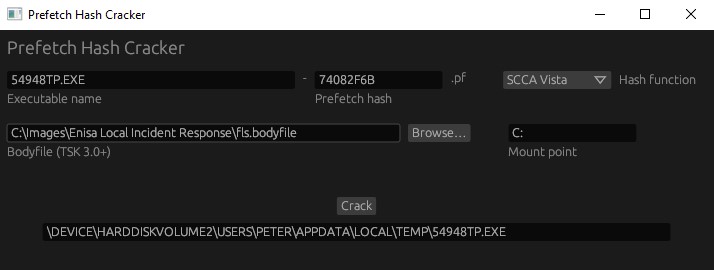 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

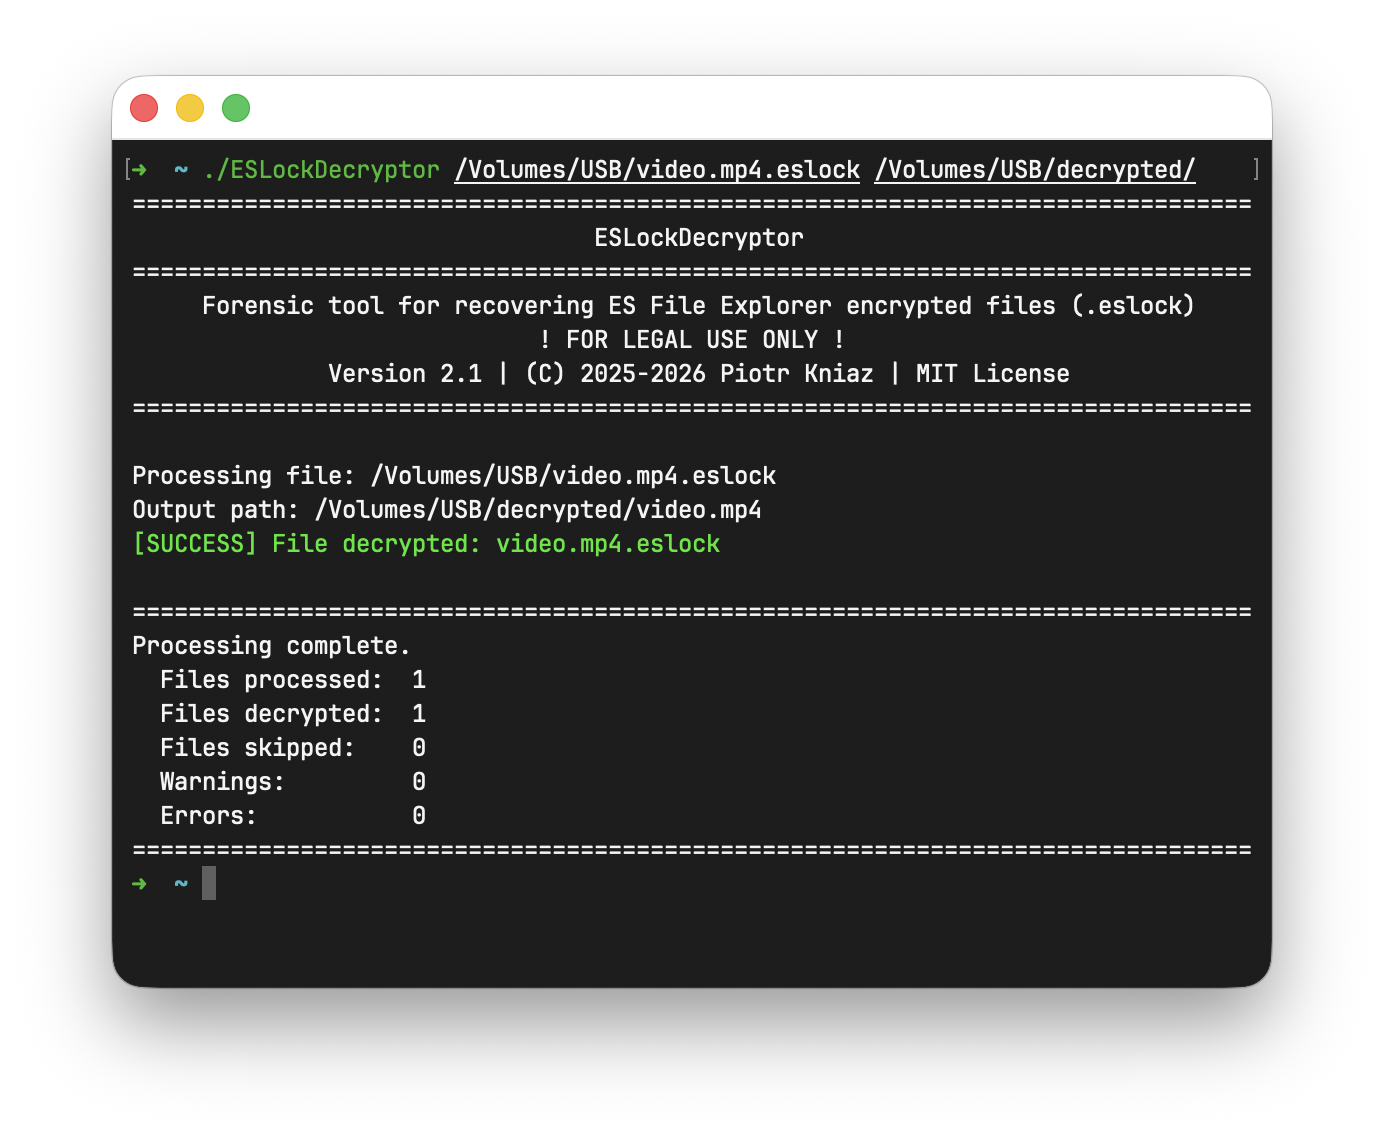 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
 ivmks74/iiita-iot-security-research
IoT Security research conducted during my internship at IIIT Allahabad, leading to CVE-2026-65893, CVE-2026-65894, and the CERT-In Vulnerability Note…