
yaml2yara
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input
digital-forensicsincident-responseintrusion-detection+4
22
nccgroup/yaml2yaraGenerate bulk YARA rules from YAML input
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
 uthrasri/openssl_g2.5_cve-2014-8275
General-purpose cryptography library and SSL/TLS toolkit implementing ciphers, digests, public key algorithms, and X.509 certificates for secure…
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
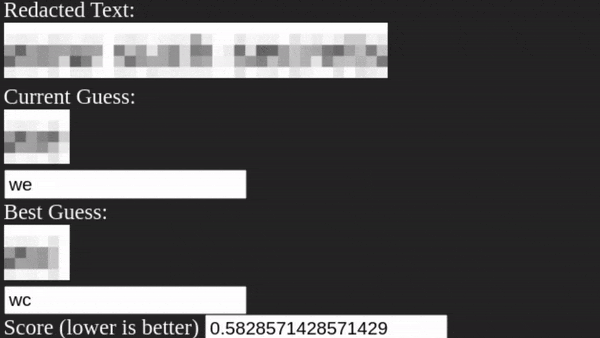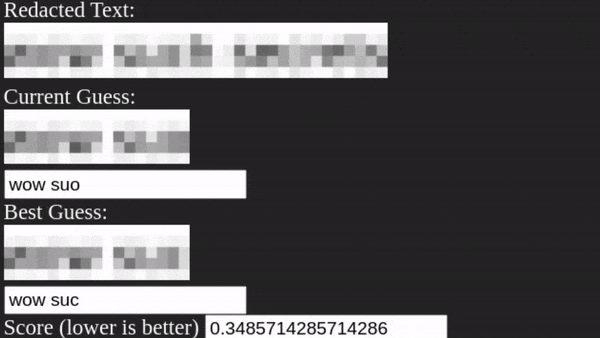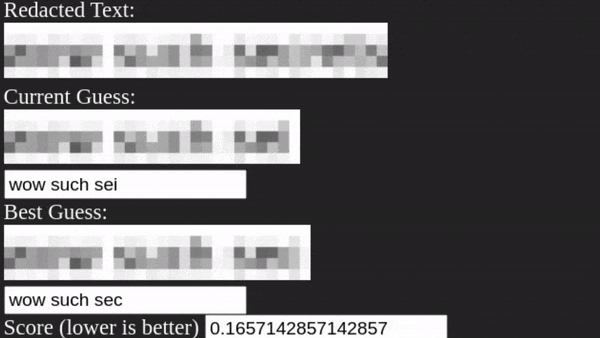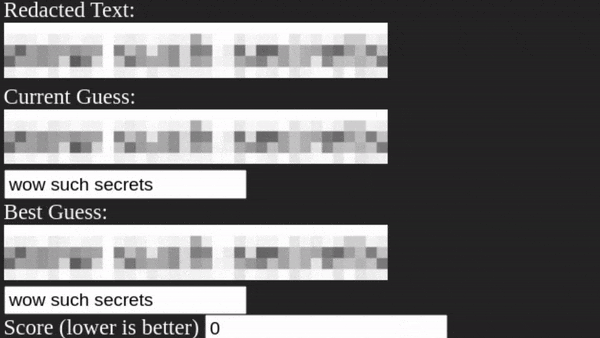 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 downunderctf/challenges_2022_public
Files + Writeups for DownUnderCTF 2022 Challenges
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
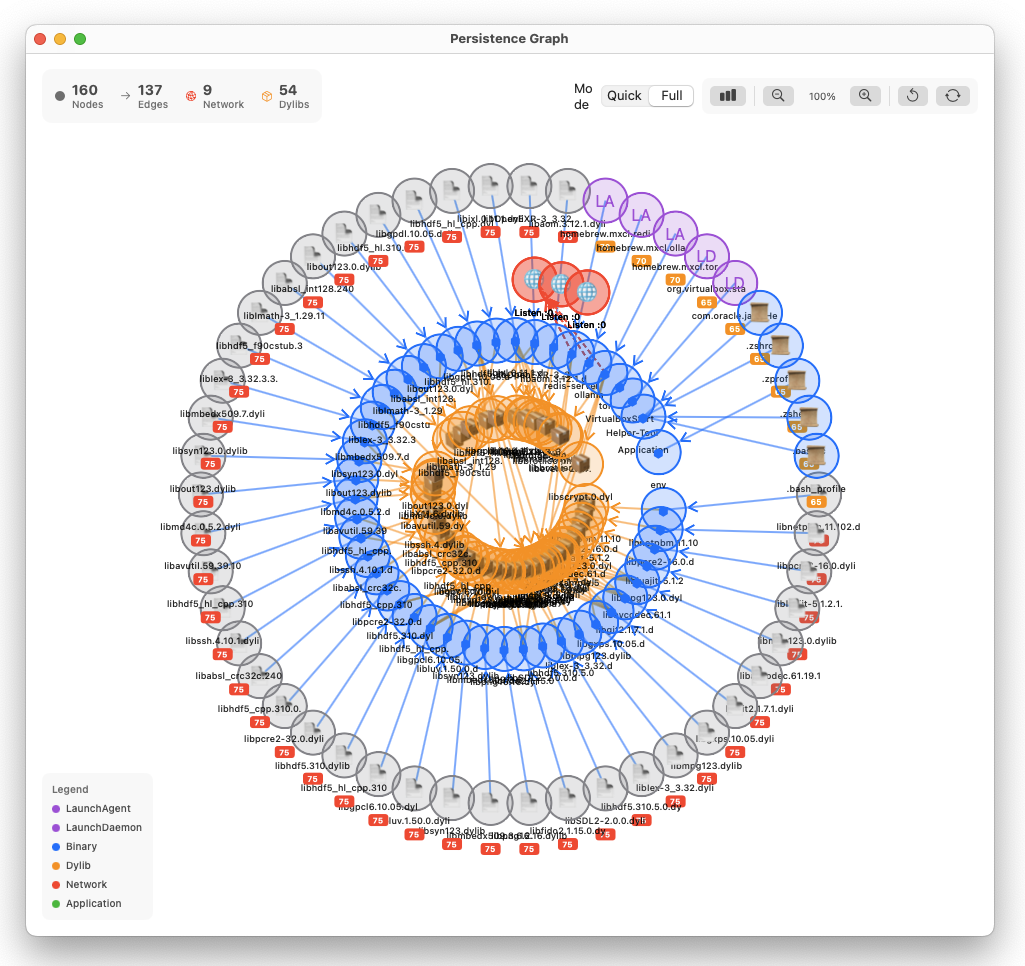 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
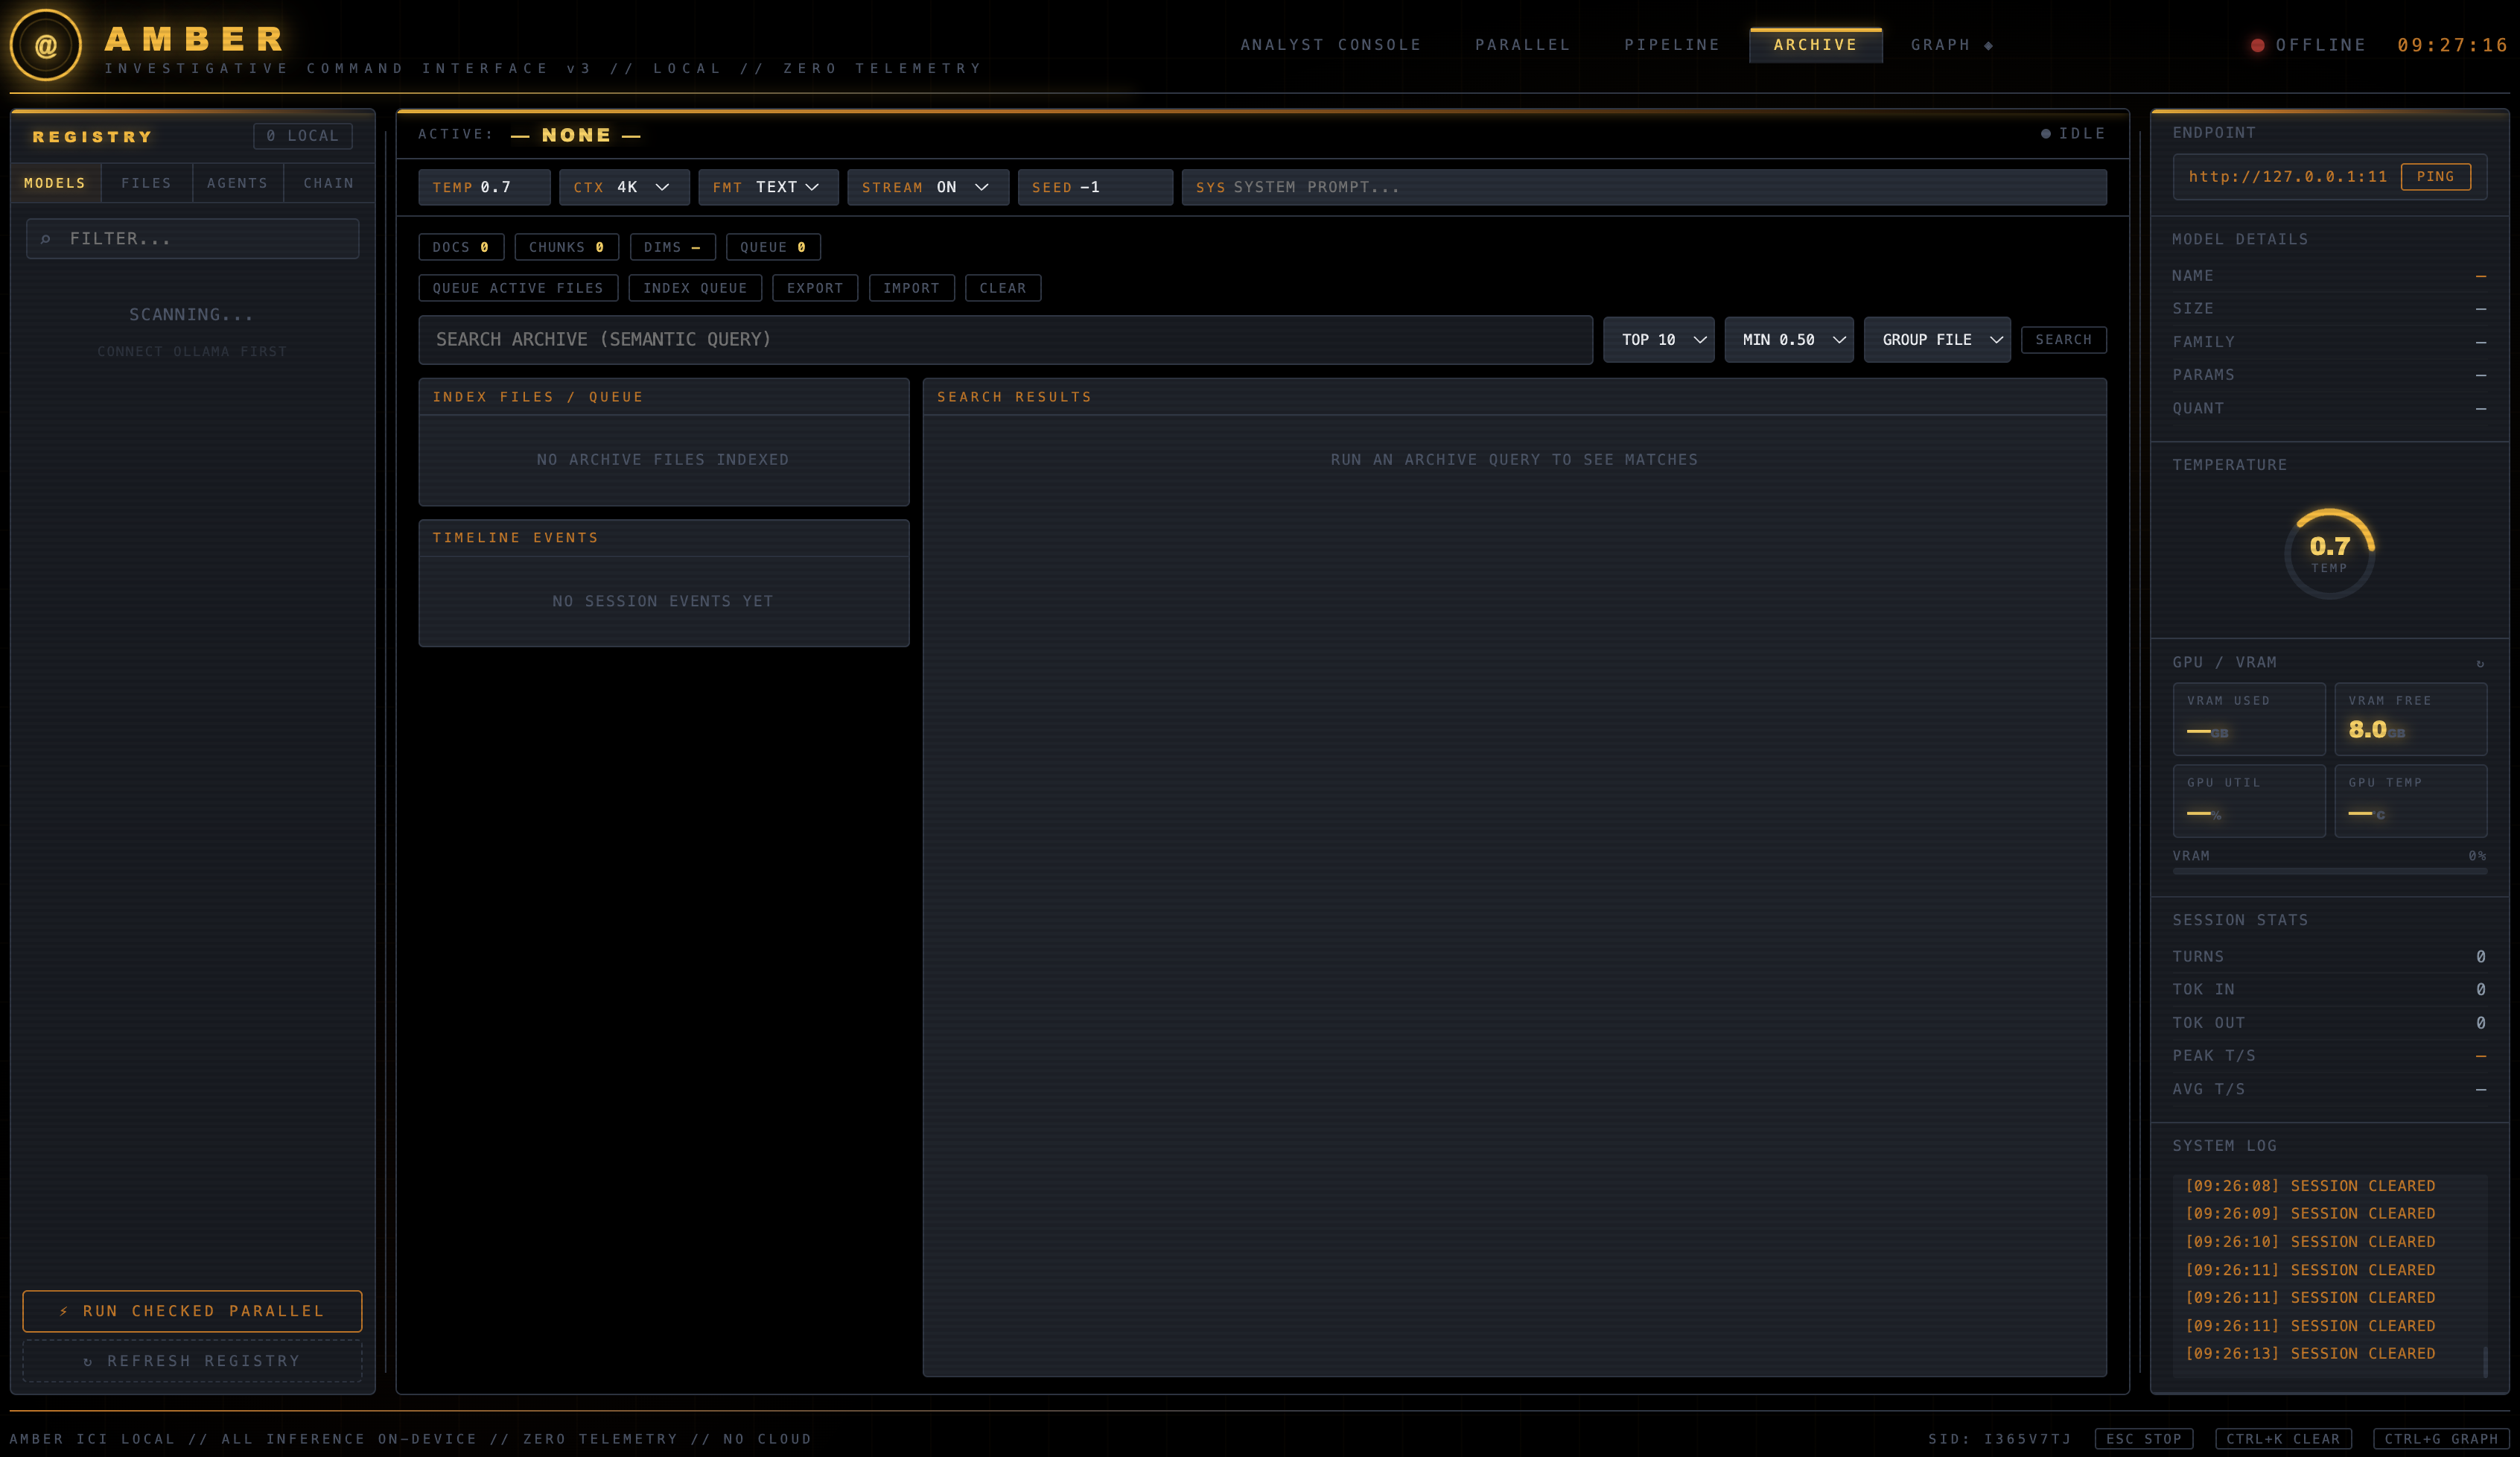 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…