
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
338 results
THM-Tempest preview

THM-Tempest

GitHubczabatta/thm-tempest

TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts
command-and-controlctfdigital-forensics+9
3 months ago
Sharepoint-cve-2023-29375-incident-response preview

Sharepoint-cve-2023-29375-incident-response

GitHubzedocun/sharepoint-cve-2023-29375-incident-response

End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29375) using SIEM logs,…
digital-forensicseducationincident-response+3
11 month ago
osxcollector preview
Archived

osxcollector

GitHubyelparchive/osxcollector

A forensic evidence collection & analysis toolkit for OS X
digital-forensicsdisk-forensicsforensics+3
1.9k7 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…

cryptographydigital-forensicseducation+7
313 months ago
DC30-Badge-Challenge-Writeup preview

DC30-Badge-Challenge-Writeup

GitHubkybr-git/dc30-badge-challenge-writeup

Writeup for the DEF CON 30 badge challenge
ctfcurated-resourcesdigital-forensics+3
724 years ago
K2-CLI preview

K2-CLI

GitHubodinglyn0/k2-cli

Putting the analysis in steganalysis.

anomaly-detectionctfdigital-forensics+7
128 months ago
ZeroScout preview

ZeroScout

GitHubsumidcyber/zeroscout

🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…

defensive-toolsdigital-forensicseducation+7
119 months ago
sharepoint-2026-poc preview

sharepoint-2026-poc

GitHubwismansec/sharepoint-2026-poc

PoC, IOCs, and detection logic for the SharePoint /_trust WS-Federation BinaryFormatter deserialization chain. Lab reconstruction covering…

digital-forensicseducationexploitation+5
21 month ago
follina-msdt-threat-investigation preview

follina-msdt-threat-investigation

GitHubzavikhttak/follina-msdt-threat-investigation

🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…

digital-forensicseducationincident-response+4
1 month ago
FAMA preview
Archived

FAMA

GitHublabcif/fama

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser

android-securitydata-recoverydigital-forensics+3
1542 years ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
8.0k1 day ago
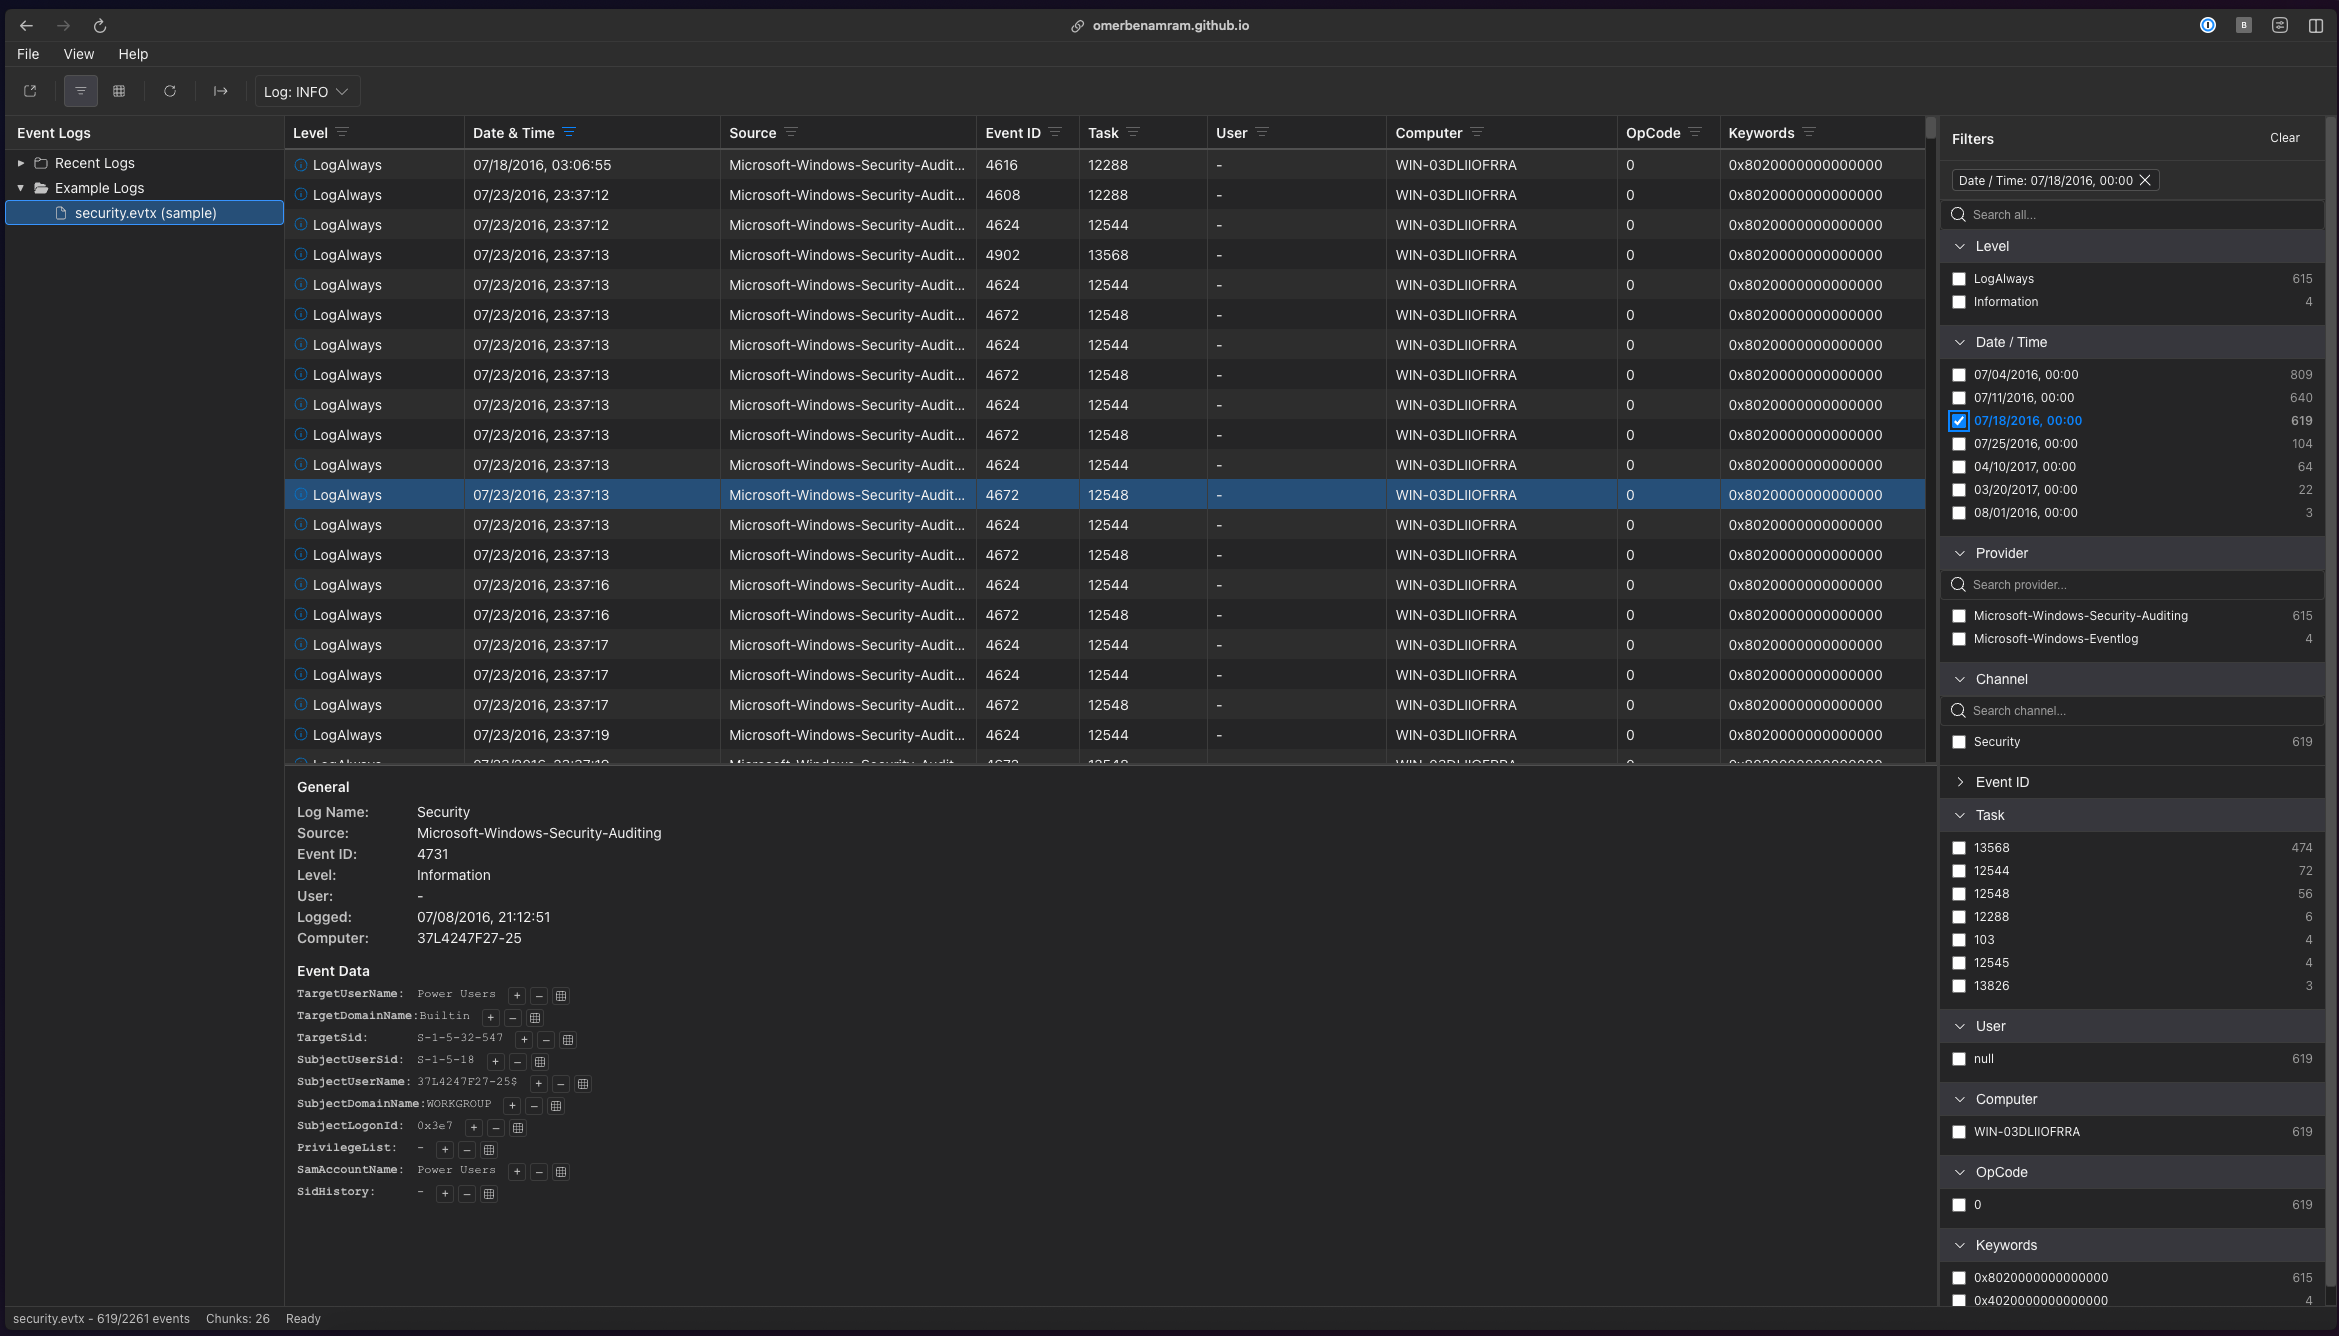
evtx preview

evtx

GitHubomerbenamram/evtx

A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
digital-forensicsforensicsincident-response+1
9643 days ago
no-gdid preview

no-gdid

GitHubkorben00/no-gdid

Read, understand and silence the Windows GDID device identifier (the ID that tracked a hacker through a VPN). Verified on a real Win11 VM. Honest: it…

configuration-auditingdefensive-toolsdigital-forensics+2
2981 month ago
CIRTKit preview

CIRTKit

GitHubopensourcesec/cirtkit

Tools for the Computer Incident Response Team :computer:
digital-forensicsforensicsincident-response+2
1539 years ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
252 months ago
CVE-NetScalerFileSystemCheck preview

CVE-NetScalerFileSystemCheck

GitHubdanielwep/cve-netscalerfilesystemcheck

This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
digital-forensicsforensicsincident-response+3
25 years ago
CVE-2024-33901-ProofOfConcept preview

CVE-2024-33901-ProofOfConcept

GitHubgmikisilva/cve-2024-33901-proofofconcept

Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
data-exfiltrationdigital-forensicsexploitation+3
21 year ago
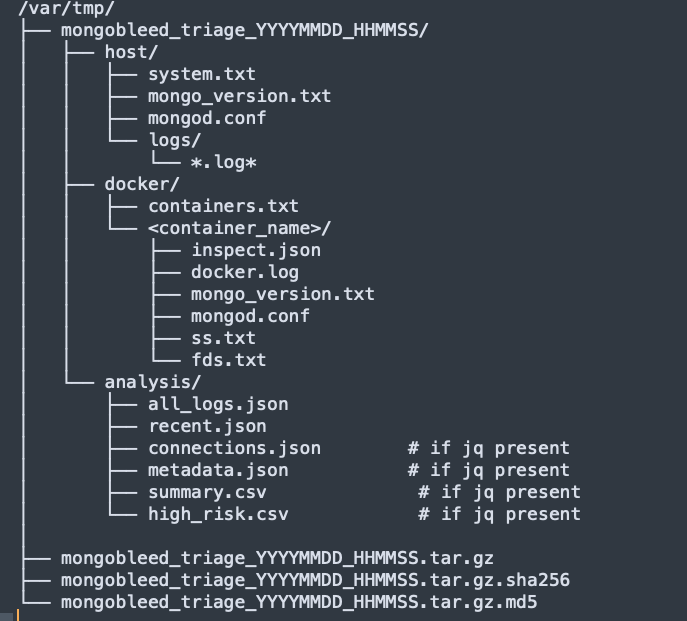
MongoBleed-DFIR-Triage-Script-CVE-2025-14847 preview

MongoBleed-DFIR-Triage-Script-CVE-2025-14847

GitHubjemhadar/mongobleed-dfir-triage-script-cve-2025-14847

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

container-securitydatabase-securitydigital-forensics+5
8 months ago
Previous1…151617…19Next