
netwatch
 matthart1983/netwatch
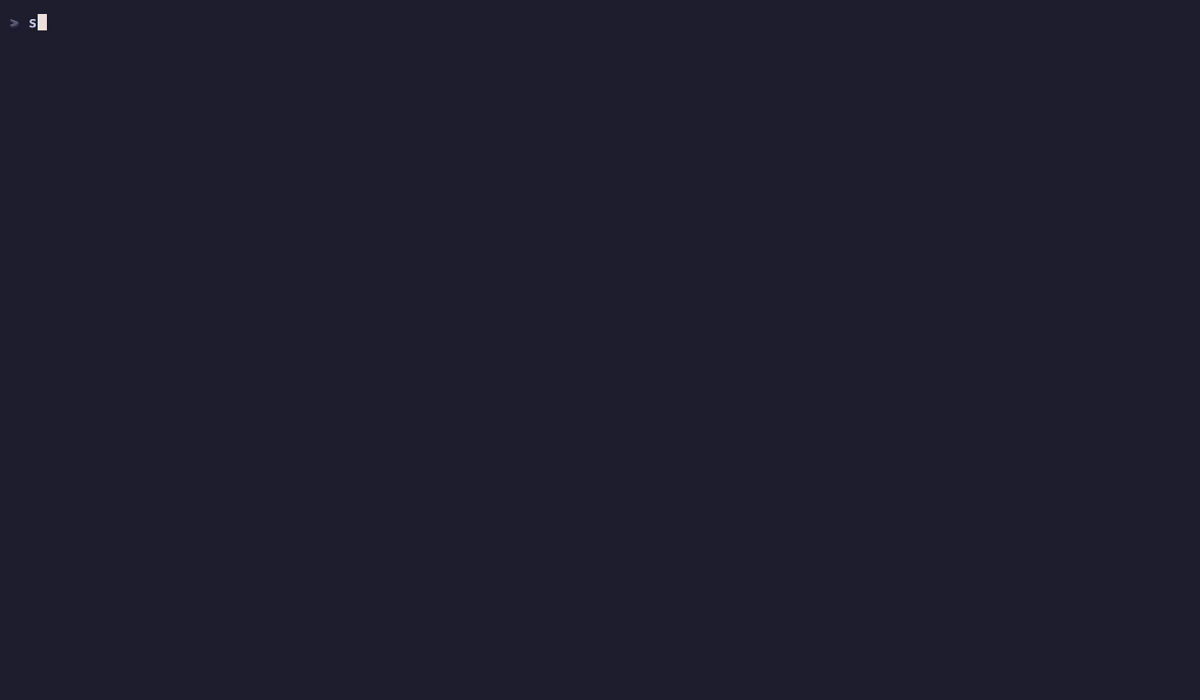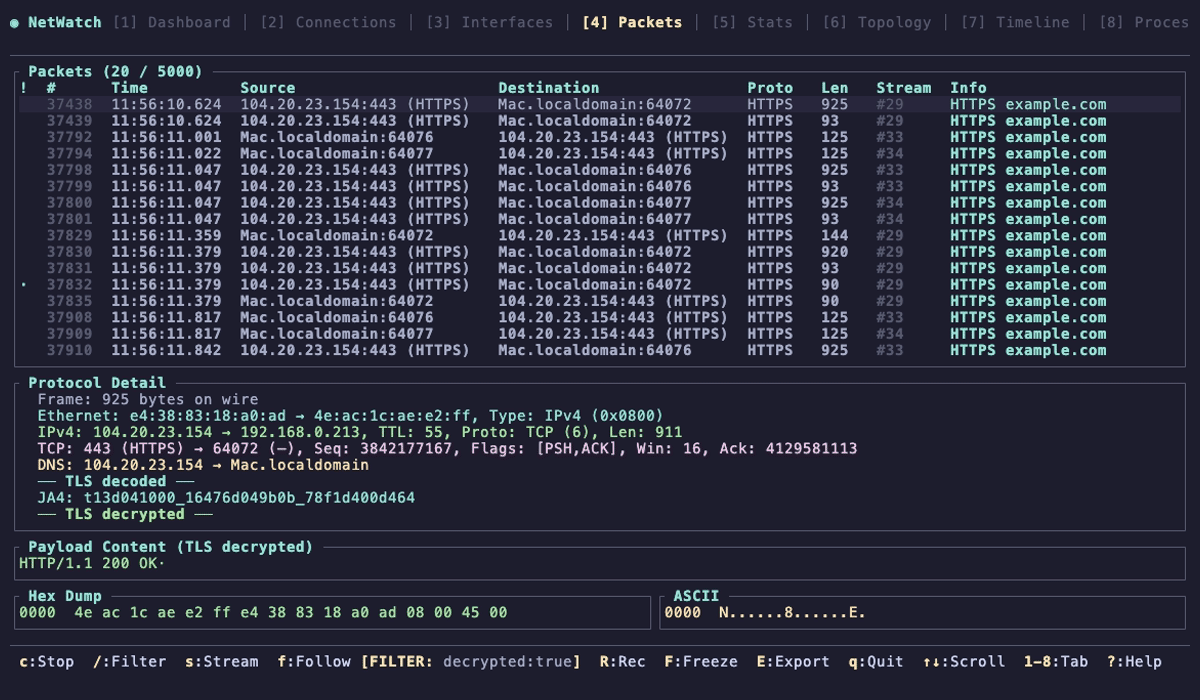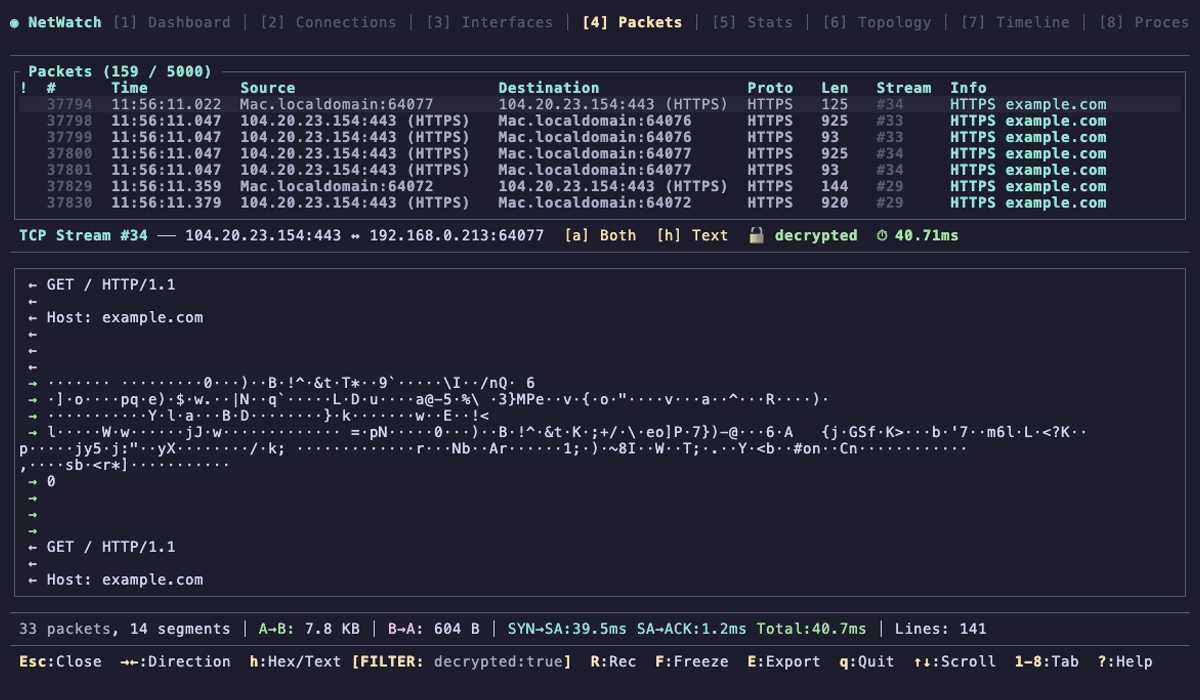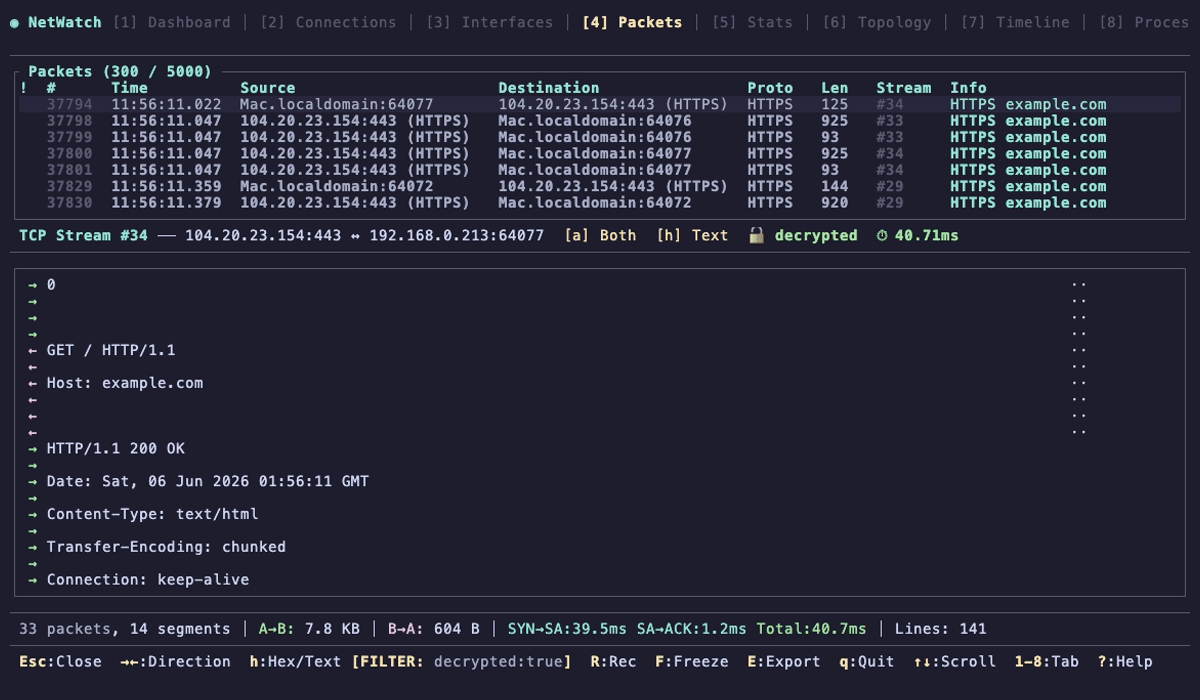
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
defensive-toolsdigital-forensicsdns-analysis+8
3.1k
matthart1983/netwatchReal-time network diagnostics in your terminal. One command, zero config, instant visibility.
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
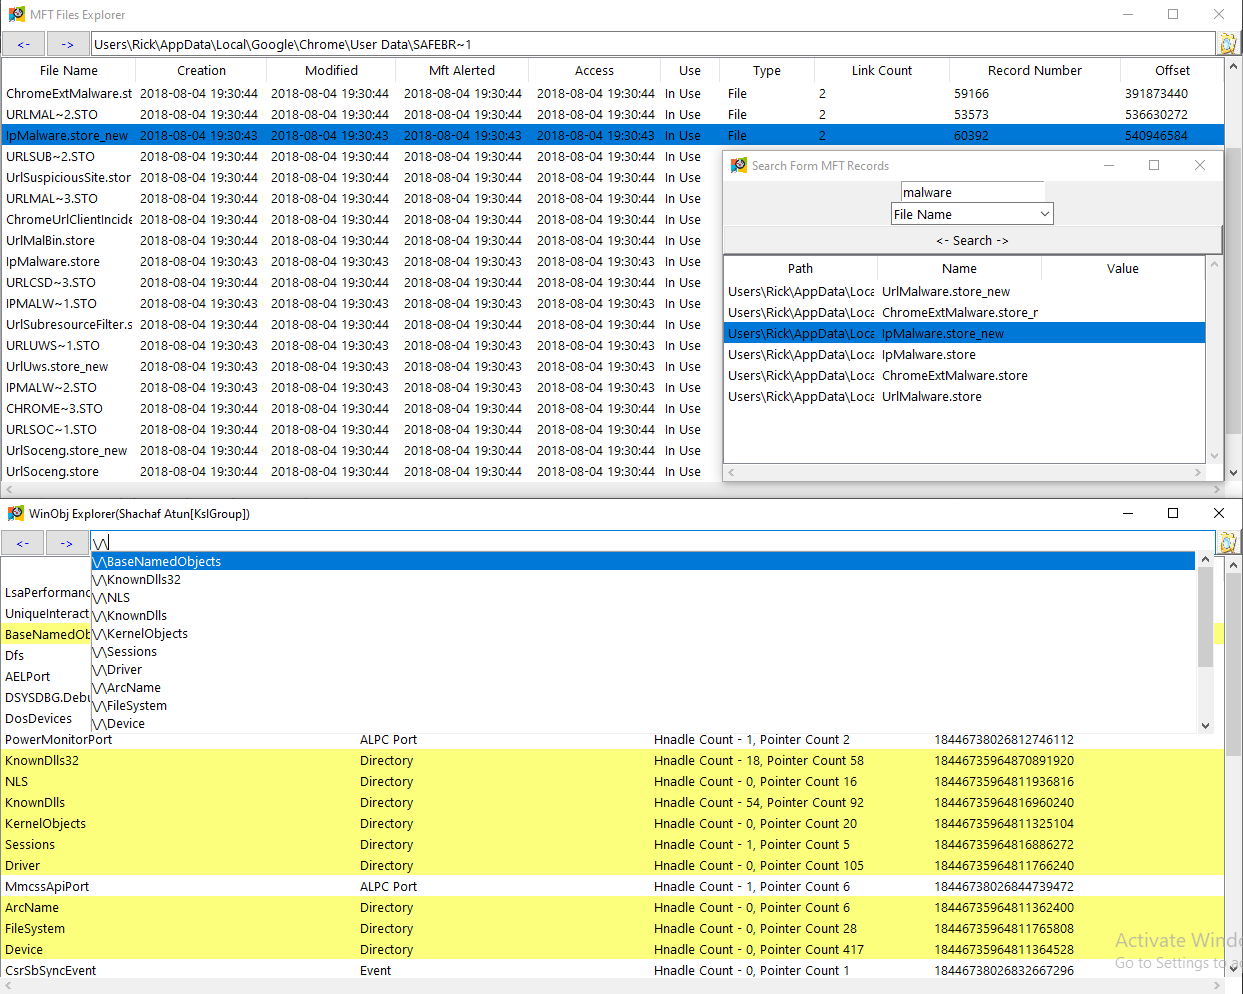 memoryforensics1/volexp
volatility explorer (volatility 2)
 crowdstrike/xwf-yara-scanner
Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
 jwa7470/cve-2026-20131-post-incident-written-report
Post-incident report on CVE-2026-20131 (CVSS 10.0), a Cisco FMC insecure deserialization vulnerability exploited by Interlock ransomware. Details…
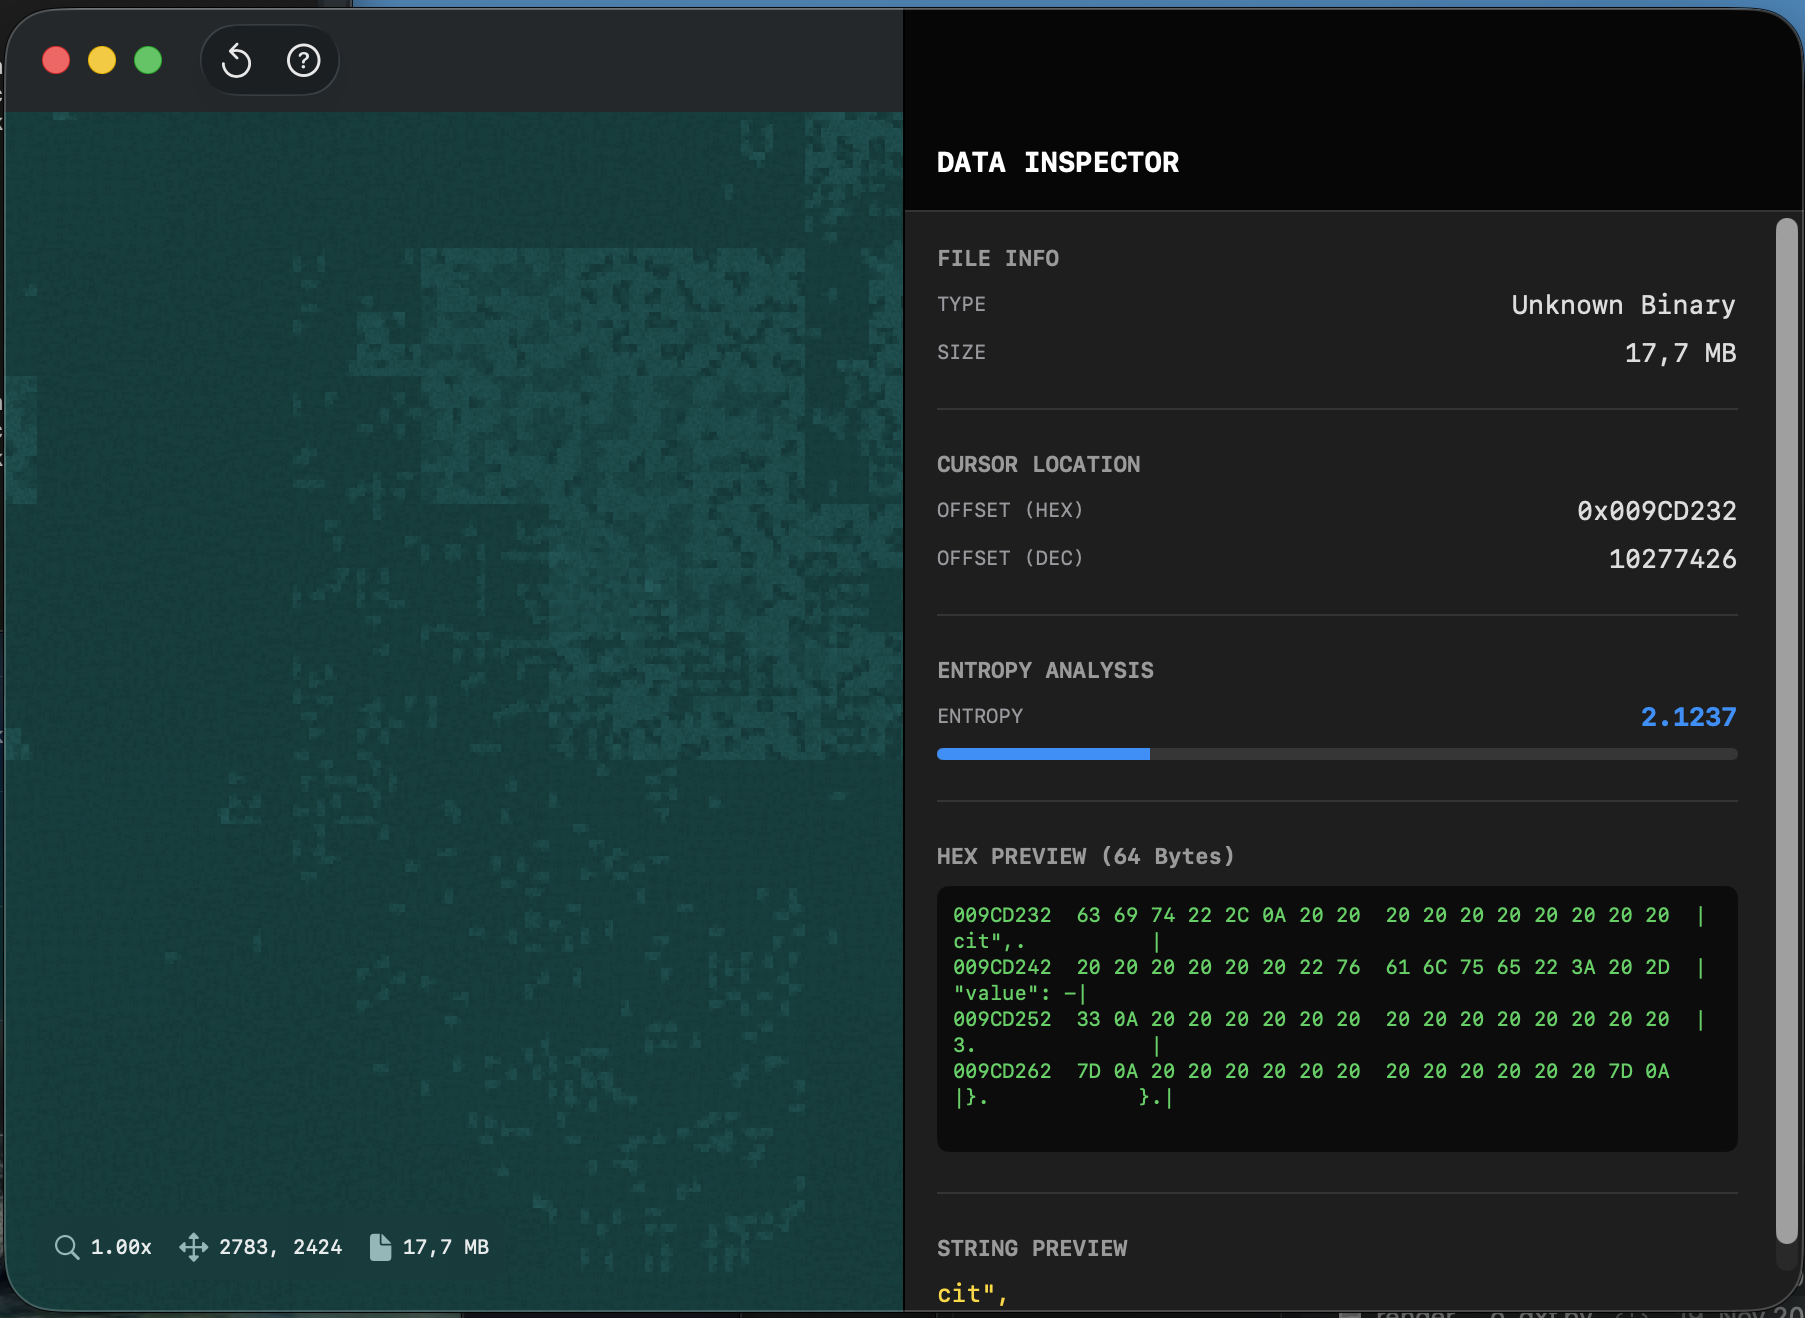 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 bilalalshiekh912/incident-response-report-teamcity-compromise-cve-2024-27198-
CyberDefenders JetBrains Lab
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
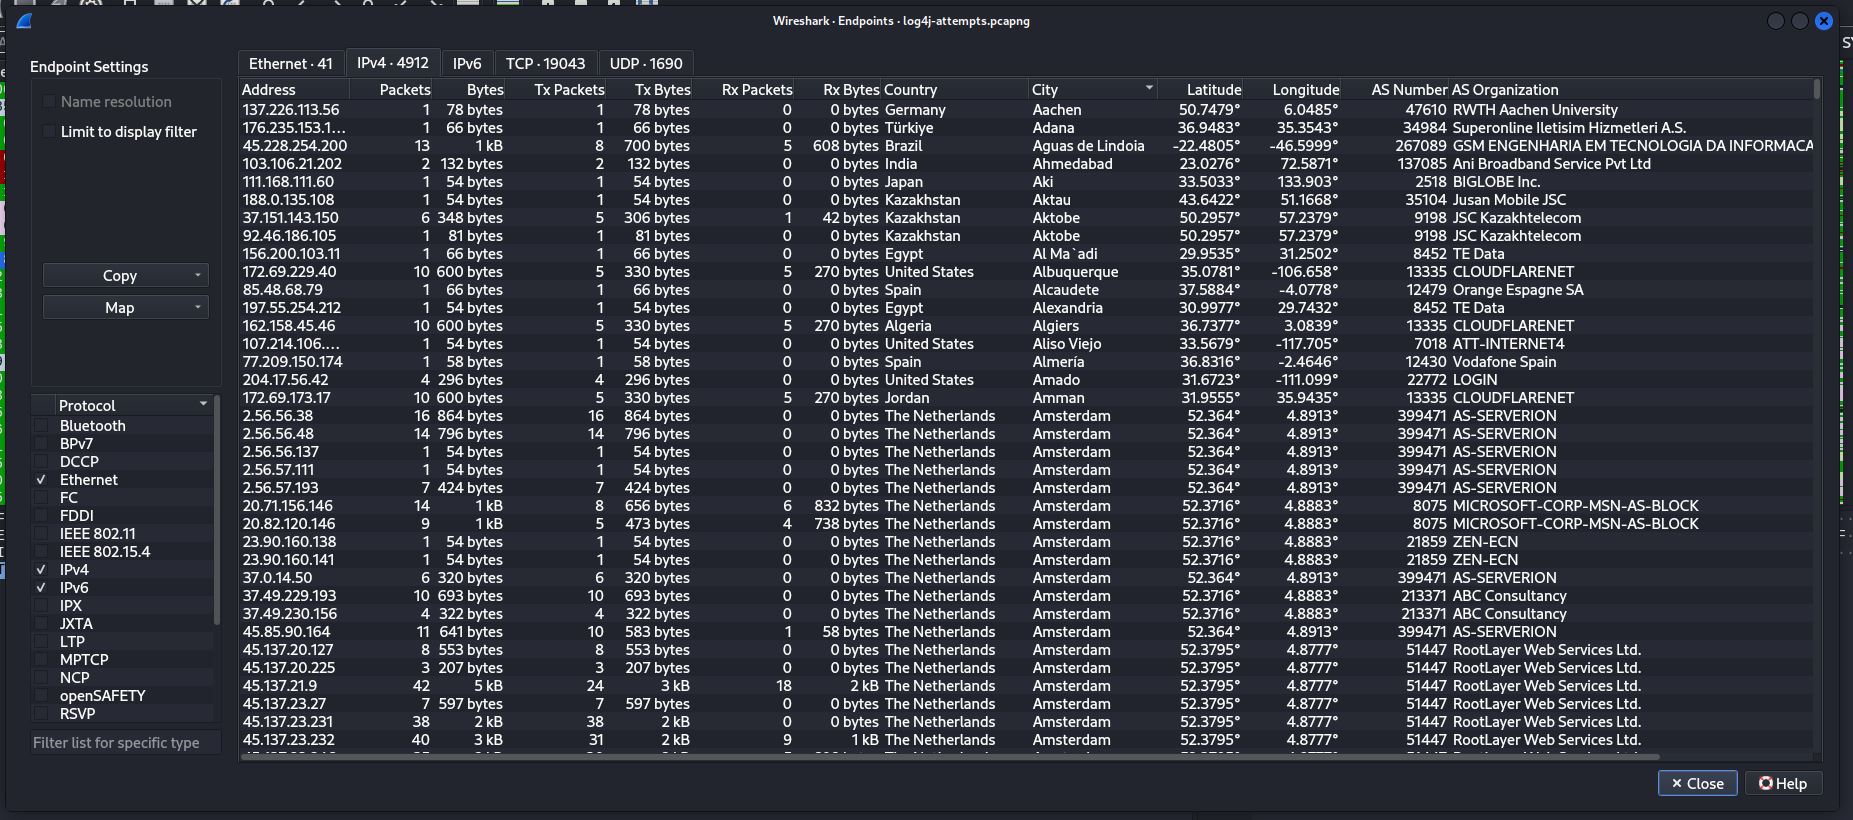 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 redrum0381/ataboy
ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…