

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
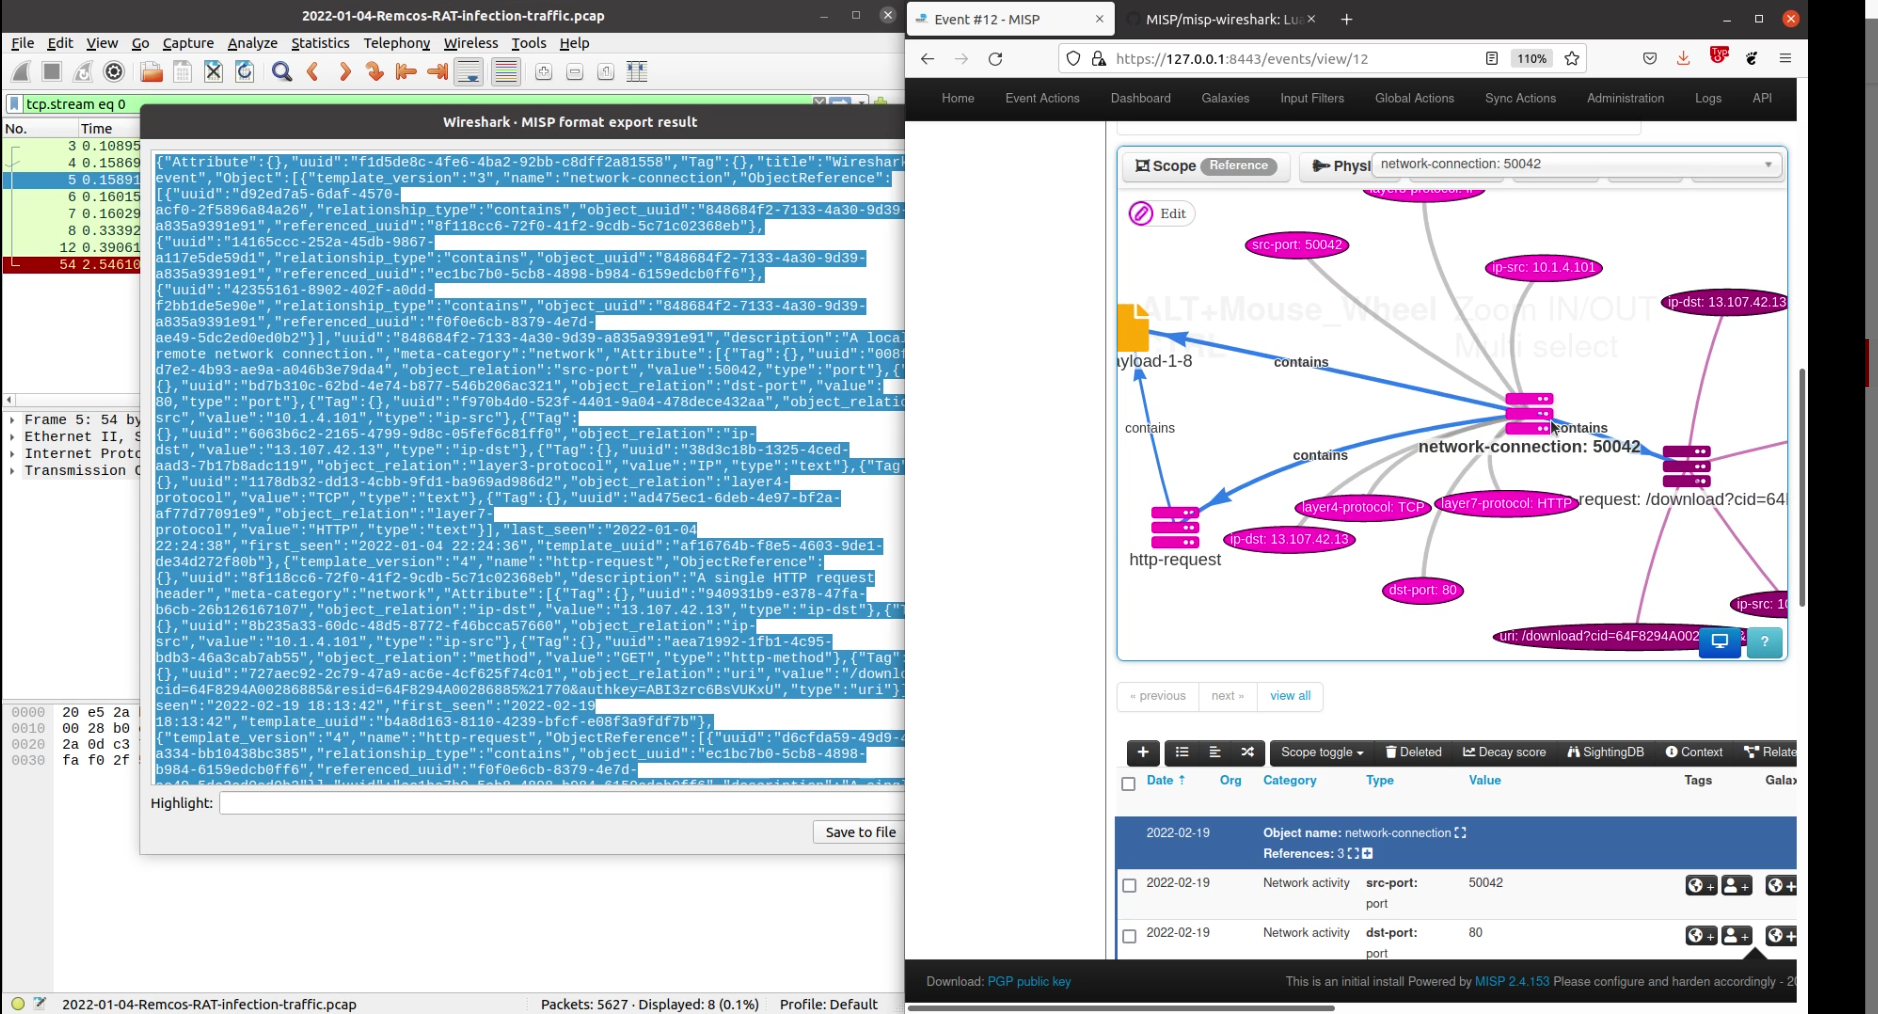 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…