
mboxshell
 dcarrero/mboxshell
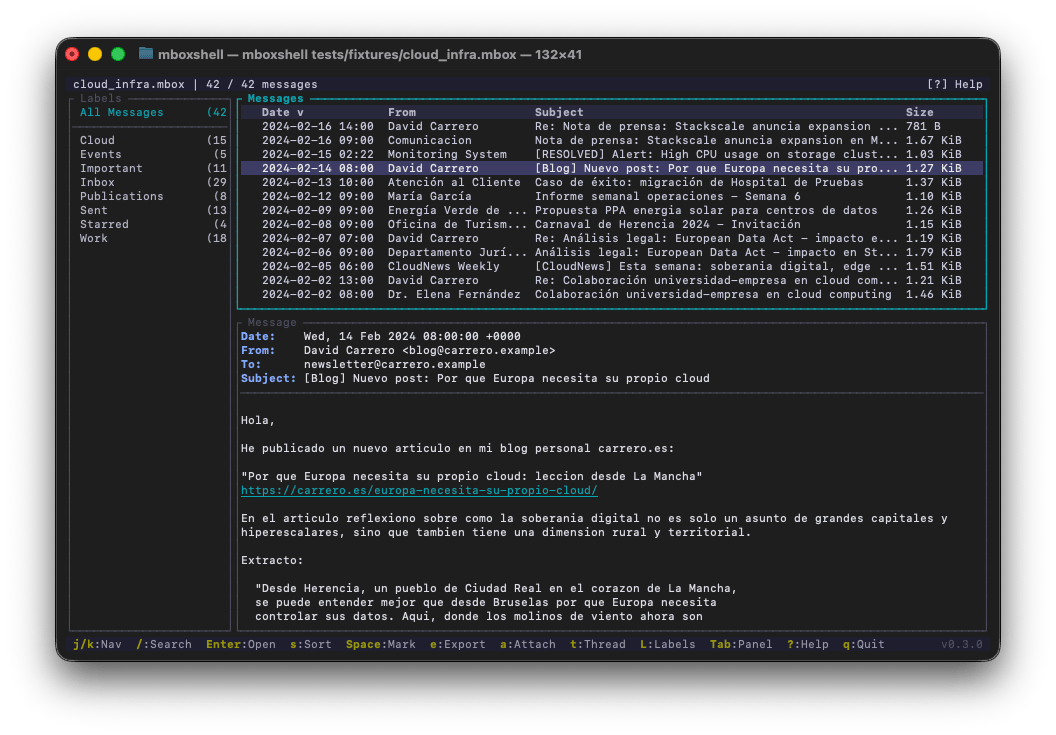
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
data-recoverydigital-forensicsemail-security+4
31
dcarrero/mboxshellmboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 omerbenamram/evtx
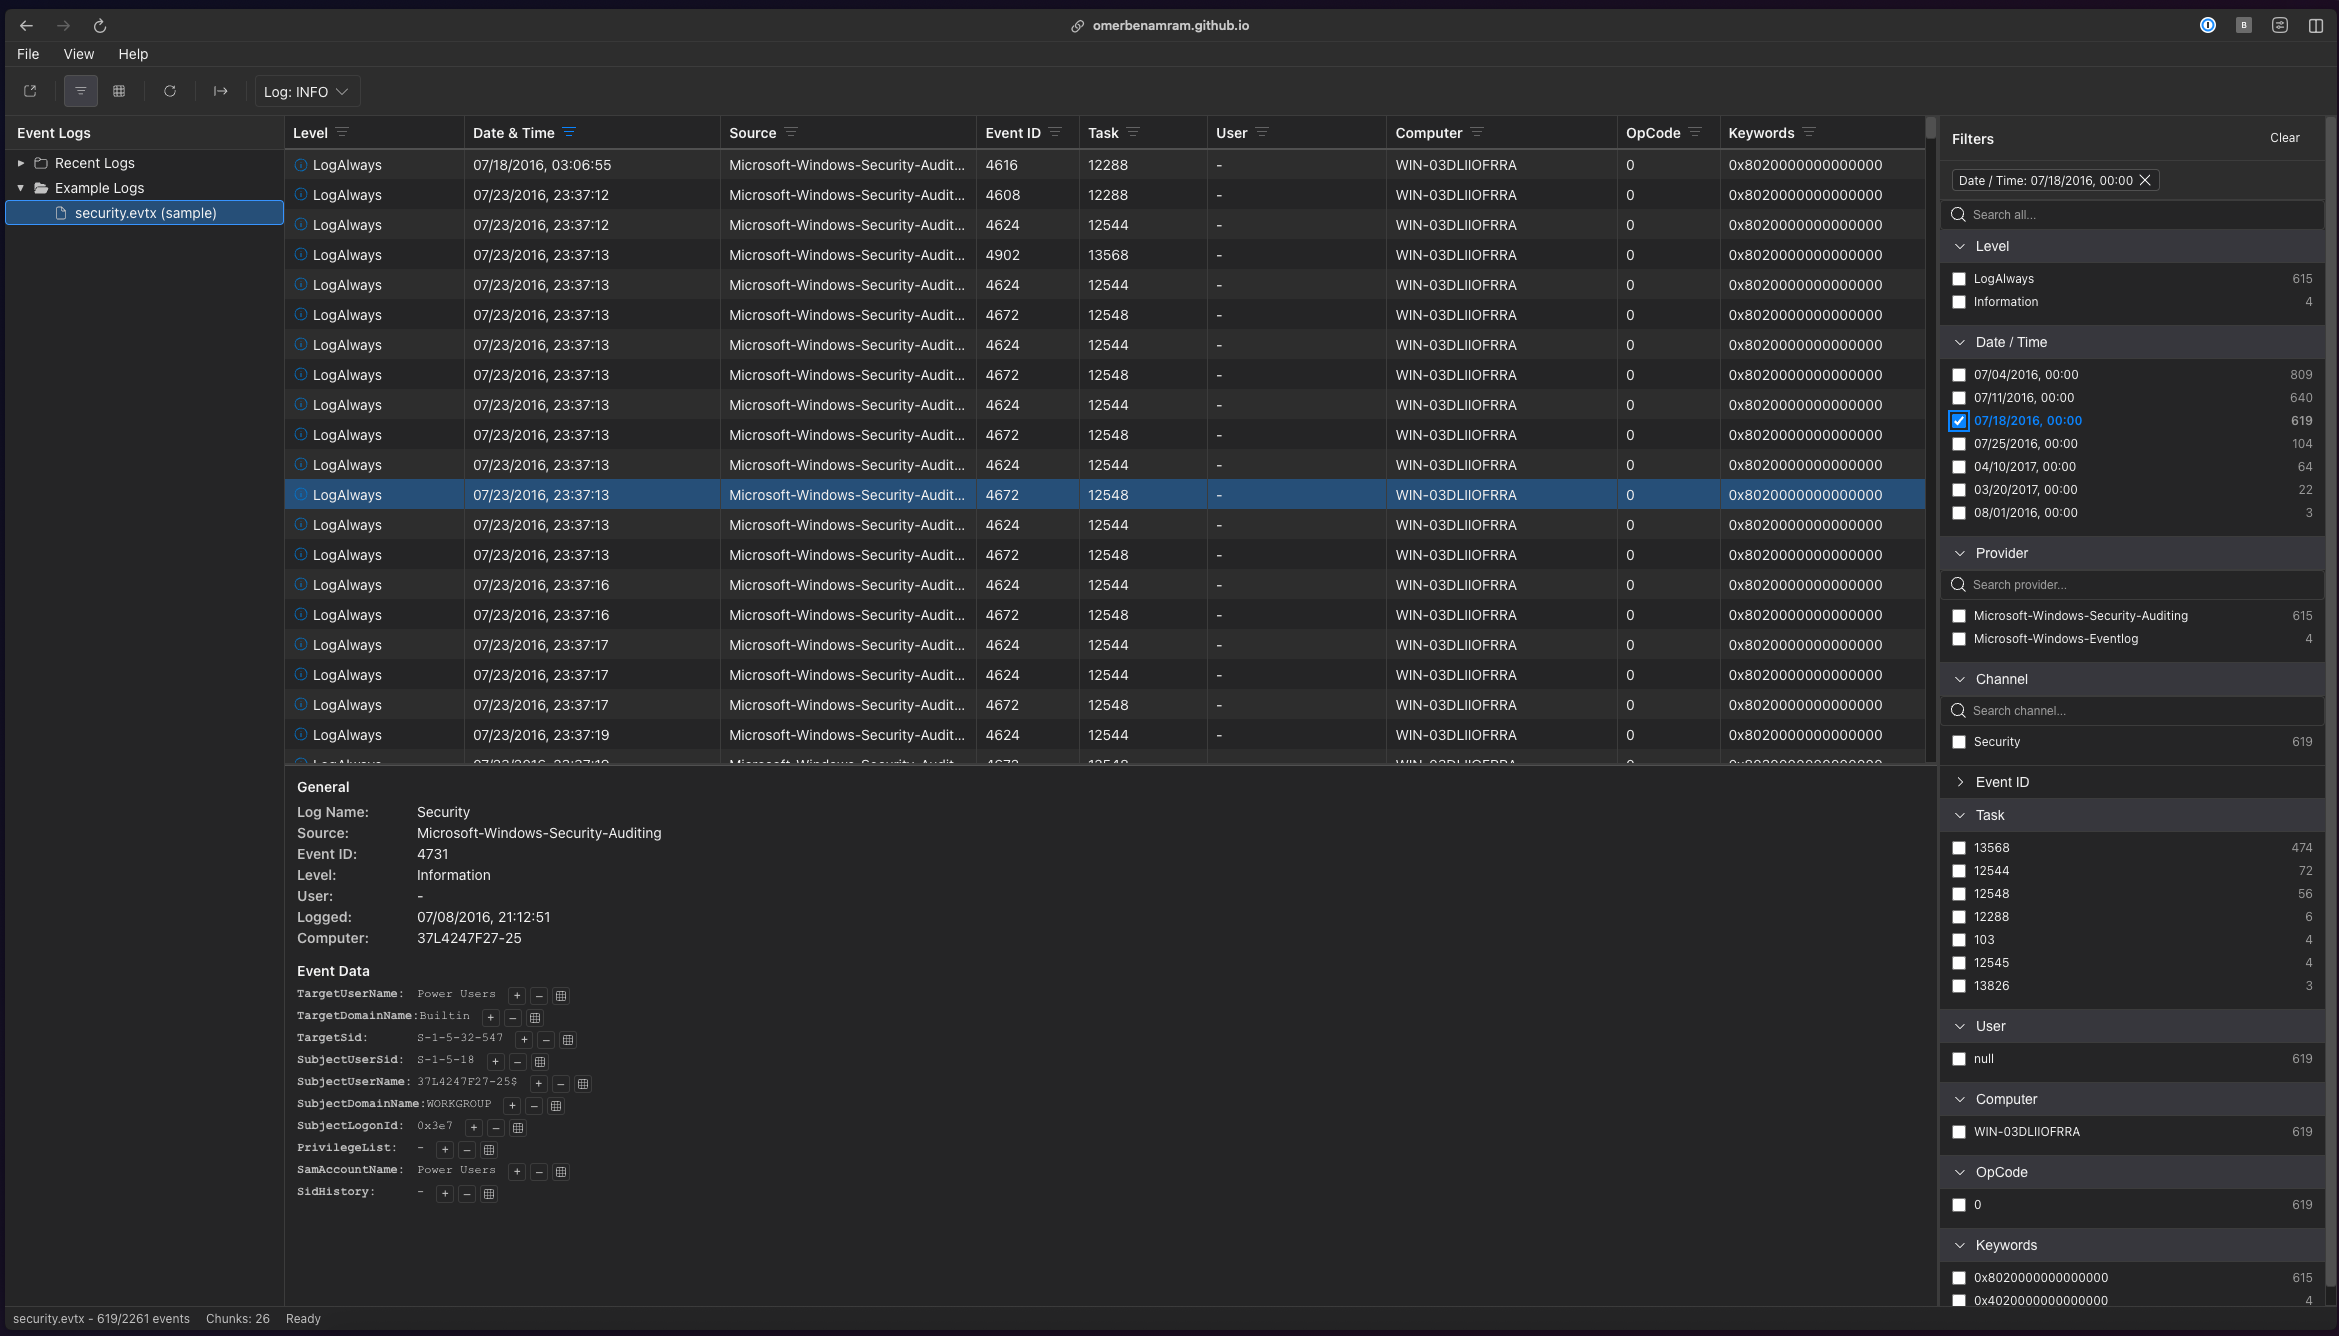
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 circl/ail-framework
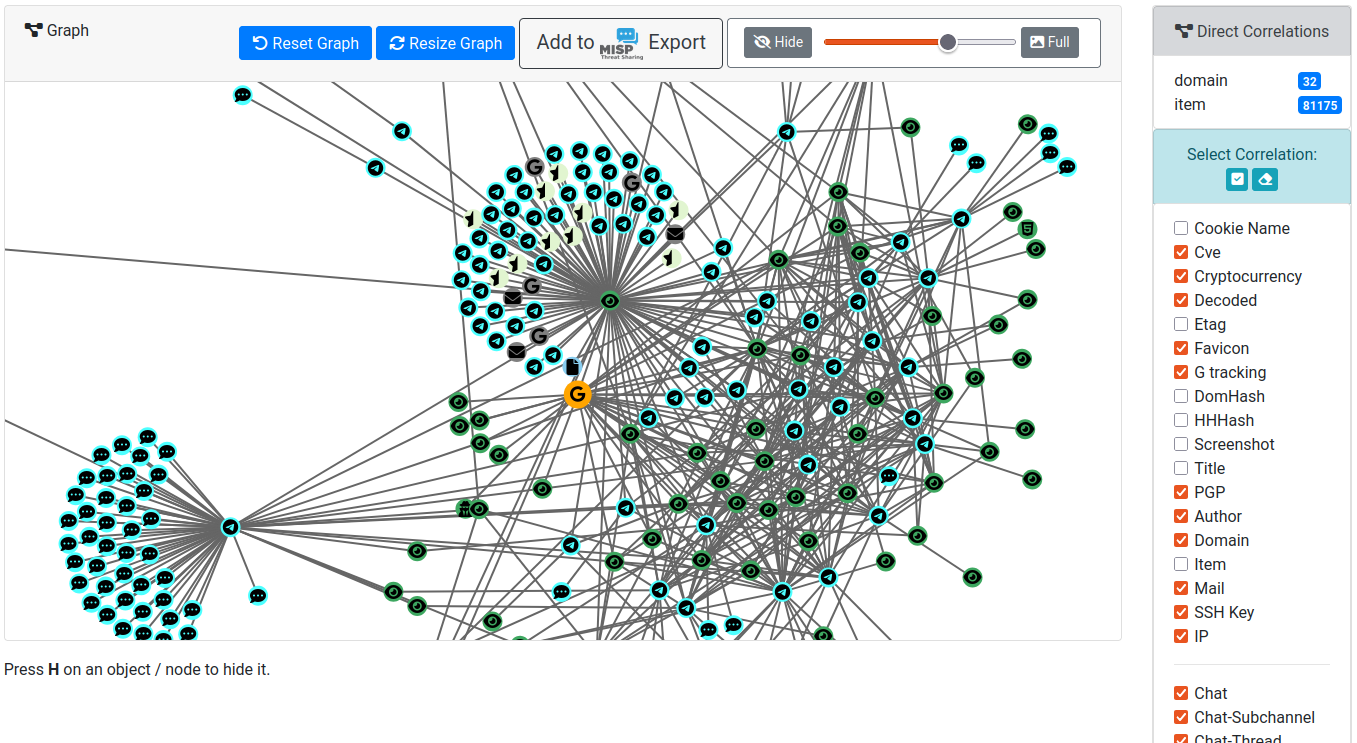
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 cea-sec/usbsas
Tool and framework for securely reading untrusted USB mass storage devices.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
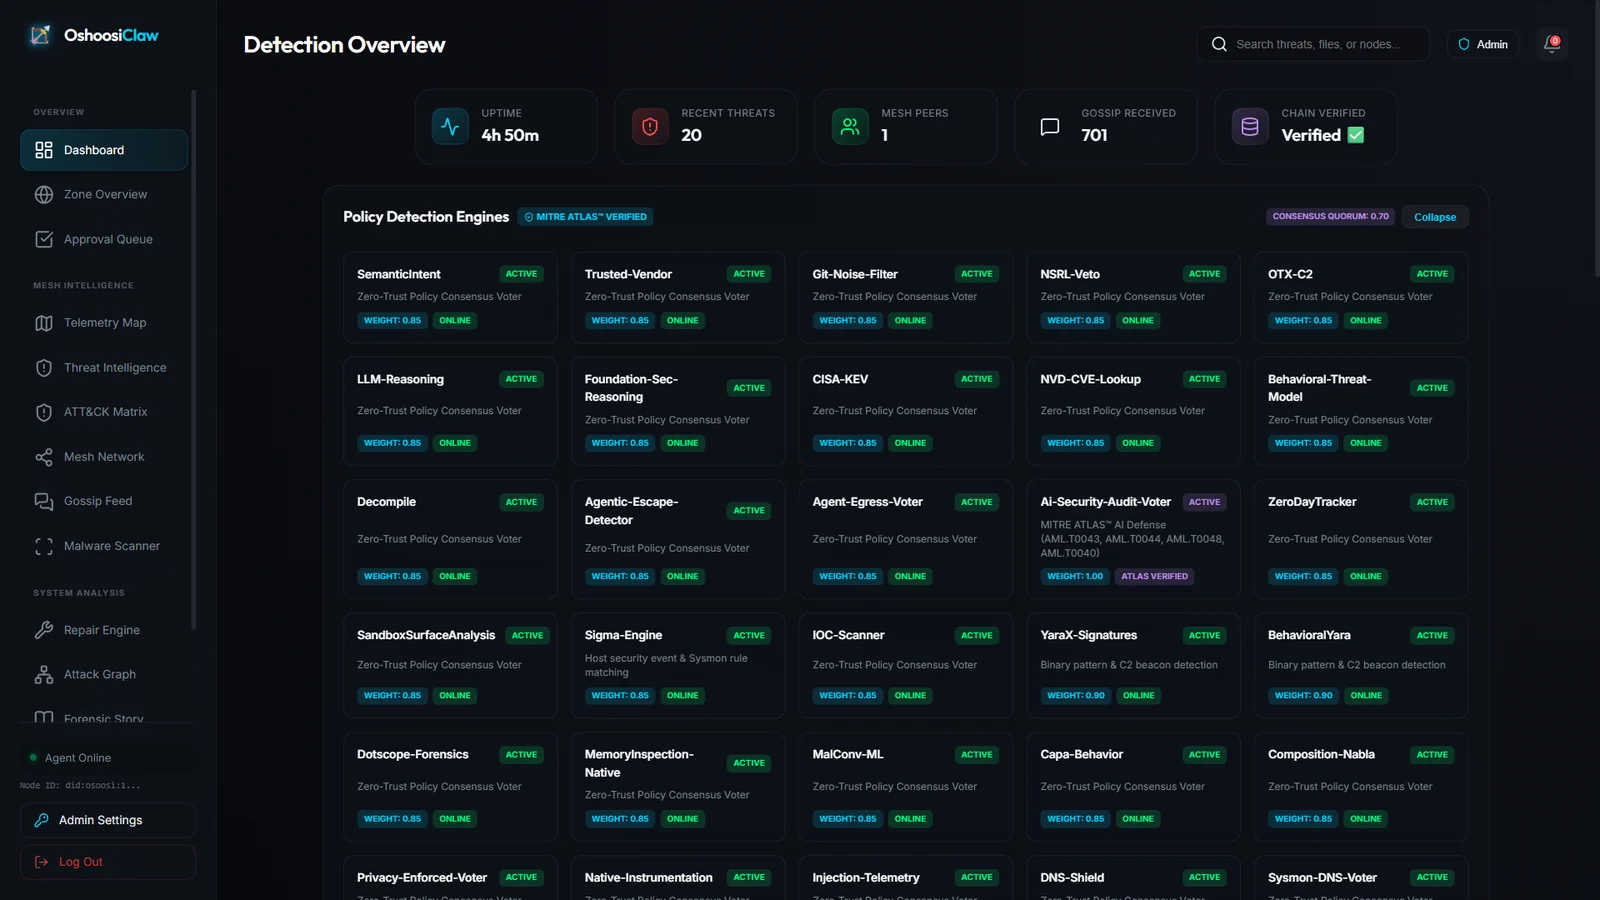 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 irsdl/webhacklist
Archive of the Top 10 Web Hacking Techniques - every nominee since 2006, preserved
 abrignoni/aleapp
Android Logs Events And Protobuf Parser