
iLEAPP
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
abrignoni/ileappParses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 graphworlok/cve-2021-35394-ecosystem
Tracking the family of unrelated IoT botnets sharing CVE-2021-35394 as a delivery vector — findings, relationships, methodology.
 mkorman90/regipy
Regipy is an os independent python library for parsing offline registry hives
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
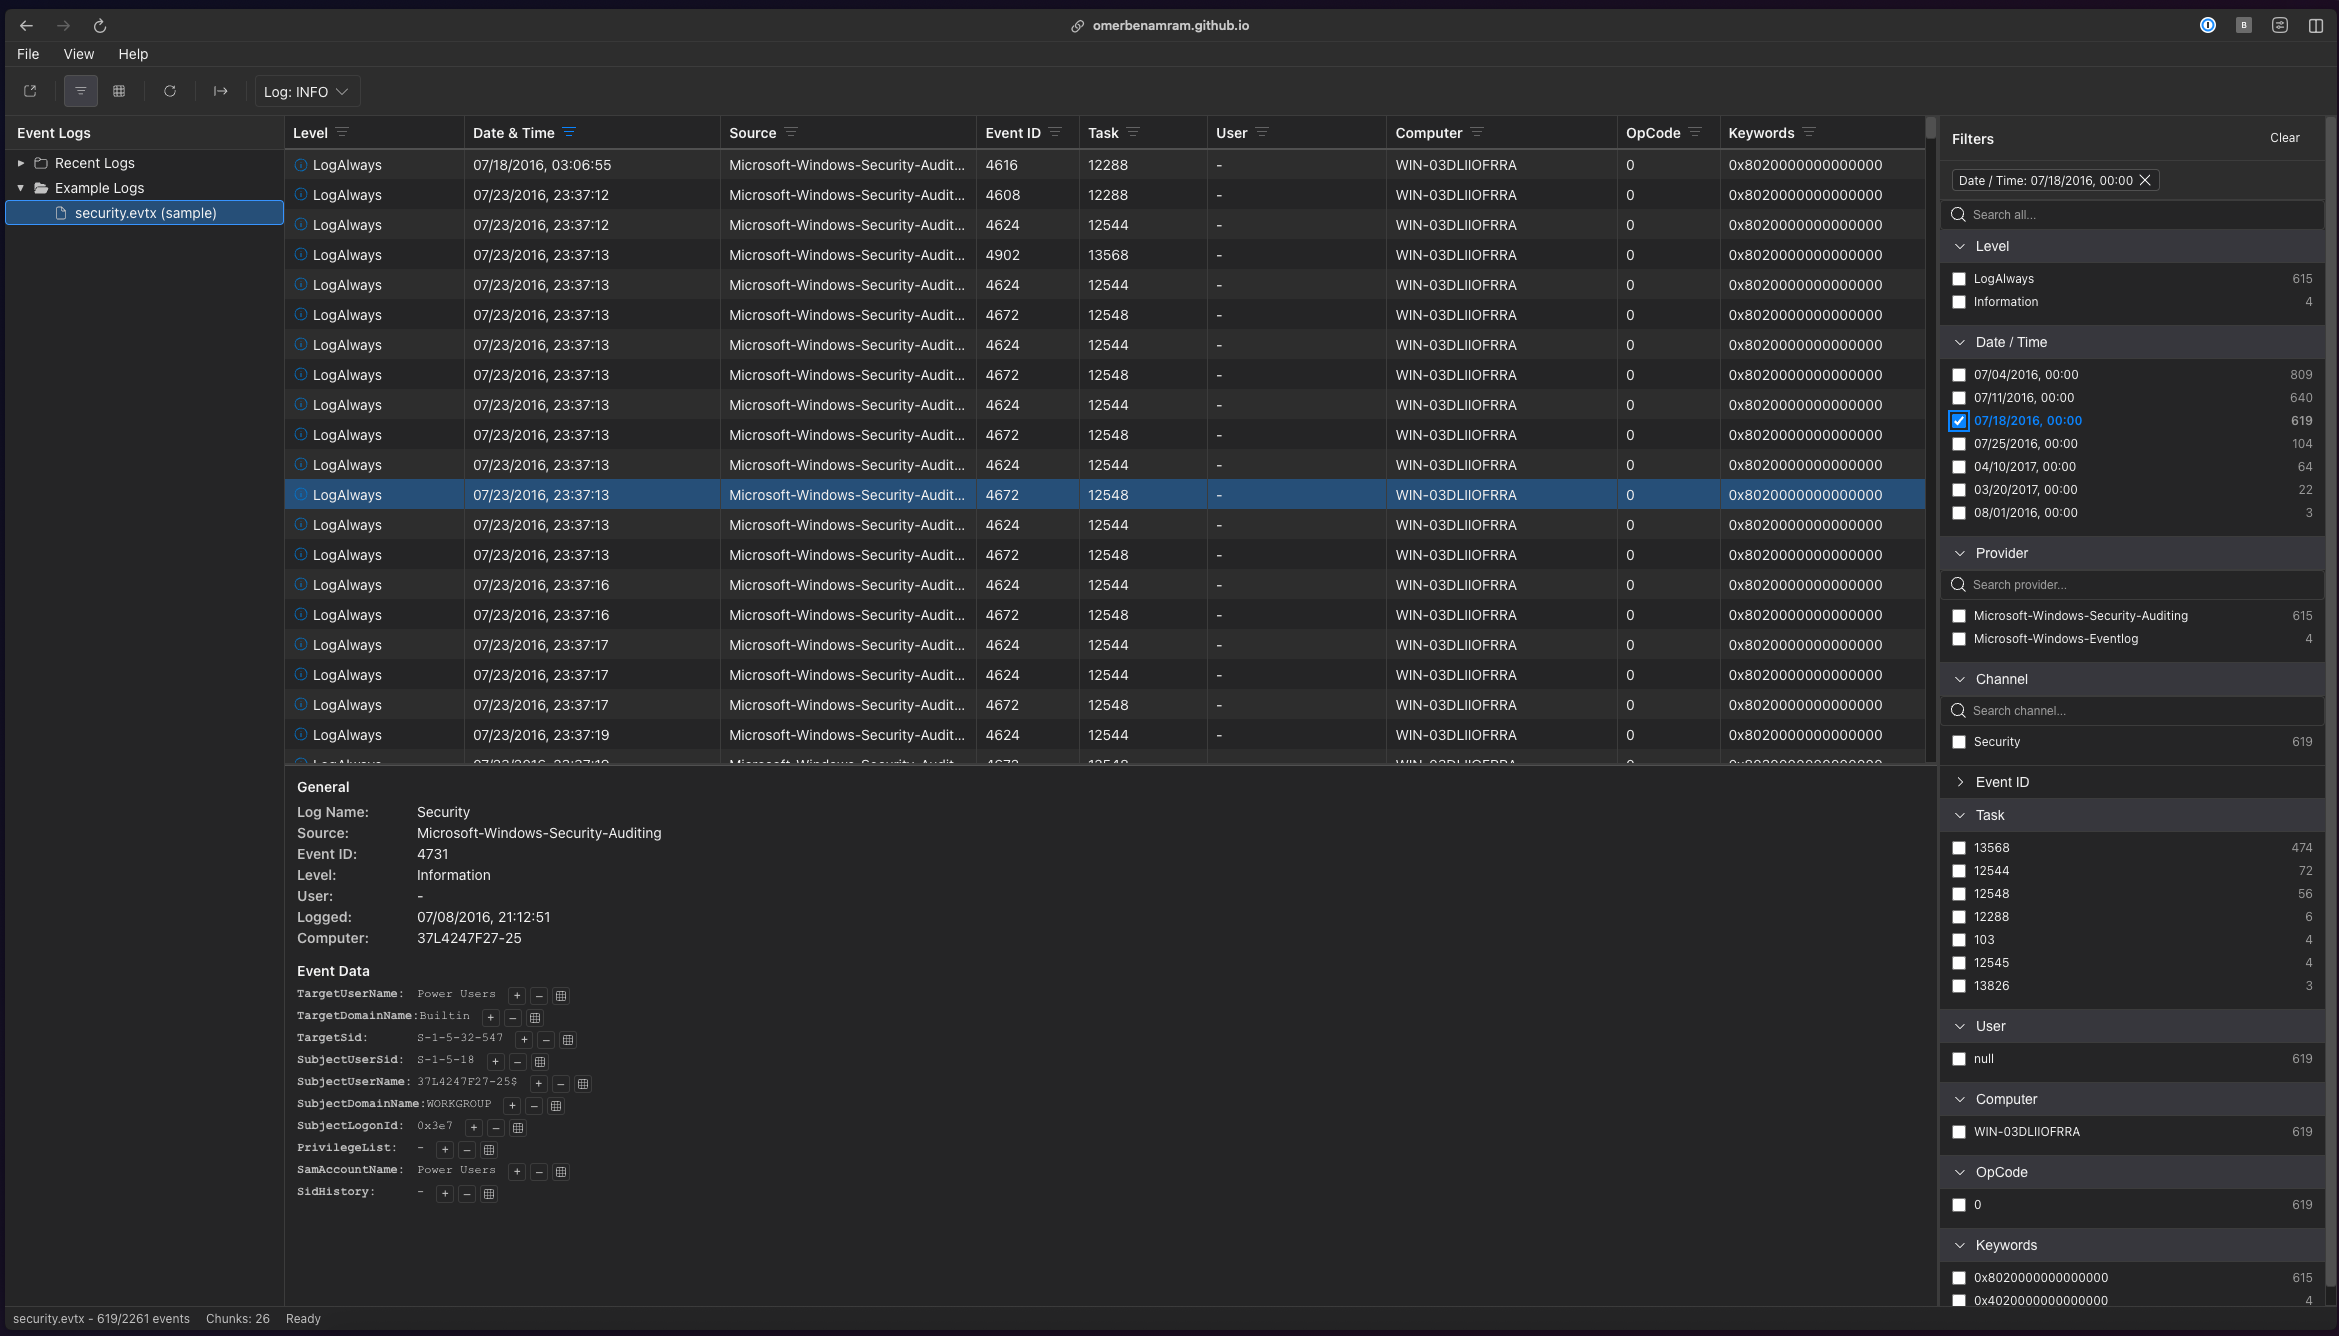 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
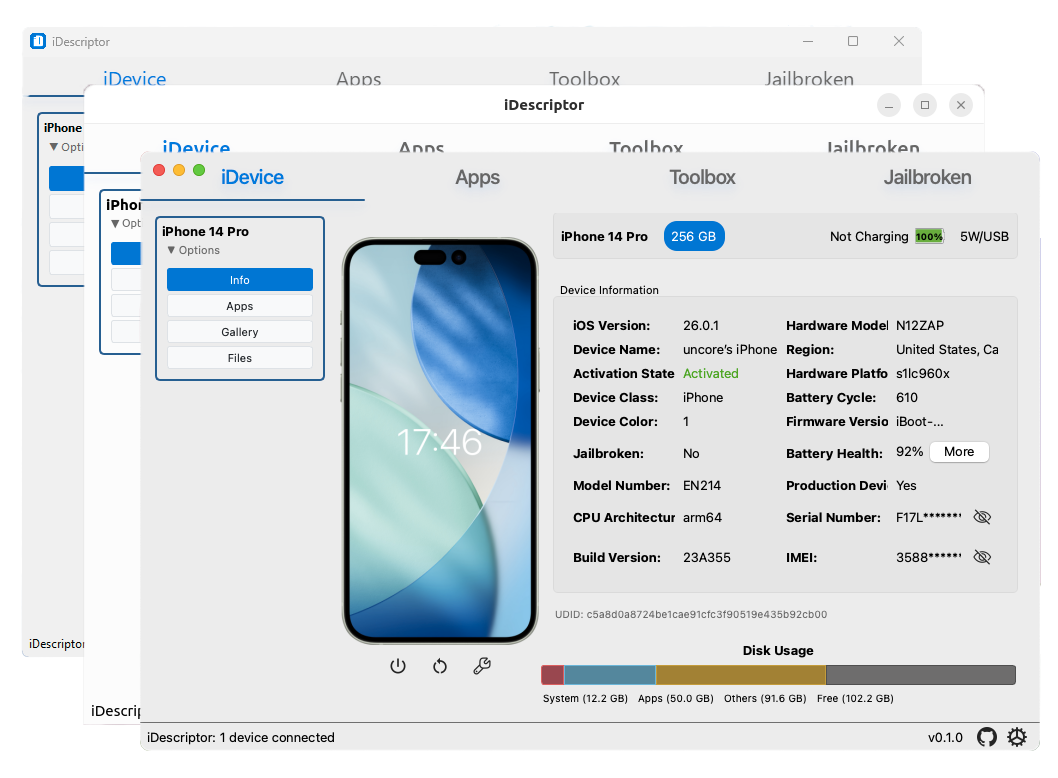 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
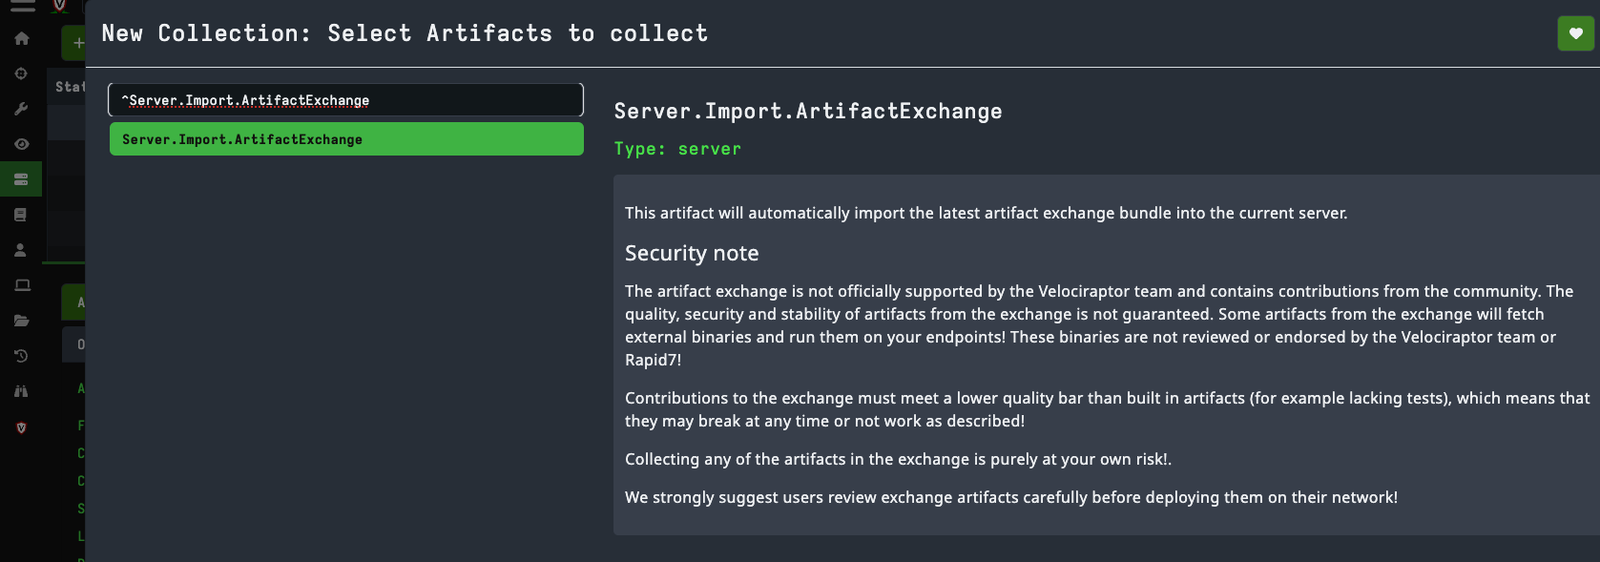 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…