

Argos
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
anomaly-detectiondigital-forensicsinformation-gathering+3
1
functori/argos/argosAnalysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
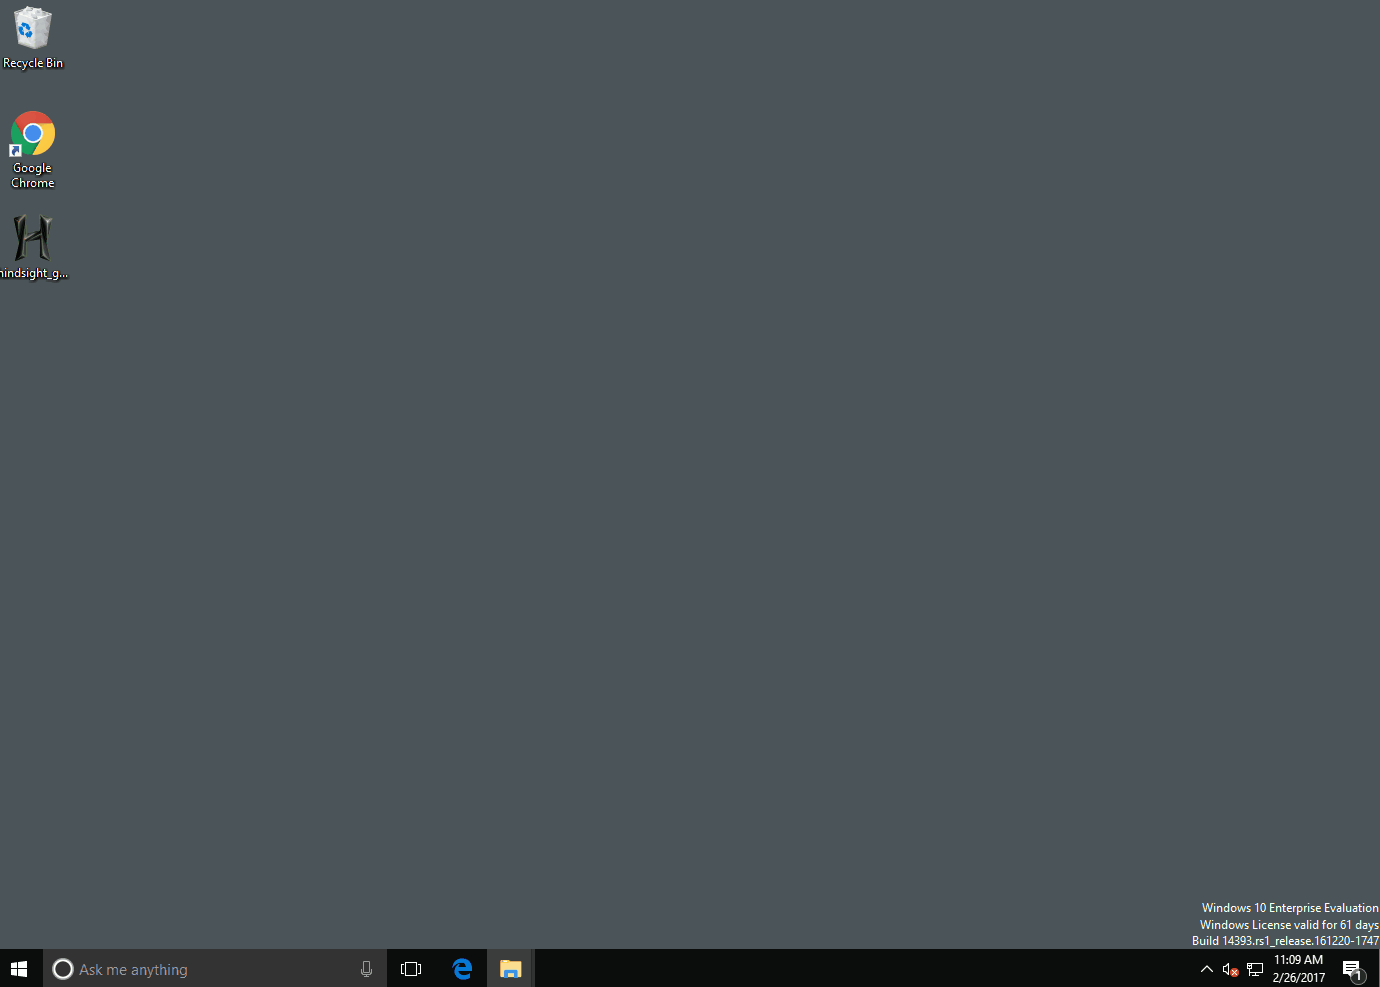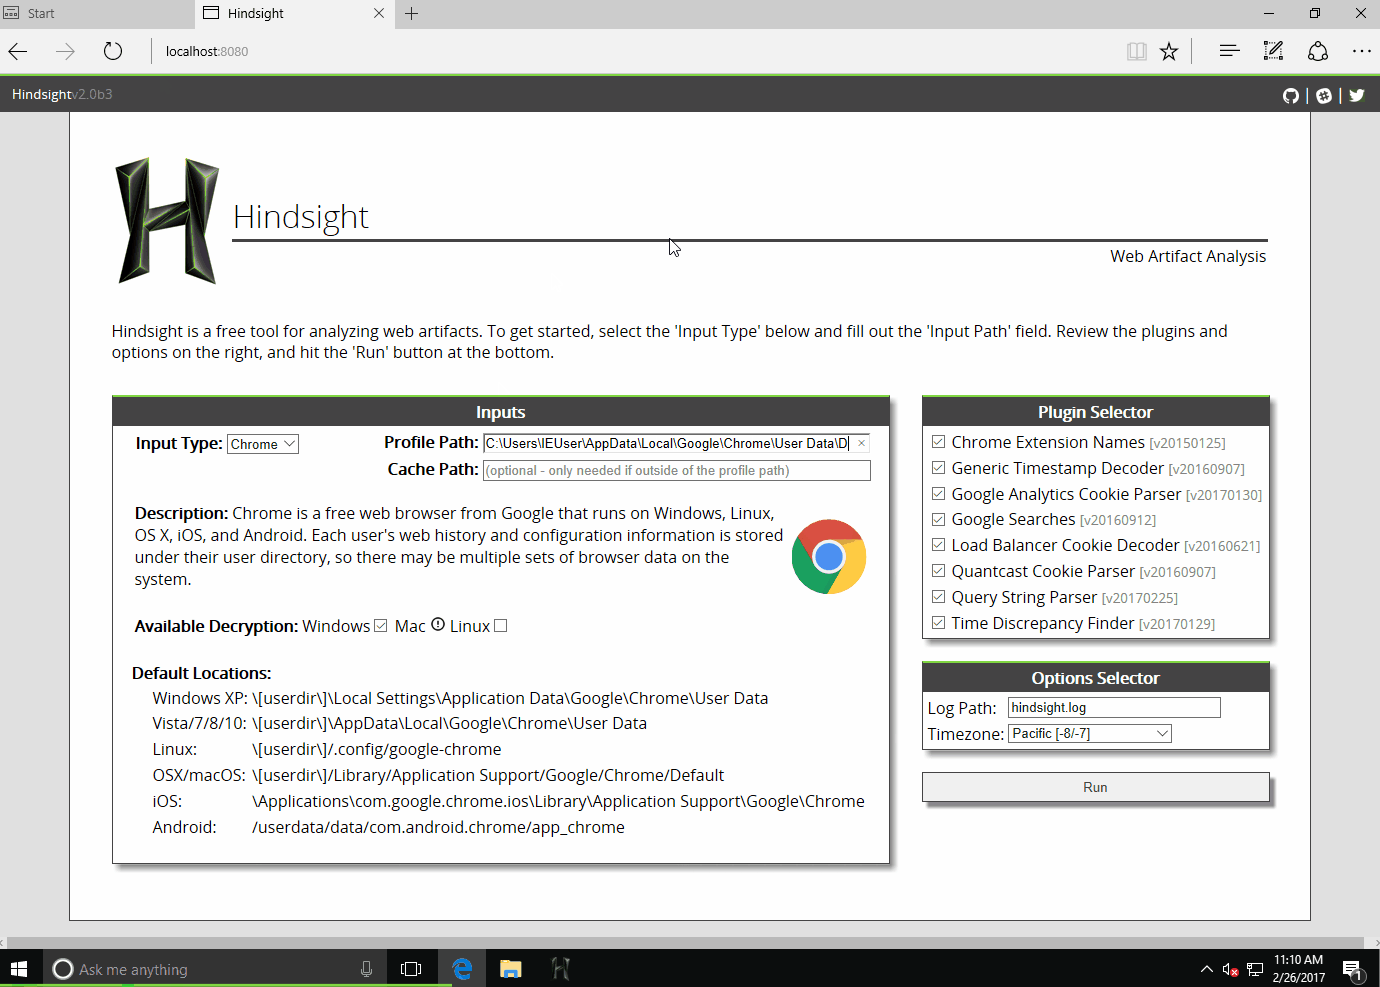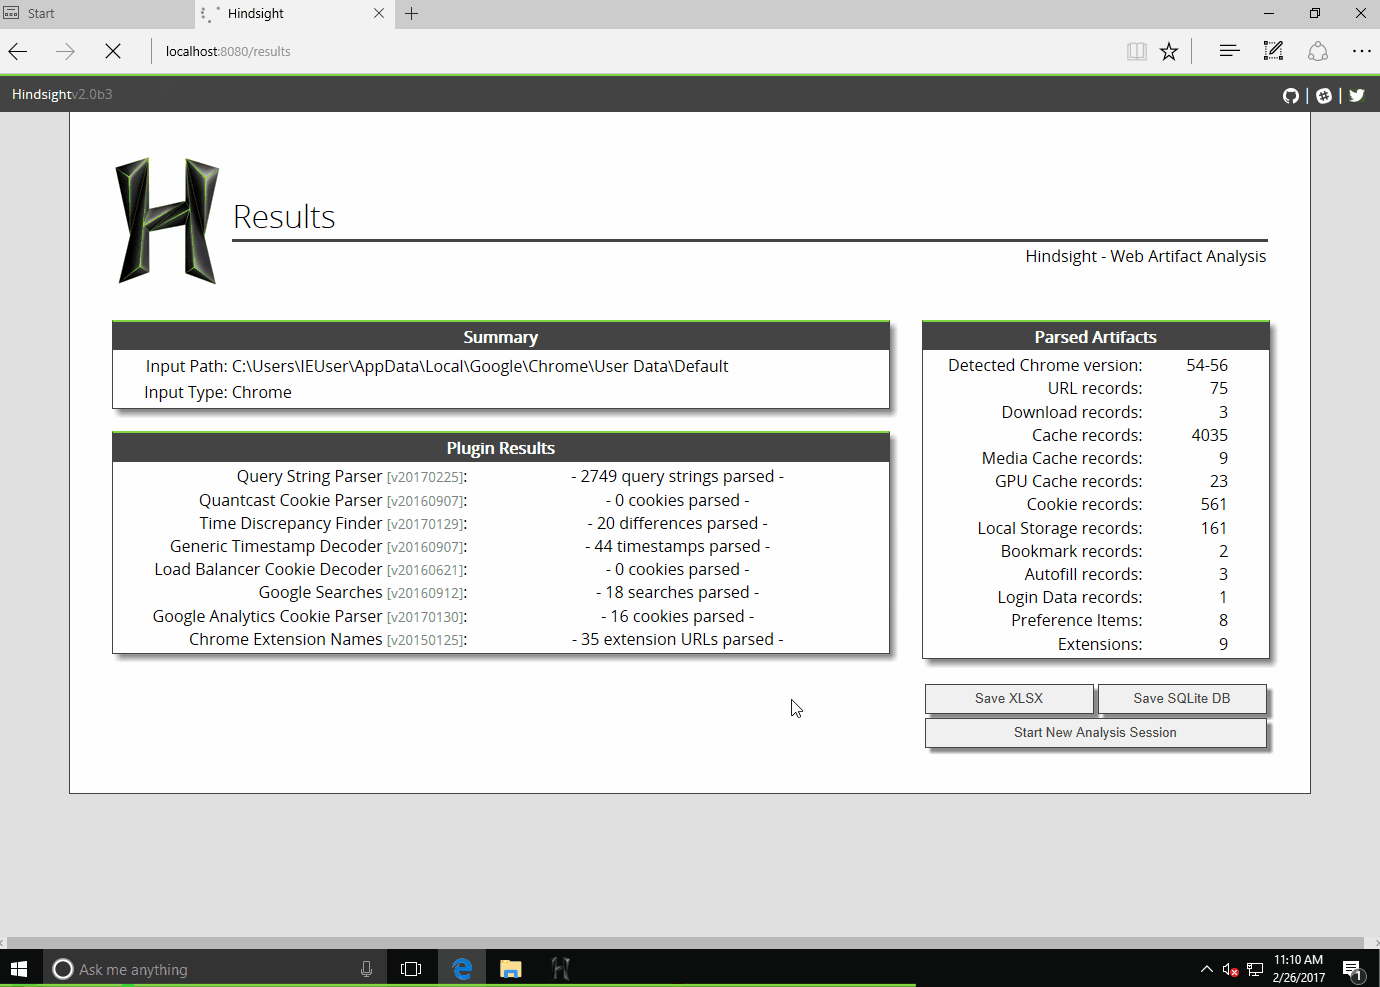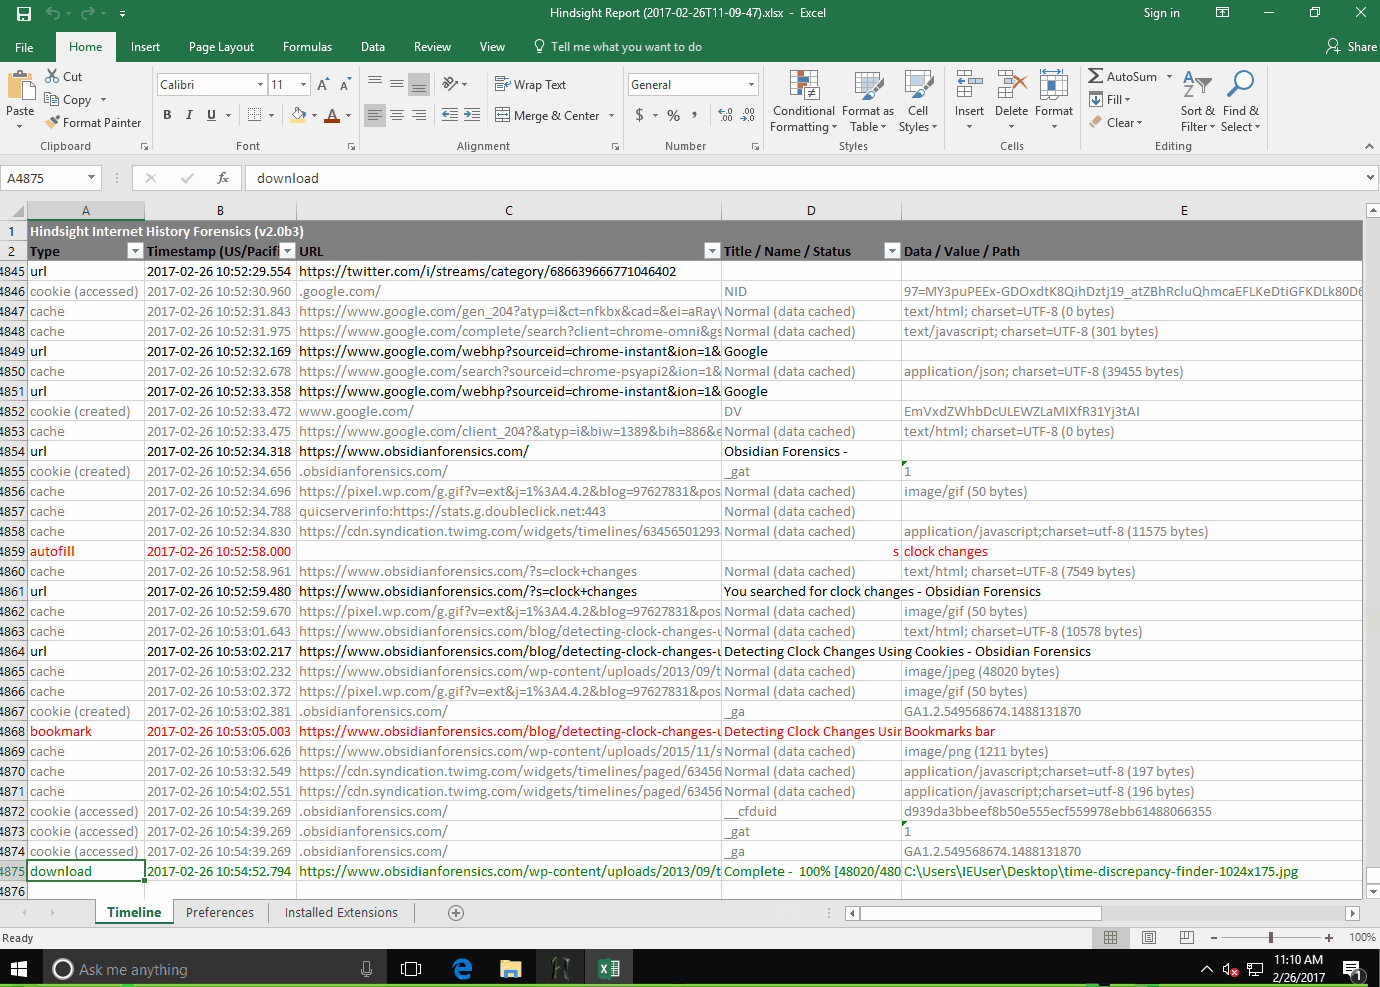 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
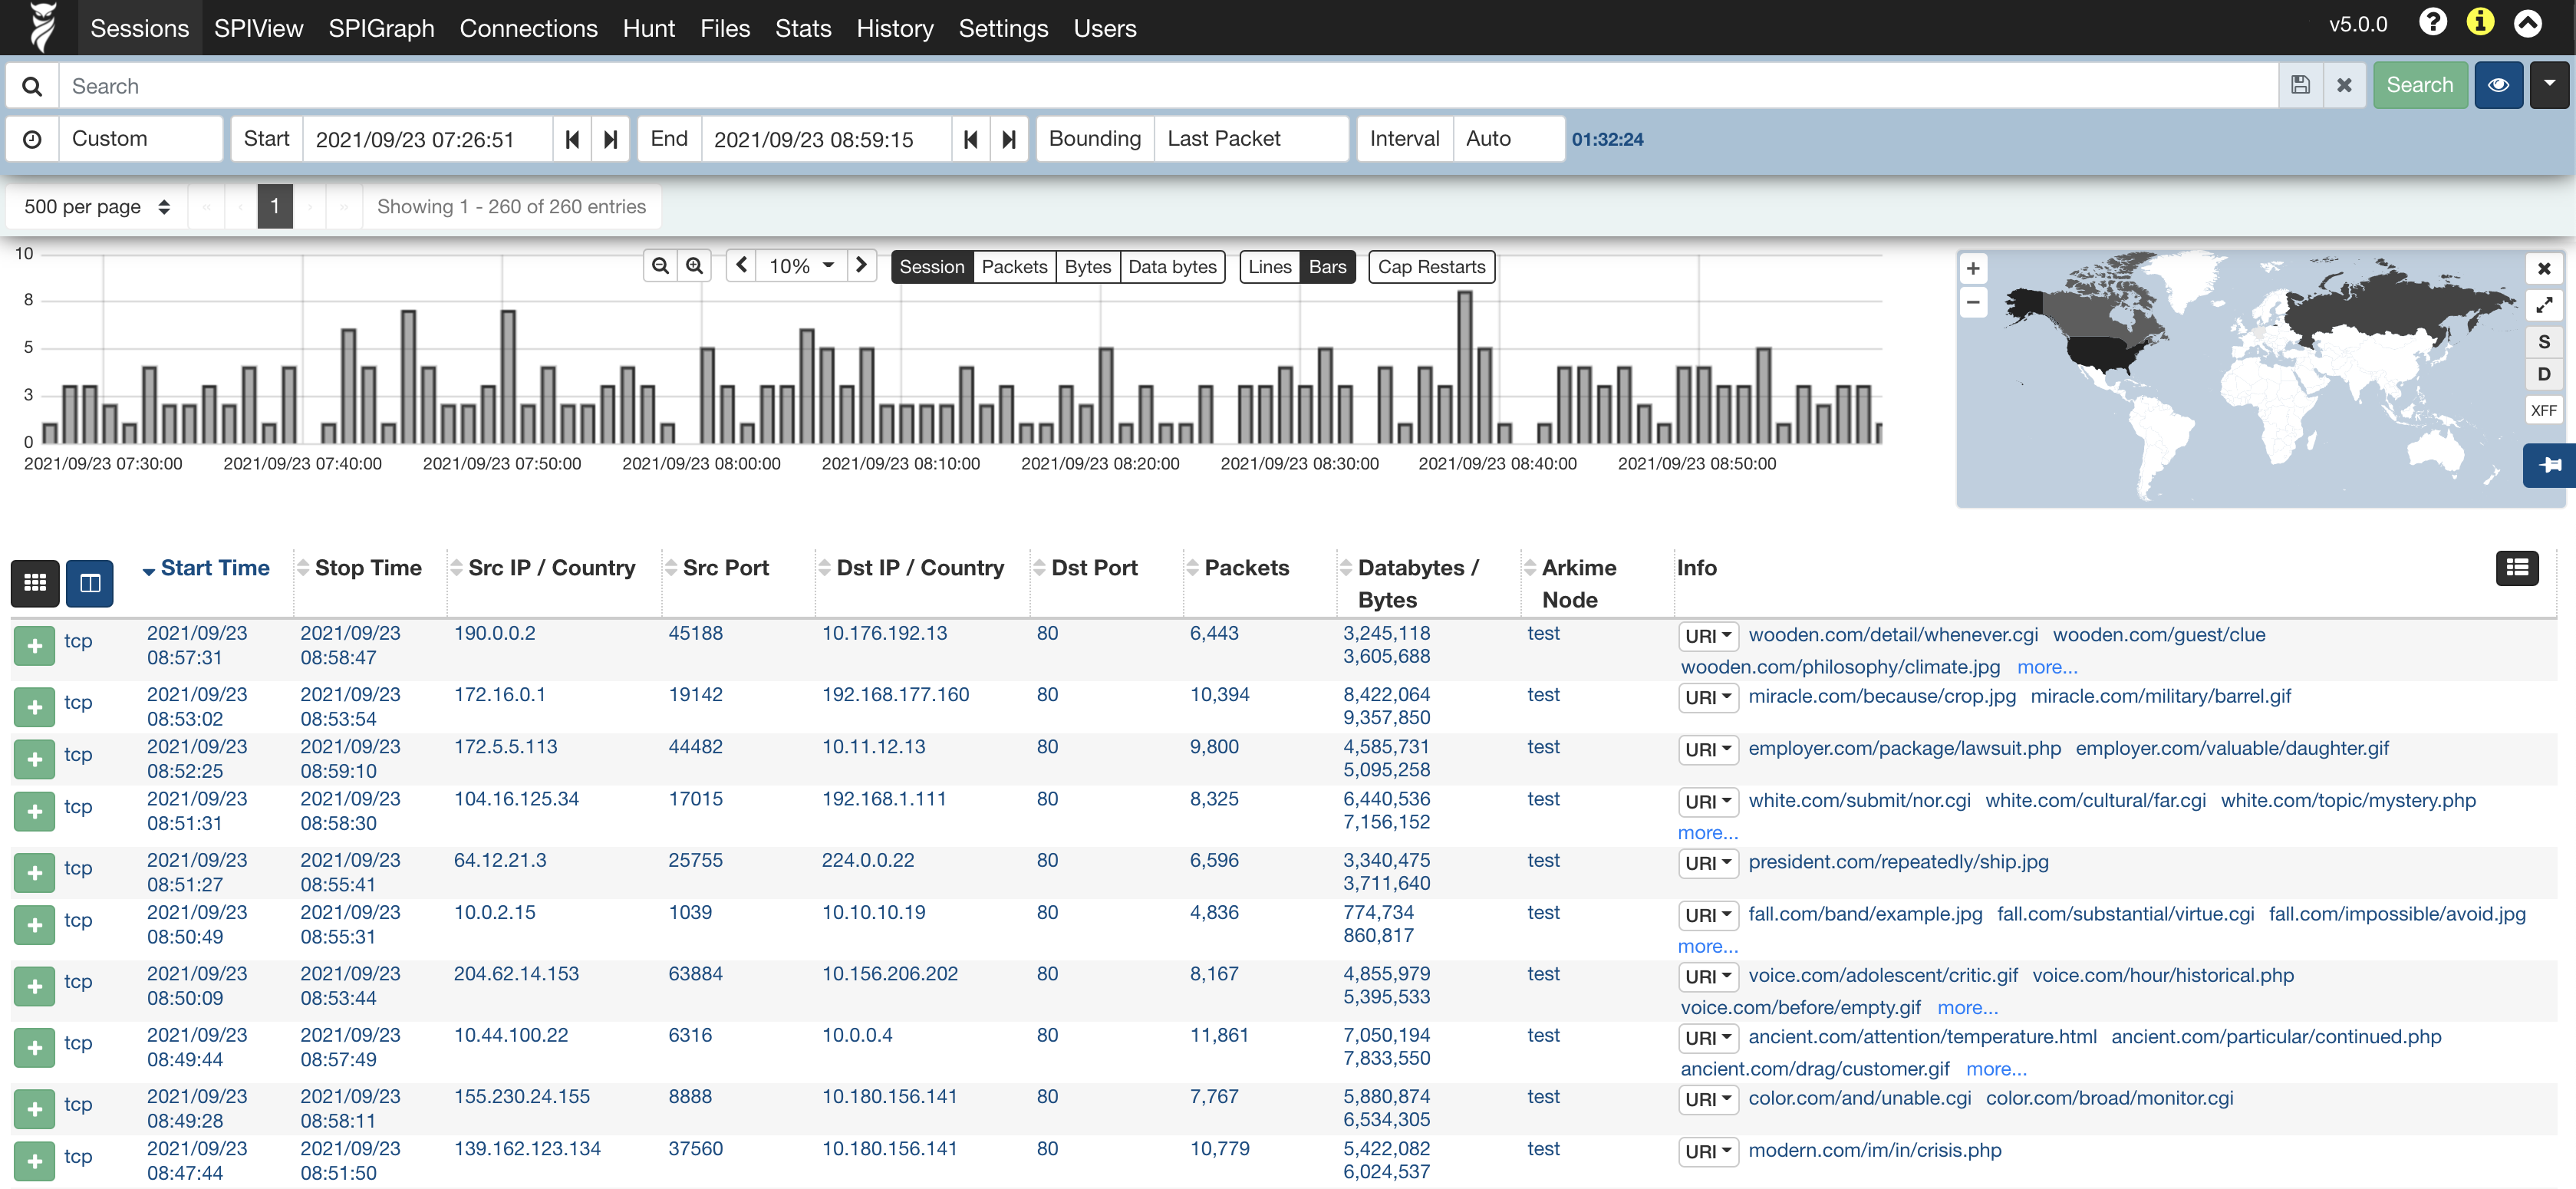 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
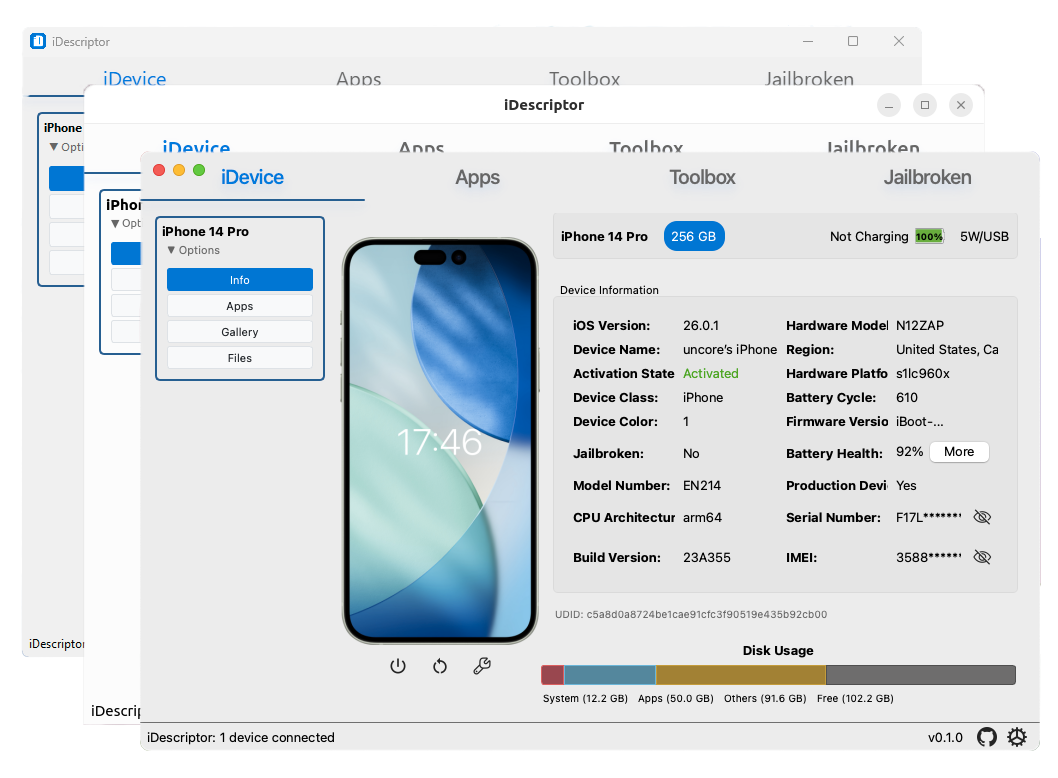 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
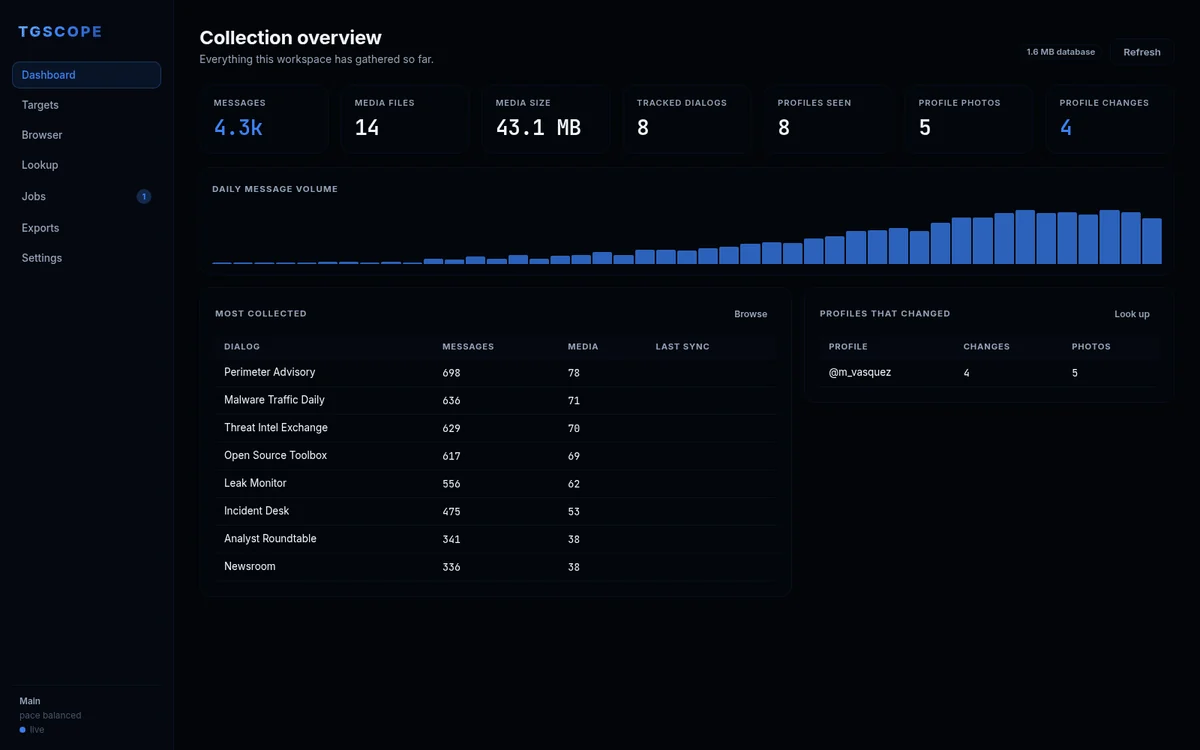 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
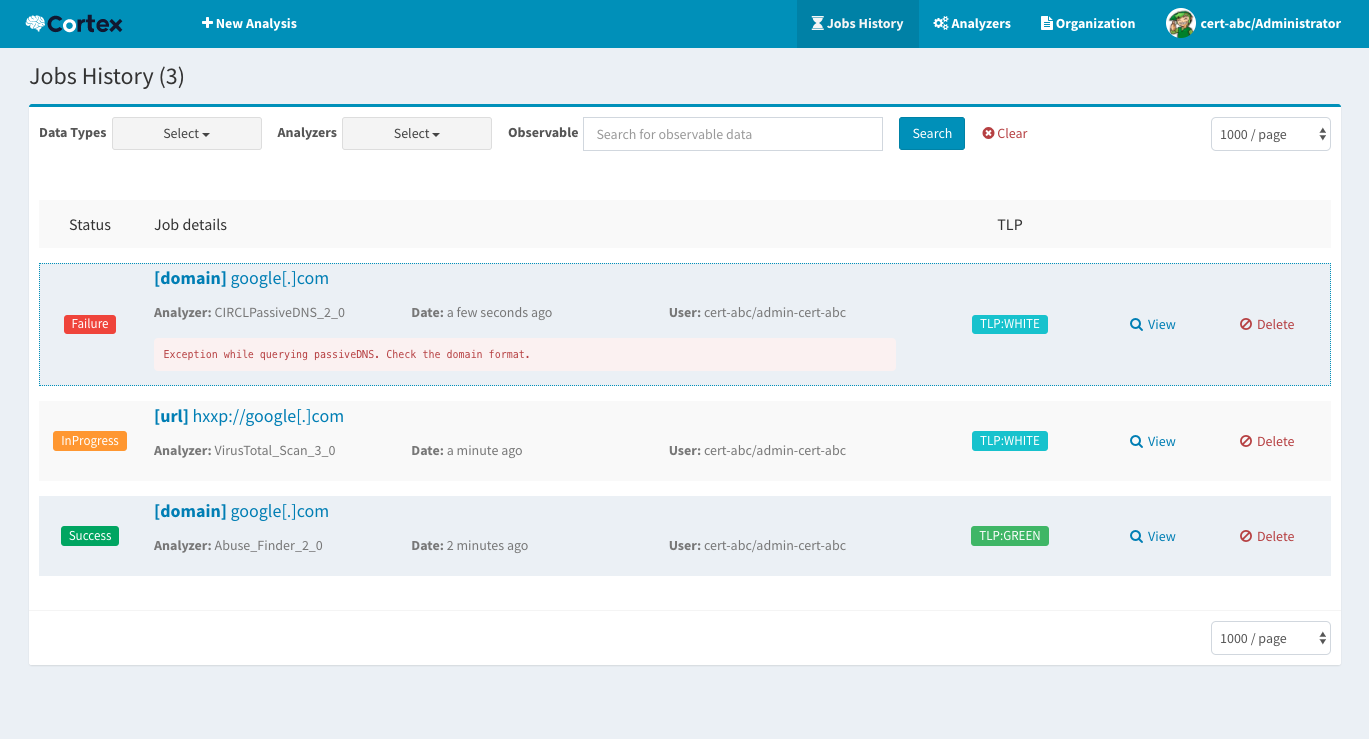 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping

 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…