

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.3k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 dsheirer/sdrtrunk
A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 lazza/recuperabit
A tool for forensic file system reconstruction.
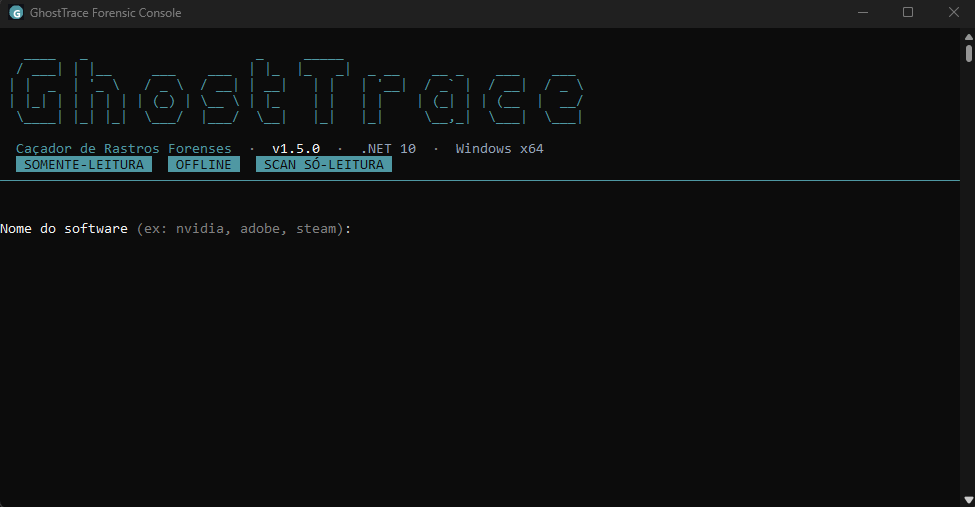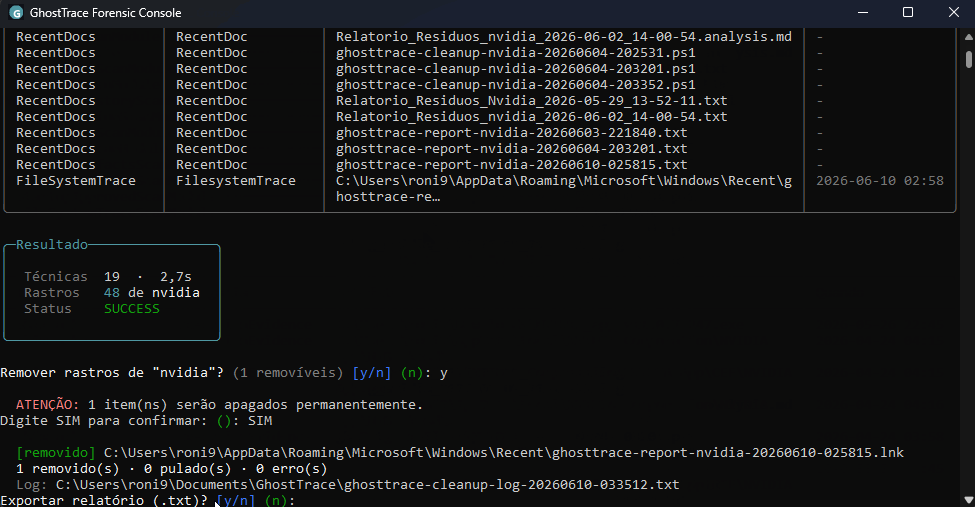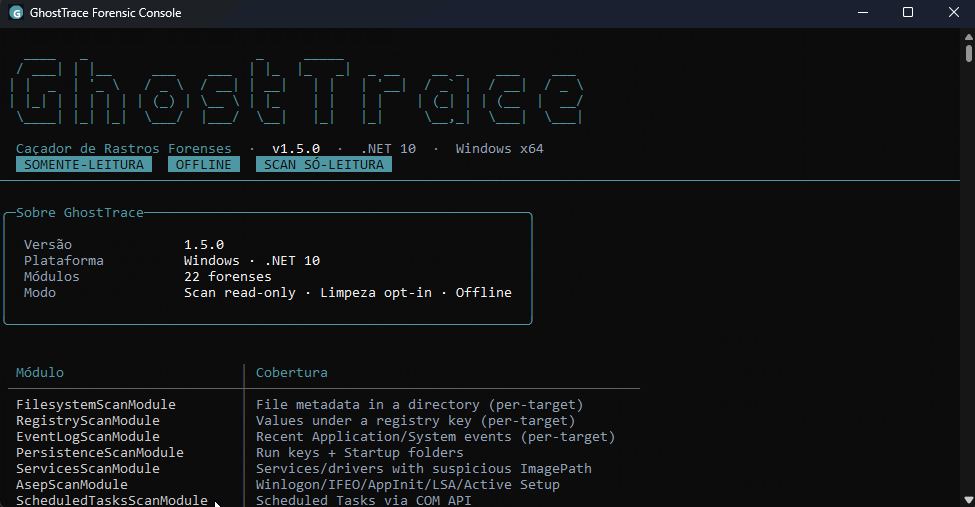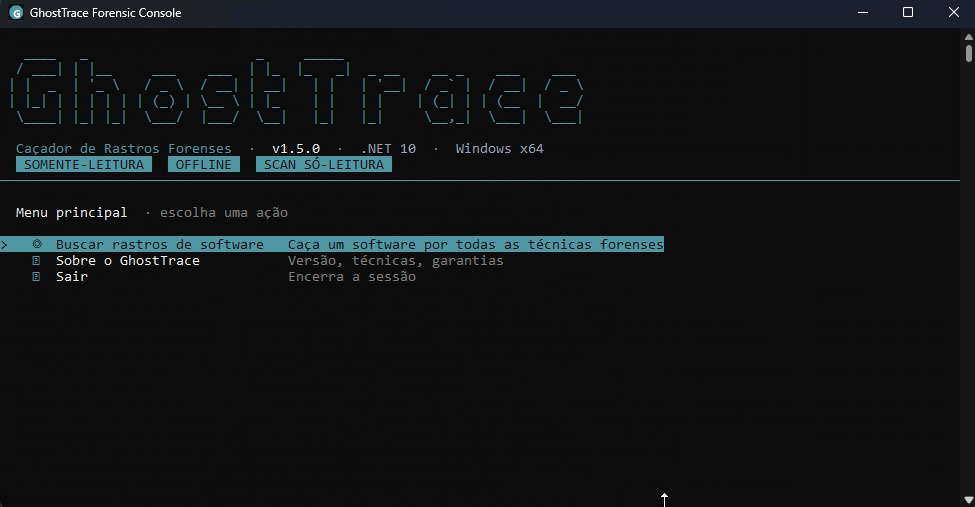 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 ercihan/cve-2026-34621_pdf_sample
Technical analysis of a multi-stage Adobe Acrobat PDF JavaScript sample, detailing environment triage, Acrobat API abuse, and in-memory payload…
 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 sastraadiwiguna-purpleeliteteaming/dissecting-cve-2026-0628-chromium-extension-privilege-escalation
Technical dissection of CVE-2026-0628, a Chromium WebView privilege escalation vulnerability, including root cause analysis, PoC exploit, detection…
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
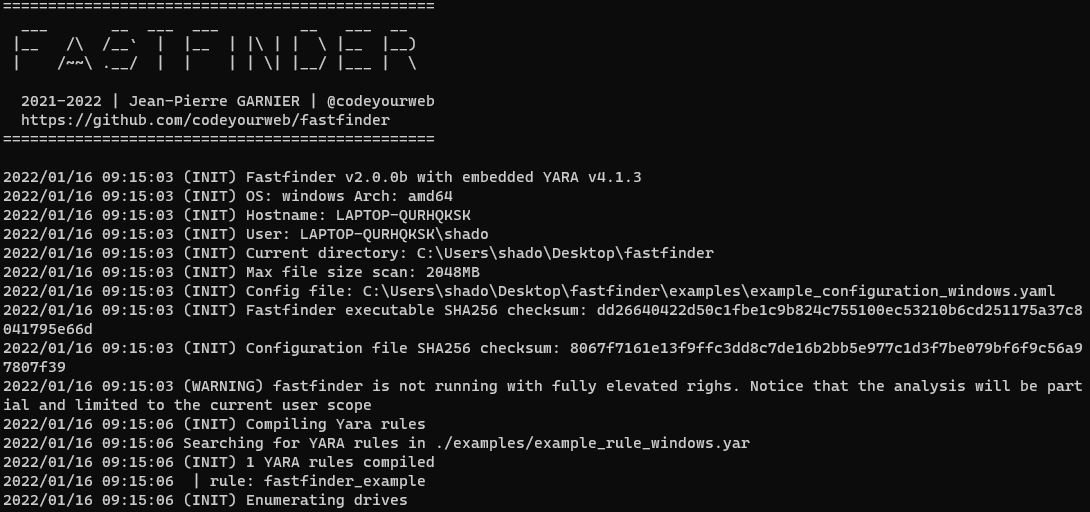 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder