
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
35 results
watermarks-remover preview

watermarks-remover

GitHubguillaumemeyer/watermarks-remover

A privacy-first app that strips AI watermarks from content you own.
adversarial-attackai-securitydigital-forensics+5
22.8k
11h 24m ago
regipy preview

regipy

GitHubmkorman90/regipy

Regipy is an os independent python library for parsing offline registry hives

digital-forensicsforensicsincident-response+1
27711 days ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
digital-forensicsforensicsincident-response+2
3.4k12 days ago
psa-2026-00043-recovery preview

psa-2026-00043-recovery

GitHubdisqualifier/psa-2026-00043-recovery

Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
cloud-infrastructure-securitydata-recoverydigital-forensics+3
21 days ago
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k1 month ago
NetScope preview

NetScope

GitHubspectralzero/netscope

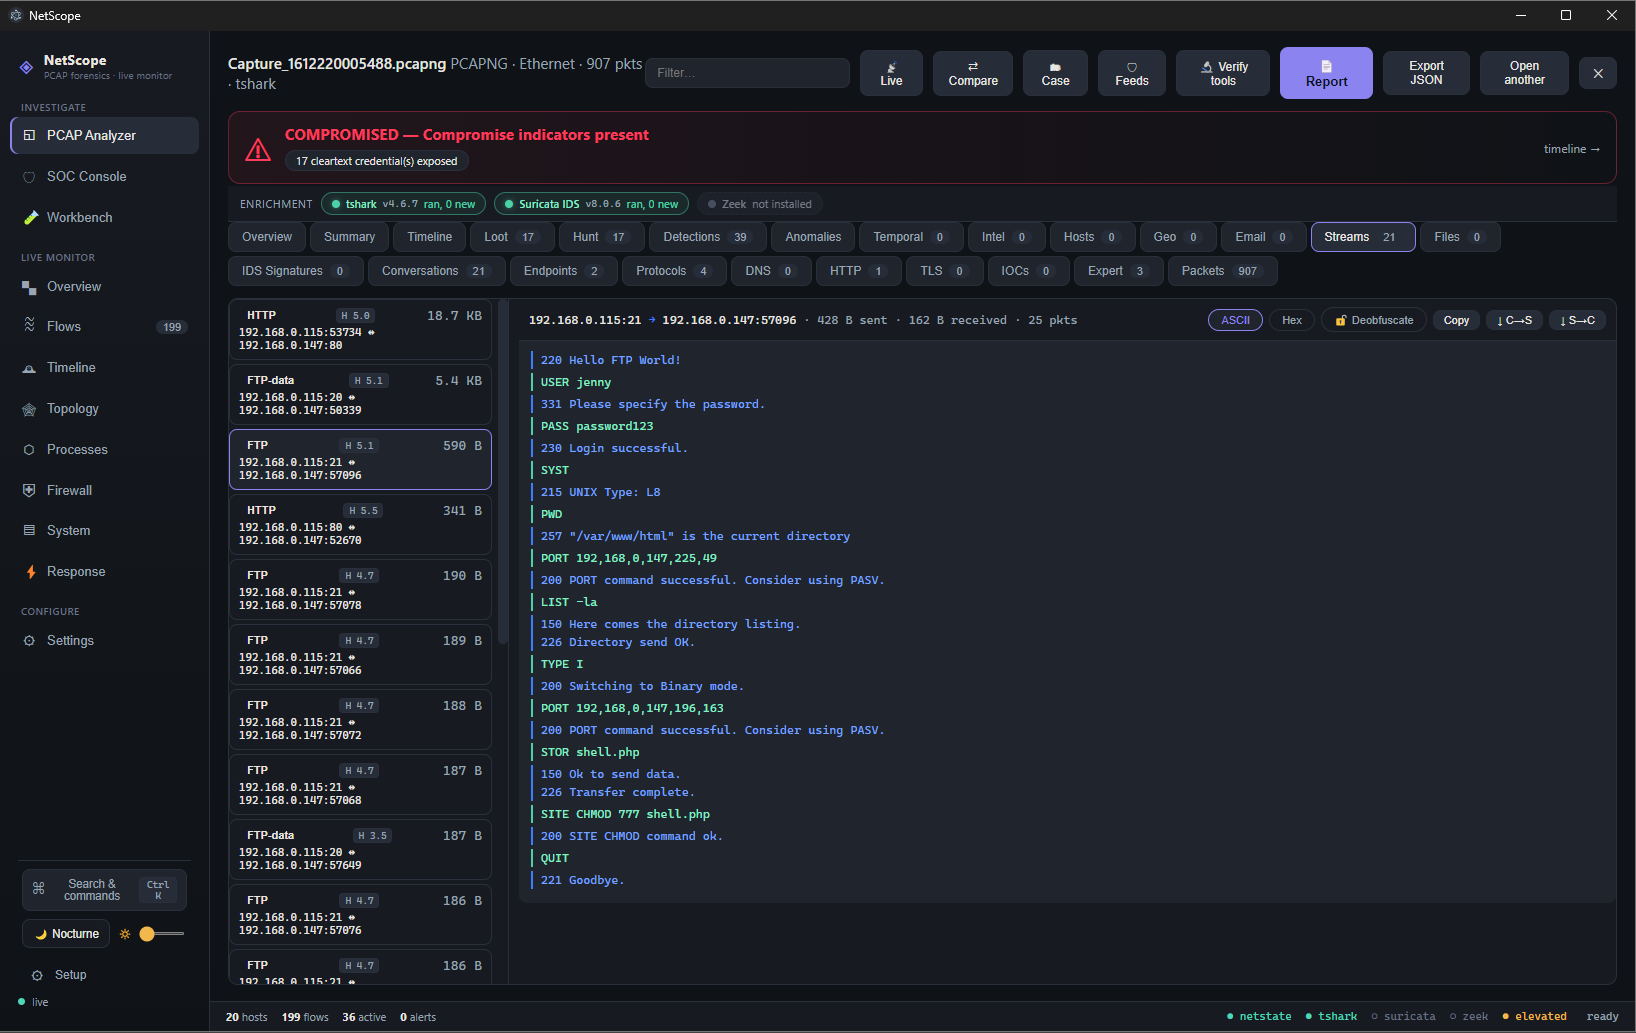
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
31 month ago
npm-incident-response preview

npm-incident-response

GitHubsecurest8/npm-incident-response

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
digital-forensicsincident-responsemalware-analysis+3
21 month ago
pcileech preview

pcileech

GitHubufrisk/pcileech

Direct Memory Access (DMA) Attack Software
digital-forensicsexploitationhardware-security+7
7.9k2 months ago
reverse-SynthID preview

reverse-SynthID

GitHubaloshdenny/reverse-synthid

reverse engineering Gemini's SynthID detection
adversarial-attackai-securitycurated-resources+6
4.9k2 months ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

data-recoverydigital-forensicsexploitation+3
1042 months ago
Awesome-BEC preview

Awesome-BEC

GitHubrandomaccess3/awesome-bec

Repository of attack and defensive information for Business Email Compromise investigations
cloud-securitycurated-resourcesdigital-forensics+7
2813 months ago
PAN-OS-CVE-2024-3400-Command-Injection-Investigation preview

PAN-OS-CVE-2024-3400-Command-Injection-Investigation

GitHubzedocun/pan-os-cve-2024-3400-command-injection-investigation

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
digital-forensicsincident-responselog-analysis+3
15 months ago
conti-ransomware-writeup preview

conti-ransomware-writeup

GitHubjustjeff211/conti-ransomware-writeup

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
digital-forensicseducationforensics+6
6 months ago
LockBit-Ransomware-Analysis preview

LockBit-Ransomware-Analysis

GitHubvignesh-hp/lockbit-ransomware-analysis

Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
data-exfiltrationdigital-forensicseducation+8
7 months ago
wcw-cyberring-pav-decryptor preview

wcw-cyberring-pav-decryptor

GitHubblakebratcher/wcw-cyberring-pav-decryptor

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

binary-analysiscryptographydata-recovery+5
257 months ago
HashTag preview

HashTag

GitHubsmeegesec/hashtag

Password Hash Identification

digital-forensicsforensicshash-analysis+3
2248 months ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
inception preview

inception

GitHubcarmaa/inception

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…

digital-forensicsexploitationhardware-security+6
1.6k1 year ago
Previous12Next